 CTF思路
点击放大
GoRAT - GoRAT (Go Remote Access Tool) is an extremely powe
项目说明
!GitHub
![Go Reference]()
!Go Report Card
![Codacy Badge]()
GoRAT(Go Remote Access Tool) is an extremely powerful yet simple reverse shell, file server, and control plane using HTTPS reverse tunnels as a transport mechanism. (GoRAT is not anonymous and designed for CTF players, Go enthusiasts, and security experts.)
Supported Distros:
| 64Bit Distros | 32Bit Distros |
|---------------------|-------------------------------|
| Linux | Linux |
| FreeBSD | FreeBSD |
| OpenBSD | OpenBSD |
| Linux ARM | Linux ARM |
| FreeBSD ARM | FreeBSD ARM |
| OpenBSD ARM | OpenBSD ARM |
| Linux MIPS | Linux MIPS |
| MacOS | (NOT BUILDING) MacOS |
| Android ARM | (NOT BUILDING) Android ARM |
| Windows (kinda) | Windows (kinda) |
Installing and Building Native
1. Set up a full GoLang build en
2. Install UPX
3. Install Garble with
go get mvdan.cc/garble4. Fill out
config.sh5. Run
./build_payload.sh --allInstalling and Building with Docker
1. Install and start docker
2. Fill out
config.sh 3. Run
./build_payload.sh --dockerUsing the Payloads
1. Transfer the
BUILD folder to your "attacking" machine, install bc and run ./start_server.sh2. Exploit your system and run the binary
3. Connect to the "target" ssh from the "attacking" machine
Chisel Ser
GoRAT uses the standard release binaries provided by the chisel project. The ser a number of configure options and has fairly logging. For this reason a small shell script is provided to start and parse the output of chisel for easy use. To use it, run the following:
1.
cd server 2.
./start_server.sh As clients connect you will see a log like this. We will use this log to access each clients SSH Server, HTTP File Server, and HTTP Control Server.
Payload Usage
As with many Go binaries, client executables require zero configure and simply need to be executed. In its current state GoRAT does not include any methods of persistence so if you would like to make it a service, you will need to do so by your own methods.
The payload also uses garble to produce a binary that works as well as a regular build, but has as little information about the original source code as possible.
SSH Server (Linux, FreeBSD, Darwin, OpenBSD)
Using the logs we can connect to clients directly via ssh using our standard unix OpenSSH package.
WSSH Windows (The Problem Child)
*WARNING THE WINDOWS SHELL IS TERRIBLE, THIS WAS JUST AN EXPERIMENT*
Please check out this thread:
When connecting to Windows hosts the following command will not work as GoRAT does not have a Windows PTY. For Windows systems we connect using a custom wrapper written for GoRAT.
Control Server
The control server is a simple http mechanism that translates
/some-page to internal go commands. In this way, requesting a webpage results directly in the execution of code on a client system. While this mechanism is not very sophisticated, it is extremely reliable and performant. The api current has the following commands:1. - Returns a status code of OK if the host is online and responding to requests
2. - Reports basic hardware survey of device in json
3. - Closes the client payload WITHOUT self-destruction
4. - Terminates the client payload AND self-destructs
File Server
Each client's file server can be accessed on the same port as the control server. The file server is, from a technical standpoint, directly part of Control Server. Files and directories can be accessed at
wget and curl.Architecture
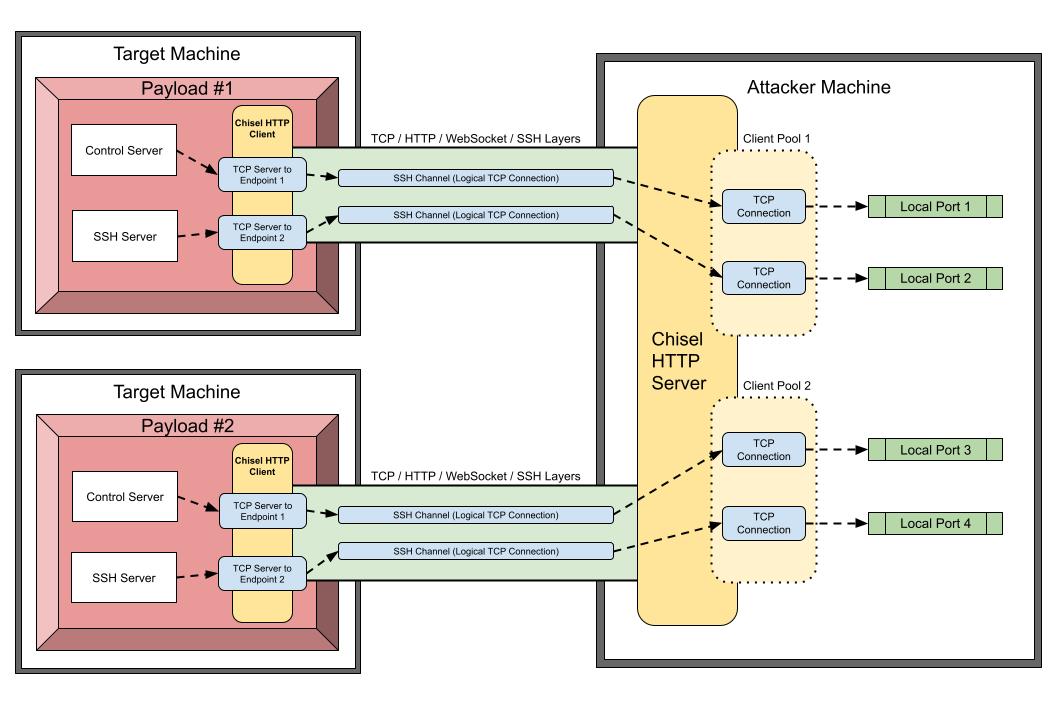
GoRAT uses chisel and gliderlabs ssh server to create a high performance remote reverse tunnel o. The diagram below shows how GoRAT establishes a link between multiple “targets” and a single “attacker”.
!image
Disclaimer
Use of GoRAT for attacking targets without prior mutual consent is illegal. It's the end user's responsibility to obey all applicable local, state and federal laws. We assume no liability and are not responsible for any misuse or damage caused by this software. Only use for educational purposes / ethical hacking. Multiple tools in this software include their own license.
项目信息
开发语言:Go
Star 数:82
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕GoRAT (Go Remote Access Tool) is an extremely powerful reverse shell, file server, and control plane using HTTPS reverse tunnels as a transport mechanism.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | GoRAT - GoRAT (Go Remote Access Tool) is an extremely powe |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:58:35 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 118 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |