 CTF思路
点击放大
flagchecker - For effective cheating detection in security compe
项目说明
flagchecker
Effecti Detection for CTFs/competitions. Feel free to submit PR.
This idea was inspired by the way flags were generated in the Korean domestic CTF contest called Cyber Conflict Exercise.
I decided to create this from the scratch. The module was tested on 4.15, 4.19, 5.8, 5.11.
Directory structure
How it works
In many recent CTF competitions, docker has been used for effecti management such as container isolation and log tracing.
!docker image
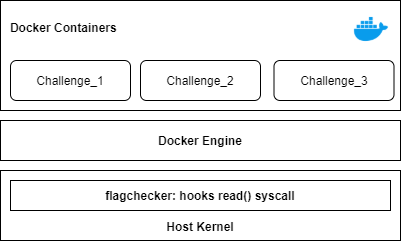
All Docker containers use the host kernel, which e means that *inserting kernel modules could affect the docker instance*. Wikipedia) says that
> Docker uses resource isolation features of the Linux kernel such as cgroups and kernel namespaces to allow independent "containers" to run within a single Linux instance, a the o of starting machines.
This also means that <u>hooking a syscall from the host kernel will e affect the container too</u>.
With this in mind, I de a simple Linux kernel module called flagchecker that generates a random flag and records it somewhere within the host instance to keep the record of user's flag submissions.
!patched-docker-structure
What flagchecker does is as follows:
1. Hooks the read() syscall.
2. When the binary calls for a read() syscall, it looks for the string.
To ensure that the server does not suffer from the performance bottleneck, <u>the module only reads for the first 255 byte</u>.
3. When there is a value that matches with the hardcoded flag value
1. The random value is generated. (0-9, a-f)
2. Replaces the original string with the randomly generated value.
3. /srv/flag.py is then executed to record the randomly generated value.
!docker2
This project was tested on a small CTF named BingoCTF sponsored by Power of Commmunity (POC).
During the test, I created an additional ser the instance to gather the flag and and communicate with the scoreboard server.
!docker3
Having the flagchecker on the same machine made it easier for the scoreboard server to integrate and for organizers to check cheating attempts.
How to use
Please refer to the each directory for more information.
Known Issues
1. Reading partial data of the flag will leak the original content of the flag.
For example, head -c68 /flag will only read the partial data of the flag, leading to the leakage of the original flag.
Make sure that the original value of flag is randomly generated and does not conflict with other flags.
2. Side Channel Attacks
I haven't or succeed on exploiting this bug, but it may be possible that strstr is to timing attacks.
(Reported by a person who tested this module during the initial de.)
Q&A
> What was the result of the test?
Worth checking here.
We failed to catch direct flag trades but we managed to catch people who broke the rules.
> I' some challenges but my flag wasn't changing at that time. What happened to those challenges?
We had a lenient code to co that didn't really require LKM. Check out the following code.
I' the code to generate the flag but didn't disclose this part while handing out the dist file.
> You said your idea was inspired from the other CTF i.e. CCE. Are you sure they implemented such codes?
It's just an assumption. I have not directly asked organizers how they implemented such behaviors, but I tried to make something similar because it seemed pretty interesting.
项目信息
开发语言:C
Star 数:69
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕For effective cheating detection in security competitions. Uses Linux Kernel Module (LKM) for generating flags.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | flagchecker - For effective cheating detection in security compe |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:01:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 422 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |