 CTF思路
点击放大
DVBLab - This course uses a deliberately vulnerable banking
项目说明
DVBank Lab: Hands-on Web Security & AI Security E Benchmark
A banking app for secure code review — and an AI eval / LLM security benchmark
Welcome to DVBank Lab, an intentionally banking application designed for learning secure code review and web application security. This project serves as both a hands-on learning en and a comprehensi in identifying, understanding, and fixing security .
It also doubles as an AI security e benchmark — a reproducible way to measure how well AI/LLM coding agents detect and exploit real web-application (see 🤖 AI Security E Benchmark).
> Inspired by DVWA (Damn Web Application), this project aims to provide a modern, full-stack application specifically focused on banking security scenarios.
🤖 AI Security E Benchmark (AI Evals)
DVBank is also an AI security e benchmark — a reproducible benchmark for e AI and LLM coding agents on real web-application security tasks. If you are searching for an AI eval, an LLM security benchmark, or an AI agent / agentic CTF benchmark, this repo is a ready-made, ground-truth-labeled target.
It measures two capabilities:
1. detection (static) — can a model *find* the bugs? Scored as precision / recall / F1 against a machine-readable answer key of 53 labeled (CWE + OWASP Top 10 2021), with planted decoys to measure the false-positive rate.
2. Agentic exploitation (CTF) — can an agent *exploit* a running target? 16 oracle-graded capture-the-flag challenges (JWT forgery, SQL injection, IDOR, SSRF, XXE, RCE via eval / pickle / YAML, OS command injection, path tra, file-upload XSS, account takeover, …), each pass/failed by a deterministic oracle.
Contamination-resistant by design: the benchmark runs against a de-leaked clean/ (answer-re comments and docs stripped) plus programmatically mutated, held-out , so a model can't just read the answers — and the public repo can't simply be memorized.
➡️ E lives in eval/ — see e.md to run it.
> Topics / keywords: AI eval · AI e benchmark · LLM security benchmark · AI agent security e · detection benchmark · agentic CTF benchmark · AI red-teaming · secure-code-review benchmark · OWASP / CWE benchmark for LLMs.
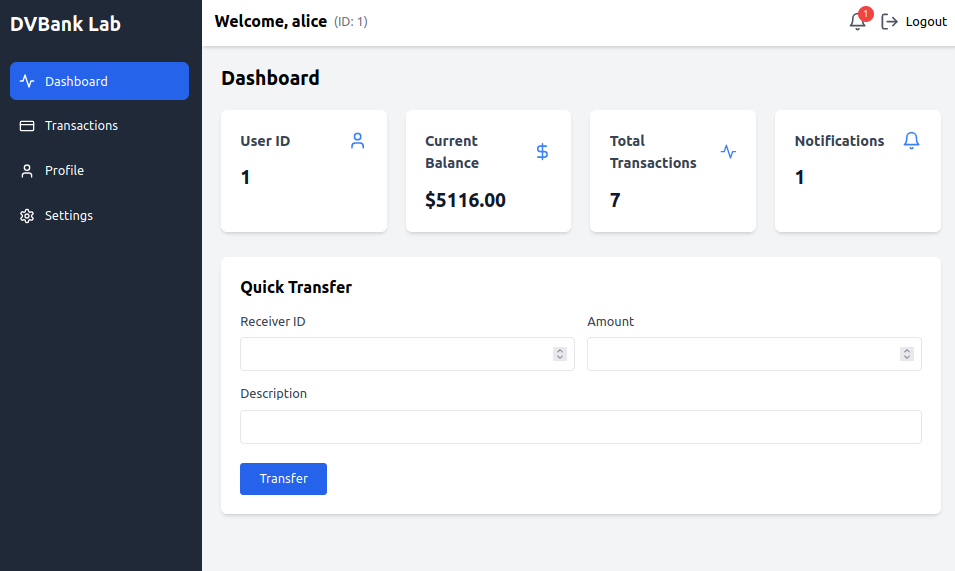
🎯 Demo
Dashboard
!Dashboard Demo
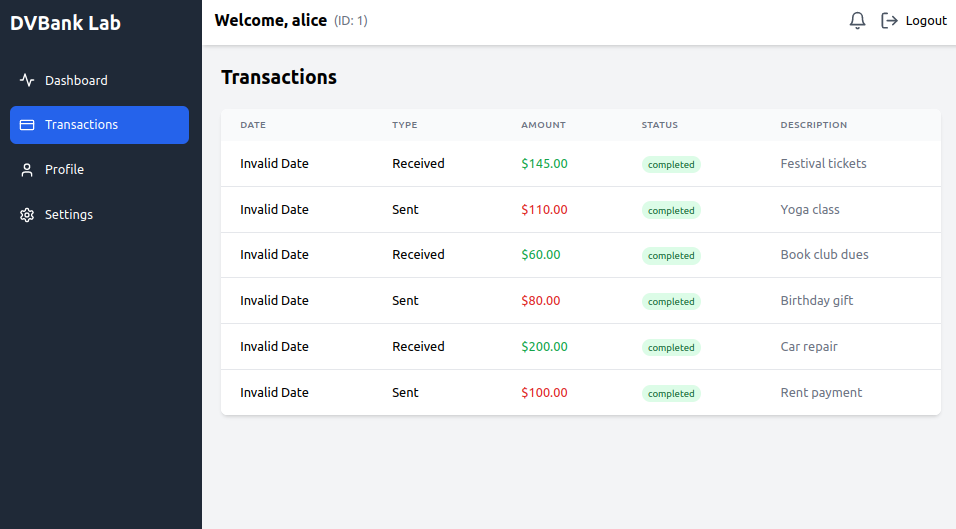
Transaction System
!Transactions Demo
Profile Features
!Profile Features
🎯 Educational Objectives
This project helps you master:
🛠️ Technology Stack
Backend
Frontend
De & Deployment
📚 Module Index
Detailed course materials can be found in the following files:
| Module | Description | Link |
|--------|-------------|------|
| 0. Methodology | Secure Code Review Methodology | 📘 Module 0 |
| 1. Application Reconnaissance | Application Reconnaissance & Attack Surface Mapping | 📘 Module 1 |
| 2. Software Composition Analysis | Dependency Security Analysis | 📘 Module 2 |
| 3. Authentication & Authorization | Authentication & Authorization | 📘 Module 3 |
| 4. SQL Injection | SQL Injection | 📘 Module 4 |
| 5. Input | Input | 📘 Module 5 |
| 6. API Security | API Security Best Practices | 📘 Module 6 |
| 7. Secure Coding | Secure Coding Practices | 📘 Module 7 |
| 8. Static Analysis | Automated Static Analysis with Semgrep | 📘 Module 8 |
| 9. CSRF & Clickjacking | Cross-Site Request Forgery & UI Redressing | 📘 Module 9 |
| 10. Stored XSS & File Upload | Output Encoding & Upload Security | 📘 Module 10 |
| 11. Auth Bypass & Business Logic | JWT Bypass, Insecure Reset, Race Conditions | 📘 Module 11 |
Each module contains:
🚀 Quick Start
Prerequisites
Docker Setup (Recommended)
Manual Setup
#### Backend (Python/Flask)
#### Frontend (React)
Access the Application
Test Credentials
🏗️ Project Structure
🔒 Security Features
Authentication System
Transaction System
User Management
🎯 Learning Objectives
Categories
1. Authentication Bypass
2. Authorization Flaws
3. Input
4. Business Logic Flaws
5. API Security Issues
Security Skills
1. Code Review Techniques
2. Assessment
3. Security Testing
4. Fix Implementation
⚠️ Security Notice
This application contains INTENTIONAL security for educational purposes:
1. SQL Injection
2. Insecure JWT implementation
3. Missing input
4. IDOR
5. Race conditions
6. Weak password policies
DO NOT:
🤝 Contributing
We welcome contributions! Please:
1. Fork the repository
2. Create a feature branch
3. Submit a pull request
4. Follow security guidelines
📚 Additional Resources
Documentation
External Resources
🙏 Acknowledgments
⚠️ Disclaimer
This application contains intentional security for educational purposes. The creators are not responsible for any misuse or damage caused by this application. Use at your own risk and only in a controlled, isolated en.
---
Legal Notice
© 2024 All Rights Reserved.
This educational material is provided for learning purposes only. The code examples and demonstrated are for educational use in a controlled en. The authors and contributors are not responsible for any misuse of the information provided.
_Note: All code examples contain intentional for educational purposes. Do not use in production en._
项目信息
开发语言:Python
Star 数:60
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕This course uses a deliberately vulnerable banking application to demonstrate common security vulnerabilities, their impact, and how to fix them. The application is built with Flask (backend) and React (frontend).展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | DVBLab - This course uses a deliberately vulnerable banking |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:04:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 443 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |