 CTF思路
点击放大
ctf_proxy - An Intrusion Prevention System for Attack-Defense
项目说明
ctf_proxy - An Intrusion Pre System for Attack-Defense CTFs
ctf_proxy creates a proxy process for each configured service, with the possibility to block malicious attacks by means of custom Python filters.
This tool is purposely made for *Attack/Defense* CTF competitions.
Features
Architecture
!architecture
This architecture implements a failo through the usage of NGINX:
Configuration
You can configure each service to be proxied using
proxy/config/config.json.Parameters
In the
services list, the following parameters can be set for each service:true to enable HTTP parsing, default=proxy/config/certificates folder:- ser: ser
- ser: server key file
- client_certificate: *(optional)* for client authentication between proxy and service
- client_key: *(optional)* for client authentication between proxy and service
- ca_file: *(optional)* certificate authority for checking client authentication between client and proxy
The global_config contains:
- connect_timeout: (*seconds*) timeout given to NGINX to declare the proxy as down when trying a connection
- fail_timeout: (*seconds*) sets the time during which the specified number of unsuccessful attempts to communicate with the ser happen to consider the ser and the period of time the server will be considered una.
- max_fails: (*seconds*) sets the number of unsuccessful attempts to communicate with the server that should happen in the duration set by the
fail_timeout parameter to consider the ser.- enabled: *(boolean)*
- duration: *(seconds)* time to wait before closing the socket
- interval: *(seconds)* time inter packets to keep the socket alive
pre queue in the Stream objectspre queue in the Stream objectsUsage
Clone the repository:
Edit the docker-compose.yml file with the current port mapping. For example, if you want to listen on port 8080 and 9090, you need to set:
Edit the proxy configuration file at proxy/config/config.json.
Run the container:
:warning: NGINX at boot requires all services to be up and running. It may cause restart loops until you start all containers. :warning:
#### FOR A/D CONTAINERIZED SERVICES
You may want to add this configuration to the services docker-compose.yml file and *remove any address/port binding* it may have, to take ad of the docker network DNS.
This way, you can use the services' hostname directly in the target_ip parameters. Moreover, as the services are connected to the proxy network they are reachable inside it without exposing or changing any port, but not reachable from the outside.
Note: the network must already exist, so the proxy should be run before the services.
Automatic script (CyberChallenge)
All the abo can be done with the provided setup script. Either clone the repository, install ruamel.yaml and run the script or directly run
The script will work as long as it is called from inside ctf_proxy or besides all the services. In the latter case it will clone ctf_proxy before configuring it.
You can manually provide paths for the services as arguments when you call the script. If you don't it will automatically scan cwd and look for services, asking for confirmation.
Modules
These are the core filtering entities of the proxy. For each proxied service, a pair of modules is *automatically generated* inside the
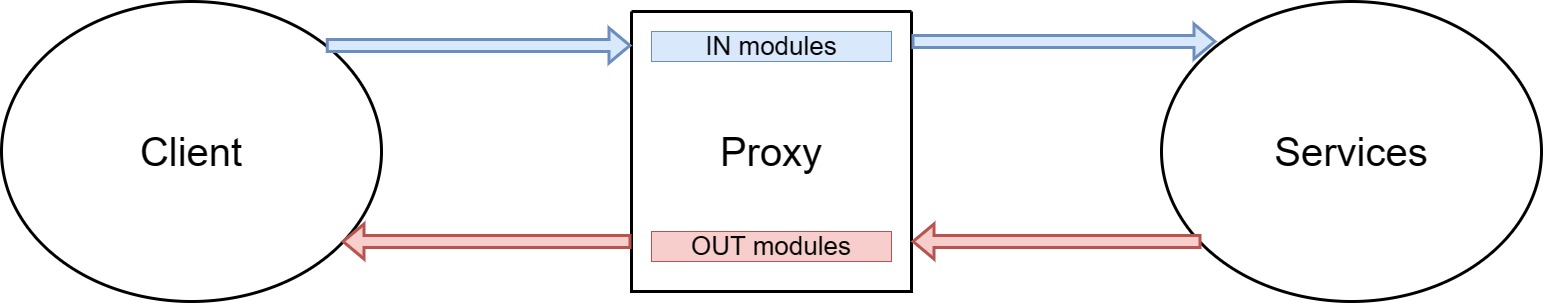
proxy/filter_modules/<ser>/ folder the first time you run the proxy. Modules execution will follow this flow: !proxy
Inside the modules you will find an execute method that receives a *Stream object* from the proxy and returns to the proxy whether the stream contains an attack or not. If an attack is found, the proxy will send to the attacker a custom string () to easily find attacks in PCAP files if a packet analyzer is used in the system. At this point, the socket will be kept alive to interfere with attackers' scripts if the dos parameter is enabled, otherwise the socket will be closed.
:warning: Note that dos may not work properly if ssl is enabled :warning:
Stream
Stream is the interface for TCPStream and HTTPStream classes and contains the current and previous exchanged messages on the socket.
#### TCPStream
TCPStream is used in case of TCP only connections. The pre queue contains the latest max_stored_messages messages that went through the socket before the current recei. The latter will be stored in the current_message and can be modified to alter the content of the message that will be sent from the proxy. Note that in this case you should return False inside the filter to not drop the connection.
#### HTTPStream
HTTPStream is used in case of HTTP connections. Two more are a: pre and current_http_message. They are the parsed of the correspective raw as HttpMessage objects. The actual sent through the socket are the ones stored in current_message, which means you should edit this to alter the content of the message sent from the proxy.
:warning: Watch out for Content-Length header in the raw HTTP message if you intend to modify it. :warning:
Update module
To add a new filter, define a new function inside the class Module called as the name of the attack (or a custom one if you prefer) that accepts a Stream object as parameter and returns a boolean (True if attack found, False if not). You will find a filter example in
proxy/filter_modules/template.py.Every module will be *automatically reloaded on the fly* by simply modifying it. If an exception is thrown during the import, the module will not be loaded and the previous will be used instead. If an exception is thrown at runtime, the packet will simply flow through the proxy.
Database
For stateful filters, you can build and use the local Mongo database. You can access the database inside the modules through the
DBManager interface. You can find some examples in proxy/filter_modules/example_functions.py.Logging
A simple log file
proxy/log.txt will count all the blocked packets for each service. If the file already exists at startup, the proxy will update the counts based on their initial value inside the file. Otherwise, the file will be created at startup.You can monitor the file by using:
Any relevant information will be printed to stdout. Set to true for more info.
If you're using the Docker , you can inspect the docker logs to access them:
Credits
Written by:
This tool is inspired by and partially based on the TCP proxy logic of tcpproxy.py.
项目信息
开发语言:Python
Star 数:59
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An Intrusion Prevention System for Attack-Defense CTFs展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ctf_proxy - An Intrusion Prevention System for Attack-Defense |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:04:30 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 379 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |