 防护思路
点击放大
Claude-Code-CyberSecurity-Skill - 22 production-quality Claude Code Skills for cyber
项目说明
<p align="center">
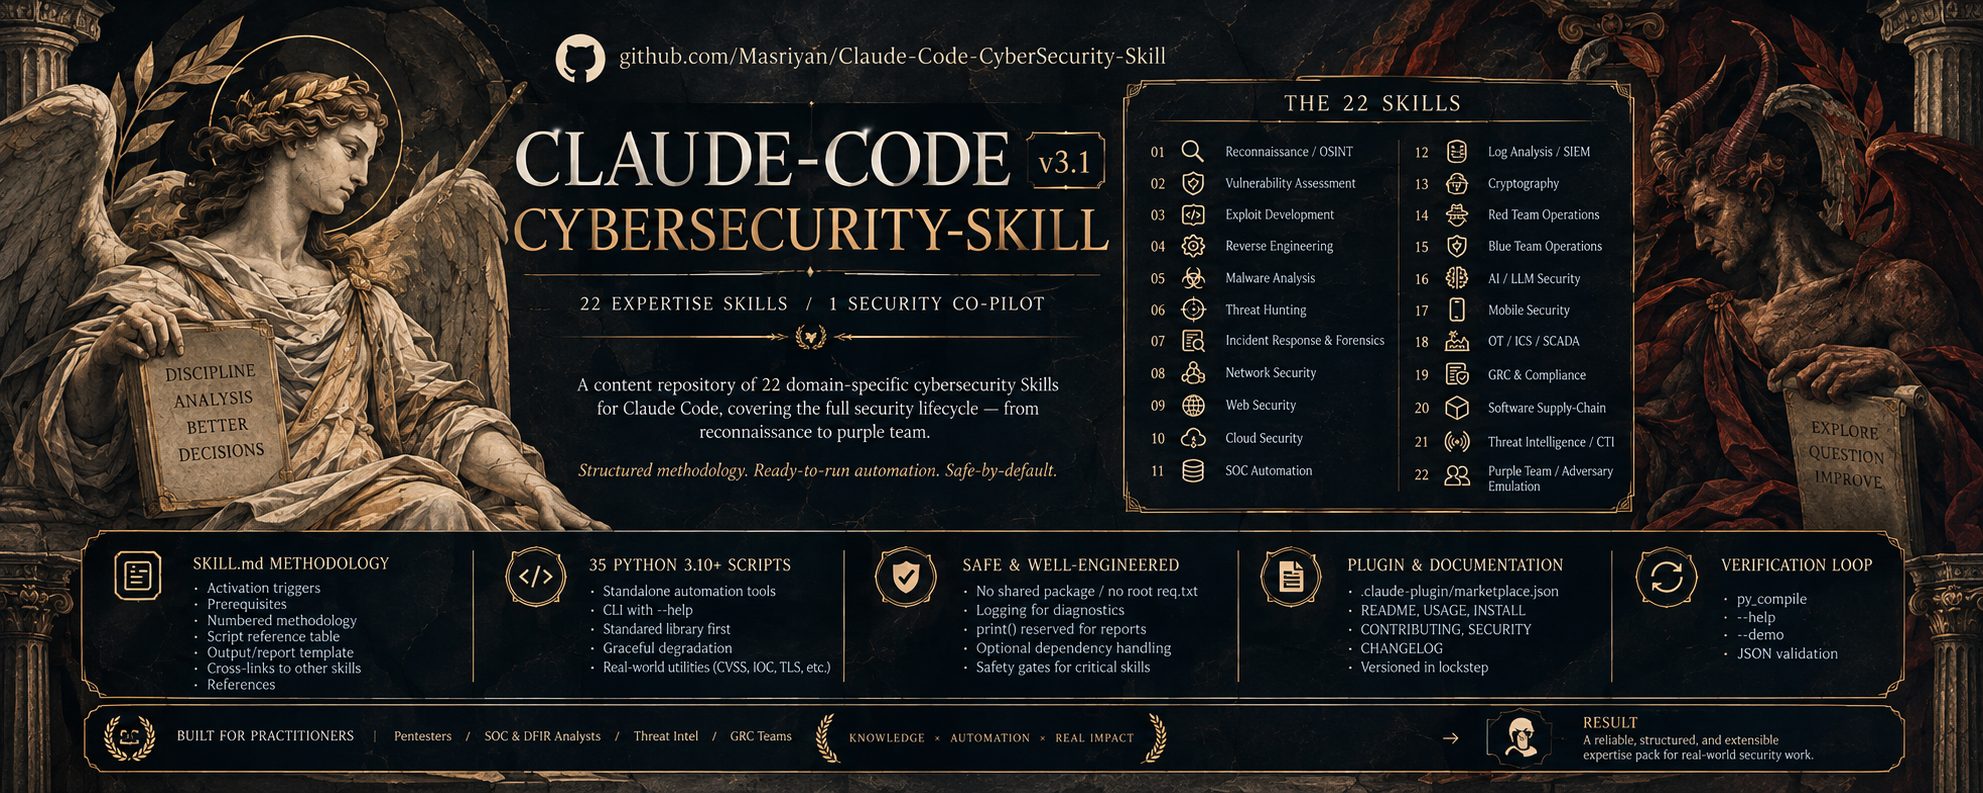
<img src="assets/banner.png" alt="Claude Code Cyber Security Skills" width="100%">
<img src=" alt="Claude Code CyberSecurity Skills"/>
<br/>
<img src=" alt="Skills"/>
<img src=" alt=""/>
<img src=" alt="License"/>
<img src=" alt="Python"/>
<img src=" alt="Platform"/>
</p>
> 🛡️ Antivirus Notice: Some A may flag this repository due to security testing payload *templates* (string constants for authorized pentesting). These are false positives — no executable malware exists. This is standard for all cybersecurity toolkits (SecLists, PayloadsAllTheThings, Metasploit face the same detections). See SECURITY.md for details.
Claude Code CyberSecurity Skill Collection
> 22 production-quality Claude Code Skills for cybersecurity professionals — co offensi, defensi, reverse engineering, threat hunting, threat intelligence, purple team / ad emulation, CSOC automation, AI/LLM security, mobile, OT/ICS, GRC, software supply chain security, and more. 3.1 — expanded co, sharper methodology, and stronger automation.
Transform Claude Code into your ultimate cybersecurity co-pilot. Each skill provides Claude with structured methodology, decision frameworks, ready-to-run commands, and output templates that enable precise, expert-le for real-world security operations.
---
What Are Claude Code Skills?
Claude Code Skills are structured SKILL.md files that you install into your ~/.claude/skills/ directory (global) or .claude/skills/ (project-specific). When Claude reads these files, it gains deep, domain-specific expertise that goes far beyond generic knowledge.
How Skills Work
Skills are instruction documents Claude reads at con start. Each SKILL.md contains:
1. YAML frontmatter — name, description, tags for skill identification
2. Acti triggers — Explicit list of prompts that should invoke this skill
3. Methodology — Step-by-step procedures Claude follows natively
4. Output templates — Exact formats for reports, rules, and artifacts Claude produces
5. Script references — When and how to use the included Python automation scripts
6. Authorization gates — Built-in prompts for offensi to confirm legal scope
Claude Code-Nati
These skills are built around what Claude does natively in Claude Code:
---
Update proof of works
<img src="assets/Updates.png" alt="Claude Code Cyber Security Skills Install Proof" width="100%">
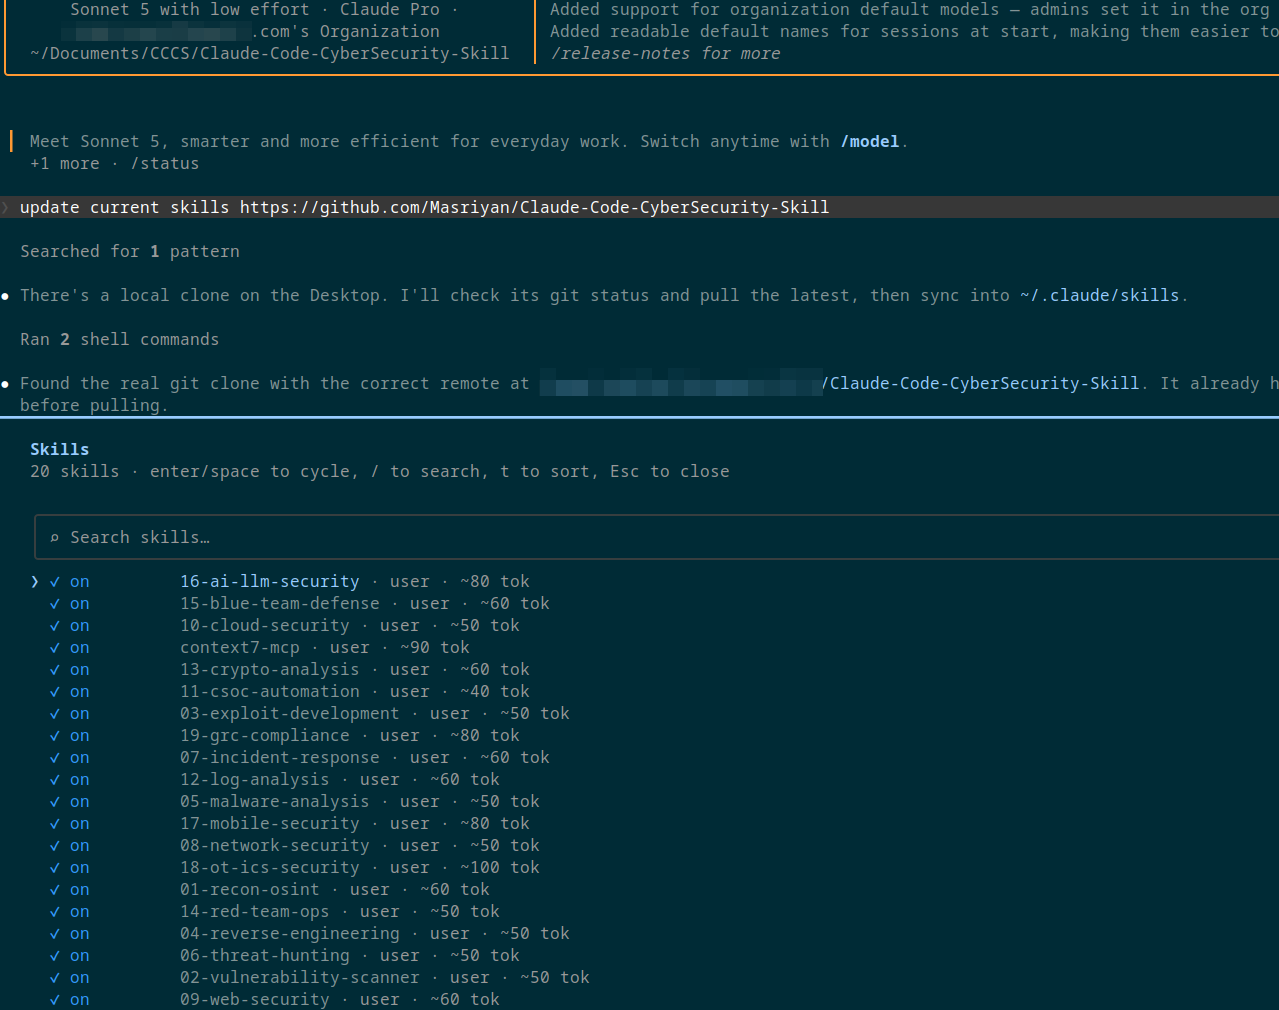
Update testing
<img src="assets/Updates2.png" alt="Claude Code Cyber Security Skills Testing" width="100%">
Skill Collection
| # | Skill | Domain | Key Capabilities |
|:-:| ----- | ------ | ---------------- |
| 01 | Recon & OSINT | Reconnaissance | Subdomain enum, DNS analysis, technology fingerprinting, Google dorking, WHOIS |
| 02 | Scanner | Assessment | Dependency auditing, config review, C, structured reports |
| 03 | Exploit De | Offensive | PoC templates, payload generation, buffer o, web exploit payloads |
| 04 | Reverse Engineering | Analysis | Binary triage, assembly interpretation, firmware RE, protocol re, CTF |
| 05 | Malware Analysis | Threat Analysis | Static analysis, YARA generation, sandbox setup, beha analysis, IOC extraction |
| 06 | Threat Hunting | Hunting | IOC extraction, ATT&CK mapping, hunt hypotheses, Sigma + SIEM query library |
| 07 | Incident Response | IR & Forensics | PICERL playbooks, e collection, timeline analysis, memory forensics, IR reports |
| 08 | Network Security | Network | PCAP analysis, Suricata/Snort rules, firewall auditing, beaconing detection |
| 09 | Web Security | Web | OWASP Top 10, injection testing, API security, JWT analysis, security headers |
| 10 | Cloud Security | Cloud | AWS/Azure/GCP audit, Dockerfile review, K8s hardening, IaC scanning |
| 11 | CSOC Automation | SOC Operations | Alert triage, playbook YAML, escalation workflows, shift reports, KPI tracking |
| 12 | Log Analysis & SIEM | Log Analysis | SIEM query library (Splunk/KQL/EQL), Sigma rules, anomaly detection, correlation |
| 13 | Cryptographic Analysis | Cryptography | TLS auditing, cipher analysis, hash identification, crypto code review, PQC guidance |
| 14 | Red Team Operations | Red Team | Engagement planning, C2 design, AD attacks, OPSEC, social engineering, reporting |
| 15 | Blue Team Defense | Blue Team | Linux/Windows hardening, detection engineering, baselines, patch management |
| 16 | AI & LLM Security | AI Security | Prompt injection, OWASP LLM Top 10, RAG & agent/tool-use security, model supply chain, AI red teaming |
| 17 | Mobile Security | Mobile | Android/iOS testing, MAS, APK/IPA static analysis, Frida/objection, mobile malware triage |
| 18 | OT / ICS / SCADA Security | Industrial | Purdue model, Modbus/DNP3/S7 analysis, IEC 62443, ATT&CK for ICS, safety-first methodology |
| 19 | GRC & Compliance | Go | Risk scoring, NIST CSF 2.0/ISO 27001/SOC 2 mapping, gap analysis, audit e, policy generation |
| 20 | Supply Chain Security | Supply Chain | SBOM generation/analysis, dependency confusion & typosquatting detection, CI/CD pipeline hardening, SLSA/Sigstore pro |
| 21 | Threat Intelligence & CTI | Threat Intel | Intelligence cycle, IOC extraction/defang/normalize, STIX/TAXII & MISP, Diamond/Kill Chain, source & confidence scoring, attribution, finished reporting |
| 22 | Purple Team & Ad Emulation | Purple Team | Threat-informed emulation planning (ATT&CK, Atomic Red Team, CALDERA), detect–tune– loop, co measurement (Na/DeTT&CT), MTTD/co reporting |
---
Quick Start
1. Clone the Repository
2. Install Skills into Claude Code
Claude Code loads skills from two locations:
| Location | Scope | Path |
|----------|-------|------|
| Global | All projects | ~/.claude/skills/ |
| Project | This project only | ./.claude/skills/ |
3. Use Claude Code
Open Claude Code and talk naturally. Claude activates the relevant skill based on what you ask:
Example interactions:
You can also explicitly name a skill:
---
What's New in v3.1
Two new domains and a reliability pass across the collection:
cti_processor.py.detection_.py.report_generator.py --demo now runs standalone (was rejected by required --shift/--date); C, GHSA MODERATE→MEDIUM mapping, auth-log field extraction for anomaly chaining, and TLS expired-cert detection corrected (see CHANGELOG).SKILL.md is now aligned at 3.1.0, and the marketplace manifest lists all 22 skills.---
What's New in v3.0
Bigger, sharper, more powerful — four new domains and a full refresh of the original 15:
pickle) scanner---
Project Structure
---
Prerequisites
| Requirement | | Purpose |
|-------------|---------|---------|
| Claude Code | Latest | AI coding assistant — install guide |
| Python | 3.10+ | Automation scripts |
| Git | 2.x+ | Repository management |
Optional Tools (Enhanced by Specific Skills)
---
Contributing
Contributions are welcome. See CONTRIBUTING.md for:
---
License
MIT License — see LICENSE for details.
---
Disclaimer
> This skill collection is intended for authorized security testing, research, CTF competitions, and educational purposes only. Users are solely responsible for compliance with all applicable laws. Offensi (Exploit De, Red Team Operations) require explicit authorization confirmation before Claude will assist. The authors assume no liability for misuse.
---
<p align="center">
<b>Built for the CyberSecurity Community</b><br/>
<a href=" •
<a href=" •
<a href="
</p>
项目信息
开发语言:Python
Star 数:464
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕22 production-quality Claude Code Skills for cybersecurity professionals — covering offensive security, defensive operations, reverse engineering, threat hunting, threat intelligence, purple team / adversary emulation, CSOC automation, AI/LLM security, mobile, OT/ICS, GRC, software supply chain security, and more. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Claude-Code-CyberSecurity-Skill - 22 production-quality Claude Code Skills for cyber |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:07:52 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 330 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |