项目说明
Cybersecurity: Theory, Techniques, and Tools
###### Welcome to the most extensi of encyclopedic knowledge in the world of Cybersecurity:
An ongoing & curated collection of awesome software best practices and techniques, libraries and frameworks, E-books and , websites, blog posts, links to github Repositories, technical guidelines and important resources in Cybersecurity.
> Thanks to all contributors, you're awesome and wouldn't be possible without you! Our goal is to build a categorized community-dri of very well-known resources.
What is Cybersecurity?
Cybersecurity is the collecti of protecting computer systems, networks, and programs from cyberattacks.> CISA defines it as "Cybersecurity is the art of protecting networks, devices, and data from unauthorized access or criminal use and the practice of ensuring confidentiality, integrity, and a of information."
> It seems that e relies on computers and the internet now—communication (e.g., email, smartphones, tablets), entertainment (e.g., interacti games, social media, apps ), transportation (e.g., na systems), shopping (e.g., online shopping, credit cards), medicine (e.g., medical equipment, medical records), and the list goes on. How much of your daily life relies on technology? How much of your personal information is stored either on your own computer, smartphone, tablet or on someone else's system?
<p align="center">
<img src=" alt="Sublime's custom image"/>
</p>
Cybersecurity, computer security, or information technology security (IT Security) is a very important part of the cyberspace.
> Cyberspace is a larger term than the internet. It refers to digital en in which the exchange of electronic information takes place—that includes private networks and online services beyond the public internet.
The role of cybersecurity has only become more important for the modern enterprise and increasingly for the indi. Cybersecurity is unlike any other technology sector. It’s an industry that thrives on human fear, not greed. The sector isn’t a revenue driver for businesses neither can its cost-saving impact always be empirically measured.
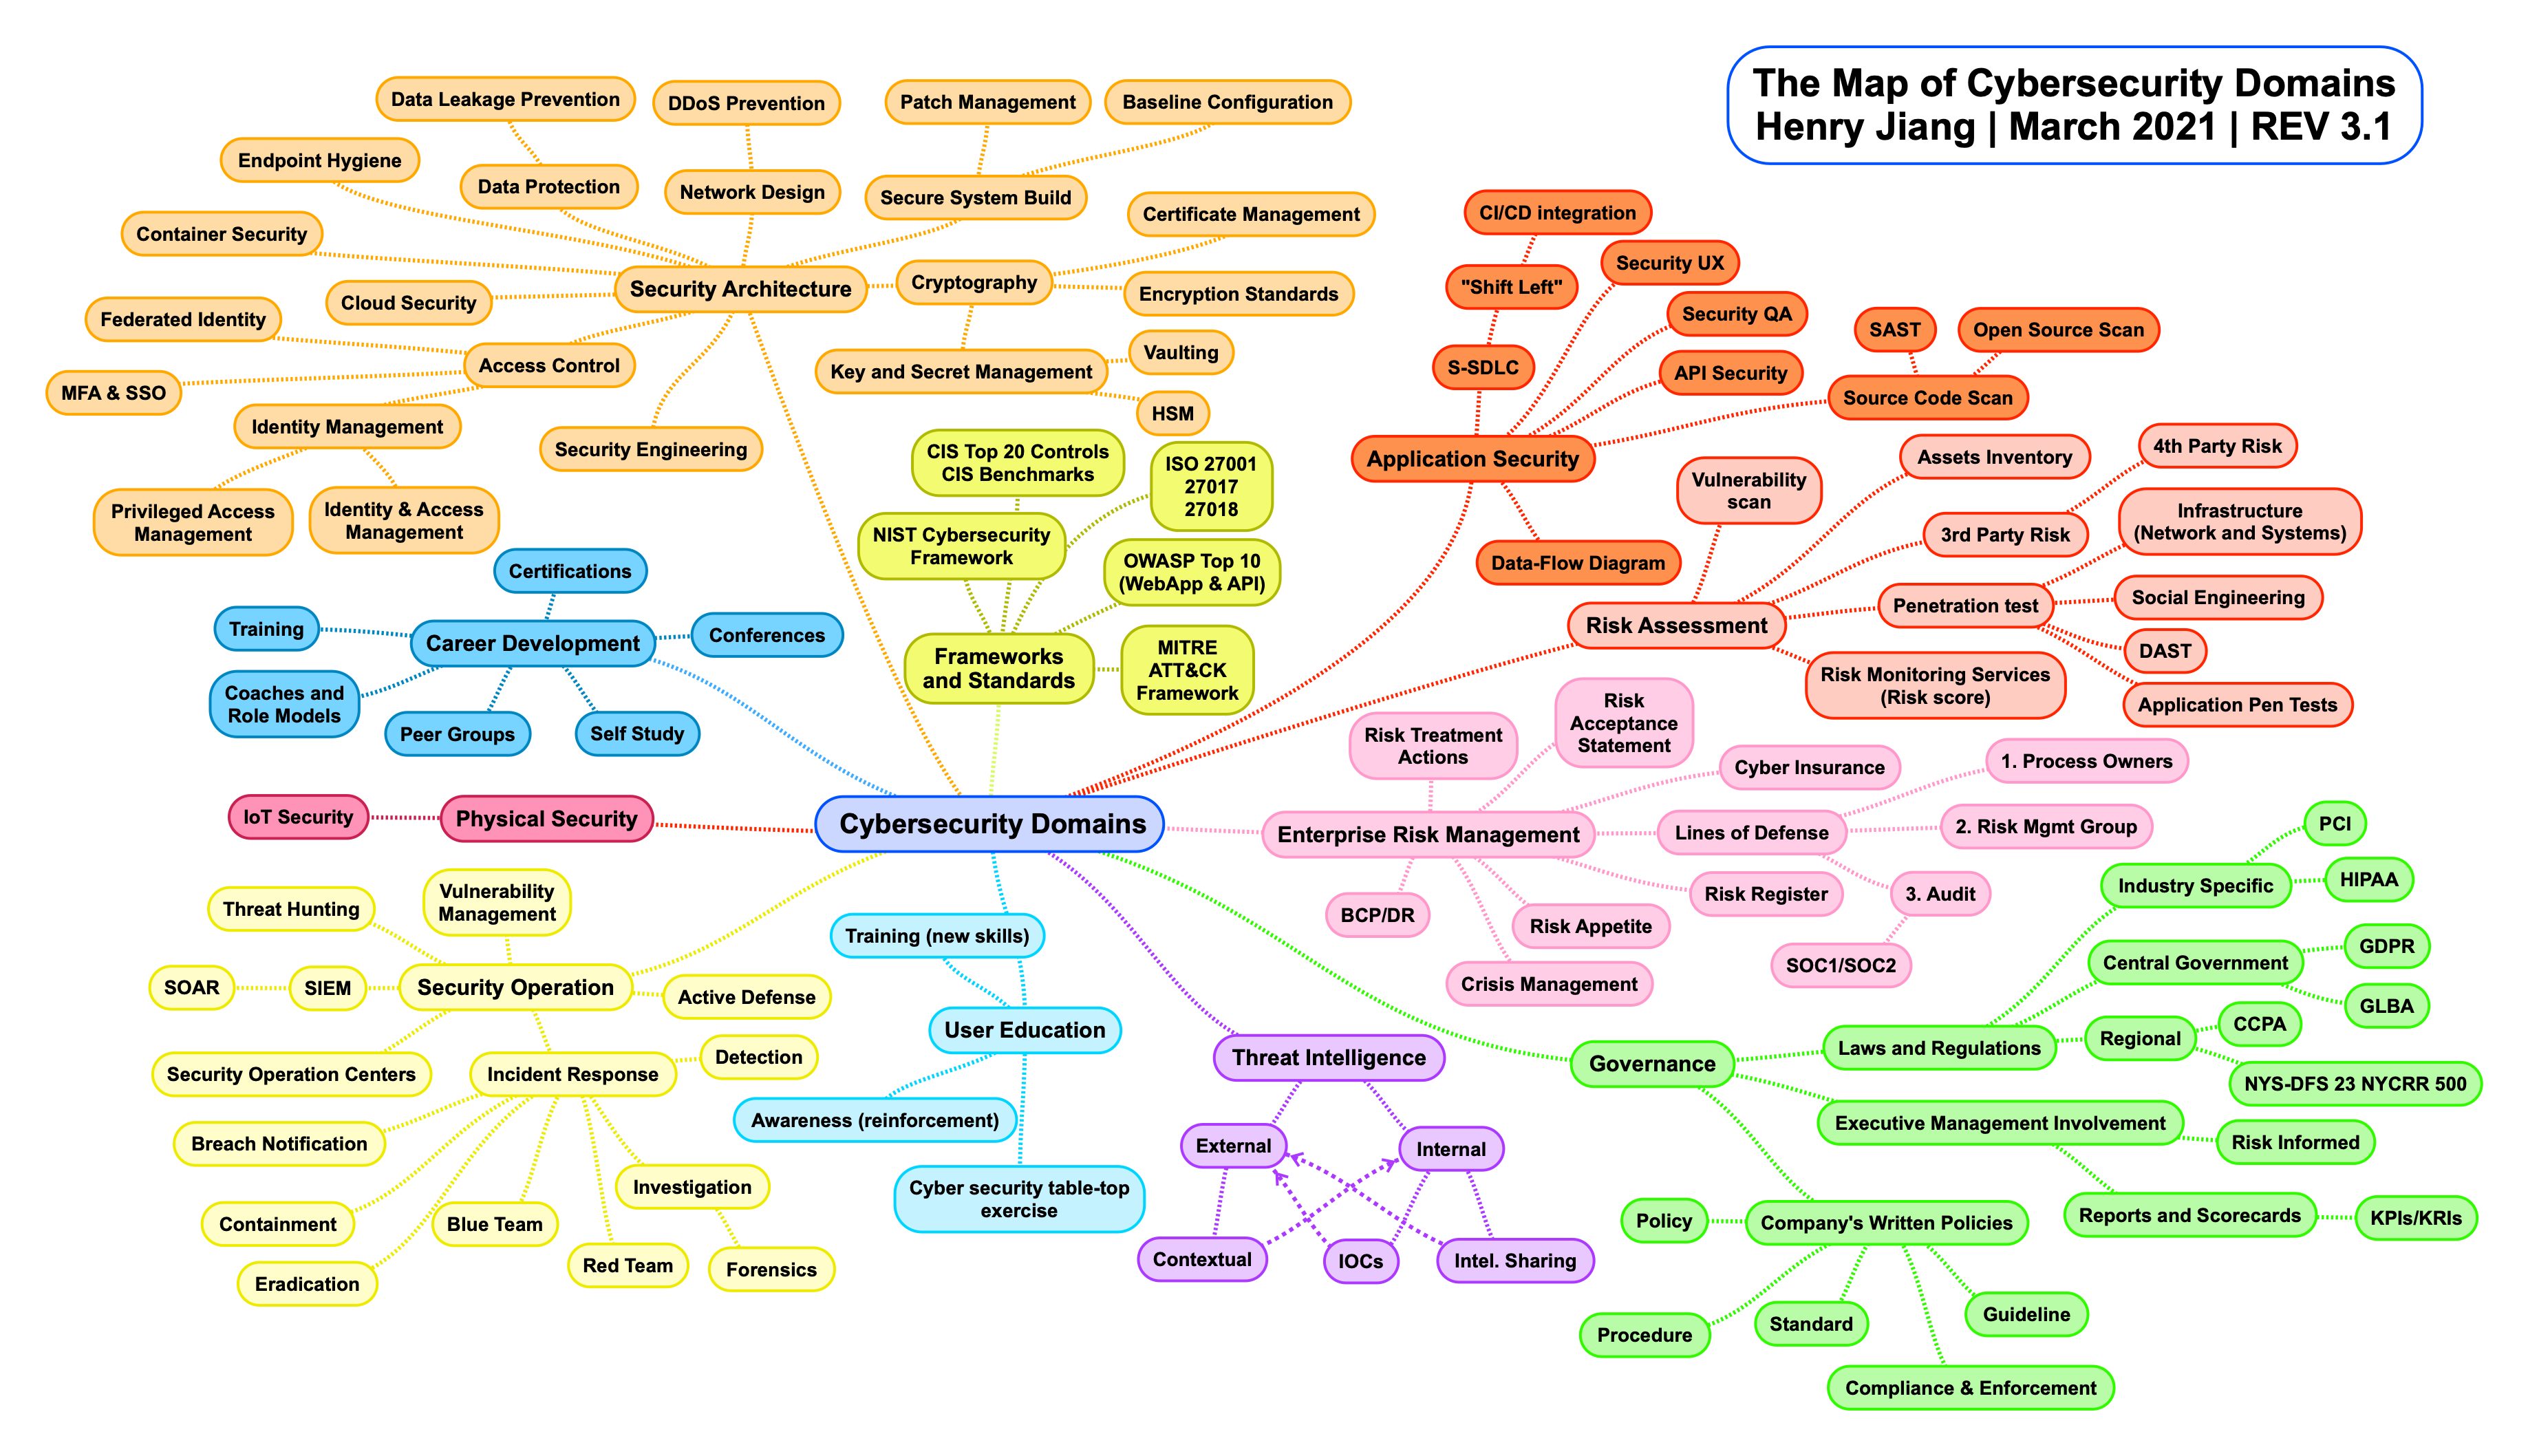
Security is a $200B industry growing over 11% each year, making it one of the largest and most mission-critical technology sectors.Today, The field of cybersecurity can be categorized into ten (10) main domains:
Table of Contents
- Cybersecurity
- Security Domains
- Security Sectors
- Security
- Security Publications
- Security Repositories
- Network
- Scanning / Pentesting
- Monitoring / Logging
- IDS / IPS / Host IDS / Host IPS
- Honey Pot / Honey Net
- Full Packet Capture / Forensic
- Sniffer
- Security Information & Event Management
- VPN
- Fast Packet Processing
- Firewall
- Anti-Spam
- Docker
- Endpoint
- Anti-Virus / Anti-Malware
- Content Disarm & Reconstruct
- Configuration Management
- Authentication
- Mobile / Android / iOS
- Forensics
- Threat Intelligence
- Social Engineering
- Web
- Organization
- Web Application Firewall
- Scanning / Pentesting
- Runtime Application Self-Protection
- De
- Red Team Infrastructure Deployment
- Exploits & Payloads
- Usability
- Big Data
- DevOps
- Operating Systems
- Online resources
- Datastores
- Fraud pre
- EBooks
- Other Cybersecurity Lists
- Other Security Awesome Lists
- Other Common Awesome Lists
- Contributing
------
Cybersecurity
Security Domains
<p align="center">
<img src=" alt="Sublime's custom image"/>
</p>
* Access Control
* Telecommunications and Network Security
* Information Security Go and Risk Management
* Software De Security
* Cryptography
* Security Architecture and Design
* Operations Security & Threat Intelligence
* Business Continuity and Disaster Recovery Planning
* Legal, Regulations, In and Compliance
* Physical (En) Security
Security Sectors
From a market perspecti & emerging technologies & services, key facts, sector background and analysis of the following 15 cybersecurity sectors:
1. Endpoint Security
2. Identity and Access Management
3. Mobile Enterprise Management
4. Mobile Security
5. Security Information and Event Management (SIEM)
6. Content Security
7. Malware Mitigation
8. Data Loss Pre (DLP)
9. Datacenter Security
10. Firewalls
11. Next Generation Firewalls
12. IDS/IPS
13. Unified Threat Management (UTM)
14. Cloud-Based Services
15. /Risk Management & Managed Security Services
Security
#### Top 200 Cybersecurity
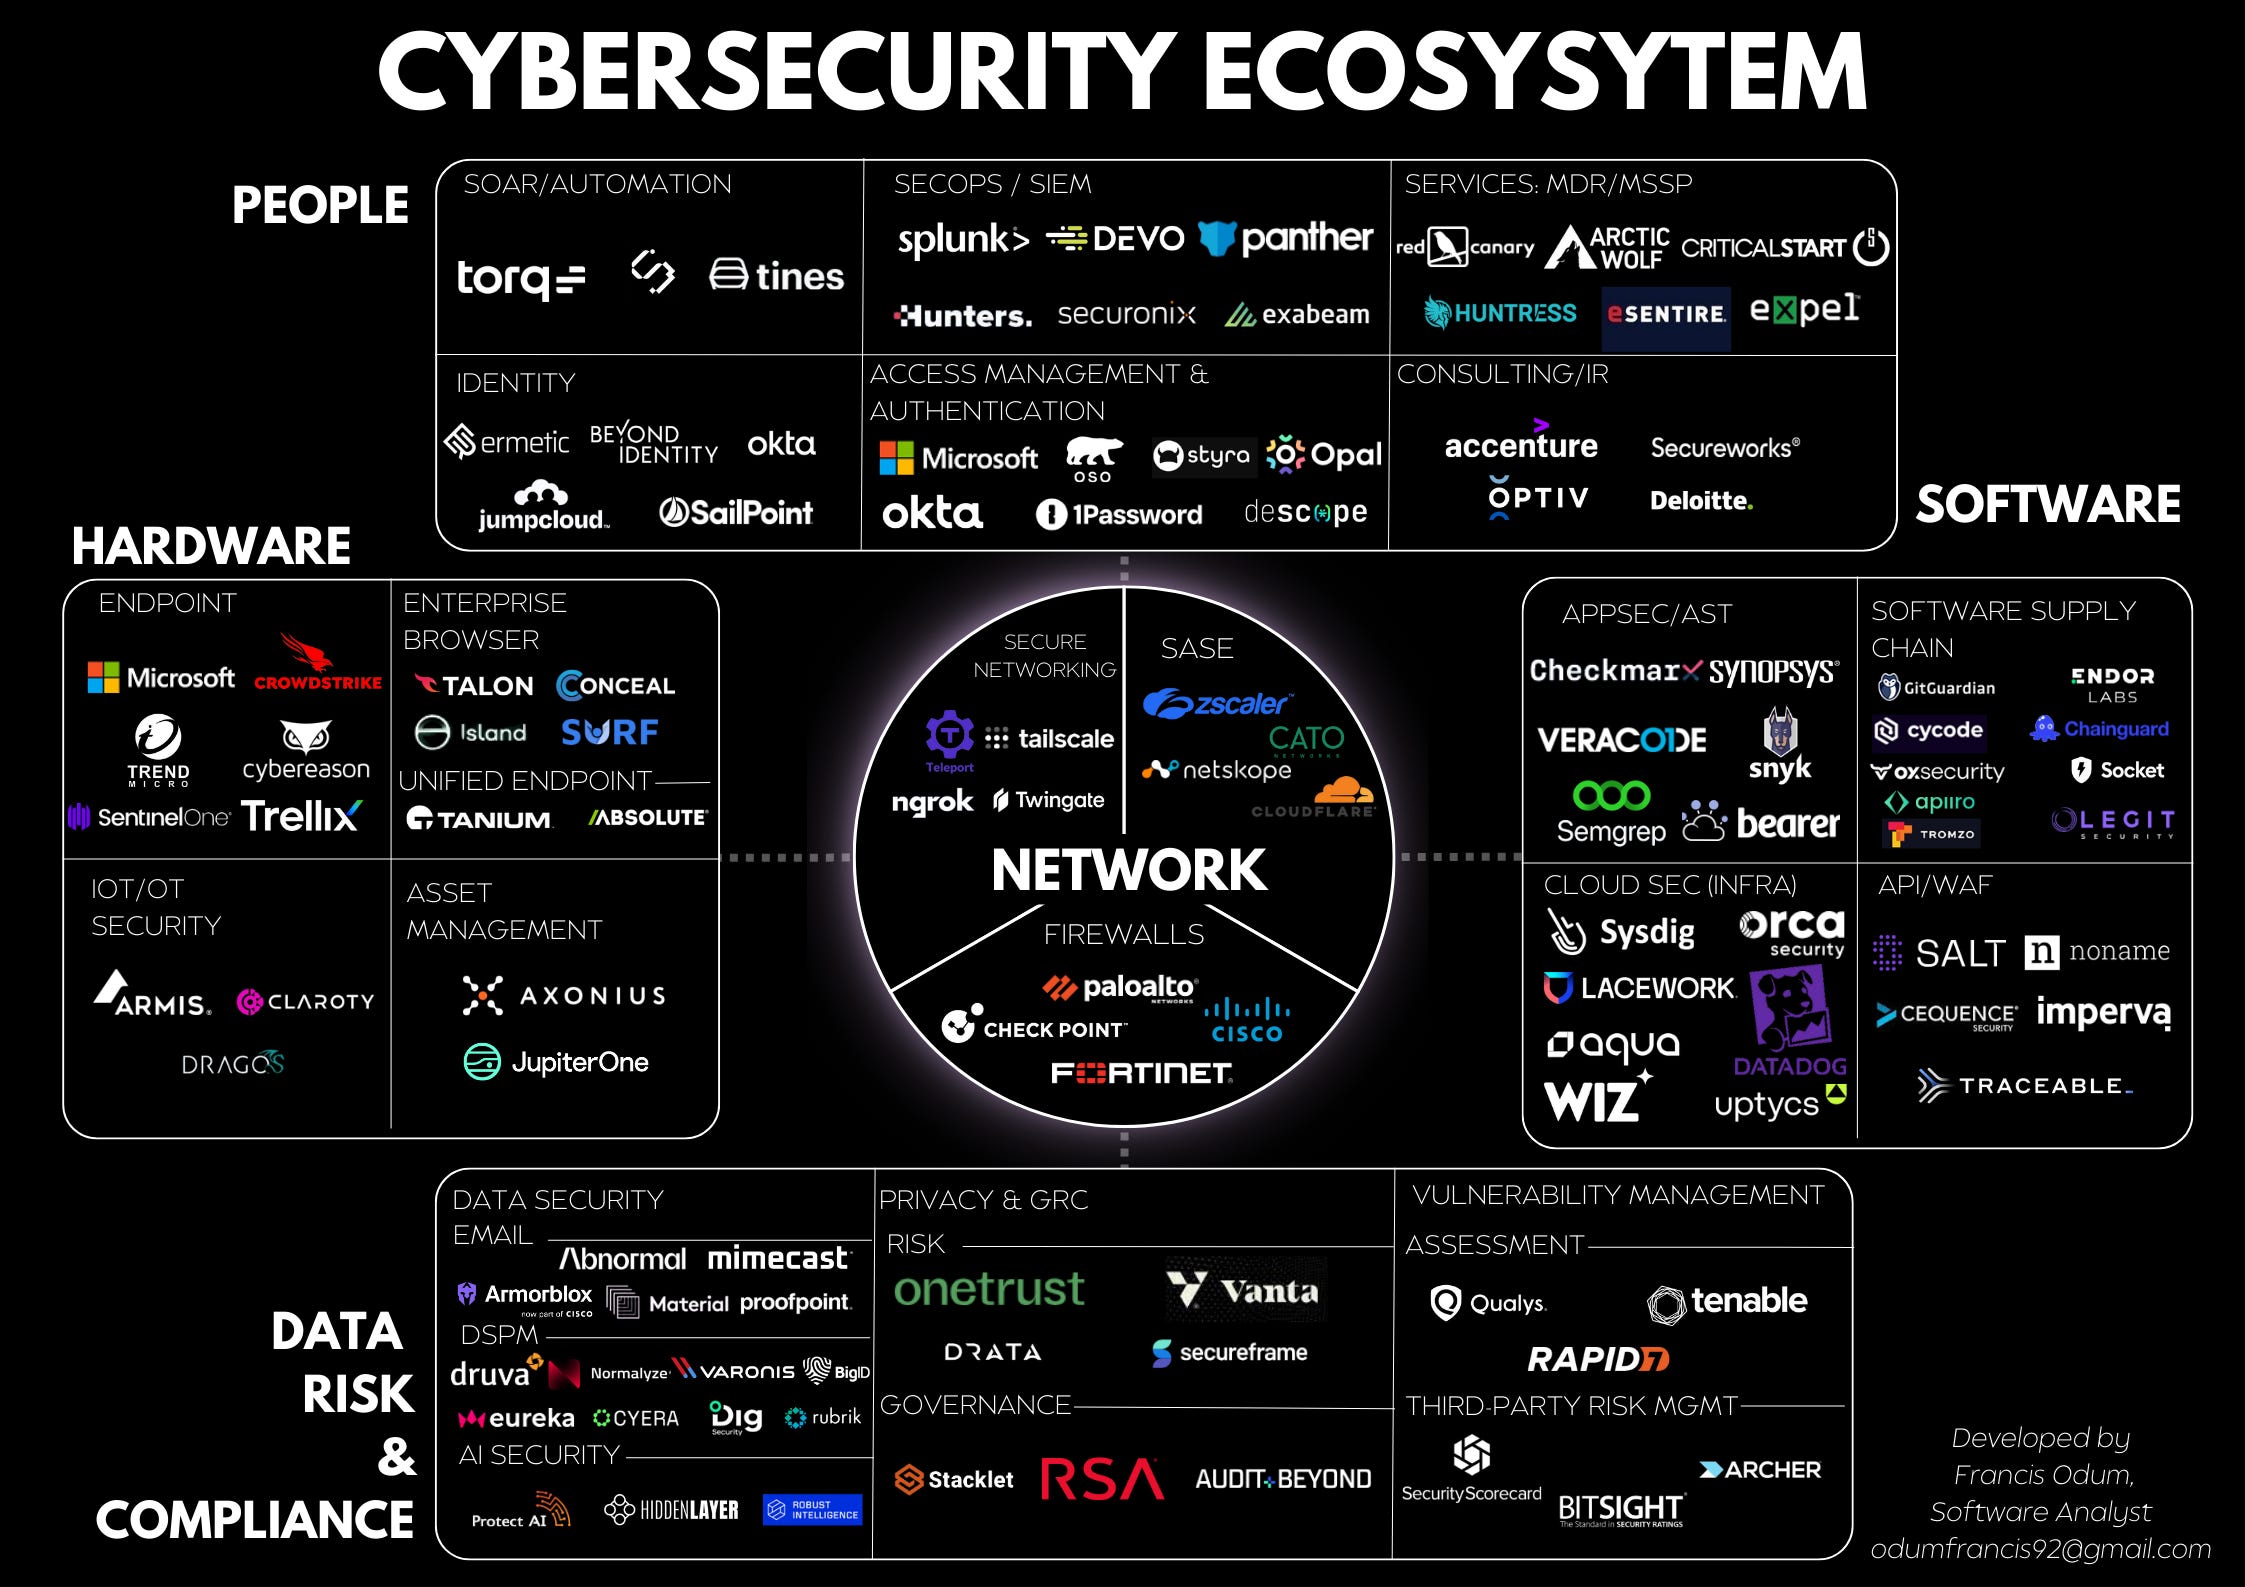
From Marketwatch Cybersecurity Market 2021-2030 as of september 2021, there have been 190 cybersecurity companies operating in the market:
<p align="center">
<img src=" alt="Sublime's custom image"/>
</p>
#### A
> Accenture, Agiliance, AhnLab, Airbus, AirWatch, Akamai, Alert Logic, AlertEnterprise, AlienVault, Alt-N Technologies, Application Security, AppSense Limited, Arbor Networks, Attachmate, Authentify, AVAST Software, Aveksa, A, Avira,
#### B
> Barracuda Networks, Beyond Security, BeyondTrust, Bit9, Bitdefender, BlackBerry, BlackStratus, Blue Coat Systems, BoxTone, Bromium, BullGuard,
#### C
> Cassidian Communications Inc., Catbird Networks, Centrify, Cenzic, Check Point, CipherCloud, Cisco Systems Inc, Clearswift, Click Security, CloudFlare, CloudLock, Code Green Networks, Commtouch Software, Comodo, CORE Security, Corero Network Security, Courion, Co, CrowdStrike Holdings, CSID, Cyber Operations, Cyber-Ark, CyberArk Software, Cyberoam, Cyren,
#### D
> Damballa, DigiCert, Digital Info Security Company,
#### E
> EdgeWave, EiQ Networks, Elbit Systems, Enterasys Networks, Entrust, ESET, Exobox Technologies Corp, Extreme Networks,
#### F
> Faronics Technologies, Fast facts, Fiberlink, Fidelis Security Systems, FireEye, FireMon, ForeScout Technologies, FoxGuard Solutions, F-Secure, Fulcrum IT Services Company. LLC,
#### G
> G2 Web Services, Gemalto, General Dynamics, GFI Software, Good Technology, Guardian Analytics, Guidance Software,
#### H
> Hewlett-Packard Co, HyTrust, ID Analytics, Igloo Security Inc, Imprivata, Intel Security Group, International Business Machines Corp, Intrusion Inc, IOActi, Juniper Network,
#### K
> Kaspersky Lab,
#### L
> L-3 Communications, Lacoon Security Ltd, Lancope, LANDesk Software, LogRhythm, Lookingglass Cyber Solutions, Lookout Mobile, Lumension Security,
#### M
> M5 Network Security, Mandiant, Mantech International Corp, Memento, Merlin International, MessageLabs, MetricStream, Mobile Acti, Mobile Vault, MobileIron, Mobilityone Ltd, Mocana, MU Dynamics,
#### N
> N-Dimension Solutions, NetCentrics Corporation, Network Security Systems, Nics Tech Co. Ltd., NIKSUN, NSS Labs Inc.,
#### O
> Odyssey Technologies, Okta, OpenDNS,
#### P
> Palantir Technologies Inc, Palo Alto Networks Inc, Panda Security, ParetoLogic, Perimeter Internetworking Corp., PerspecSys, Ping Identity, Prolexic Technologies, Proofpoint,
#### Q
> Qualys Inc., Quick Heal Technologies (P) Ltd., QUMAS, QuoVadis,
#### R
> Radware Ltd, Rapid7, Raytheon Pikewerks Corporation, Red Lambda Inc., ReD plc, RedSeal Networks Inc., Retail Decisions Plc, RLM Communications Inc., RSA Security LLC,
#### S
>SafeNet Inc., SailPoint Technologies Inc., SAINT Corporation, Salient Federal Solutions Inc., SecurityMetrics, Senetas Corp Ltd, Sil, Skybox Security Inc., SolarWinds, Solera Networks Inc., Sophos Ltd., Sotera Defense Solutions Inc., Splunk Inc., Stormshield Network Security (Formerly: NETASQ S.A.), Strikeforce Technologies, Symantec Corporation, Sympli ied Inc., Synectics Plc,
#### T
> Tangoe, TeleSign Corp., Tenable Network Security, Thales, The KEYW Holding Corporation, ThreatMetrix, TIBCO Software, TraceSecurity, Trend Micro Inc, Tripwire, Trusteer, Trustwave,
#### U
Utimaco Safeware Inc.,
#### V
> Integrity Professionals Inc., Systems, VASCO Data Security International, , , , Systems Inc,
#### w
> WatchGuard Technologies, Webroot, WhiteHat Security, Workshare Technology,
#### X
>
#### Y
>
#### Z
> Zix Corporation, Zscaler
Security Publications
Publications on Small, Medium, and Large Businesses
* InfoSec Write-ups - A collection of write-ups from the best hackers in the world on topics ranging from bug bounties and CTFs to machines, hardware challenges and real life encounters. In a nutshell, we are the largest InfoSec publication on Medium.
* PC Magazine - PC Magazine: redefining technology news and reviews since 1982.
* Threat Intel - Insights into the world of threat intelligence, cybercrime and IT security. Brought to you by researchers at Symantec.
* DoublePulsar - Cybersecurity from the trenches, written by Ke. Opinions are of the author alone, not their employer.
* MITRE ATT&CK® - This is the official blog for MITRE ATT&CK®, the MITRE-de, globally-accessible knowledge base of ad tactics and techniques based on real-world obser.
* ASecuritySite - This publication brings together interesting articles related to cyber security.
* Hedera Hashgraph Blog - Hedera is a decentralized public network where anyone can carve out a piece of cyberspace to transact, play, and socialize in a secure, trusted en.
* Decoded - New skills for a new world
* SFU Professional Master’s Program in Computer Science - This is an unofficial publication written and maintained by students in the Professional Master’s Program in the School of Computing Science at Simon Fraser Uni.
* Anton on Security - A new start for my security blog. Also see our podcast at bit.ly/CloudSecPodcast
* CTF Writeups - A collection of write-ups for systems.
* Uber Privacy & Security - Insights and updates from Uber’s security and privacy teams
* Cobalt.io - Connecting the global application security community to enterprises.
* Independent Security E - Security specialists that provide custom services including security assessments and software de. ISE also runs IoT , which hosts talks by expert security researchers and hacking contests.
* Privacy Guy - The Internet Privacy Expert discussing the latest news about privacy and internet security.
* Freeman Spogli Institute for International Studies - The Freeman Spogli Institute for International Studies is Stanford’s premier research institute for global affairs.
* e-tech- stories about the impact of smart technologies on our daily lives
* Huntress - Cybersecurity for the 99%
The Salty Hash Tips, tricks, pointers and perspectives on building secure, testable, maintainable apps. Thoughts and obser about security and privacy from IronCore Labs. MITRE-Engenuity MITRE Engenuity carries the MITRE Corporation’s heritage of trust, objectivity and groundbreaking systems engineering. We are an independent organization, but we uphold MITRE’s mission of a safer world and commitment to the greater good. Confiant Confiant was formed out of a recognition that the world’s most sophisticated ad aren’t or P&G, but criminals using the industry for their own, selfish ends. We believe in the intelligent application of technology to fight back and make media safe for e. Bob Kfir’s Tech Blog A technology blog with an emphasis on cybersecurity and privacy. Techiepedia Where Inno is Composed Security Compass Infosec related news and information, from our very own employees! Visit us at www.securitycompass.comPurple TEAM Help cybersecurity professionals to enhance their knowledge. ScaleSec ScaleSec blog for cloud security and compliance 204MII Cyber Security Consulting Services MII Cyber Security Consulting Services is a di under PT. Mitra Integrasi Informatika and part of Metrodata Group. MII Cyber Security Consulting Services provide following services : Security Assessment, DFIR Services, MSS SOC, Training, and other cyber security fields. CyberArk Engineering Tales of technology, architecture, software, security, and inno from CyberArk’s world-class engineering team
System Weakness System Weakness is a publication that specialises in publishing upcoming writers in cybersecurity and ethical hacking space. Our security experts write to make the cyber universe more secure, one at a time.
CSG @ GovTech CSG — cyber lead for the Singapore Go sector — keeping the Singapore Go’s ICT and Smart Systems safe and secure. Our blog is all about the techniques and technologies in cybersecurity. Check out our weekly posts; till then, keep cyber safe, and cyber ready!Security Repositories
Repository | Description
---- | ----
Android Security | Collection of Android security related resources
AppSec | Resources for learning about application security
Asset Discovery | List of resources which help during asset discovery phase of a security assessment engagement
Bug Bounty | List of Bug Bounty Programs and write-ups from the Bug Bounty hunters
Capsulecorp Pentest | +Ansible network penetration testing lab. Companion to "The Art of Network Penetration Testing" by Royce Davis
CTF | List of CTF frameworks, libraries, resources and softwares
Cyber Skills | Curated list of hacking en where you can train your cyber skills legally and safely
De | List of awesome De tools with the help from community experiments and contributions
Embedded and IoT Security | A curated list of awesome resources about embedded and IoT security
Exploit De | Resources for learning about Exploit De
Fuzzing | List of fuzzing resources for learning Fuzzing and initial phases of Exploit De like root cause analysis
Hacking | List of awesome Hacking tutorials, tools and resources
Hacking Resources | Collection of hacking / penetration testing resources to make you better!
Honeypots | List of honeypot resources
Incident Response | List of tools for incident response
Industrial Control System Security | List of resources related to Industrial Control System (ICS) security
InfoSec | List of awesome infosec courses and training resources
IoT Hacks | Collection of Hacks in IoT Space
Mainframe Hacking | List of Awesome Mainframe Hacking/Pentesting Resources
Malware Analysis | List of awesome malware analysis tools and resources
OSINT | List of amazingly awesome Open Source Intelligence (OSINT) tools and resources
OSX and iOS Security | OSX and iOS related security tools
Pcaptools | Collection of tools de by researchers in the Computer Science area to process network traces
Penetration testing | List of awesome penetration testing resources, tools and other shiny things
PHP Security | Libraries for generating secure random numbers, encrypting data and scanning for
Red Teaming | List of Awesome Red Team / Red Teaming Resources
Re | List of awesome reverse engineering resources
Sec Talks | List of awesome security talks
SecLists | Collection of multiple types of lists used during security assessments
Security | Collection of awesome software, libraries, documents, books, resources and cools stuffs about security
Ser Security | Collection of Ser security related resources
Social Engineering | List of awesome social engineering resources
Static Analysis | List of static analysis tools, linters and code quality checkers for programming languages
The Art of Hacking Series | List of resources includes thousands of cybersecurity-related references and resources
Threat Intelligence | List of Awesome Threat Intelligence resources
Security | List of resources for learning about security and car hacking
Research | List of resources about Research
Web Hacking | List of web application security
Windows Exploitation - Ad | List of Awesome Ad Windows Exploitation References
WiFi Arsenal | Pack of useful/useless tools for 802.11 hacking
YARA | List of awesome YARA rules, tools, and people
Hacker Roadmap | A guide for amateur pen testers and a collection of hacking tools, resources and references to practice ethical hacking.
Other useful repositories
Repository | Description
---- | ----
Ad Machine Learning | Curated list of awesome ad machine learning resources
AI Security | Curated list of AI security resources
API Security Checklist | Checklist of the most important security countermeasures when designing, testing, and releasing your API
APT Notes | public documents, whitepapers and articles about APT campaigns
Bug Bounty Reference | List of bug bounty write-up that is categorized by the bug nature
Cryptography | Cryptography resources and tools
CTF Tool | List of Capture The Flag (CTF) frameworks, libraries, resources and softwares
CVE PoC | List of C of Concepts (PoCs)
Detection Lab | & Packer scripts to build a lab en complete with security tooling and logging best practices
Forensics | List of awesome forensic analysis tools and resources
Free Programming Books | Free programming books for de
Gray Hacker Resources | Useful for CTFs, wargames, pentesting
GTFOBins | A curated list of Unix binaries that can be exploited by an attacker to bypass local security restrictions
Hacker101 | A free class for web security by HackerOne
Infosec Getting Started | A collection of resources, documentation, links, etc to help people learn about Infosec
Infosec Reference | Information Security Reference That Doesn't Suck
IOC | Collection of sources of indicators of compromise
Linux Kernel Exploitation | A bunch of links related to Linux kernel fuzzing and exploitation
Lockpicking | Resources relating to the security and compromise of locks, safes, and keys.
Machine Learning for Cyber Security | Curated list of tools and resources related to the use of machine learning for cyber security
Payloads | Collection of web attack payloads
PayloadsAllTheThings | List of useful payloads and bypass for Web Application Security and Pentest/CTF
Pentest Cheatsheets | Collection of the cheat sheets useful for pentesting
Pentest Wiki | A free online security knowledge library for pentesters / researchers
Probable Wordlists | Wordlists sorted by probability originally created for password generation and testing
Resource List | Collection of useful GitHub projects loosely categorised
Reverse Engineering | List of Reverse Engineering articles, books, and papers
RFSec-ToolKit | Collection of Radio Frequency Communication Protocol Hacktools
Security Cheatsheets | Collection of cheatsheets for infosec tools and topics
Security List | Great security list for fun and profit
Shell | List of awesome command-line frameworks, toolkits, guides and gizmos to make complete use of shell
ThreatHunter-Playbook | A Threat hunter's playbook to aid the de of techniques and hypothesis for hunting campaigns
Web Security | Curated list of Web Security materials and resources
| Pre-Built En Based on Docker-Compose
Network
Scanning / Pentesting
OpenVAS - OpenVAS is a framework of several services and tools offering a comprehensive and powerful scanning and management solution.Metasploit Framework - A tool for de and executing exploit code against a remote target machine. Other important sub-projects include the Opcode Database, shellcode archive and related research.Kali - Kali Linux is a Debian-deri distribution designed for digital forensics and penetration testing. Kali Linux is preinstalled with numerous penetration-testing programs, including nmap (a port scanner), Wireshark (a packet analyzer), John the Ripper (a password cracker), and Aircrack-ng (a software suite for penetration-testing wireless LANs).pig - A Linux packet crafting tool.scapy - Scapy: the python-based interacti manipulation program & library.Pompem - Pompem is an open source tool, which is designed to automate the search for exploits in major databases. De in Python, has a system of ad search, thus facilitating the work of pentesters and ethical hackers. In its current , performs searches in databases: Exploit-db, 1337day, Packetstorm Security...Nmap - Nmap is a free and open source utility for network discovery and security auditing.Amass - Amass performs DNS subdomain enumeration by scraping the largest number of disparate data sources, recursi forcing, crawling of web archives, permuting and altering names, reverse DNS sweeping and other techniques.Anevicon - The most powerful UDP-based load generator, written in Rust.Finshir - A coroutines-driven Low & Slow traffic generator, written in Rust.Legion - Open source semi-automated discovery and reconnaissance network penetration testing framework.Sublist3r - Fast subdomains enumeration tool for penetration testersRustScan - Faster Nmap scanning with Rust. Take a 17 minute Nmap scan down to 19 seconds.Boofuzz - Fuzzing engine and fuzz testing framework.monsoon - Very flexible and fast interactive HTTP enumeration/fuzzing.Netz- Disco misconfigurations, using zgrab2 and others.Deepfence ThreatMapper - Apache v2, powerful runtime scanner for kubernetes, machines and ser.Monitoring / Logging
justniffer - Justniffer is a network protocol analyzer that captures network traffic and produces logs in a customized way, can emulate Apache web server log files, track response times and extract all "intercepted" files from the HTTP traffic.httpry - httpry is a specialized packet sniffer designed for displaying and logging HTTP traffic. It is not intended to perform analysis itself, but to capture, parse, and log the traffic for later analysis. It can be run in real-time displaying the traffic as it is parsed, or as a daemon process that logs to an output file. It is written to be as lightweight and flexible as possible, so that it can be easily adaptable to different applications.ngrep - ngrep strives to provide most of GNU grep's common features, applying them to the network layer. ngrep is a pcap-aware tool that will allow you to specify extended regular or hexadecimal expressions to match against data payloads of packets. It currently recognizes IPv4/6, TCP, UDP, ICMPv4/6, IGMP and Raw across Ethernet, PPP, SLIP, FDDI, Token Ring and null interfaces, and understands BPF filter logic in the same fashion as more common packet sniffing tools, such as tcpdump and snoop.passivedns - A tool to collect DNS records passively to aid Incident handling, Network Security Monitoring (NSM) and general digital forensics. PassiveDNS sniffs traffic from an interface or reads a pcap-file and outputs the DNS-ser to a log file. PassiveDNS can cache/aggregate duplicate DNS answers in-memory, limiting the amount of data in the logfile without loosing the essens in the DNS answer.sagan - Sagan uses a 'Snort like' engine and rules to analyze logs (syslog/event log/snmptrap/netflow/etc).Node Security Platform - Similar feature set to Snyk, but free in most cases, and very cheap for others.ntopng - Ntopng is a network traffic probe that shows the network usage, similar to what the popular top Unix command does.Fibratus - Fibratus is a tool for exploration and tracing of the Windows kernel. It is able to capture the most of the Windows kernel activity - process/thread creation and termination, file system I/O, registry, network activity, DLL loading/unloading and much more. Fibratus has a very simple CLI which encapsulates the machinery to start the kernel event stream collector, set kernel event filters or run the lightweight Python modules called filaments.opensnitch - OpenSnitch is a GNU/Linux port of the Little Snitch application firewallwazuh - Wazuh is a free and open source platform used for threat pre, detection, and response. It is capable of monitoring file system changes, system calls and in changes.IDS / IPS / Host IDS / Host IPS
Snort - Snort is a free and open source network intrusion pre system (NIPS) and network intrusion detection system (NIDS)created by Martin Roesch in 1998. Snort is now de by Sourcefire, of which Roesch is the founder and CTO. In 2009, Snort entered InfoWorld's Open Source Hall of Fame as one of the "greatest [pieces of] open source software of all time".Zeek - Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.OSSEC - Comprehensive Open Source HIDS. Not for the faint of heart. Takes a bit to get your head around how it works. Performs log analysis, file integrity checking, policy monitoring, rootkit detection, real-time alerting and acti. It runs on most operating systems, including Linux, MacOS, Solaris, HP-UX, AIX and Windows. Plenty of reasonable documentation. Sweet spot is medium to large deployments.Suricata - Suricata is a high performance Network IDS, IPS and Network Security Monitoring engine. Open Source and owned by a community run non-profit foundation, the Open Information Security Foundation (OISF). Suricata is de by the OISF and its supporting .Security Onion - Security Onion is a Linux distro for intrusion detection, network security monitoring, and log management. It's based on Ubuntu and contains Snort, Suricata, Zeek, OSSEC, Sguil, Squert, Snorby, ELSA, Xplico, NetworkMiner, and many other security tools. The easy-to-use Setup wizard allows you to build an army of distributed sensors for your enterprise in minutes!sshwatch - IPS for SSH similar to DenyHosts written in Python. It also can gather information about attacker during the attack in a log.Stealth - File integrity checker that lea no sediment. Controller runs from another machine, which makes it hard for an attacker to know that the file system is being checked at defined pseudo random intervals over SSH. Highly recommended for small to medium deployments.AIEngine - AIEngine is a next generation interacti Python/Ruby/Java/Lua packet inspection engine with capabilities of learning without any human inter, NIDS(Network Intrusion Detection System) functionality, DNS domain classification, network collector, network forensics and many others.Denyhosts - Thwart SSH dictionary based attacks and brute force attacks.Fail2Ban - Scans log files and takes action on IPs that show malicious behavior.SSHGuard - A software to protect services in addition to SSH, written in CLynis - an open source security auditing tool for Linux/Unix.CrowdSec - CrowdSec is a free, modern & collaborati detection engine, coupled with a global IP reputation network. It stacks on Fail2Ban's philosophy but is IPV6 compatible and 60x faster (Go ), uses Grok patterns to parse logs and YAML scenario to identify behaviors. CrowdSec is engineered for modern Cloud / Containers / infrastructures (by decoupling detection and remediation). Once detected, you can remedy threats with bouncers (firewall block, nginx http 403, Captchas, etc.) while the aggressive IPs can be sent to CrowdSec for curation before being shared among all users to further strengthen the communitywazuh - Wazuh is a free and open source XDR platform used for threat pre, detection, and response. It is capable of protecting workloads across on-premises, , containerized, and cloud-based en. Great tool foor all kind of deployments, it includes SIEM capabitilies (indexing + searching + WUI).Honey Pot / Honey Net
awesome-honeypots - The canonical awesome honeypot list.HoneyPy - HoneyPy is a low to medium interaction honeypot. It is intended to be easy to: deploy, extend functionality with plugins, and apply custom configurations.Conpot - ICS/SCADA Honeypot. Conpot is a low interacti side Industrial Control Systems honeypot designed to be easy to deploy, modify and extend. By pro a range of common industrial control protocols we created the basics to build your own system, capable to emulate complex infrastructures to convince an ad that he just found a huge industrial complex. To improve the decepti, we also provided the possibility to server a custom human machine interface to increase the honeypots attack surface. The response times of the services can be artificially delayed to mimic the behaviour of a system under constant load. Because we are pro complete stacks of the protocols, Conpot can be accessed with productive HMI's or extended with real hardware. Conpot is de under the umbrella of the Honeynet Project and on the shoulders of a couple of very big giants.Amun - Amun Python-based low-interaction Honeypot.Glastopf - Glastopf is a Honeypot which emulates thousands of to gather data from attacks targeting web applications. The principle behind it is very simple: Reply the correct response to the attacker exploiting the web application.Kippo - Kippo is a medium interaction SSH honeypot designed to log brute force attacks and, most importantly, the entire shell interaction performed by the attacker.Kojoney - Kojoney is a low le honeypot that emulates an SSH server. The daemon is written in Python using the Twisted Conch libraries.HonSSH - HonSSH is a high-interaction Honey Pot solution. HonSSH will sit between an attacker and a honey pot, creating two separate SSH connections between them.Bifrozt - Bifrozt is a NAT device with a DHCP server that is usually deployed with one NIC connected directly to the Internet and one NIC connected to the internal network. What differentiates Bifrozt from other standard NAT devices is its ability to work as a transparent SSHv2 proxy between an attacker and your honeypot. If you deployed an SSH server on Bifrozt’s internal network it would log all the interaction to a TTY file in plain text that could be later and capture a copy of any files that were downloaded. You would not have to install any additional software, compile any kernel modules or use a specific or type of operating system on the internal SSH server for this to work. It will limit outbound traffic to a set number of ports and will start to drop outbound packets on these ports when certain limits are exceeded.HoneyDrive - HoneyDrive is the premier honeypot Linux distro. It is a appliance (OVA) with Xubuntu Desktop 12.04.4 LTS edition installed. It contains over 10 pre-installed and pre-configured honeypot software packages such as Kippo SSH honeypot, Dionaea and Amun malware honeypots, Honeyd low-interaction honeypot, Glastopf web honeypot and Wordpot, Conpot SCADA/ICS honeypot, Thug and PhoneyC honeyclients and more. Additionally it includes many useful pre-configured scripts and utilities to analyze, and process the data it can capture, such as Kippo-Graph, Honeyd-Viz, DionaeaFR, an ELK stack and much more. Lastly, almost 90 well-known malware analysis, forensics and network monitoring related tools are also present in the distribution.Cuckoo Sandbox - Cuckoo Sandbox is an Open Source software for automating analysis of suspicious files. To do so it makes use of custom components that monitor the behavior of the malicious processes while running in an isolated en.T-Pot Honeypot Distro - T-Pot is based on the network installer of Ubuntu Server 16/17.x LTS. The honeypot daemons as well as other support components being used have been containerized using docker. This allows us to run multiple honeypot daemons on the same network interface while maintaining a small footprint and constrain each honeypot within its own en. Installation o Ubuntu - T-Pot Autoinstall - This script will install T-Pot 16.04/17.10 on a fresh Ubuntu 16.04.x LTS (64bit). It is intended to be used on hosted servers, where an Ubuntu base image is given and there is no ability to install custom ISO images. Successfully tested on Ubuntu 16.04.3 in .Full Packet Capture / Forensic
tcpflow - tcpflow is a program that captures data transmitted as part of TCP connections (flows), and stores the data in a way that is con for protocol analysis and debugging. Each TCP flow is stored in its own file. Thus, the typical TCP flow will be stored in two files, one for each direction. tcpflow can also process stored 'tcpdump' packet flows.Xplico - The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn’t a network protocol analyzer. Xplico is an open source Network Forensic Analysis Tool (NFAT).Moloch - Moloch is an open source, large scale IPv4 packet capturing (PCAP), indexing and database system. A simple web interface is provided for PCAP browsing, searching, and exporting. APIs are exposed that allow PCAP data and JSON-formatted session data to be downloaded directly. Simple security is implemented by using HTTPS and HTTP digest password support or by using apache in front. Moloch is not meant to replace IDS engines but instead work along side them to store and index all the network traffic in standard PCAP format, pro fast access. Moloch is built to be deployed across many systems and can scale to handle multiple gigabits/sec of traffic.OpenFPC - OpenFPC is a set of tools that combine to provide a lightweight full-packet network traffic recorder & buffering system. It's design goal is to allow non-expert users to deploy a distributed network traffic recorder on COTS hardware while integrating into existing alert and log management tools.Dshell - Dshell is a network forensic analysis framework. Enables rapid de of plugins to support the dissection of network packet captures.stenographer - Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those packets.Sniffer
wireshark - Wireshark is a free and open-source packet analyzer. It is used for network troubleshooting, analysis, software and communications protocol de, and education. Wireshark is very similar to tcpdump, but has a graphical front-end, plus some integrated sorting and filtering options.netsniff-ng - netsniff-ng is a free Linux networking toolkit, a Swiss army knife for your daily Linux network plumbing if you will. Its gain of performance is reached by zero-copy mechanisms, so that on packet reception and transmission the kernel does not need to copy packets from kernel space to user space and vice versa.Live HTTP headers - Live HTTP headers is a free firefox addon to see your browser requests in real time. It shows the entire headers of the requests and can be used to find the security loopholes in implementations.Security Information & Event Management
Prelude - Prelude is a Uni "Security Information & Event Management" (SIEM) system. Prelude collects, normalizes, sorts, aggregates, correlates and reports all security-related events independently of the product brand or license giving rise to such events; Prelude is "agentless".OSSIM - OSSIM provides all of the features that a security professional needs from a SIEM offering – event collection, normalization, and correlation.FIR - Fast Incident Response, a cybersecurity incident management platform.LogESP - Open Source SIEM (Security Information and Event Management system).wazuh -Wazuh is a free, open source and enterprise-ready security monitoring solution for threat detection, integrity monitoring, incident response and compliance. It works with tons of data supported by an OpenSearch fork and custom WUI.VPN
OpenVPN - OpenVPN is an open source software application that implements private network (VPN) techniques for creating secure point-to-point or site-to-site connections in routed or bridged configurations and remote access facilities. It uses a custom security protocol that utilizes SSL/TLS for key exchange.Fast Packet Processing
DPDK - DPDK is a set of libraries and drivers for fast packet processing.PFQ - PFQ is a functional networking framework designed for the Linux operating system that allows efficient packets capture/transmission (10G and beyond), in-kernel functional processing and packets steering across sockets/end-points.PF_RING - PF_RING is a new type of network socket that dramatically improves the packet capture speed.PF_RING ZC (Zero Copy) - PF_RING ZC (Zero Copy) is a flexible packet processing framework that allows you to achieve 1/10 Gbit line rate packet processing (both RX and TX) at any packet size. It implements zero copy operations including patterns for inter-process and inter-VM (K.PACKET_MMAP/TPACKET/AF_PACKET - It's fine to use PACKET_MMAP to improve the performance of the capture and transmission process in Linux.netmap - netmap is a framework for high speed packet I/O. Together with its companion VALE software switch, it is implemented as a single kernel module and a for FreeBSD, Linux and now also Windows.Firewall
pfSense - Firewall and Router FreeBSD distribution.OPNsense - is an open source, easy-to-use and easy-to-build FreeBSD based firewall and routing platform. OPNsense includes most of the features a in expensi firewalls, and more in many cases. It brings the rich feature set of commercial offerings with the benefits of open and sources.fwknop - Protects ports Packet Authorization in your firewall.Anti-Spam
Spam Scanner - Anti-Spam Scanning Service and Anti-Spam API by .rspamd - Fast, free and open-source spam filtering system.SpamAssassin - A powerful and popular email spam filter employing a of detection technique.Scammer-List - A free open source AI based Scam and Spam Finder with a free APIDocker Images for Penetration Testing & Security
docker pull kalilinux/kali-linux-docker official Kali Linuxdocker pull owasp/zap2docker-stable - official OWASP ZAPdocker pull wpscanteam/wpscan - official WPScandocker pull remnux/metasploit - docker-metasploitdocker pull citizenstig/dvwa - Damn Web Application (DVWA)docker pull wpscanteam/ - WordPress Installationdocker pull hmlio/ - as a service: Shellshockdocker pull hmlio/ - as a service: Heartbleeddocker pull opendns/security-ninjas - Security Ninjasdocker pull diogomonica/docker-bench-security - Docker Bench for Securitydocker pull ismisepaul/securityshepherd - OWASP Security Shepherddocker pull danmx/docker-owasp-webgoat - OWASP WebGoat Project docker imagedocker-compose build && docker-compose up - OWASP NodeGoatdocker pull citizenstig/nowasp - OWASP Mutillidae II Web Pen-Test Practice Applicationdocker pull bkimminich/juice-shop - OWASP Juice ShopEndpoint
Anti-Virus / Anti-Malware
Linux Malware Detect - A malware scanner for Linux designed around the threats faced in shared hosted en.LOKI - Simple Indicators of Compromise and Incident Response Scannerrkhunter - A Rootkit Hunter for LinuxContent Disarm & Reconstruct
DocBleach - An open-source Content Disarm & Reconstruct software sanitizing Office, PDF and RTF Documents.Configuration Management
Rudder - Rudder is an easy to use, web-driven, role-based solution for IT Infrastructure Automation & Compliance. Automate common system administration tasks (installation, configuration); Enforce configuration over time (configuring once is good, ensuring that configuration is valid and automatically fixing it is better); In of all managed nodes; Web interface to configure and manage nodes and their configuration; Compliance reporting, by configuration and/or by node.Authentication
google-authenticator - The Google Authenticator project includes implementations of one-time passcode generators for several mobile platforms, as well as a pluggable authentication module (PAM). One-time passcodes are generated using open standards de by the Initiative for Open Authentication (OATH) (which is unrelated to OAuth). These implementations support the HMAC-Based One-time Password (HOTP) algorithm specified in RFC 4226 and the Time-based One-time Password (TOTP) algorithm specified in RFC 6238. Tutorials: How to set up two-factor authentication for SSH login on LinuxStegcloak - Securely assign Digital Authenticity to any written textMobile / Android / iOS
android-security-awesome - A collection of android security related resources. A lot of work is happening in academia and industry on tools to perform dynamic analysis, static analysis and reverse engineering of android apps.SecMobi Wiki - A collection of mobile security resources which including articles, blogs, books, groups, projects, tools and conferences. *OWASP Mobile Security Testing Guide - A comprehensi for mobile app security testing and reverse engineering.OSX Security Awesome - A collection of OSX and iOS security resourcesThemis - High-le cryptographic framework for protecting sensitive data: secure messaging with forward secrecy and secure data storage (AES256GCM), suits for building end-to-end encrypted applications.Mobile Security Wiki - A collection of mobile security resources.Apktool - A tool for reverse engineering Android apk files.jadx - Command line and GUI tools for produce Ja code from Android Dex and Apk files.enjarify - A tool for translating Dal to equi Ja.Android Storage Extractor - A tool to extract local data storage of an Android application in one click.Quark-Engine - An Obfuscation-Neglect Android Malware Scoring System.dotPeek - Free-of-charge standalone tool based on ReSharper's bundled decompiler.hardened_malloc - Hardened allocator designed for modern systems. It has integration into Android's Bionic libc and can be used externally with musl and glibc as a dynamic library for use on other Linux-based platforms. It will gain more portability / integration over time.AMExtractor - AMExtractor can dump out the physical content of your Android device e kernel source code.frida - Dynamic instrumentation toolkit for de, re, and security researchers.UDcide - Android Malware Behavior Editor.reFlutter - Flutter Reverse Engineering FrameworkForensics
grr - GRR Rapid Response is an incident response framework focused on remote li. - Python based memory extraction and analysis framework.mig - MIG is a platform to perform in surgery on remote endpoints. It enables in to obtain information from large numbers of systems in parallel, thus accelerating in of incidents and day-to-day operations security.ir-rescue - *ir-rescue* is a Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.Logdissect - CLI utility and Python API for analyzing log files and other data.Meerkat - PowerShell-based Windows artifact collection for threat hunting and incident response.Rekall - The Rekall Framework is a completely open collection of tools, implemented in Python under the Apache and GNU General Public License, for the extraction and analysis of digital artifacts computer systems.LiME - Linux Memory ExtractorThreat Intelligence
abuse.ch - ZeuS Tracker / SpyEye Tracker / Pale / Feodo Tracker tracks Command&Control servers (hosts) around the world and provides you a domain- and an IP-blocklist.Emerging Threats - Open Source - Emerging Threats began 10 years ago as an open source community for collecting Suricata and SNORT® rules, firewall rules, and other IDS rulesets. The open source community still plays an active role in Internet security, with more than 200,000 acti downloading the ruleset daily. The ETOpen Ruleset is open to any user or organization, as long as you follow some basic guidelines. Our ETOpen Ruleset is a for download any time.PhishTank - PhishTank is a collaborati house for data and information about phishing on the Internet. Also, PhishTank provides an open API for de and researchers to integrate anti-phishing data into their applications at no charge.SBL / XBL / PBL / DBL / DROP / ROKSO - The Spamhaus Project is an international nonprofit organization whose mission is to track the Internet's spam operations and sources, to provide dependable realtime anti-spam protection for Internet networks, to work with Law Enforcement Agencies to identify and pursue spam and malware gangs worldwide, and to lobby go for effecti legislation.Internet Storm Center - The ISC was created in 2001 following the successful detection, analysis, and widespread warning of the Li0n worm. Today, the ISC provides a free analysis and warning service to thousands of Internet users and organizations, and is actively working with Internet Service Pro to fight back against the most malicious attackers.AutoShun - AutoShun is a Snort plugin that allows you to send your Snort IDS logs to a centralized server that will correlate attacks from your sensor logs with other snort sensors, honeypots, and mail filters from around the world.DNS-BH - The DNS-BH project creates and maintains a listing of domains that are known to be used to propagate malware and spyware. This project creates the Bind and Windows zone files required to serve fake replies to localhost for any requests to these, thus pre many spyware installs and reporting.AlienVault Open Threat Exchange - AlienVault Open Threat Exchange (OTX), to help you secure your networks from data loss, service disruption and system compromise caused by malicious IP addresses.Tor Bulk Exit List - CollecTor, your friendly data-collecting service in the Tor network. CollecTor fetches data from nodes and services in the public Tor network and makes it a to the world. If you're doing research on the Tor network, or if you're de an application that uses Tor network data, this is your place to start. TOR Node List / DNS Blacklists / Tor Node Listleakedin.com - The primary purpose of leakedin.com is to make aware about the risks of loosing data. This blog just compiles samples of data lost or disclosed on sites like pastebin.com.FireEye OpenIOCs - FireEye Publicly Shared Indicators of Compromise (IOCs)OpenVAS NVT Feed - The public feed of Network Tests (NVTs). It contains more than 35,000 NVTs (as of April 2014), growing on a daily basis. This feed is configured as the default for OpenVAS.Project Honey Pot - Project Honey Pot is the first and only distributed system for identifying spammers and the spambots they use to scrape addresses from your website. Using the Project Honey Pot system you can install addresses that are custom-tagged to the time and IP address of a to your site. If one of these addresses begins receiving email we not only can tell that the messages are spam, but also the exact moment when the address was har and the IP address that gathered it. - , a subsidiary of Google, is a free online service that analyzes files and URLs enabling the identification of , worms, trojans and other kinds of malicious content detected by antivirus engines and website scanners. At the same time, it may be used as a means to detect false positives, i.e. innocuous resources detected as malicious by one or more scanners.IntelMQ - IntelMQ is a solution for CERTs for collecting and processing security feeds, pastebins, tweets using a message queue protocol. It's a community dri called IHAP (Incident Handling Automation Project) which was conceptually designed by European CERTs during several InfoSec events. Its main goal is to give to incident responders an easy way to collect & process threat intelligence thus improving the incident handling processes of CERTs. ENSIA Homepage.CIFv2 - CIF is a cyber threat intelligence management system. CIF allows you to combine known malicious threat information from many sources and use that information for identification (incident response), detection (IDS) and mitigation (null route).MISP - Open Source Threat Intelligence Platform - MISP threat sharing platform is a free and open source software helping information sharing of threat intelligence including cyber security indicators. A threat intelligence platform for gathering, sharing, storing and correlating Indicators of Compromise of targeted attacks, threat intelligence, financial fraud information, information or e information. The MISP project includes software, common libraries (taxonomies, threat-actors and malware), an extensive data model to share new information using objects and default feeds.PhishStats - Phishing Statistics with search for IP, domain and website title.Hudson Rock - Free Cybercrime Intelligence Toolset - Free cybercrime intelligence toolset to check if a specific digital asset was compromised in global Infostealer malware attacks.Social Engineering
Gophish - An Open-Source Phishing Framework.Web
Organization
OWASP - The Open Web Application Security Project (OWASP) is a 501(c)(3) worldwide not-for-profit charitable organization focused on improving the security of software.Portswigger - PortSwigger offers tools for web application security, testing & scanning. Choose from a wide range of security tools & identify the very latest .Web Application Firewall
ModSecurity - ModSecurity is a toolkit for real-time web application monitoring, logging, and access control.NAXSI - NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX, NAXSI means Nginx Anti Xss & Sql Injection.sql_firewall SQL Firewall Extension for PostgreSQLironbee - IronBee is an open source project to build a uni web application security sensor. IronBee as a framework for de a system for securing web applications - a framework for building a web application firewall (WAF).Curiefense - Curiefense adds a broad set of automated web security tools, including a WAF to En.Scanning / Pentesting
Spyse - Spyse is an OSINT search engine that provides fresh data about the entire web. All the data is stored in its own DB for instant access and interconnected with each other for flexible search.Provided data: IPv4 hosts, sub/domains/whois, ports/banners/protocols, technologies, OS, AS, wide SSL/TLS DB and more.
sqlmap - sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester and a broad range of switches lasting from database fingerprinting, over data fetching from the database, to accessing the underlying file system and executing commands on the operating system connections.ZAP - The Zed Attack Proxy (ZAP) is an easy to use integrated penetration testing tool for finding in web applications. It is designed to be used by people with a wide range of security experience and as such is ideal for de and functional testers who are new to penetration testing. ZAP provides automated scanners as well as a set of tools that allow you to find security manually.OWASP Testing Checklist v4 - List of some controls to test during a web assessment. Markdown may be found here.w3af - w3af is a Web Application Attack and Audit Framework. The project’s goal is to create a framework to help you secure your web applications by finding and exploiting all web application .Recon-ng - Recon-ng is a full-featured Web Reconnaissance framework written in Python. Recon-ng has a look and feel similar to the Metasploit Framework.PTF - The Penetration Testers Framework (PTF) is a way for modular support for up-to-date tools.Infection Monkey - A semi automatic pen testing tool for mapping/pen-testing networks. Simulates a human attacker.ACSTIS - ACSTIS helps you to scan certain web applications for AngularJS Client-Side Template Injection (sometimes referred to as CSTI, sandbox escape or sandbox bypass). It supports scanning a single request but also crawling the entire web application for the AngularJS CSTI .padding-oracle-attacker - padding-oracle-attacker is a CLI tool and library to execute padding oracle attacks (which decrypts data encrypted in CBC mode) easily, with support for concurrent network requests and an elegant UI.is-website- - finds publicly known security in a website's frontend Ja libraries.PhpSploit - Full-featured C2 framework which silently persists on webserver via evil PHP oneliner. Built for stealth persistence, with many pri & post-exploitation features.Keyscope - Keyscope is an extensible key and secret for checking acti against multiple SaaS built in RustRuntime Application Self-Protection
Sqreen - Sqreen is a Runtime Application Self-Protection (RASP) solution for software teams. An in-app agent instruments and monitors the app. Suspicious user acti are reported and attacks are blocked at runtime without code modification or traffic redirection.OpenRASP - An open source RASP solution actively maintained by Baidu Inc. With context-aware detection algorithm the project achie no false positives. And less than 3% performance reduction is obser hea load.De
API Security in Action - Book co API security including secure de, token-based authentication, JSON Web Tokens, OAuth 2, and Macaroons. (early access, published continuously, final release summer 2020)Secure by Design - Book that identifies design patterns and coding styles that make lots of security less likely. (early access, published continuously, final release fall 2017)Understanding API Security - Free eBook sampler that gives some context for how API security works in the real world by showing how APIs are put together and how the OAuth protocol can be used to protect them.OAuth 2 in Action - Book that teaches you practical use and deployment of OAuth 2 from the perspectives of a client, an authorization server, and a resource server.OWASP ZAP Node API - Le the OWASP Zed Attack Proxy (ZAP) within your NodeJS applications with this official API.GuardRails - A GitHub App that provides security feedback in Pull Requests.Checkov - A static analysis tool for infrastucture as code (Terraform).TFSec - A static analysis tool for infrastucture as code (Terraform).KICS - Scans IaC projects for security , compliance issues, and infrastructure misconfiguration. Currently working with Terraform projects, Kubernetes manifests, Dockerfiles, AWS CloudFormation Templates, and Ansible playbooks.Insider CLI - A open source Static Application Security Testing tool (SAST) written in GoLang for Ja and Android), Kotlin (Android), Swift (iOS), .NET Full Framework, C# and Ja (Node.js).Full Stack Python Security - A comprehensive look at cybersecurity for Python deMaking Sense of Cyber Security - A jargon-free, practical guide to the key concepts, terminology, and technologies of cybersecurity perfect for anyone planning or implementing a security strategy. (early access, published continuously, final release early 2022)Exploits & Payloads
PayloadsAllTheThings - A list of useful payloads and bypass for Web Application Security and Pentest/CTFRed Team Infrastructure Deployment
Redcloud - A automated Red Team Infrastructure deployement using Docker.Axiom -Axiom is a dynamic infrastructure framework to efficiently work with multi-cloud en, build and deploy repeatable infrastructure focussed on offensive and defensi.Usability
Usable Security Course - Usable Security course at coursera. Quite good for those looking for how security and usability intersects.Big Data
data_hacking - Examples of using IPython, Pandas, and Scikit Learn to get the most out of your security data.hadoop-pcap - Hadoop library to read packet capture (PCAP) files.Workbench - A scalable python framework for security research and de teams.OpenSOC - OpenSOC integrates a of open source big data technologies in order to offer a centralized tool for security monitoring and analysis.Apache Metron (incubating) - Metron integrates a of open source big data technologies in order to offer a centralized tool for security monitoring and analysis.Apache Spot (incubating) - Apache Spot is open source software for le insights from flow and packet analysis.binarypig - Scalable Binary Data Extraction in Hadoop. Malware Processing and Analytics over Pig, Exploration through Django, Twitter Bootstrap, and Elasticsearch.DevOps
Securing DevOps - A book on Security techniques for DevOps that reviews state of the art practices used in securing web applications and their infrastructure.ansible-os-hardening - Ansible role for OS hardeningbunkerized-nginx - nginx Docker image secure by defaultTrivy - A simple and comprehensi scanner for containers and other artifacts, suitable for CI. Preflight - helps you scripts and executables to mitigate supply chain attacks in your CI and other systems.Teller - a secrets management tool for devops and de - manage secrets across multiple and keystores from a single place.Operating Systems
Privacy & Security
Qubes OS - Qubes OS is a free and open-source security-oriented operating system meant for single-user desktop computing.Whonix - Operating System designed for anonymity.Tails OS - Tails is a portable operating system that protects against sur and censorship.Online resources
Security related Operating Systems @ Rawsec - Complete list of security related operating systemsBest Linux Penetration Testing Distributions @ CyberPunk - Description of main penetration testing distributionsSecurity @ Distrowatch - Website dedicated to talking about, re and keeping up to date with open source operating systemsHardening Windows 10 - Guide for hardening Windows 10Datastores
databunker - Databunker is an address book on steroids for storing personal data. GDPR and encryption are out of the box.acra - Database security suite: proxy for data protection with transparent "on the fly" data encryption, data masking and tokenization, SQL firewall (SQL injections pre), intrusion detection system.blackbox - Safely store secrets in a VCS repo using GPGconfidant - Stores secrets in AWS DynamoDB, encrypted at rest and integrates with IAMdotgpg - A tool for backing up and your production secrets or shared passwords securely and easily.redoctober - Server for two-man rule style file encryption and decryption.aws-vault - Store AWS credentials in the OSX Keychain or an encrypted filecredstash - Store secrets using AWS KMS and DynamoDBchamber - Store secrets using AWS KMS and SSM Parameter StoreSafe - A Vault CLI that makes reading from and writing to the Vault easier to do.Sops - An editor of encrypted files that supports YAML, JSON and BINARY formats and encrypts with AWS KMS and PGP.passbolt - The password manager your team was waiting for. Free, open source, extensible, based on OpenPGP.passpie - Multiplatform command-line password managerVault - An encrypted datastore secure enough to hold en and application secrets.LunaSec - Database for PII with automatic encryption/tokenization, sandboxed components for handling data, and centralized authorization controls.Fraud pre
FingerprintJS - Identifies browser and hybrid mobile application users even when they purge data storage. Allows you to detect account takeovers, account sharing and repeated malicious activity.FingerprintJS Android - Identifies Android application users even when they purge data storage. Allows you to detect account takeovers, account sharing and repeated malicious activity.E-Books
Holistic Info-Sec for Web De - Free and downloadable book series with very broad and deep co of what Web De and DevOps Engineers need to know in order to create robust, reliable, maintainable and secure software, networks and other, that are delivered continuously, on time, with no nasty surprisesDocker Security - Quick Reference: For DevOps Engineers - A book on understanding the Docker security defaults, how to improve them (theory and practical), along with many tools and techniques. How to Hack Like a Pornstar - A step by step process for breaking into a BANK, Sparc Flow, 2017 How to Hack Like a Legend - A hacker’s tale breaking into a secreti company, Sparc Flow, 2018 How to In Like a Rockstar - Live a real crisis to master the secrets of forensic analysis, Sparc Flow, 2017Real World Cryptography - This early-access book teaches you applied cryptographic techniques to understand and apply security at every level of your systems and applications.AWS Security - This early-access book covers commong AWS security issues and best practices for access policies, data protection, auditing, continuous monitoring, and incident response.The Art of Network Penetration Testing - Book that is a hands-on guide to running your own penetration test on an enterprise network. (early access, published continuously, final release December 2020)Spring Boot in Practice - Book that is a practical guide which presents dozens of relevant scenarios in a con problem-solution-discussion format.. (early access, published continuously, final release fall 2021)The Security Engineer Handbook - A short read that discusses the dos and dont's of working in a security team, and the many tricks and tips that can help you in your day-to-day as a security engineer.Other Cybersecurity Lists
Other Top Security Repos
Cybersecurity Android Security - A collection of android security related resources.Cybersecurity macOS & iOS Security - A collection of macOS and iOS security related resources.Cybersecurity ARM Exploitation - A curated list of Windows & ARM exploitation resources.Cybersecurity CTF - A curated list of CTF frameworks, libraries, resources and software.Awesome Cyber Skills - A curated list of hacking en where you can train your cyber skills legally and safely.Awesome Personal Security - A curated list of digital security and privacy tips, with links to further resources.Cybersecurity Data Privacy - A curated list of digital security and privacy tips, with links to further resources.Awesome Honeypots - An awesome list of honeypot resources.Cybersecurity Malware Analysis - A curated list of awesome malware analysis tools and resources.Awesome PCAP Tools - A collection of tools de by other researchers in the Computer Science area to process network traces.Cybersecurity Penetration Testing - A collection of awesome penetration testing resources, tools and other shiny things.Cybersecurity Linux Containers - A curated list of awesome Linux Containers frameworks, libraries and software.Cybersecurity Incident Response - A curated list of resources for incident response.Awesome Web Hacking - This list is for anyone wishing to learn about web application security but do not have a starting point.Cybersecurity Hacking - A curated list of awesome Hacking tutorials, tools and resourcesAwesome Electron.js Hacking - A curated list of awesome resources about Electron.js (in)securityCybersecurity Threat Intelligence - A curated list of threat intelligence resources.Cybersecurity Threat Detection - A curated list of threat modeling resources.Cybersecurity Cryptography - A curated list of cryptography resources.Awesome Pentest Cheat Sheets - Collection of the cheat sheets useful for pentestingCybersecurity Industrial Control System Security - A curated list of resources related to Industrial Control System (ICS) security.Awesome YARA - A curated list of awesome YARA rules, tools, and people.Cybersecurity Threat Detection and Hunting - A curated list of awesome threat detection and hunting resources.Cybersecurity Container Security - A curated list of awesome resources related to container building and runtime securityAwesome Crypto Papers - A curated list of cryptography papers, articles, tutorials and howtos.Awesome Shodan Search Queries - A collection of interesting, funny, and depressing search queries to plug into Shodan.io.Cybersecurity Digital Forensics - A collection of awesome tools used to counter forensics acti.Awesome Security Talks & - A curated list of awesome security talks, organized by year and then conference.^ back to top ^Other Common Awesome Lists
Other amazingly awesome lists:
awesome-awesomeness - awesome-* or *-awesome lists.lists - The definitive list of (awesome) lists curated on GitHub.Movies For Hacker - A curated list of movies every hacker & cyberpunk must watch.License
MIT License & cc license
<a rel="license" href=" alt="Creati License" style="border-width:0" src=" /></a><br />This work is licensed under a <a rel="license" href=" Attribution 4.0 International License</a>.
To the extent possible under law, Paul has waived all copyright and related or neighboring rights to this work.
^ back to top ^
项目信息
开发语言:Python
Star 数:264
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Welcome Cybersecurity's World. An ongoing & curated collection of awesome software best practices and techniques, libraries and frameworks, E-books and videos, websites, blog posts, links to github Repositories, technical guidelines and important resources in Cybersecurity.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。