 防护思路
点击放大
Blackbird - Powerful Kernel Malware Investigation Platform | S
项目说明
<h1 align="center">BLACKBIRD</h1>
<p align="center"><b>A powerful, instrumentable, real-time malware analysis platform, software re suite & IDS.</b></p>
<p align="center">
<a href="
<img src=" />
</a>
<a href="
<img src=" />
</a>
<a href="
<img src=" />
</a>
<img src=" />
<img src=" />
<img src=" />
<img src=" />
</p>
<h2 align="center">ROADMAP</h2>
<p align="center">
<strong>Current:</strong> Community Preview Beta 2.0<br>
<strong>Next public release:</strong> <italic>Early September 2026<italic><br><br>
</p>
<p align="center">
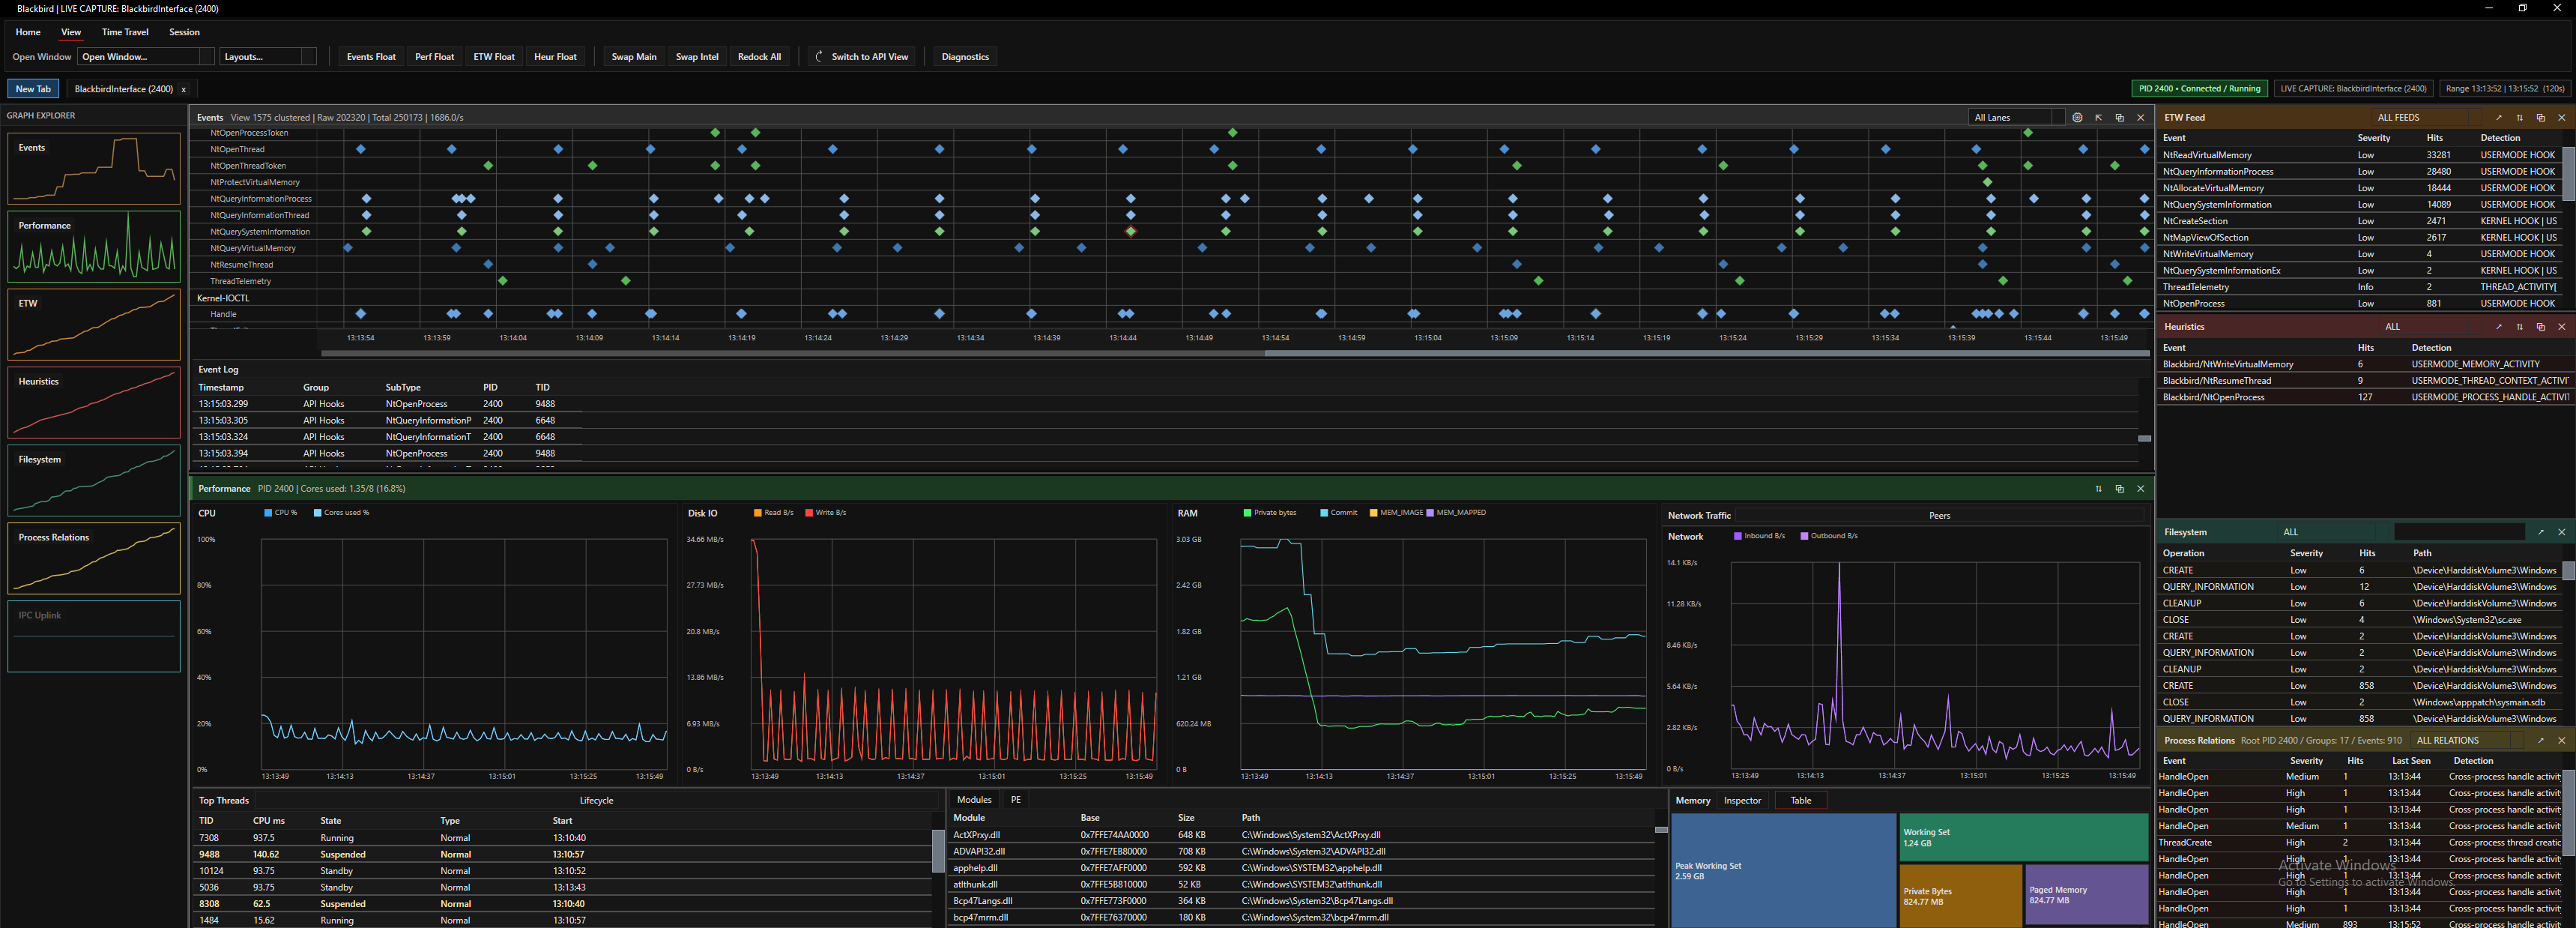
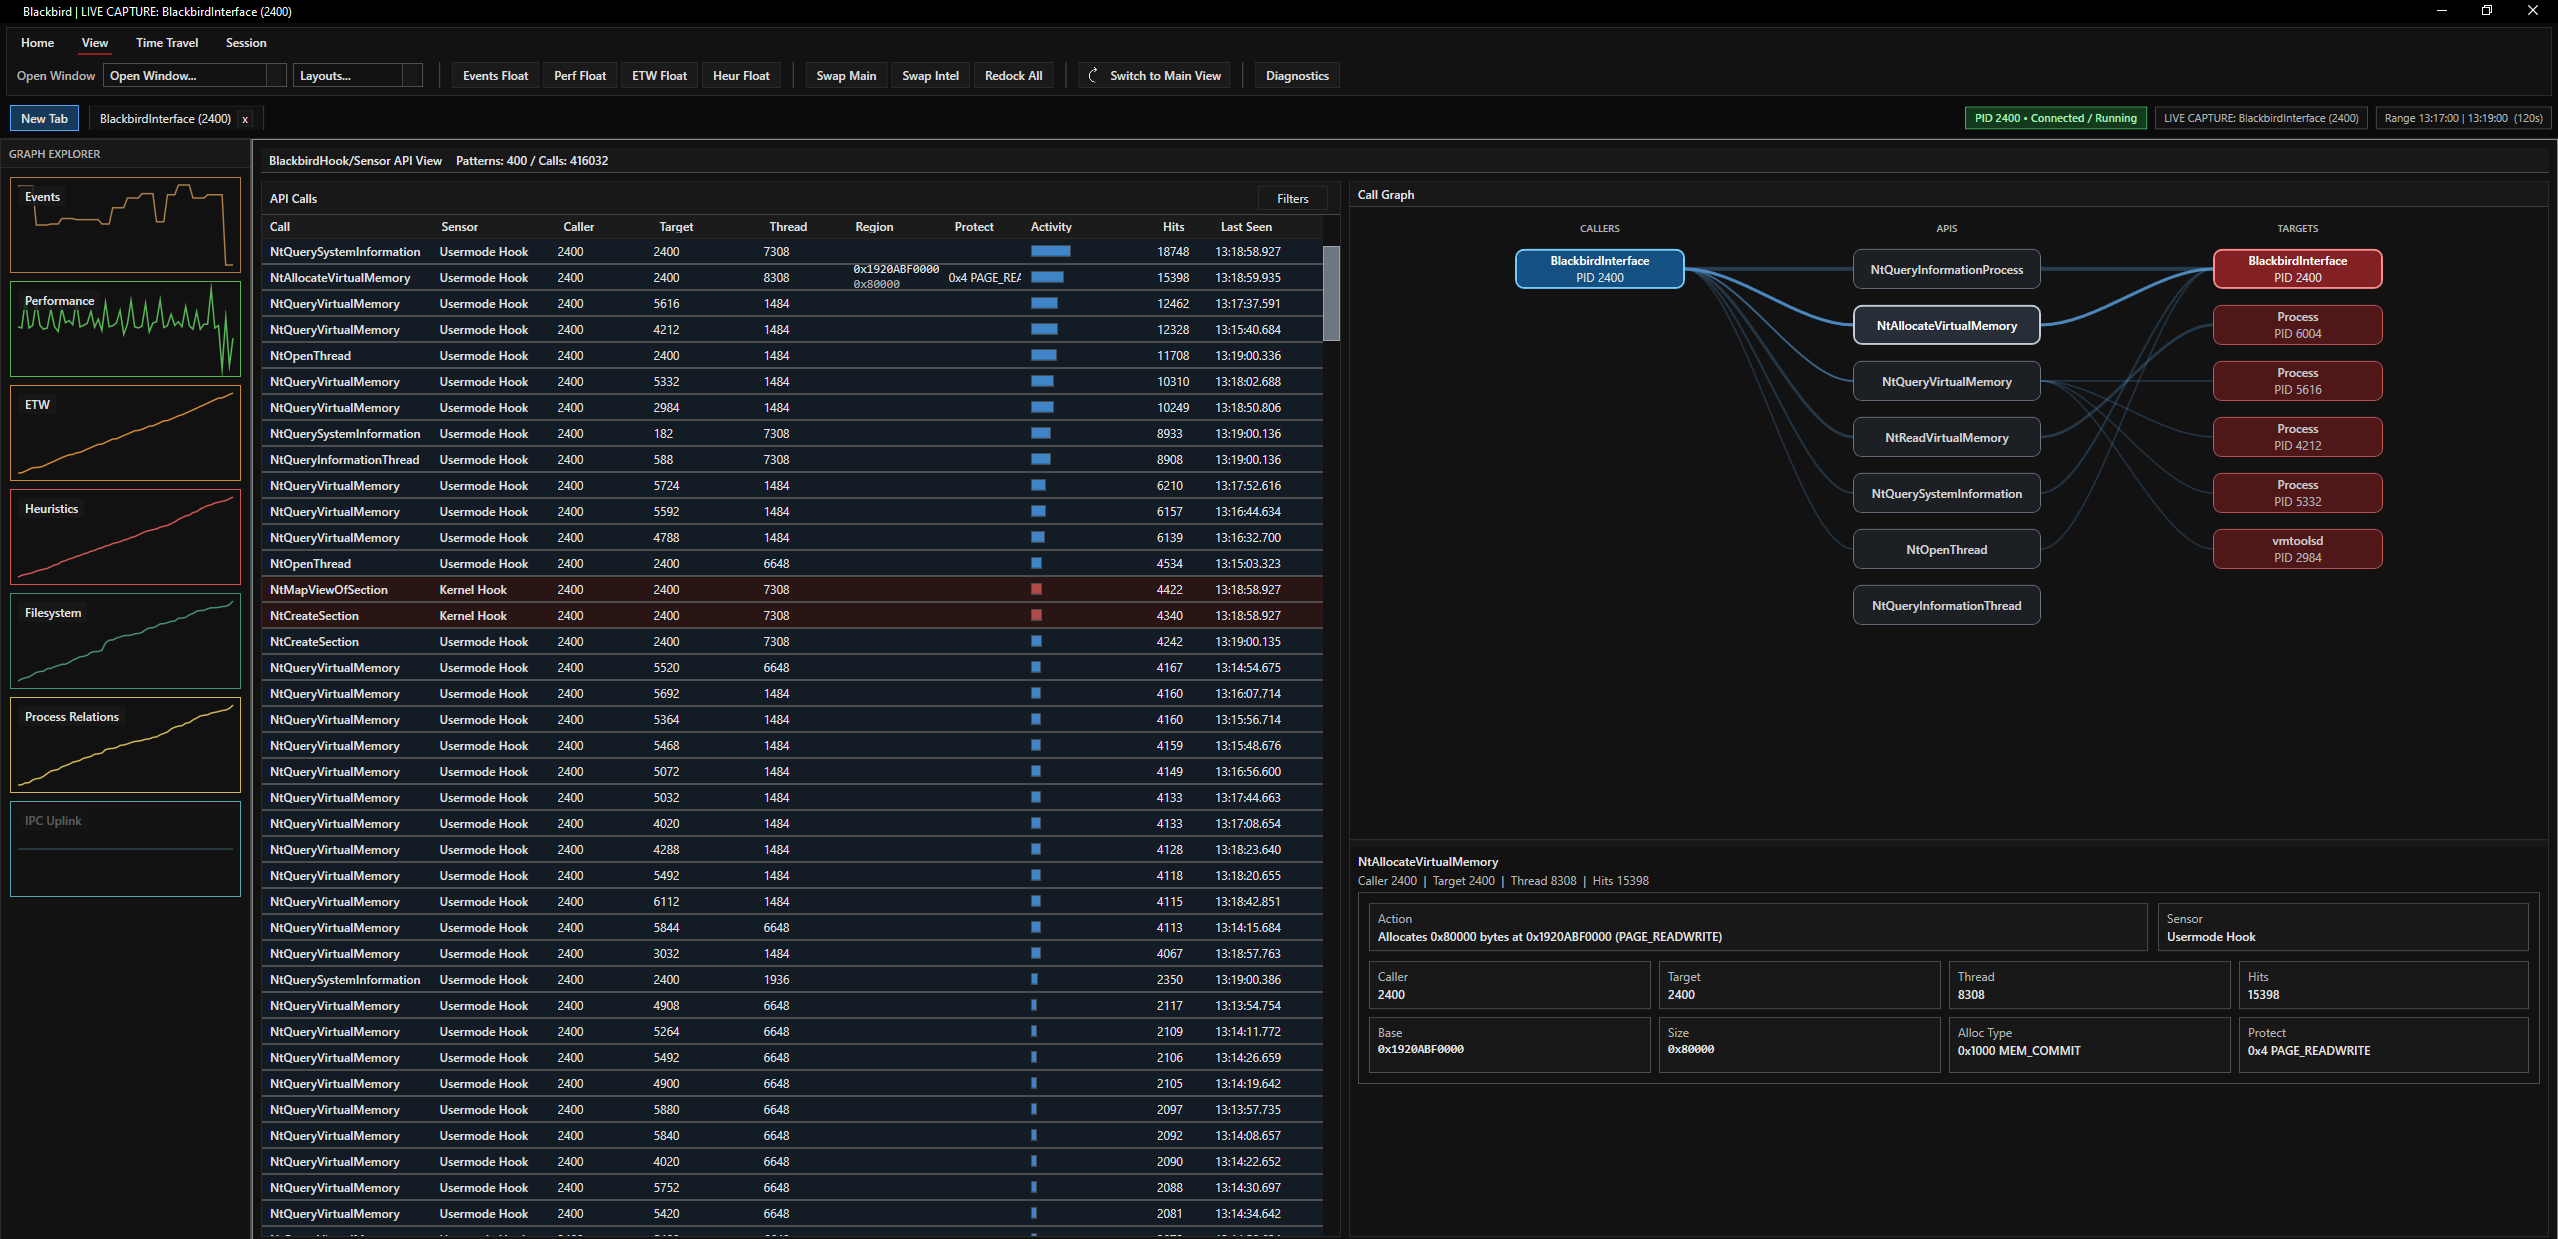
<img src=" width="980" alt="Blackbird main interface" />
</p>
<p align="center">
<img src=" width="980" alt="Blackbird main interface" />
</p>
REQUIREMENTS
A machine on Windows 10 22H2 or higher, 64-bit.
> [!WARNING]
> Blackbird performs kernel-le and may affect system stability depending on configuration.
> Always use it within a controlled machine en and not on systems containing important data.
> [!IMPORTANT]
> Blackbird is in early-de. The current state of Blackbird showcases the core system's functionality and implementation. Detection tuning, threat-intel integration, performance impro and much more are in the works. Blackbird Community (This) is a subset of a larger of Blackbird, so updates may be delayed.
FEATURES
BUGS & ENHANCEMENTS
Please use this project board to open issues & enhancements. This also loosely tracks li.
DOCUMENTATION
The public local-stack introduction, installation, architecture, security notes,
and UI manual are provided here:
Session archives are stored as .bkcap (SQLite + LZ4). Detections can be exported as SIEM JSON Lines, Splunk HEC JSON, Elastic ECS NDJSON, CEF, or CS reference scenarios are in DetectionExamples.exe.
COMPILATION
You need Studio 2022+ with Windows Driver Kit (WDK) and .NET (Desktop De).
Clone Blackbird:
`git clone
Open the Blackbird.slnx file & select Release` & build.
> [!NOTE]
> Some instability or unexpected behavior may occur due to the low-le of the platform. This is expected during de.
项目信息
开发语言:C#
Star 数:65
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Powerful Kernel Malware Investigation Platform | Software Analysis & Threat Hunting 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Blackbird - Powerful Kernel Malware Investigation Platform | S |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:09:14 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 177 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |