项目说明
Cybersecurity-Homelab-and-Penetration-Testing-Project
I designed and implemented a multi-platform cybersecurity homelab to simulate real-world Enterprise en for practicing penetration testing, Network defense, and Acti management. I am building this homelab to stimulate both Offensive and Defensi
Cybersecurity Homelab
O
This project is a hands-on cybersecurity homelab designed to simulate real-world working en. The lab includes a firewall (OPNsense), a (Metasploitable 2) machine for ethical hacking, a Windows Server with Acti, a Kali Linux machine for penetration testing, and a Windows client machine for domain joining and interaction. The goal of the lab is to practice penetration testing, scanning, network defense, and Acti management in a secure and controlled en.
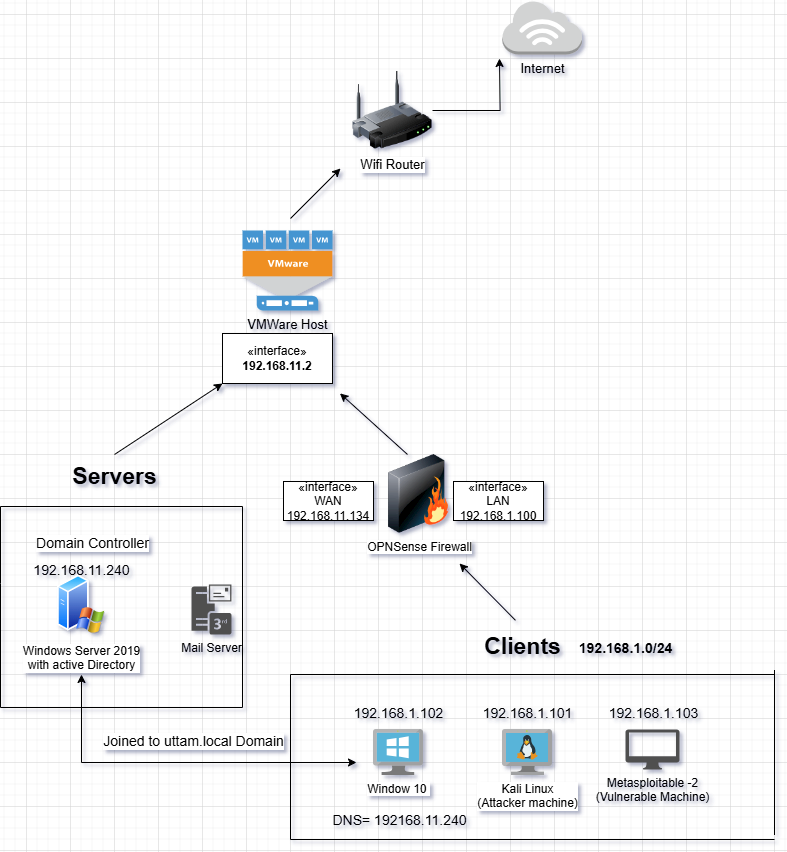
Network Topology
!Network Diagram
The network diagram abo the architecture of the HomeLab en.
Network Configuration
Ensure that your platform (e.g., Workstation or ) is configured with the following networks:
VLan3: Used for connecting pfSense.VLan1: Used for connecting Kali Linux, windows client machine and the machine.VLan2: Used for connecting windows Server and mail server.The homelab consists of the following components:
Firewall/Router: OPNsense firewall managing network segmentation and traffic filtering. Also act as a router, VPN and IDS/IPS configuration.Penetration Testing: Kali Linux machine for ethical hacking and security assessments. Target: Metasploitable 2 machine with for exploitation.Acti En: Windows Server 2019 configured with Acti for managing users, groups, and policies.Windows Client Machine: A Windows 10 client machine connected to the AD domain for testing domain user operations and policies.---
Components
1. OPNsense Firewall
Configured firewall rules to control and filter LAN and WAN traffic.Implemented VLANs for network segmentation, separating internal network segments , One for the client machines and one for the servers.Installed and configured Suricata IDS/IPS for monitoring and blocking malicious network traffic.Enabled for secure remote access to the lab.2. Kali Linux (Penetration Testing Machine)
Kali Linux serves as the main platform for penetration testing and assessments.Used tools such as Nmap, Metasploit, Burp Suite, and Wireshark,Mfconsole,Veiland lot of scanning and exploitation tools to conduct security testing.Launched attacks against the Metasploitable machine and Windows Server to identify and test defense mechanisms.Conducted network reconnaissance, scanning, and exploitation tasks.3. Metasploitable 2 ( Target)
Metasploitable 2 is used as the machine to practice exploitation techniques. scanning was performed using Nmap and OpenVAS to disco with known .Successfully exploited such as FTP, SSH, and MySQL using Metasploit Framework.Documented the exploitation process, results, and mitigations.4. Windows Server 2019 with Acti
Deployed Windows Server 2019 with Acti Domain Services (AD DS) to simulate an enterprise-level AD en.Created users, groups, and Group Policy Objects (GPOs) to enforce security policies and manage network resources.Tested Acti exploitation techniques such as Kerberoasting, Pass-the-Hash, and Lateral Mo using tools like BloodHound and PowerView.Demonstrated secure password policies, account lockout mechanisms, and multi-factor authentication (MFA).5. Windows 10 Client Machine
Joined the Windows 10 client machine to the Acti domain.Tested AD user logins, group policies, and security settings from a client perspective.Simulated attacks on the client machine to see how GPOs and other security settings could prevent or limit user exploitation.Interacted with shared network resources and remote services, testing network policies and permissions.Also act as a target Machine to carry out the attacks like malware deployment and browser exploitation and MITM attacks.---
Tools and Technologies
Firewall/IDS: OPNsense, SuricataPenetration Testing: Kali Linux with tools like Metasploit, Nmap, Burp Suite, Wireshark, BeeF and lot more. Scanning: OpenVASActi: Windows Server 2019, BloodHound, PowerViewOperating Systems: Kali Linux, Windows Server, Windows 10, UbuntuAutomation: Bash scripting, Python, Powershell, Ruby, Perl etc.---
Project Structure
images/: Contains screenshots for configuation and tasks.config/: Configuration files for OPNsense, Suricata, and other tools.scripts/: Bash, Python, Perl and Python and other scripts for automation and testing.reports/: reports, penetration testing documentation.---
How to Set Up the Homelab
Prerequisites
or Workstation for ,here I am using workstation.ISO files for Windows Server, Kali Linux, Windows 10, and Metasploitable 2OPNsense ISO for firewall setupStep 1: Set Up OPNsense Firewall
Download and install OPNsense in workstation.Configure WAN and LAN interfaces.Set up firewall rules and VLANs for network segmentation and traffic management.Step 2: Deploy Metasploitable 2 for Testing
Install Metasploitable 2 and connect it to the internal network.Use Nmap and OpenVAS for discovery and testing.Step 3: Set Up Windows Server with Acti
Install Windows Server 2019 and configure Acti Domain Services (AD DS).Create users, groups, and GPOs to enforce security policies.Step 4: Set Up Kali Linux for Penetration Testing
Install Kali Linux and connect it to the internal network.Perform network reconnaissance, scanning, and exploitation tasks on the Metasploitable and Windows Ser.Step 5: Set Up Windows 10 Client
Install Windows 10 and join the machine to the Acti domain.Test domain logins, policies, and user interactions with the network en.---
Sample Reports and Screenshots
Report: Open scan reportPenetration Test: Metasploit exploitation of Metasploitable 2Acti Enumeration: BloodHound attack path screenshotSuricata Alerts: Suricata IDS alerts screenshot---
Future Enhancements
Add more machines (e.g., OWASP Juice Shop) to expand penetration testing scope.Automate daily scans and alerting with Bash and Python scripts.Implement ad red team/blue team exercises using Cobalt Strike for ad emulation.Add a Linux server to simulate an enterprise multi-platform en.项目信息
开发语言:Python
Star 数:13
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕I designed and implemented a multi-platform cybersecurity homelab to simulate real-world Enterprise environments for practicing penetration testing, Network defense, and Active Directory management. I am building this homelab to stimulate both Offensive and Defensive Security展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。