 防护思路
点击放大
Vesuki - Defensive Rust control-flow obfuscation and anti-a
项目说明
is a Rust x86_64 control-flow hardening and obfuscation toolkit built for authorized anti-tamper and defensi protection. It provides a proc-macro attribute that rewrites annotated functions into a dispatcher-style execution form and injects per-build randomized “noise blocks” (entropy mixing, opaque branching, disassembly decoys) to raise the cost of static analysis and signature-based re.
> Use responsibly: is intended for defensi and protecting software you own or explicitly control. Do not deploy it to conceal malware or evade monitoring in unauthorized en.
What's Included
This repository is a small workspace with three pieces:
* runtime ()
* Core runtime functions, entropy sources, state e, and generated per-build block wrappers.
* !() macro for injecting per-site noise.
* proc-macro ()
* #[] attribute for functions and methods.
* Rewrites bodies into an obfuscated dispatcher shape and inserts noise calls.
* Example/test harness (tests)
* Minimal example program demonstrating the attribute macro on functions + methods.
High-Le
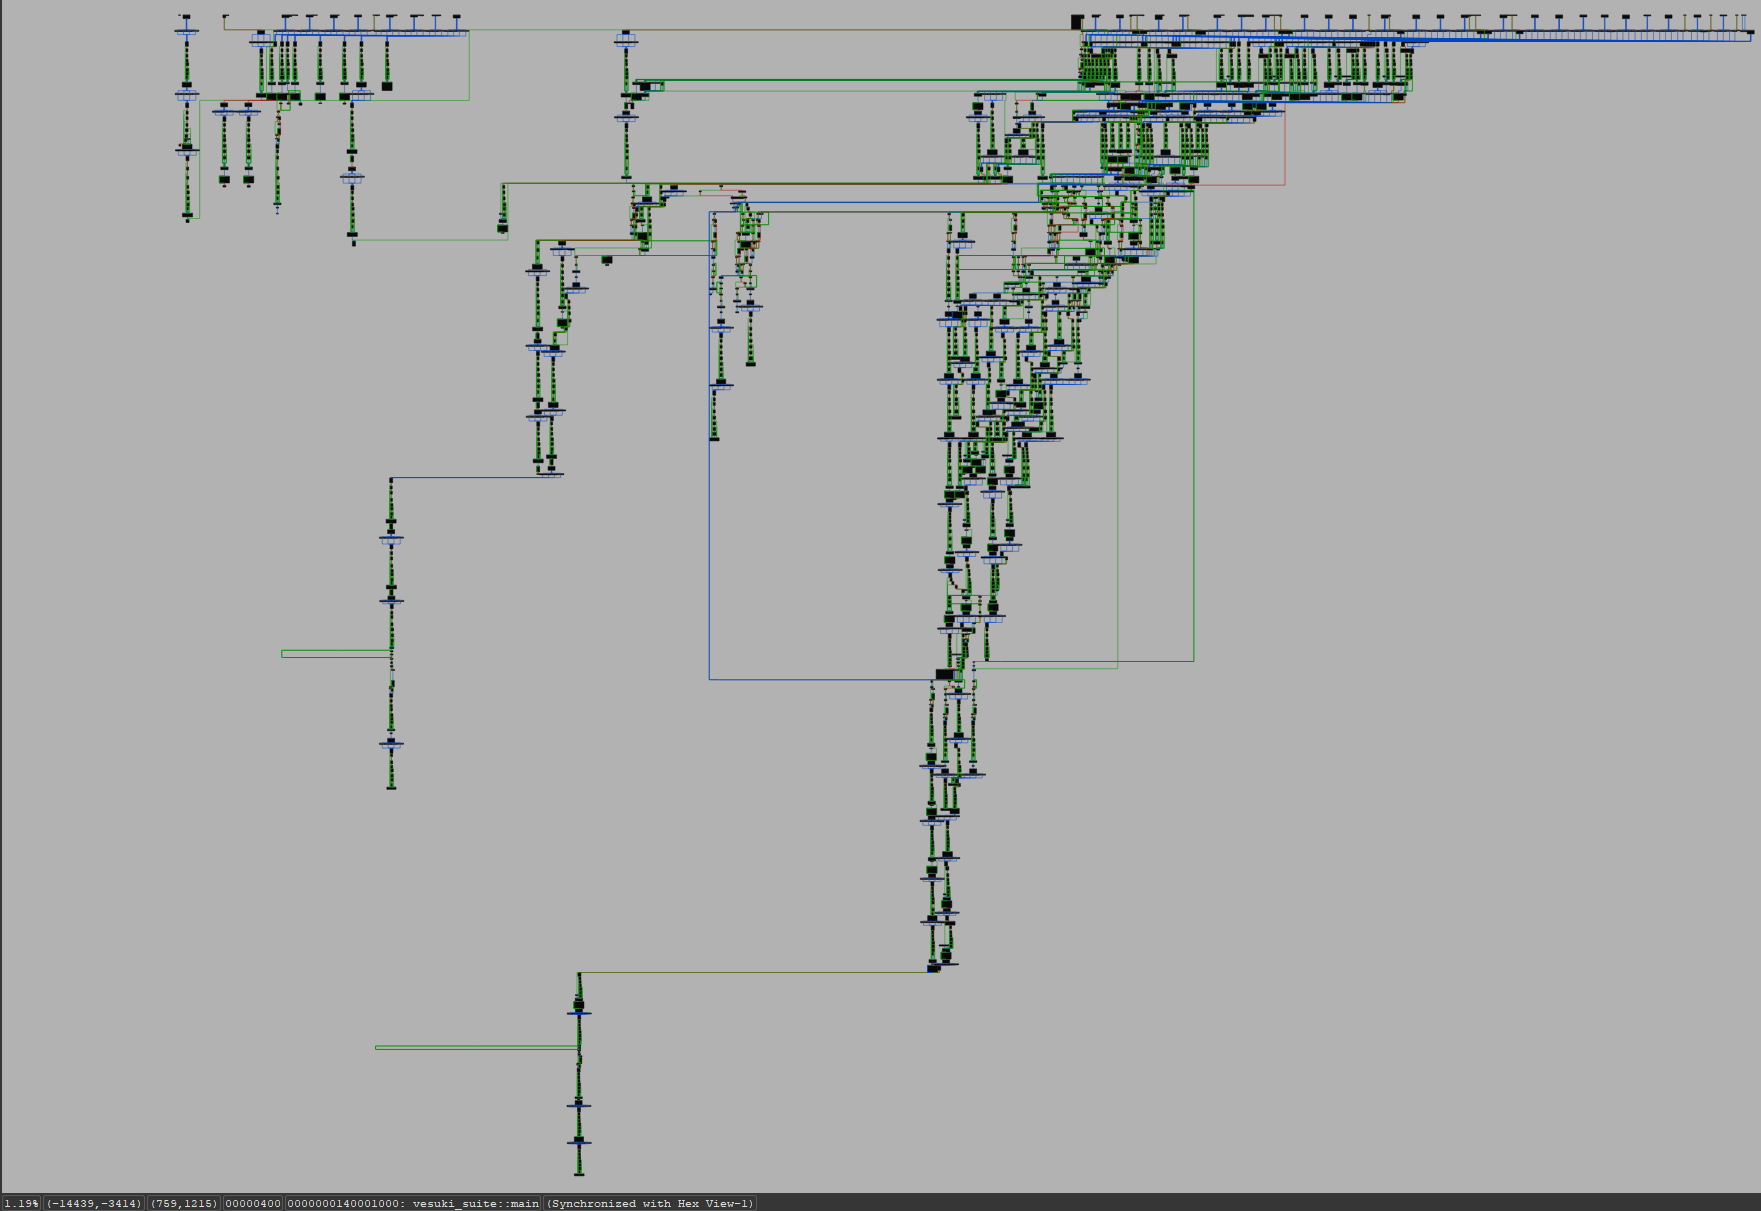
!IDA
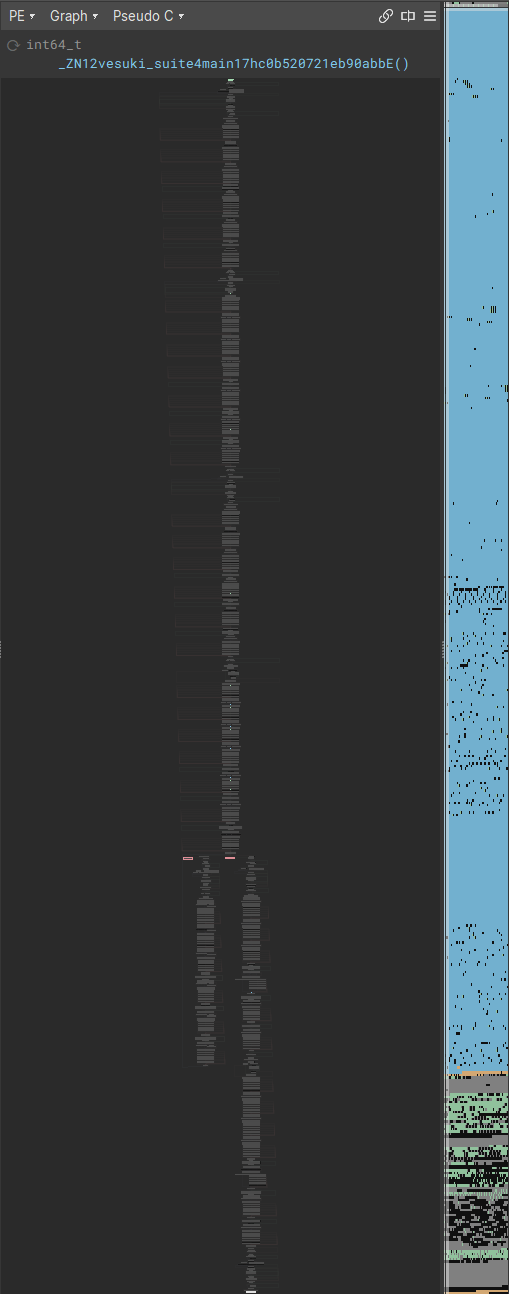
!BN2
* Attribute-based function transformation via #[]
* Per-callsite noise injection via !()
* Per-build randomized code generation (build script emits a generated module into OUT_DIR)
* Multiple “intensity” drivers:
* (), (), ()
* Entropy seeding using CPU facilities (RDSEED when a, serialized TSC fallback)
* Control-flow noise primitives:
* opaque predicates and gated execution
* state-dri selection
* inline asm nops and disassembly decoys
* randomized thunk banks for indirect execution
* Custom section placement for generated wrappers to reduce layout predictability
How It Works
Compile-Time (Proc Macro)
#[] performs a structural rewrite of the target function:
* Computes a stable hash from the signature + body tokens
* Hoists let bindings into a stable “setup” region
* Executes remaining statements through a dispatcher loop seeded from per-build constants
* Captures return (when present) into an internal Option<T> slot
This transformation is designed to preser for typical “leaf” functions and tight routines, while making the resulting control flow less directly readable.
Build-Time (Generated Runtime)
build.rs generates a per-build Rust module that contains:
* build-specific constants and seeds
* randomized execution orders for light/medium/hea
* wrapper functions around “block” primitives with randomized skins/sections
* thunk banks used to introduce additional indirection and
The generated module is included at compile time via:
Runtime (Noise Injection)
The runtime provides:
* !() for per-site injection (salted by file:line:col)
* ::<SALT, CFG>() and intensity drivers for chaining blocks
* state ad routines that mix entropy and evol selection
Requirements
* Architecture: x86_64 only (the runtime uses inline assembly and x86_64 arch intrinsics)
* Rust toolchain: stable Rust (proc-macro + build script + inline asm)
Quick Start
1) Build the workspace
2) Run the example
Usage
Annotate a function
Inject noise at a callsite
Practical Guidance
is most effective when applied to:
* small, high-value routines (checks, gates, token , licensing, policy decisions)
* leaf functions or methods where the body is relatively compact
* code paths where additional instructions and branching noise are acceptable
To avoid surprising behavior:
* Prefer wrapping tightly-ordered sequences into a single block/loop statement when possible.
* Treat as anti-analysis friction, not as a semantic optimizer or a security boundary.
Threat Model Fit
helps with:
* raising static re cost (especially for signature-based or pattern-dri)
* increasing per-build to reduce “one bypass fits all builds”
* adding execution noise around sensiti points
项目信息
开发语言:Rust
Star 数:8
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive Rust control-flow obfuscation and anti-analysis tooling for x86_64 binaries展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Vesuki - Defensive Rust control-flow obfuscation and anti-a |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:12:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 115 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |