 防护思路
点击放大
SnowBotBreaker - Deliver gzip bombs to scrapers & bots using Cloudf
项目说明
<p align="center">
<img src=" alt="Description" width="500" />
</p>
<h1 align="center">SnowBotBreaker</h1>
![Cloudflare Workers]()
![TypeScript]()
![Node.js]()
---
Crash BOTS and SCRAPERS using BOMBS💣. Delivered for free, directly by Cloudflare!
⭐ Live demo HERE - *use with a scanning tool*
---
Are you fed up with bots and scrapers getting a free pass on your website? Want to fight back??
*This is the ser of the classicdd if=/dev/zero bs=1G count=10 | gzip
trick, also described in
idiallo.com/blog/zipbomb-protection.*
---
<p align="center">
<img src=" alt="Description" width="800" />
</p>
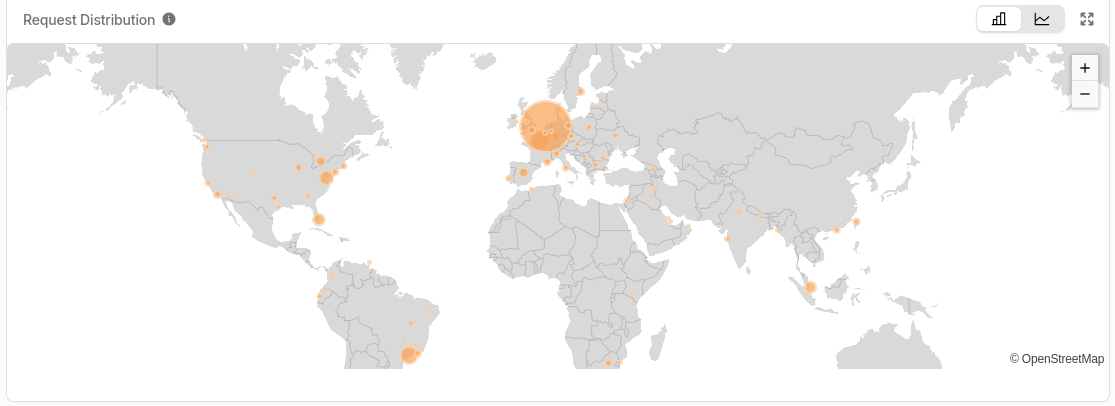
<h4 align="center">You can even keep an eye on your bombing!</h4>
> [!WARNING]
> This bombs every request. Only deploy it on a honeypot route or subdomain
> that you control. You are responsible for what
> you point it at.
---
Contents
---
Quick start
Then, in another terminal:
🧨 Every path behaves the same way: /, /wp-login.php, /.env, etc.
---
Deploy your own
You need Node.js 18+ and a Cloudflare account with a domain linked. **Setup takes only a
few minutes.**
1. Pick your bomb hostname
In Cloudflare, open your zone → DNS, and add a sundomain record for the bomb
host:
| Type | Name | Content | Proxy |
| ------ | ------ | --------- | ---------------------- |
| AAAA | bomb | 100:: | Proxied (orange cloud) |
2. Point the Worker at it
Uncomment and edit the routes block in wrangler.toml:
3. (Optional/Skip) Regenerate the bomb
Only rebuild it if you want a different
size. See Configuration.
4. Ship it
Then confirm it from outside:
🔥 Done! 🔥
---
Configuration
*Skippable in most cases, just know you can change bomb size here*
There is almost nothing to configure. The only knob is the bomb
size, set when you (re)generate the blob with make bomb:
| What | Where | Default |
| --------------------- | -------------------------- | -------------------------------- |
| Decompressed size | GIB in the Makefile | 10 = 10 GiB |
| Compression level | gzip -9 in the Makefile| -9 (max) |
| Served Content-Type | src/index.ts | text/html; charset=utf-8 |
For example, make bomb GIB=1 gives a 1 GiB bomb (~1 MB on the wire), gentler
and cheaper, good for testing.
---
FAQ
🔷 Why does curl show only 10 MB, not 10 GB?
curl does not decompress responses unless you pass --compressed. Without it you
see the raw ~10 MB on the wire. With it, curl inflates the gzip and you get the
full 10 GiB. Most bots decompress automatically, like curl --compressed.
🔷 Won't this cost me bandwidth?
Each hit sends ~10 MB out of Cloudflare. That is cheap, but not free, and it scales
with how much traffic you attract. Shrink the bomb (see
Configuration) if egress is a concern.
🔷 Will it crash a real browser / my own monitoring?
It can. Clients that auto-decompress (most scrapers and bots) try to inflate it and exhaust their own memory. That's the point. If you want to spare one path (e.g. a health check), add a
short-circuit at the top of fetch in src/index.ts:
🔷 I have a working bomb, now what?
Now you leave it as hidden link/href where ever you might get bots crawling.
Fake pagination code, fake price fetch, redirect to bomb after X failed auth. Since every URI also gets bombed (bomb.example.com/ANYTHING-HERE), you can really get creative with it!
🔷 How do I view bomb stats
In the Cloudflare dashboard, search for "Worker", select "Workers & Pages", click on your bomb worker, then select "Metrics" in the upper tabs.
---
Disclaimer
Provided this as-is, without warranty. Deploy it only on infrastructure you
control, and only against traffic you are entitled to disrupt. Serving a
decompression bomb to clients you do not control may be illegal in your
jurisdiction. You are solely responsible for how and where you deploy it.
项目信息
开发语言:TypeScript
Star 数:7
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Deliver gzip bombs to scrapers & bots using Cloudflare workers 💣展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SnowBotBreaker - Deliver gzip bombs to scrapers & bots using Cloudf |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:13:19 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 389 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |