 防护思路
点击放大
SentinelForge - This is local defensive security toolkit with sca
项目说明
SentinelForge
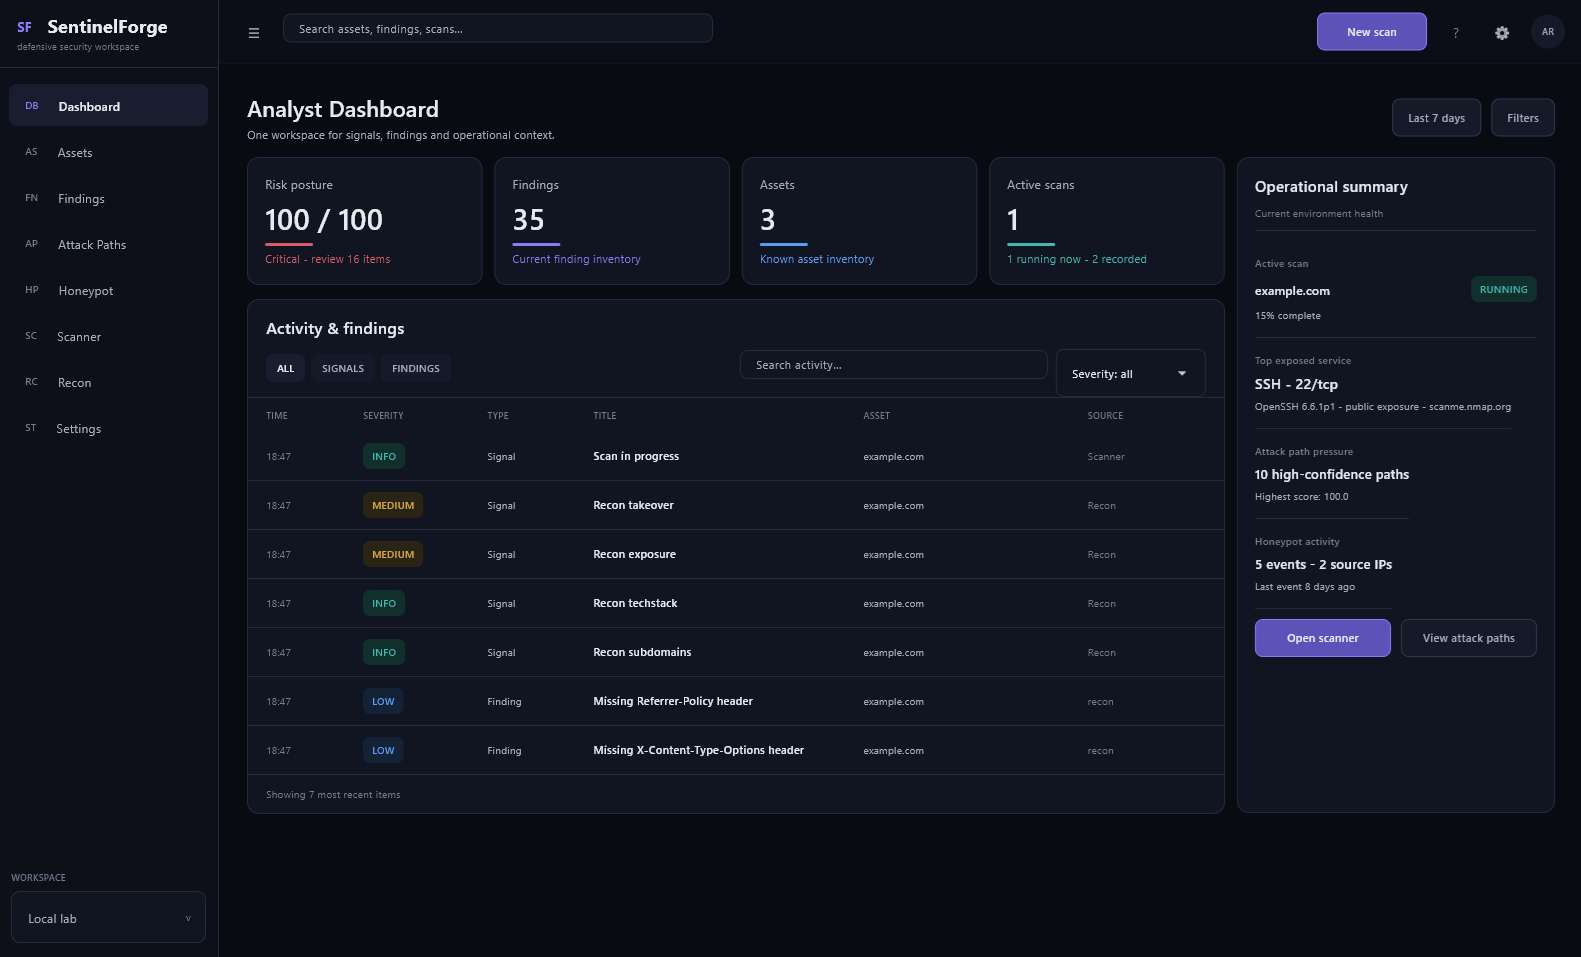
SentinelForge is a local defensi e and attack-path analysis toolkit for home labs and small en.
It normalizes findings from service scanning, intelligence, passi, web audits, control gaps, and honeypot telemetry into an e graph. SentinelForge uses that graph to rank explainable attack paths, retain supporting and contradictory e, and produce analyst-friendly reports.
The project is pre-release. Its current focus is improving correlation logic, e confidence, path explainability, and false-positi—not replacing mature scanners such as Nmap.
!SentinelForge dashboard
Features
Install
Optional packet tooling is intentionally separate:
Run UI
or:
CLI
Health Checks
Run doctor before opening an issue or enabling optional engines:
It checks Python, SQLite, DB integrity, WAL mode, optional tools, package imports, scanner policy, local counts, and source quality.
Stress Testing
SentinelForge includes local synthetic stress data tools for report, graph, attack path, and honeypot-campaign performance without scanning real systems.
stress-clear removes only synthetic records created with the SentinelForge stress prefix.
Optional Engines
Nmap is used automatically when installed and the scanner engine is set to auto or nmap. Extra Nmap flags can be configured, but SentinelForge owns output and target flags internally.
Nikto can be enabled as an optional web audit engine. SentinelForge stores Nikto output as supporting e that should be manually before treating it as confirmed.
Packet tooling is optional:
PyShark/Wireshark/TShark support is currently marked WIP.
Scope Controls
Public targets are blocked by default. Configure scanner scope before scanning external assets.
Supported scanner settings:
target_allowlist: list of wildcard patternsscope_file_path: path to a text file with one hostname/IP/wildcard per lineblock_public_targets: default trueblock_pri: default falseExample scope file:
Feeds
Use Settings or CLI before importing:
The importer supports official and generic shapes for JSON and CS. The Settings page shows accepted rows and minimum fields.
De
Tests isolate runtime data through SF_DATA_DIR.
Status
This project is pre-release. Review scope controls and local laws before using it outside a lab.
项目信息
开发语言:Python
Star 数:3
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕 This is local defensive security toolkit with scanner, recon, honeypots, vulnerability correlation, evidence graph, attack path ranking, and reports.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SentinelForge - This is local defensive security toolkit with sca |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:17:05 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 458 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |