 防护思路
点击放大
hlf-time-oracle - Chaincode for blockchain Hyperledger Fabric provid
项目说明
hlf-time-oracle
hlf-time-oracle is a chaincode for blockchain Hyperledger Fabric provides accurate time to other chaincodes. hlf-time-oracle based on ntp pakage pakage and nts pakage. Thus solving the security problem associated with possible transaction time manipulation by the blockchain client (C). The chaincode provides functions GetTimeNtp() and GetTimeNts(). Calling these functions creates a call to the NTP (Network Time Protocol) and NTS (Network Time Security) servers. The time received from any of these servers can be used to the correctness of the transaction time defined on the client side. De of chaincodes for blockchain can use hlf-time-oracle instead of independent writing code to interact with NTP and NTS servers. hlf-time-oracle does not save any data to the blockchain during its operation.hlf-time-oracle for Hyperledger Fabric 2.4.x in folder hlf_2.4. hlf-time-oracle for Hyperledger Fabric 2.5.x in folder hlf_2.5.
List of public servers
Solving the problem of centralisation
The features of the NTS protocol
Resistance to the man-in-the-middle attack
License
<a name="1"></a>
List of public servers
Public NTP servers
Public NTS servers
<a name="2"></a>
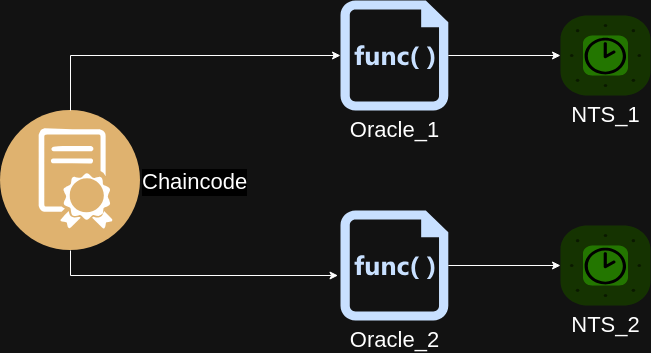
Solving the problem of centralisation
If you don't want to depend on a single time server, you can use multiple time oracles.
<p align="center">
<img src="./img/oracles.png">
<br>
Oracles
</p>
<a name="3"></a>
The features of the NTS protocol
NTS is a enhancement of NTP (see RFC 8915). There are 2 connections: TCP for TLS and UDP for NTP. The port for NTP connection is determined by the NTS server. It can be different from the standard 123/UDP. Keep this in mind when configuring the firewall.
For correct TLS connection establishment it is required that the client (i.e. the system on which hlf-time-oracle is running) has relatively correct system time (falling within the NTS-ser period). Otherwise the connection will not be established.
<a name="4"></a>
Resistance to the man-in-the-middle attack
It is recommended to use GetTimeNts() instead of GetTimeNtp(). Unlike NTP, the use of NTS is resistant to the man-in-the-middle attack. In case of unauthorized spoofing of the open data part, the following error is logged: authentication failed on client. In case of an attempt to spoof the NTS ser, the following error is logged: key exchange failure: tls: failed to certificate: x509: certificate signed by unknown authority.
Experiment
<p align="center">
<img src="./img/model.png">
<br>
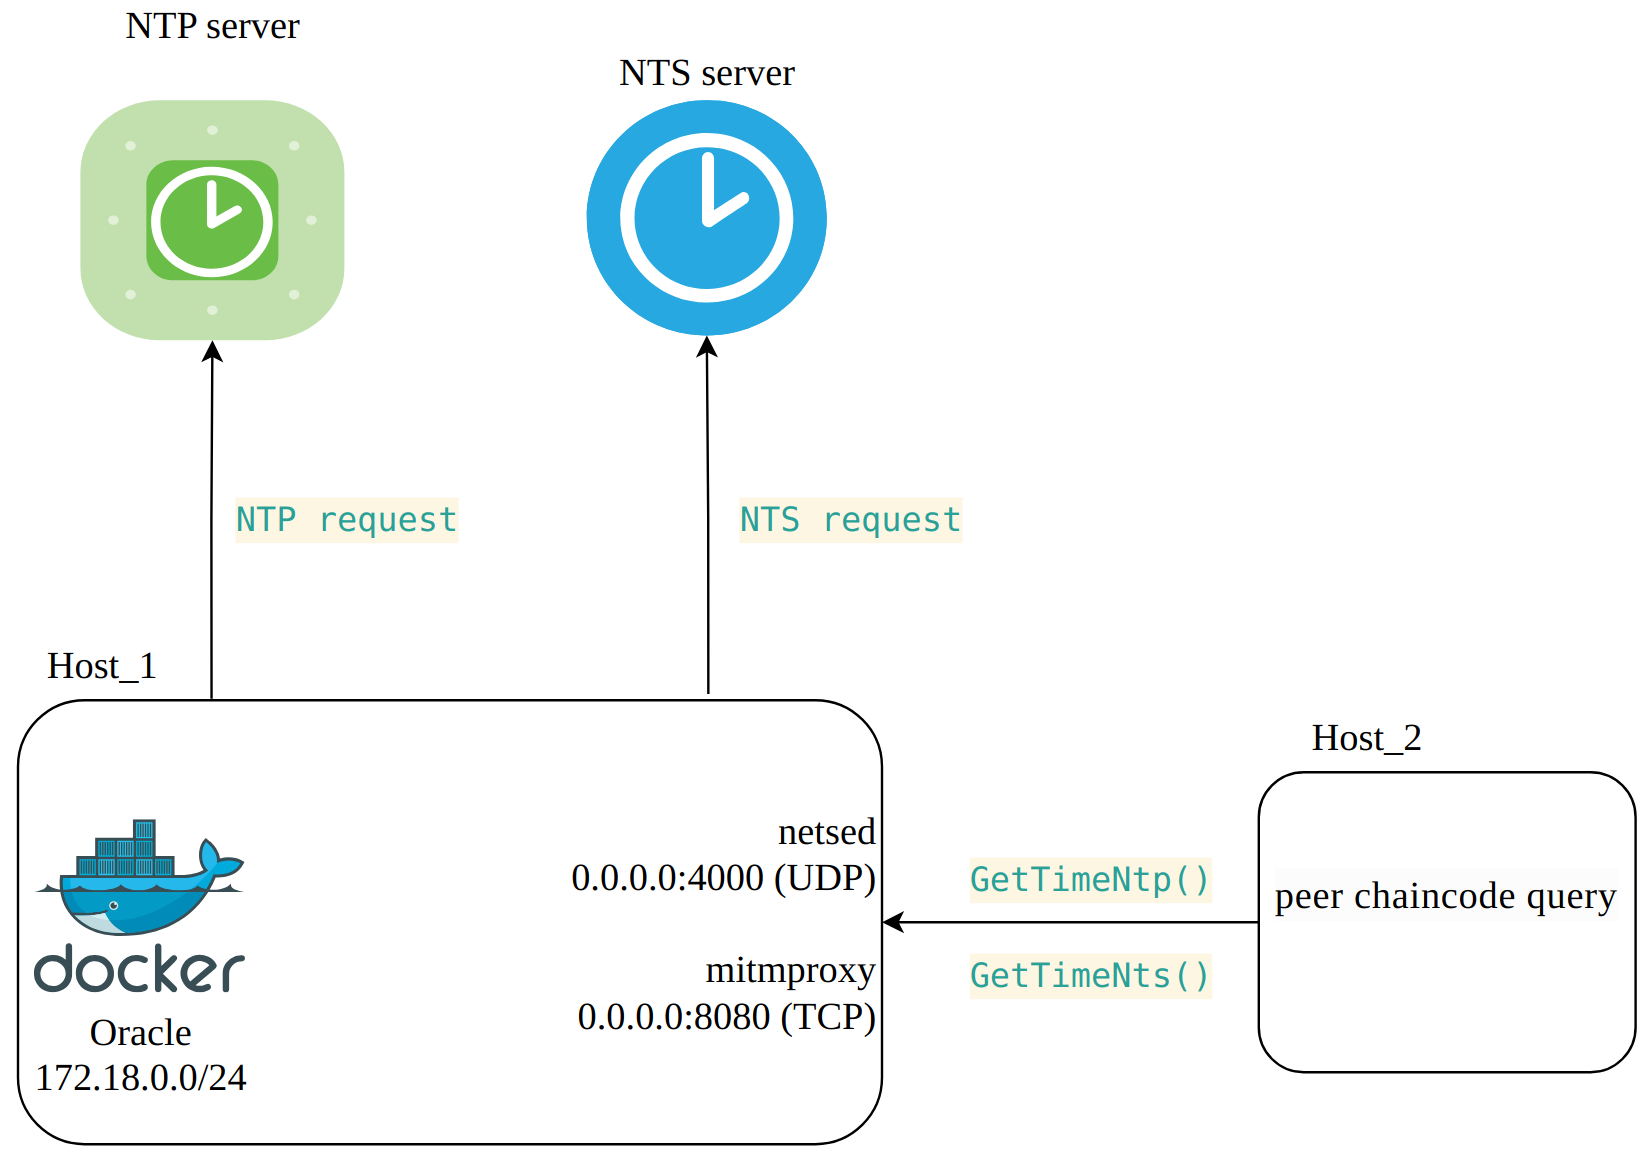
Model
</p>
hlf-time-oracle is running in the docker (docker network 172.18.0.0/24). On the docker host (Host_1) netsed (port 4000/UDP) and mitmproxy (port 8080/TCP) are running .Traffic to them from hlf-time-oracle will get through iptables. The second host (Host_2) accesses Oracle's GetTimeNtp() and GetTimeNts() functions (via peer chaincode query call). Calling these functions causes Oracle to call the NTP server and the NTS server, respectively.
#### NTP
An iptables rule to redirect traffic to netsed:
Run netsed with rule.
<p align="center">
<img src="./img/ntp_netsed_1.png" alt="" width="800">
<br>
Create a rule in netsed to replace %ea%33 with %eF%33
</p>
<p align="center">
<img src="./img/ntp_netsed_2.png" alt="" width="800">
<br>
The result of a successful attack.
</p>
#### NTS
##### netsed
An iptables rule to redirect traffic to netsed (NTS server ntp1.glypnod.com has an IP address 104.131.155.175):
Run netsed with rule.
<p align="center">
<img src="./img/nts_netsed_1.png" alt="" width="800">
<br>
Create a rule in netsed to replace %ea%33 with %eF%33
</p>
<p align="center">
<img src="./img/nts_netsed_2.png" alt="" width="800">
<br>
The result of a unsuccessful attack.
</p>
Let's see docker logs:
<p align="center">
<img src="./img/nts_netsed_3.png" alt="" width="800">
<br>
docker logs
</p>
##### mitmproxy
An iptables rule to redirect traffic to mitmproxy (NTS server ntp1.glypnod.com has an IP address 104.131.155.175):
Let's see mitmproxy logs:
<p align="center">
<img src="./img/mitmproxy_1.png" alt="" width="800">
<br>
mitmproxy logs
</p>
Let's see docker logs:
<p align="center">
<img src="./img/mitmproxy_2.png" alt="" width="800">
<br>
docker logs
</p>
<a name="License"></a>
License
MIT
项目信息
开发语言:Go
Star 数:3
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Chaincode for blockchain Hyperledger Fabric provides accurate time to other chaincodes. Thus solving the security problem associated with transaction time manipulation (CVE-2024-45244).展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | hlf-time-oracle - Chaincode for blockchain Hyperledger Fabric provid |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:18:43 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 193 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |