 防护思路
点击放大
macbastion - Defensive security audit tool for macOS
项目说明
🜲 CHIMERA — a local-first security organism for macOS
> Not a collection of tools. One mind orchestrating eight specialized nati —
> each unique alone, de together. It runs entirely on your machine:
> no cloud, no telemetry, no recovery paths.
!status
!macOS
!python
!tests
!license
CHIMERA senses you and your en and reacts autonomously to protect you — then writes
every action to an audit trail you can question (*"why did my vault lock?"*). It lives inchimera/; the wider macbastion hardening toolkit (below) is its umbrella.
---
⚡ The dead-man switch
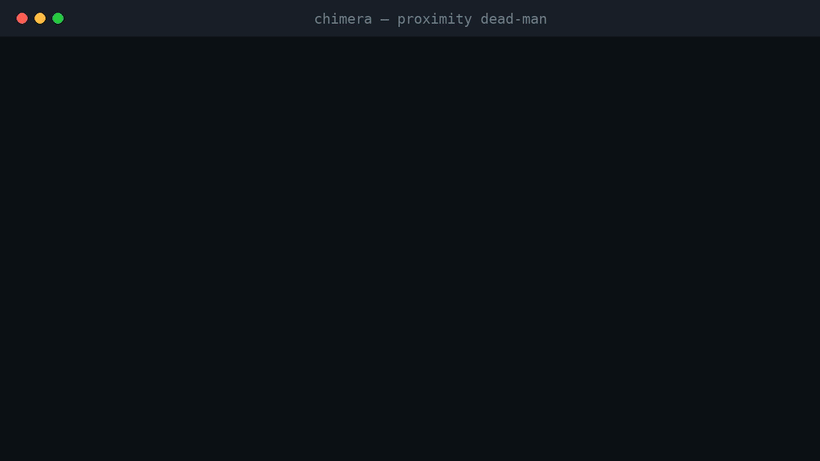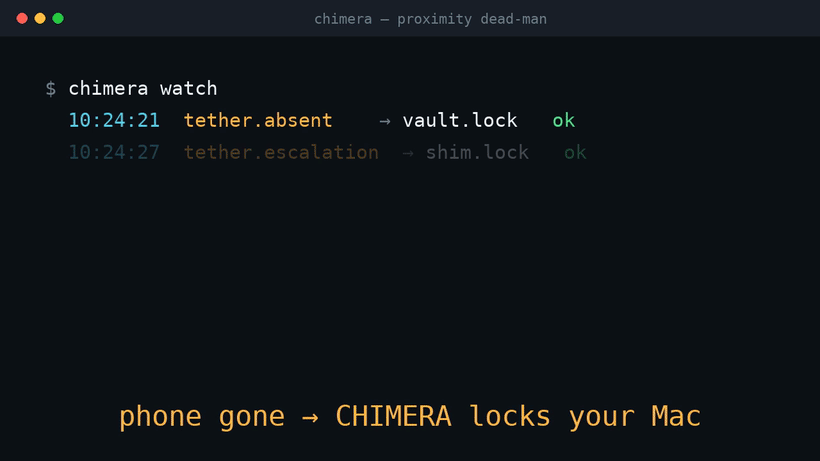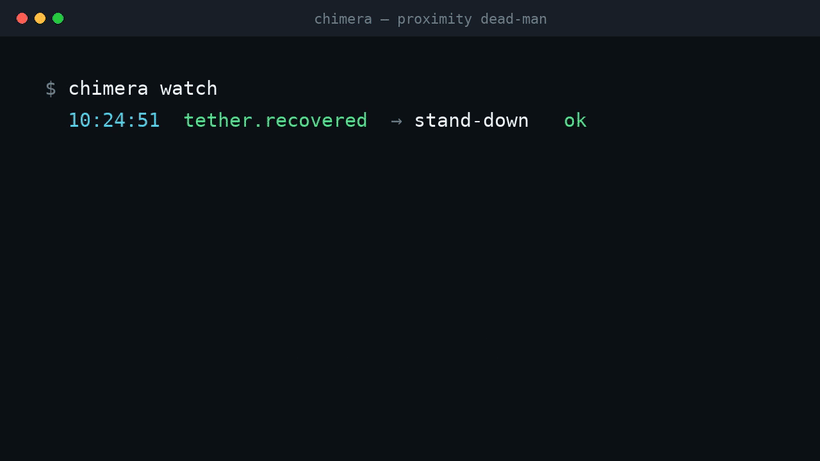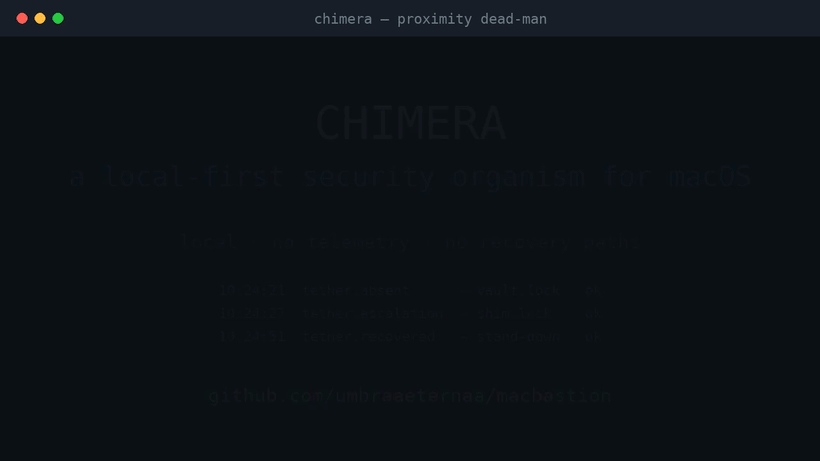
Pair CHIMERA to your phone o. Walk away — your Mac locks itself (vault sealed,
screen locked) on its own authority. Come back — it stands down, but ne.
BLE is spoofable, so making "return" an unlock would be a backdoor for anyone holding your phone.
Proximity is a key that only locks — coming back is always your password.
!CHIMERA dead-man switch — walk away with your phone and the Mac locks itself
> 📹 Live, no edits: phone leaves → tether.absent → vault.lock → tether.escalation → (the screen locks) → you return →
> shim.locktether.recovered → stand-down (still locked; you
> type your own password). Every reflex lands in an audit trail you can question. Proven on real
> hardware — including an Android phone as the beacon.
---
Quick start
Requirements: macOS on Apple Silicon · Homebrew · Python 3.11+ · Ollama.
setup.sh configures itself on your Mac — installs the Homebrew C deps + the local LLM model,
builds every nati, and ne anything pri behind your back. Full guide:chimera/README.md. Pri + TCC-gated capabilities are self-signed,
by hand: chimera/deploy/INSTALL.md.
---
The eight organs
| Organ | Lang | Role |
|---|---|---|
| CHAFF | C | decoy HTTPS traffic — masks real patterns |
| ECHO | C | constant-rate bandwidth shaping (real pf/dummynet) |
| ORACLE | Python | local LLM (Ollama) anomaly detection |
| MIRROR | C | humanlike input jitter + pri input sensing |
| PULSE | C / Py | cogniti monitor — adds friction when you're tired |
| VAULT | C | time-locked storage; decrypted plaintext lives only in RAM |
| TETHER | C++ | Bluetooth dead-man — auto-locks if your phone leaves |
| PURGE | C + asm | secure erasure (ARM64 dc zva) — the last resort |
A Python core is the brain: a JSON-RPC socket server the organs register with, a reactive
web that turns events into cross-module reflexes, a cognitive gate, and an append-only audit trail.
How it behaves: ORACLE flags an anomalous event → the core locks your VAULT, starts CHAFF
decoy traffic, normalizes bandwidth via ECHO, and heightens TETHER — then stands down when the
threat clears. Walk away with your phone → TETHER locks the screen through a root shim. Trigger a
panic → PURGE crypto-shreds the keys and zeroes RAM (operator-target file shred is opt-in).
---
Honest status (MANIFESTO §4 — no imitations)
CHIMERA is alpha, built in the open. What is real today:
qwen2.5:7b): ransomware → ~1.0, routine → ~0.05.pf/dummynet anchor on live pf (~25× rate cut measured); opt-in, off by default.
those — done by hand).
It refuses security theatre: it will not pretend to "wipe" unencrypted SSD data (wear-le flash
can't guarantee it) — it crypto-shreds keys instead, and tells you the honest limit.
---
macbastion — the umbrella toolkit
The repository is macbastion, a layered macOS defense project; CHIMERA is its autonomous core.
The broader toolkit also gives you:
macbastion scan ports: what's listening, what's exposed.sudo macbastion stealth on: anonymize hostname, suppress Apple discovery broadcasts.| Layer | Status | Covers |
|---|---|---|
| L0 Firmware / Boot | ✅ | FileVault, SIP, Gatekeeper, Full Security |
| L1 System hardening | ✅ | Telemetry off, junk daemons + legacy kexts purged |
| L1.5 Stealth mimicry | ✅ | Random hostname, mDNS off, Bonjour suppressed |
| L8 Monitoring | 🟢 | ORACLE anomaly detection + PULSE cognitive load *(CHIMERA)* |
| L9 Panic mode | 🟢 | Secure erasure (dc zva) + Bluetooth dead-man *(CHIMERA: PURGE + TETHER)* |
---
Support de
CHIMERA is free, open source, and will stay that way. If it's useful to you and you want to
support continued de — Monobank Jar (Ukraine):
<img src="docs/donate.png" alt="Monobank QR Code" width="320"/>
See docs/donate.md for what donations fund — and what they explicitly do not
change (the MANIFESTO and the no-paywall philosophy).
---
Who builds this
Built solo, in the open, by Natoptanyi (*Umbra* · ) —
a macOS security & privacy engineer. A for consulting on endpoint hardening, native
daemons, and privacy systems → umbraaeternaa.github.io
---
License
MIT — see LICENSE.
项目信息
开发语言:Python
Star 数:2
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive security audit tool for macOS展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | macbastion - Defensive security audit tool for macOS |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:18:57 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 207 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |