 防护思路
点击放大
quietscope - Defensive local security audit tool for macOS, Lin
项目说明
quietscope 🛡️
<p align="center">
<img src="docs/assets/logo.png" width="128" height="128" alt="Quietscope Logo">
</p>
<p align="center">
<a href=" src=" alt="Go Report Card"></a>
<img src=" alt="License: MIT">
<img src=" alt="">
<img src=" alt="Platforms">
</p>
quietscope is a premium, pri, local-only defensi dashboard and CLI security analyzer for system security settings, storage hygiene, and local AI-agent risk surfaces.
In the era of AI coding assistants (like Cursor, Claude Code, Cline, and aider), your local filesystem is exposed to new risk : malicious auto-loaded instructions (.cursorrules, CLAUDE.md), permissi MCP ser, and exposed API tokens. quietscope in these risks, checks standard OS security parameters, performs safe dry-run cleanups, and generates a self-contained interactive HTML dashboard—100% locally with zero telemetry.
---
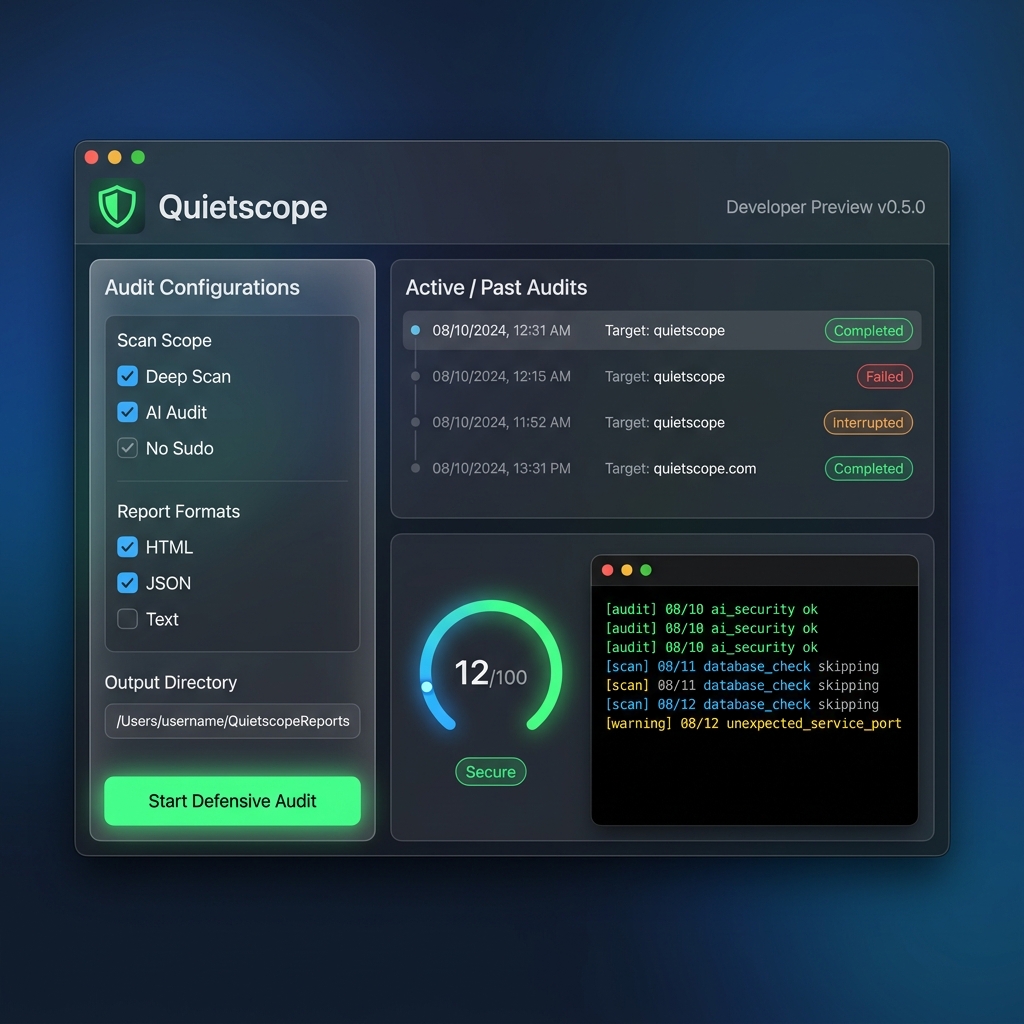
📸 Product Previews
Nati Desktop Dashboard
!Quietscope Desktop App
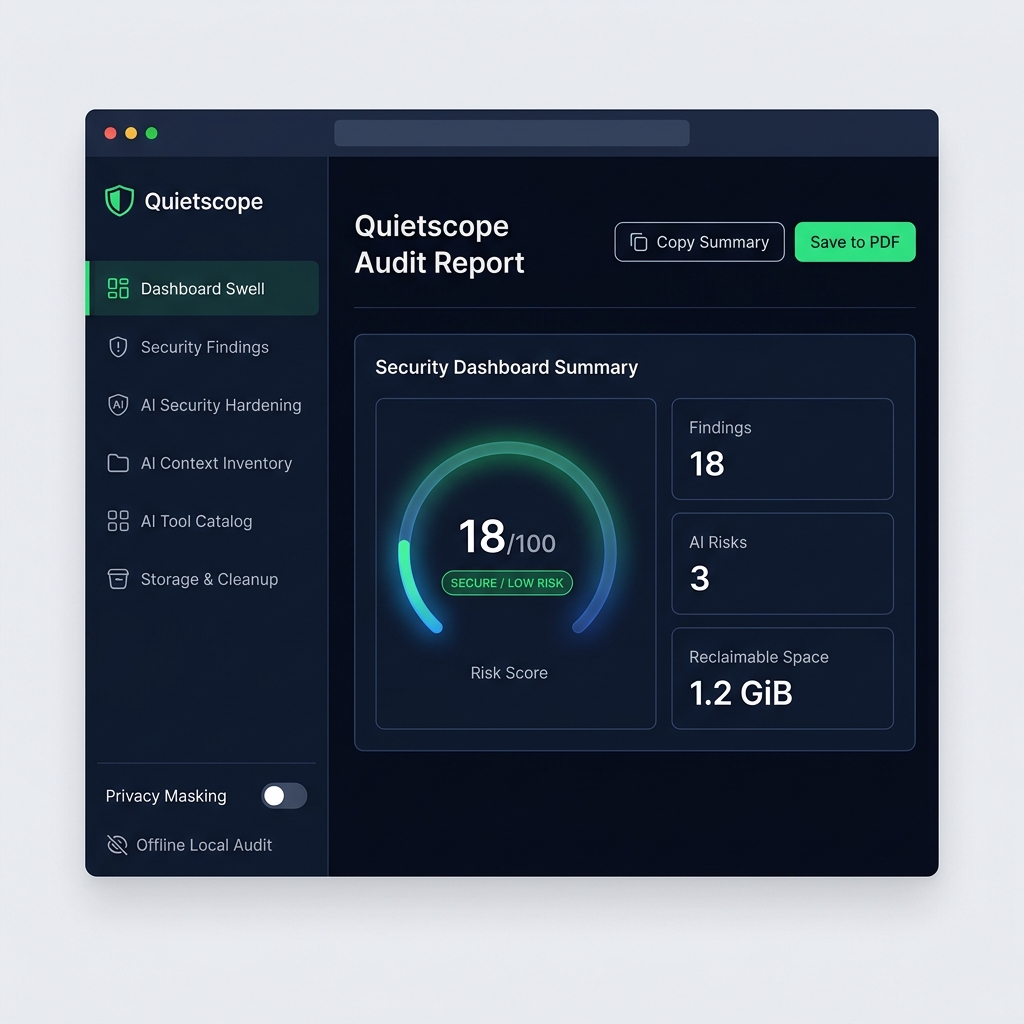
Self-Contained Interacti Report
!Quietscope Interacti
---
> [!IMPORTANT]
> Pri Local Guarantee
> - Zero Telemetry: No tracking, no phone-home, no cookies, and no third-party CDN assets.
> - Exposed Secrets Obfuscation: En with sensiti (e.g., ANTHROPIC_API_KEY) are dynamically masked (*MASKED*) in the report DOM. We never read private keys, SSH files, or actual .env contents.
> - Safe Execution: All OS command e pass through a strict argument-array runner without launching shell wrappers like sh -c.
---
Key Features 🚀
.cursorrules, .cursor/rules, CLAUDE.md, AGENTS.md, GEMINI.md, .agents, .gemini/skills, and manifests to estimate context impact and flag prompt-injection or suspicious patterns.127.0.0.1 only) to configure, execute, and view beautifully structured interacti.AI Control Center Safety Model
mcpServers, servers, command, args, env keys, ser, and related URL/transport fields without executing any discovered command..env files, Keychain data, and SSH/private keys are blocked.---
Quick Start ⏱️
1. Build from Source (Requires Go 1.22+)
2. Run an Audit and Open the Interacti
3. Launch the Audit Control UI in Browser
---
CLI Reference & Flags ⌨️
| Command Flag | Description | Default / Details |
| :--- | :--- | :--- |
| --all-reports | Save TXT, JSON, and HTML reports in the output directory. | Enabled by default |
| --ui | Start local audit control UI on a local loopback server. | 127.0.0.1:8080 only |
| --deep | Enable deeper security scan of project file contents. | Off |
| --no-sudo | Do not invoke or request sudo permissions. | Recommended for daily scans |
| --clean-dry-run | List cleanable system caches and logs without deleting anything. | Safe dry-run |
| --clean-confirm | Execute cleanup (requires typing interacti phrase). | Interactive only |
| --output DIR | Custom directory to sa reports. | ~/Desktop |
| --project-root DIR | Scan an additional local codebase for risky .cursorrules files. | Optional |
| --max-file-size-mb N | Limit size of scanned text files in Megabytes. | 5 |
| -- | Print quietscope . | - |
---
Platform Support Matrix 🖥️
| Operating System | Support Level | Core Scans A |
| :--- | :--- | :--- |
| 🍏 macOS (Darwin) | Full (Primary) | SIP, Gatekeeper, FileVault, launchd persistence, permissions, cache cleanup, AI/MCP audit, interactive HTML. |
| 🐧 Linux | Initial Support | systemd units, cron paths, SSH/sudoers metadata, autostart entries, cache dry-run, AI/MCP audit. |
| 🪟 Windows | Basic Support | Defender, Firewall, UAC status, startup folder registries, local model in, basic reports. |
---
Desktop Application (Wails De Preview) 🎨
We are building a beautiful nati app using Wails. To compile and test it:
1. Install Wails CLI:
2. Na to desktop/ and run de:
3. To compile a nati binary:
---
Contributing 🤝
Contributions are welcome! Please read CONTRIBUTING.md to learn how to add new security checks, write cross-platform checks, or improve the Wails UI.
---
License 📄
This project is licensed under the MIT License - see the LICENSE file for details.
项目信息
开发语言:Go
Star 数:2
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive local security audit tool for macOS, Linux, and Windows. Zero telemetry, zero network, single binary.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | quietscope - Defensive local security audit tool for macOS, Lin |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:19:32 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 481 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |