 防护思路
点击放大
Cyberlson-Scan - A Flask-based defensive cybersecurity toolkit for
项目说明
Cyberlson Scan – Personal Defensi Audit Toolkit
!Python
!Flask
!License
!Status
![Cyberlson Scan Banner] <p align="center">
<img src="static/images/banner.png" alt="Cyberlson Scan Banner" width="100%">
</p>
Project O
Cyberlson-Scan is a web-based, Flask-powered personal defensi audit toolkit designed to empower indi to safely and locally e their own system's security posture. Built with a strong emphasis on secure coding practices and defensi principles, this tool provides insights into system information, open ports, process activity, and password strength, offering actionable recommendations to enhance personal digital security. It is 100% defensi, and educational, explicitly a any offensi, exploit code, or malware.
Features
Cyberlson Scan offers a suite of defensi to help users understand and impro system's security:
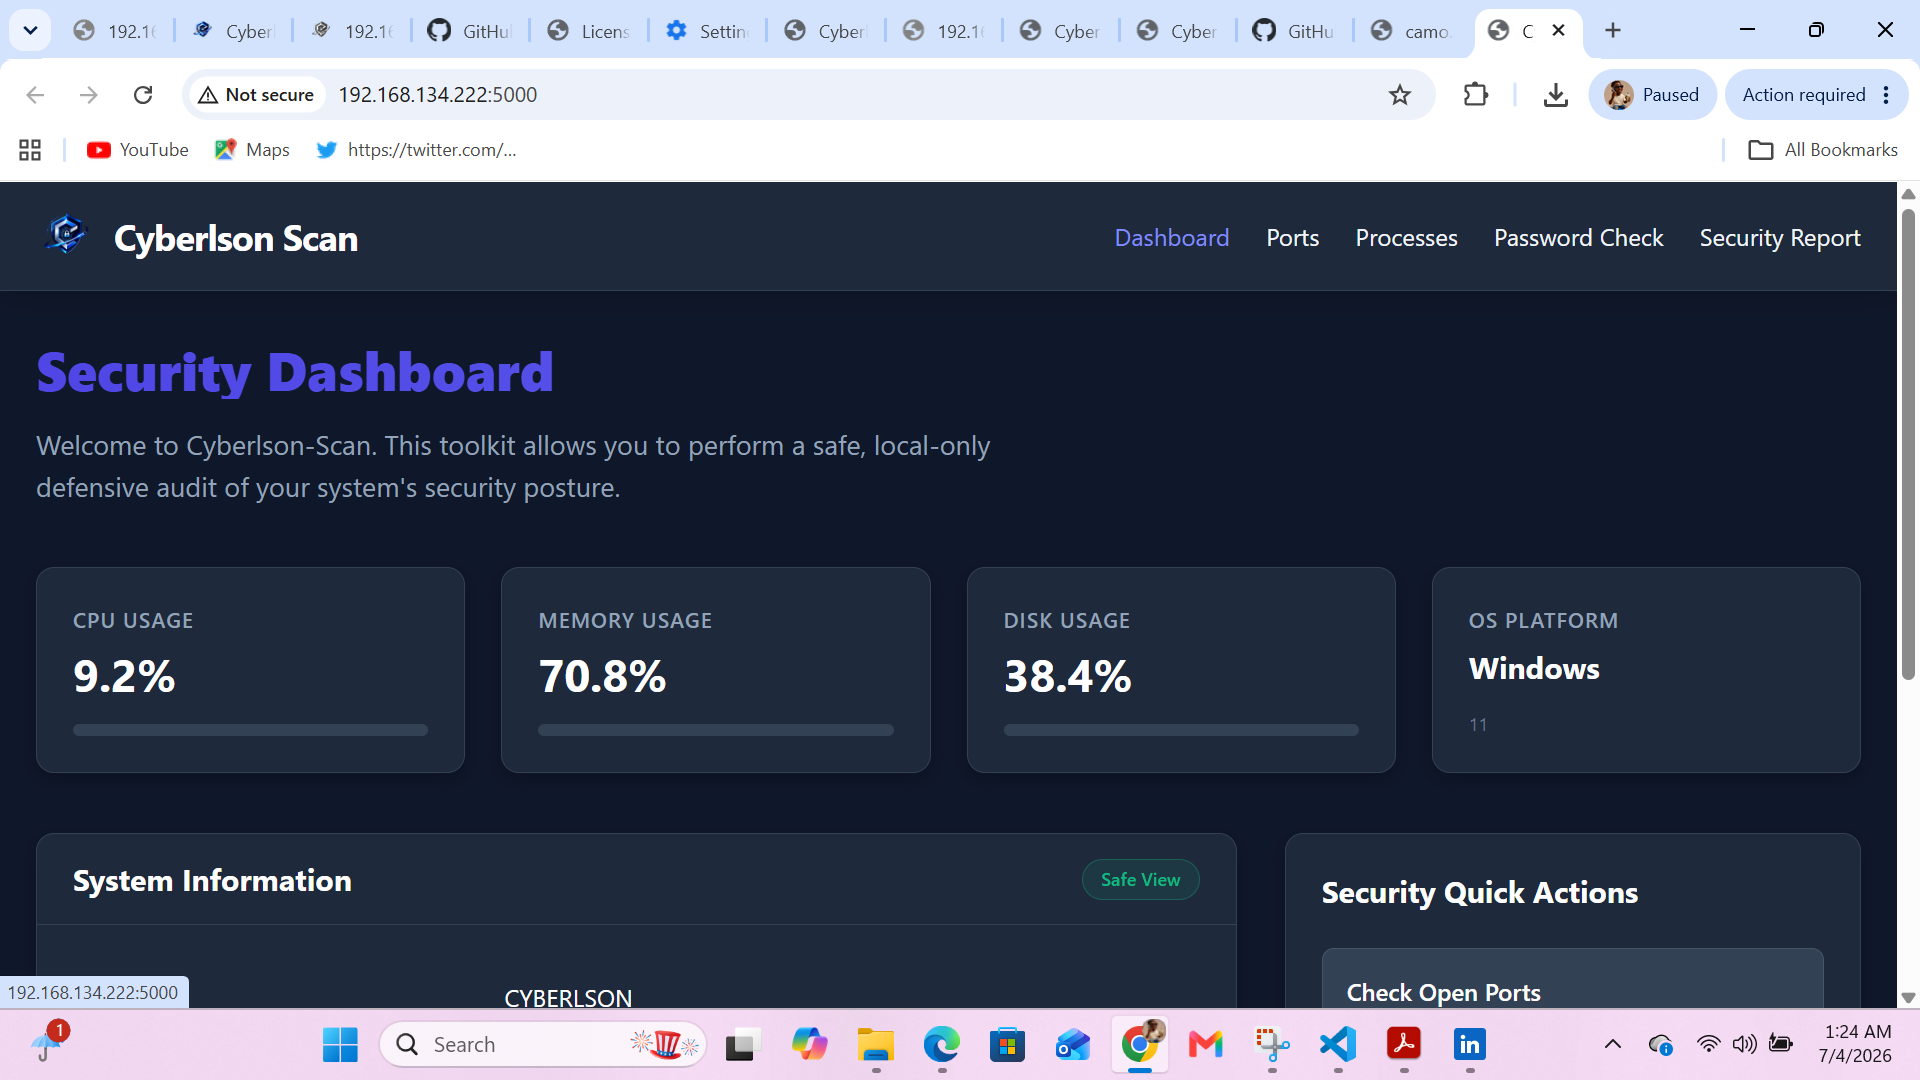
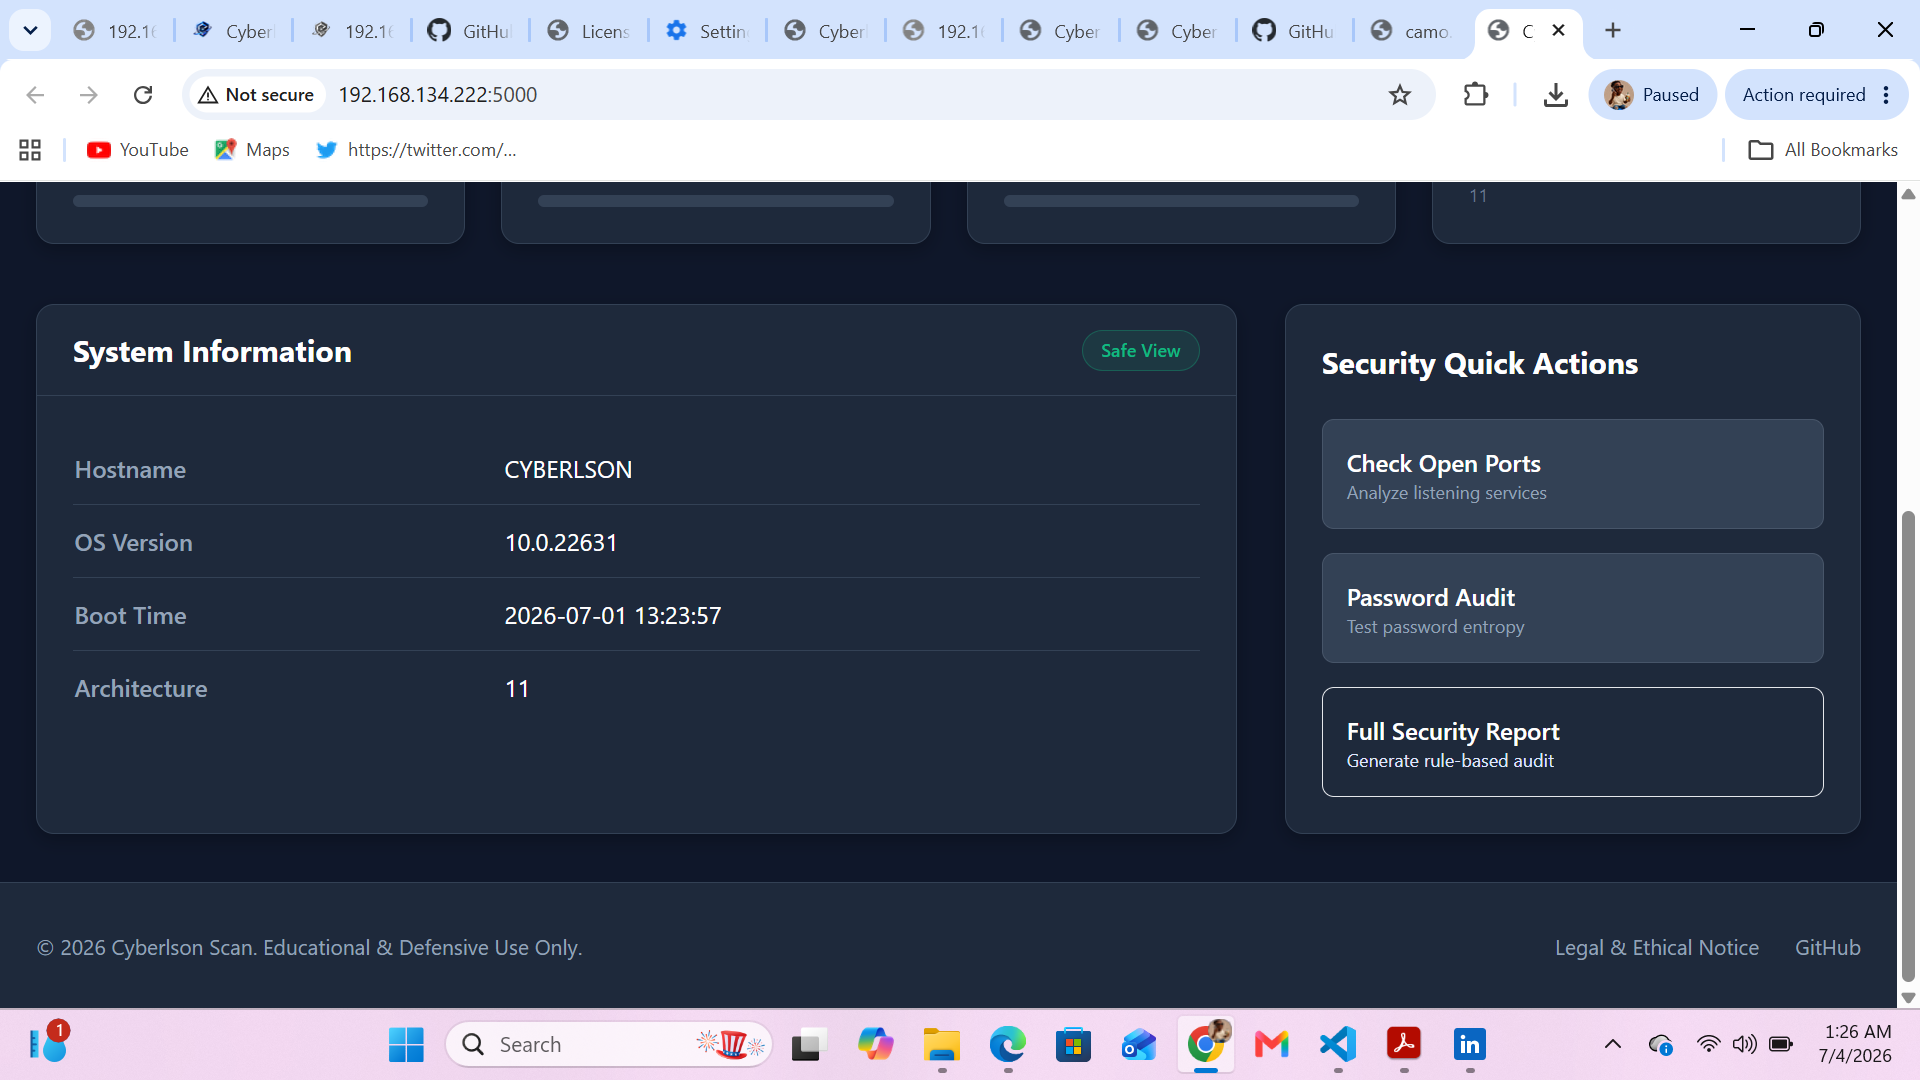
* System Information : Displays essential system details such as OS , CPU, memory, and disk usage, along with running services (read-only).
* Safe Local Port Check: Identifies currently open ports on the local machine, pro clear explanations without aggressi.
* Password Strength Analyzer: E password entropy and detects common weaknesses, offering educational feedback and impro suggestions.
* Process Analyzer: Shows top processes by CPU/memory usage and flags unusual resource spikes with educational context.
* Security Recommendations Engine: Provides rule-based suggestions (e.g., firewall checks for many open ports, password manager recommendations for weak passwords).
* Generate Security Report: Creates a downloadable PDF report with a summary risk score, timestamp, and professional formatting.
* Legal & Ethical Notice Page: Clearly outlines the tool's purpose for personal defensive use only, prohibiting unauthorized testing or network-wide scanning.
Architecture O
Cyberlson Scan follows a modular Flask architecture that separates the user interface, application logic, system analysis, and report generation.
Project Structure
Security Considerations
Cyberlson Scan is built with security as a paramount concern, adhering to De best practices and OWASP secure coding guidelines. Key security measures include:
* En : All sensiti (e.g., SECRET_KEY) are loaded from en , pre hardcoding of secrets.
* Flask Production Configuration: Configured for production en, disabling debug mode and enabling robust error handling.
* CSRF Protection: Implemented using Flask-WTF to protect against Cross-Site Request Forgery attacks.
* Input & Sanitization: All user inputs are sanitized and to prevent common like XSS (Cross-Site Scripting) and SQL Injection (though no database is used, this is a general best practice).
* Secure Headers: Utilizes Flask-Talisman to enforce HTTP Strict Transport Security (HSTS) and Content Security Policy (CSP), mitigating web-based attacks.
* Safe Subprocess Usage: System interactions are performed via psutil, which provides a safe, cross-platform interface for system information, a direct, potentially unsafe subprocess calls.
* Error Handling: Comprehensi handling is in place to prevent information leakage and ensure application stability.
* Defensi Design: The core philosophy ensures no offensi, network scanning beyond localhost, or any potentially illegal functionalities are included.
Application Screenshots
Home Page
!Home Page
---
Analysis Dashboard
!Analysis Dashboard
---
PDF Security Report
!PDF Report
---
Security Recommendations
!Recommendations
Installation Instructions
1. Clone the repository (or download the project files):
2. Create a Python En:
bash
python3 -m venv venv
source venv/bin/activate
powershell
python -m venv venv
ven\activate
bash
pip install -r requirements.txt
bash
cp .en .env
ini
SECRET_KEY='your_ret_key_here'
FLASK_CONFIG='de'
bash
flask run
# Or using the provided run.py:
# python run.py
``
The application will typically be a at .
Usage Instructions
Na to the application in your web browser. The intuiti allows you to:
* View system statistics on the Dashboard.
* Check for listening ports under the Ports section.
* Analyze running processes in the Processes tab.
* Test the strength of a password on the Password Check page.
* Generate a comprehensive Security Report with personalized recommendations.
* Review the Legal & Ethical Notice for proper usage guidelines.
Deployment Instructions
Refer to DEPLOYMENT.md for detailed instructions on deploying Cyberlson Scan to production en.
Future Impro
* Ad Process Analysis: Implement more sophisticated logic for flagging suspicious process behavior (e.g., processes running from unusual directories).
* File Integrity Monitoring (Local): Add a feature to monitor critical system files for unauthorized changes (read-only, hash-based).
* Scheduled Scans: Allow users to schedule regular security checks and recei reports.
* User Authentication (Optional): For multi-user en (e.g., small teams), implement secure user authentication and role-based access control.
* Enhanced UI/UX: Further refine the user interface with more interacti and .
Contribution Guidelines
We welcome contributions to Cyberlson Scan! Please follow these steps:
1. Fork the repository.
2. Create a new branch for your feature or bug fix.
3. Ensure your code adheres to secure coding practices and passes all tests.
4. Submit a pull request with a clear description of your changes.
License
This project is licensed under the MIT License. See the LICENSE file for details.
Professional GitHub Project Description
Cyberlson-Scan: is a Flask-based defensi toolkit for local system security auditing. It provides system monitoring, local port , password strength analysis, process inspection, and automated security recommendations while following secure coding and De best practices.
Suggested GitHub Tags
python, flask, cybersecurity, security-audit, defensi, de, web-application, system-monitoring, password-security, personal-security, education, mit-license`
---
Author
Abdulmajid Bello
Founder, Cyberlson Team Tech
Contact
项目信息
开发语言:HTML
Star 数:2
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A Flask-based defensive cybersecurity toolkit for personal system security auditing, featuring system monitoring, local port visibility, password analysis, process inspection, and automated security recommendations.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Cyberlson-Scan - A Flask-based defensive cybersecurity toolkit for |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:19:50 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 460 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |