 防护思路
点击放大
deep-security-check - Defensive, read-only security assessment skill for
项目说明
<di="center">
🛡️ deep-security-check
A defensi security assessment for any local project — with a _reproducible_ reliability grade.
Point it at a codebase. It runs best-in-class open-source scanners and returns a graded report (0–100, A–F) where the number comes from a deterministic rubric, not model opinion.

![]()


![Claude Code]()
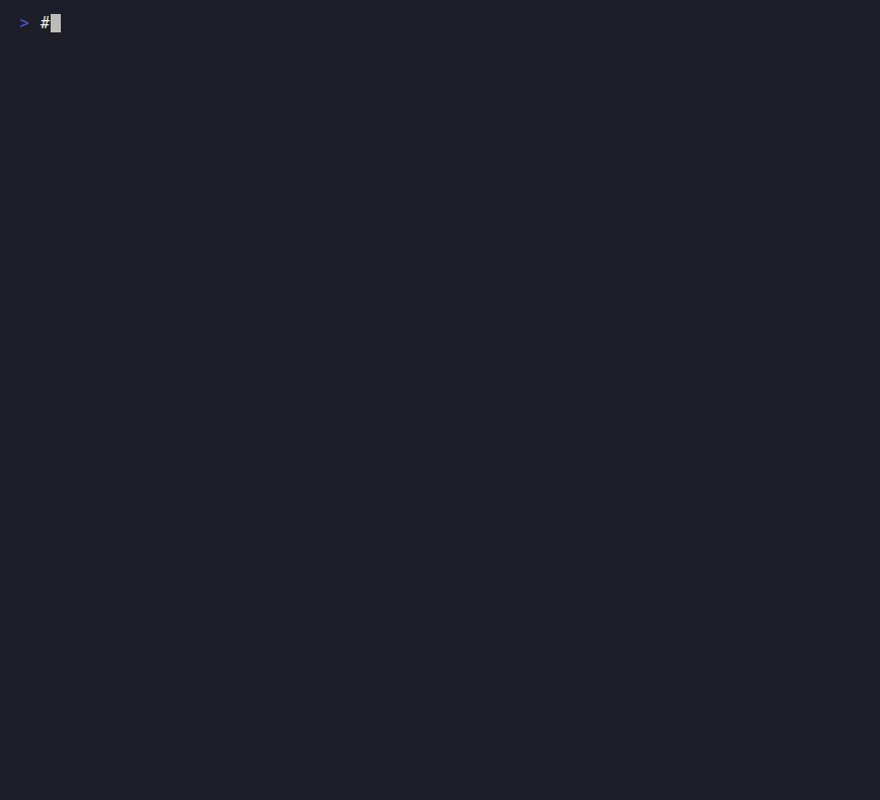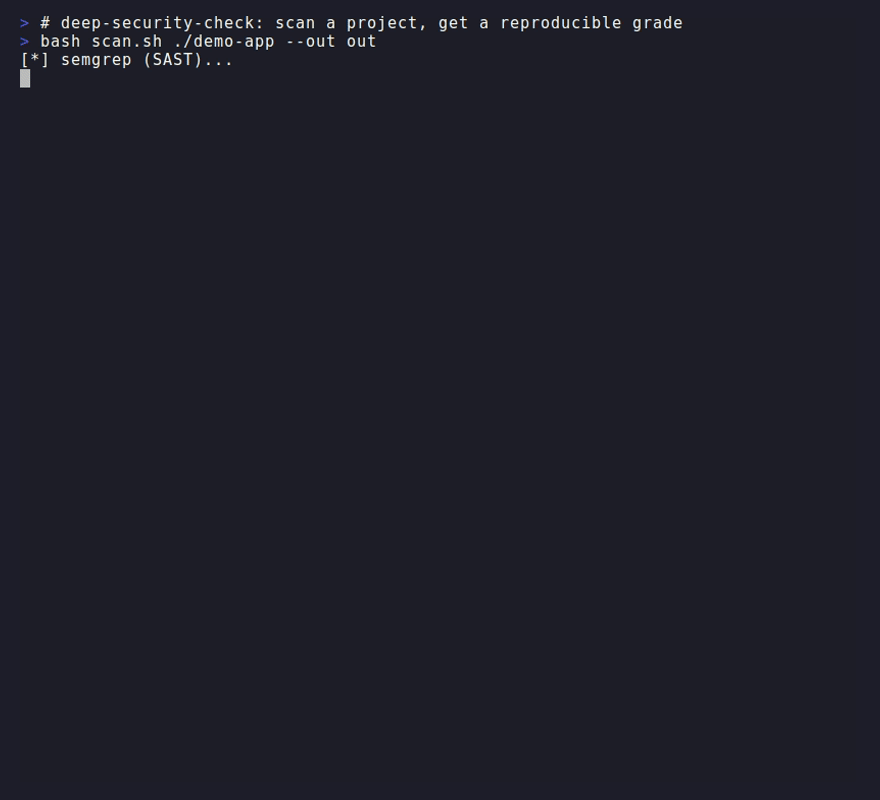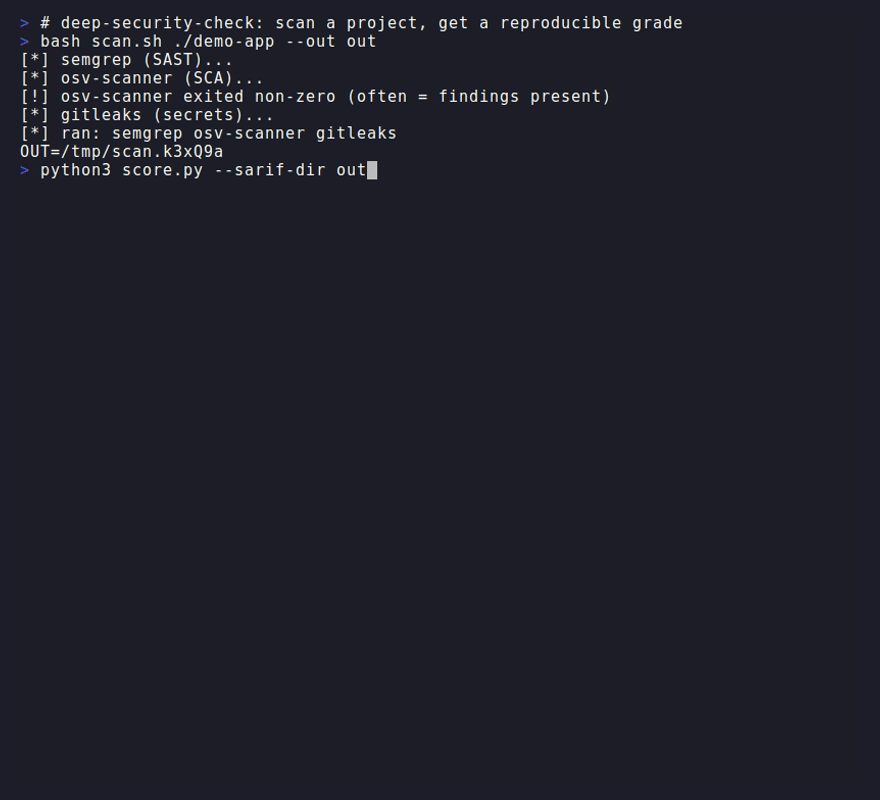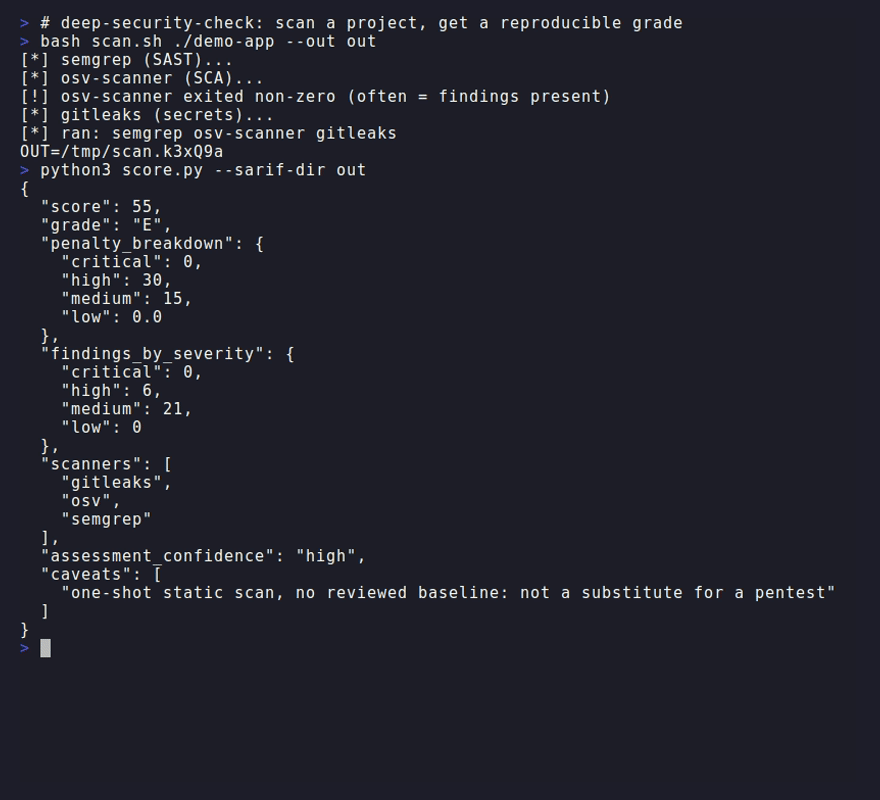
!deep-security-check demo: scan a project, get a reproducible grade
</div>
---
Contents
💡 Why
Ask an AI "is this project secure?" and you get a plausible-sounding essay that
changes every time you ask. That is not a measurement.
deep-security-check gives you a number you can reproduce and defend: a
small Python script owns the scoring with fixed penalties and hard ceilings, so
the same findings always produce the same grade. The model narrates the results
— it ne the number.
🚀 Quick start
Then just ask Claude:
> *"How reliable is this project, security-wise?"*
<sub>Installing from a local clone instead? /plugin marketplace add /path/to/security-scan-skill</sub>
🔍 What it runs
| Layer | Tool | What it catches |
|-------|------|-----------------|
| SAST | Semgrep — or Opengrep (LGPL fork) as a drop-in when semgrep is absent | Injection, unsafe deserialization, weak crypto, CI/CD & IaC misconfig |
| SCA | os — trivy as fallback | Known CVEs and malicious packages in your dependencies |
| Secrets | gitleaks ( fallback bundled) | Hardcoded credentials — in the working tree and the git history |
Plus three ad passes that ne the grade:
surface.py) — a static, zero-traffic map of where a DAST run *would* look (permissive CORS, missing security headers, insecure cookies, debug/bind-all).structure.py) — README, LICENSE, tests, CI, lockfiles, pinned deps, committed .env, SECURITY.md, dependabot/renovate, Dockerfile root user.syft when present.📊 The grade
score.py owns the number, so it is deterministic. Start at 100, subtract capped
per-se penalties over all findings, then apply hard ceilings:
| se | penalty each | cap |
|----------|:------------:|:---:|
| 🔴 critical | 25 | 60 |
| 🟠 high | 8 | 30 |
| 🟡 medium | 1.5 | 15 |
| ⚪ low | 0.25 | 6 |
Ceilings — any critical → score ≤ 69 · any high → score ≤ 84 · any malicious package → score ≤ 20.
| Grade | Range | Meaning |
|:-----:|:-----:|---------|
| A | 90–100 | Solid |
| B | 80–89 | Solid, minor debt |
| C | 70–79 | Manageable debt |
| D | 60–69 | Real risk |
| E | 50–59 | Real risk |
| F | <50 | Not trustworthy until fixed |
assessment_confidence tells you how much to trust the score itself: high only
when all three scanner classes ran. A one-shot static scan is never a substitute
for a pentest — and the report says so.
> Reproduce the rubric by hand, or run python3 …/score.py --selfcheck.
🧹 Noise reduction
So the grade reflects real risk, not scanner o:
file:line flagged by two tools counts once.tests/, fixtures/, examples/, mocks/ … are downgraded one se step (a hardcoded credential in a fixture is not a production leak).MAL-* ad are surfaced as malicious_packages, separate from CVEs, and hard-cap the score. A malicious dependency dominates e.The triage field in the report shows exactly what was deduped and downgraded.
Two more passes are opt-in via --project <dir> on score.py:
declared-but-unused). Heuristic and conser: it ne a finding, only downgrades on a confident zero-match..dsc-ignore — suppress accepted findings with a mandatory justification (<path-glob>:<ruleId-or-*> -- why). Suppressed findings are listed in the report with their reason; a rule missing its justification is rejected, not applied. Suppression stays , ne.🧰 Requirements
At least one scanner on your PATH — more installed → higher confidence:
| Tool | Install |
|------|---------|
| Semgrep | pipx install semgrep |
| os | releases |
| gitleaks | releases — * fallback included* |
Optional, used automatically when present: trivy (SCA fallback), syft (SBOM), opengrep (drop-in SAST engine).
🔌 Works offline / behind a proxy
Egress-restricted en (corporate proxies, the Claude Cowork sandbox)
degrade gracefully instead of hanging or failing:
rules/offline-basic.yaml, ~30 high-precision rules incl. CI/CD & IaC). Reduced co — and the report says so.<sub>Knobs: DSC_SEMGREP_CONFIG (local ruleset), DSC_SEMGREP_TIMEOUT, DSC_TRI, DSC_SKIP_HISTORY.</sub>
🖥️ Use it without Claude
The scripts are plain bash + Python with no project-specific dependencies:
Re-scanning over time? Add --baseline <old.json> to score.py for a delta (improved / worsened, per-se).
✅ Guarantees
📄 License
MIT. See also PRIVACY.md · ROADMAP.md · SECURITY.md.
项目信息
开发语言:Python
Star 数:2
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive, read-only security assessment skill for Claude Code (Semgrep + osv-scanner + gitleaks) with a reproducible reliability grade (0-100, A-F).展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | deep-security-check - Defensive, read-only security assessment skill for |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:20:37 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 149 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |