 防护思路
点击放大
shai-hulud-detector - 🛡️ Advanced NPM supply chain attack detection tool
项目说明
![License: MIT]()
![Node.js]()
![TypeScript]()
![CLI Tool]()
![Security Scanner]()
![Defensi]()
![npm Supply Chain]()
![Malware Detection]()
![Platform: Cross-platform]()
![Build Tool: Yarn]()
![PRs Welcome]()
<table border="0" style="border: none; background: transparent;">
<tr style="border: none; background: transparent;">
<td style="border: none; background: transparent; text-align: center;">
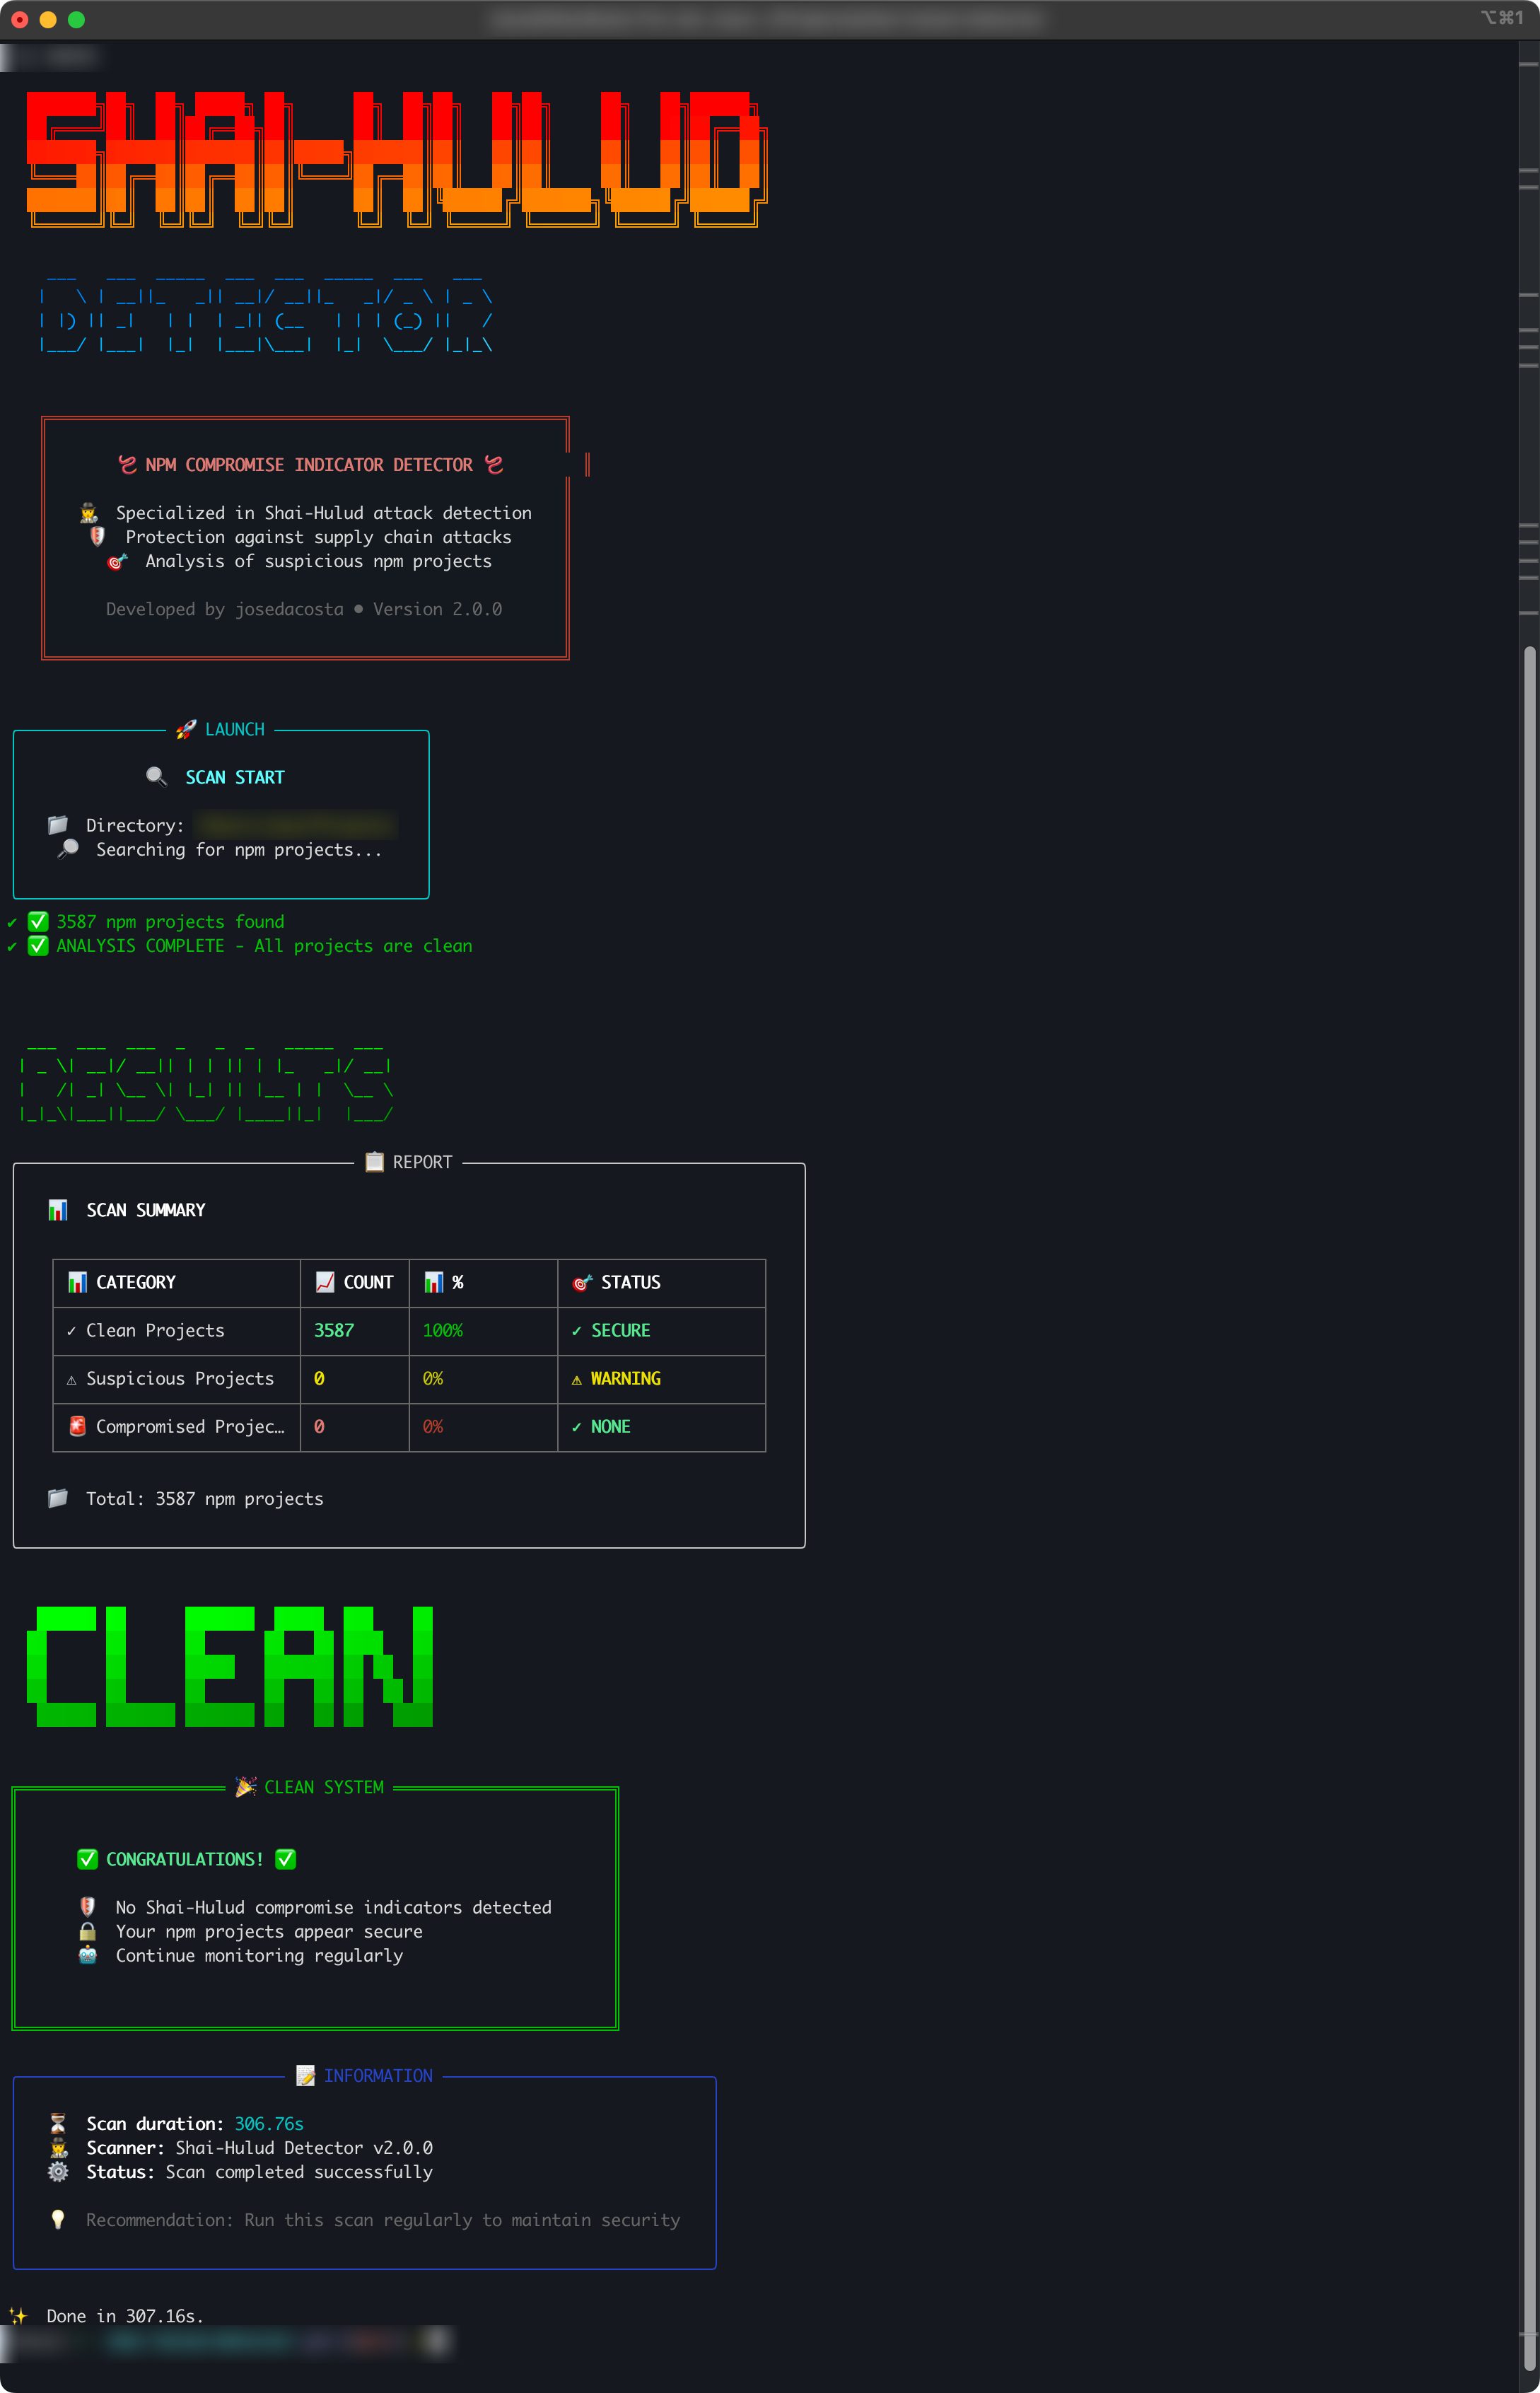
<img src="assets/img/clean.png" alt="Clean Project Status">
</td>
<td style="border: none; background: transparent; text-align: center;">
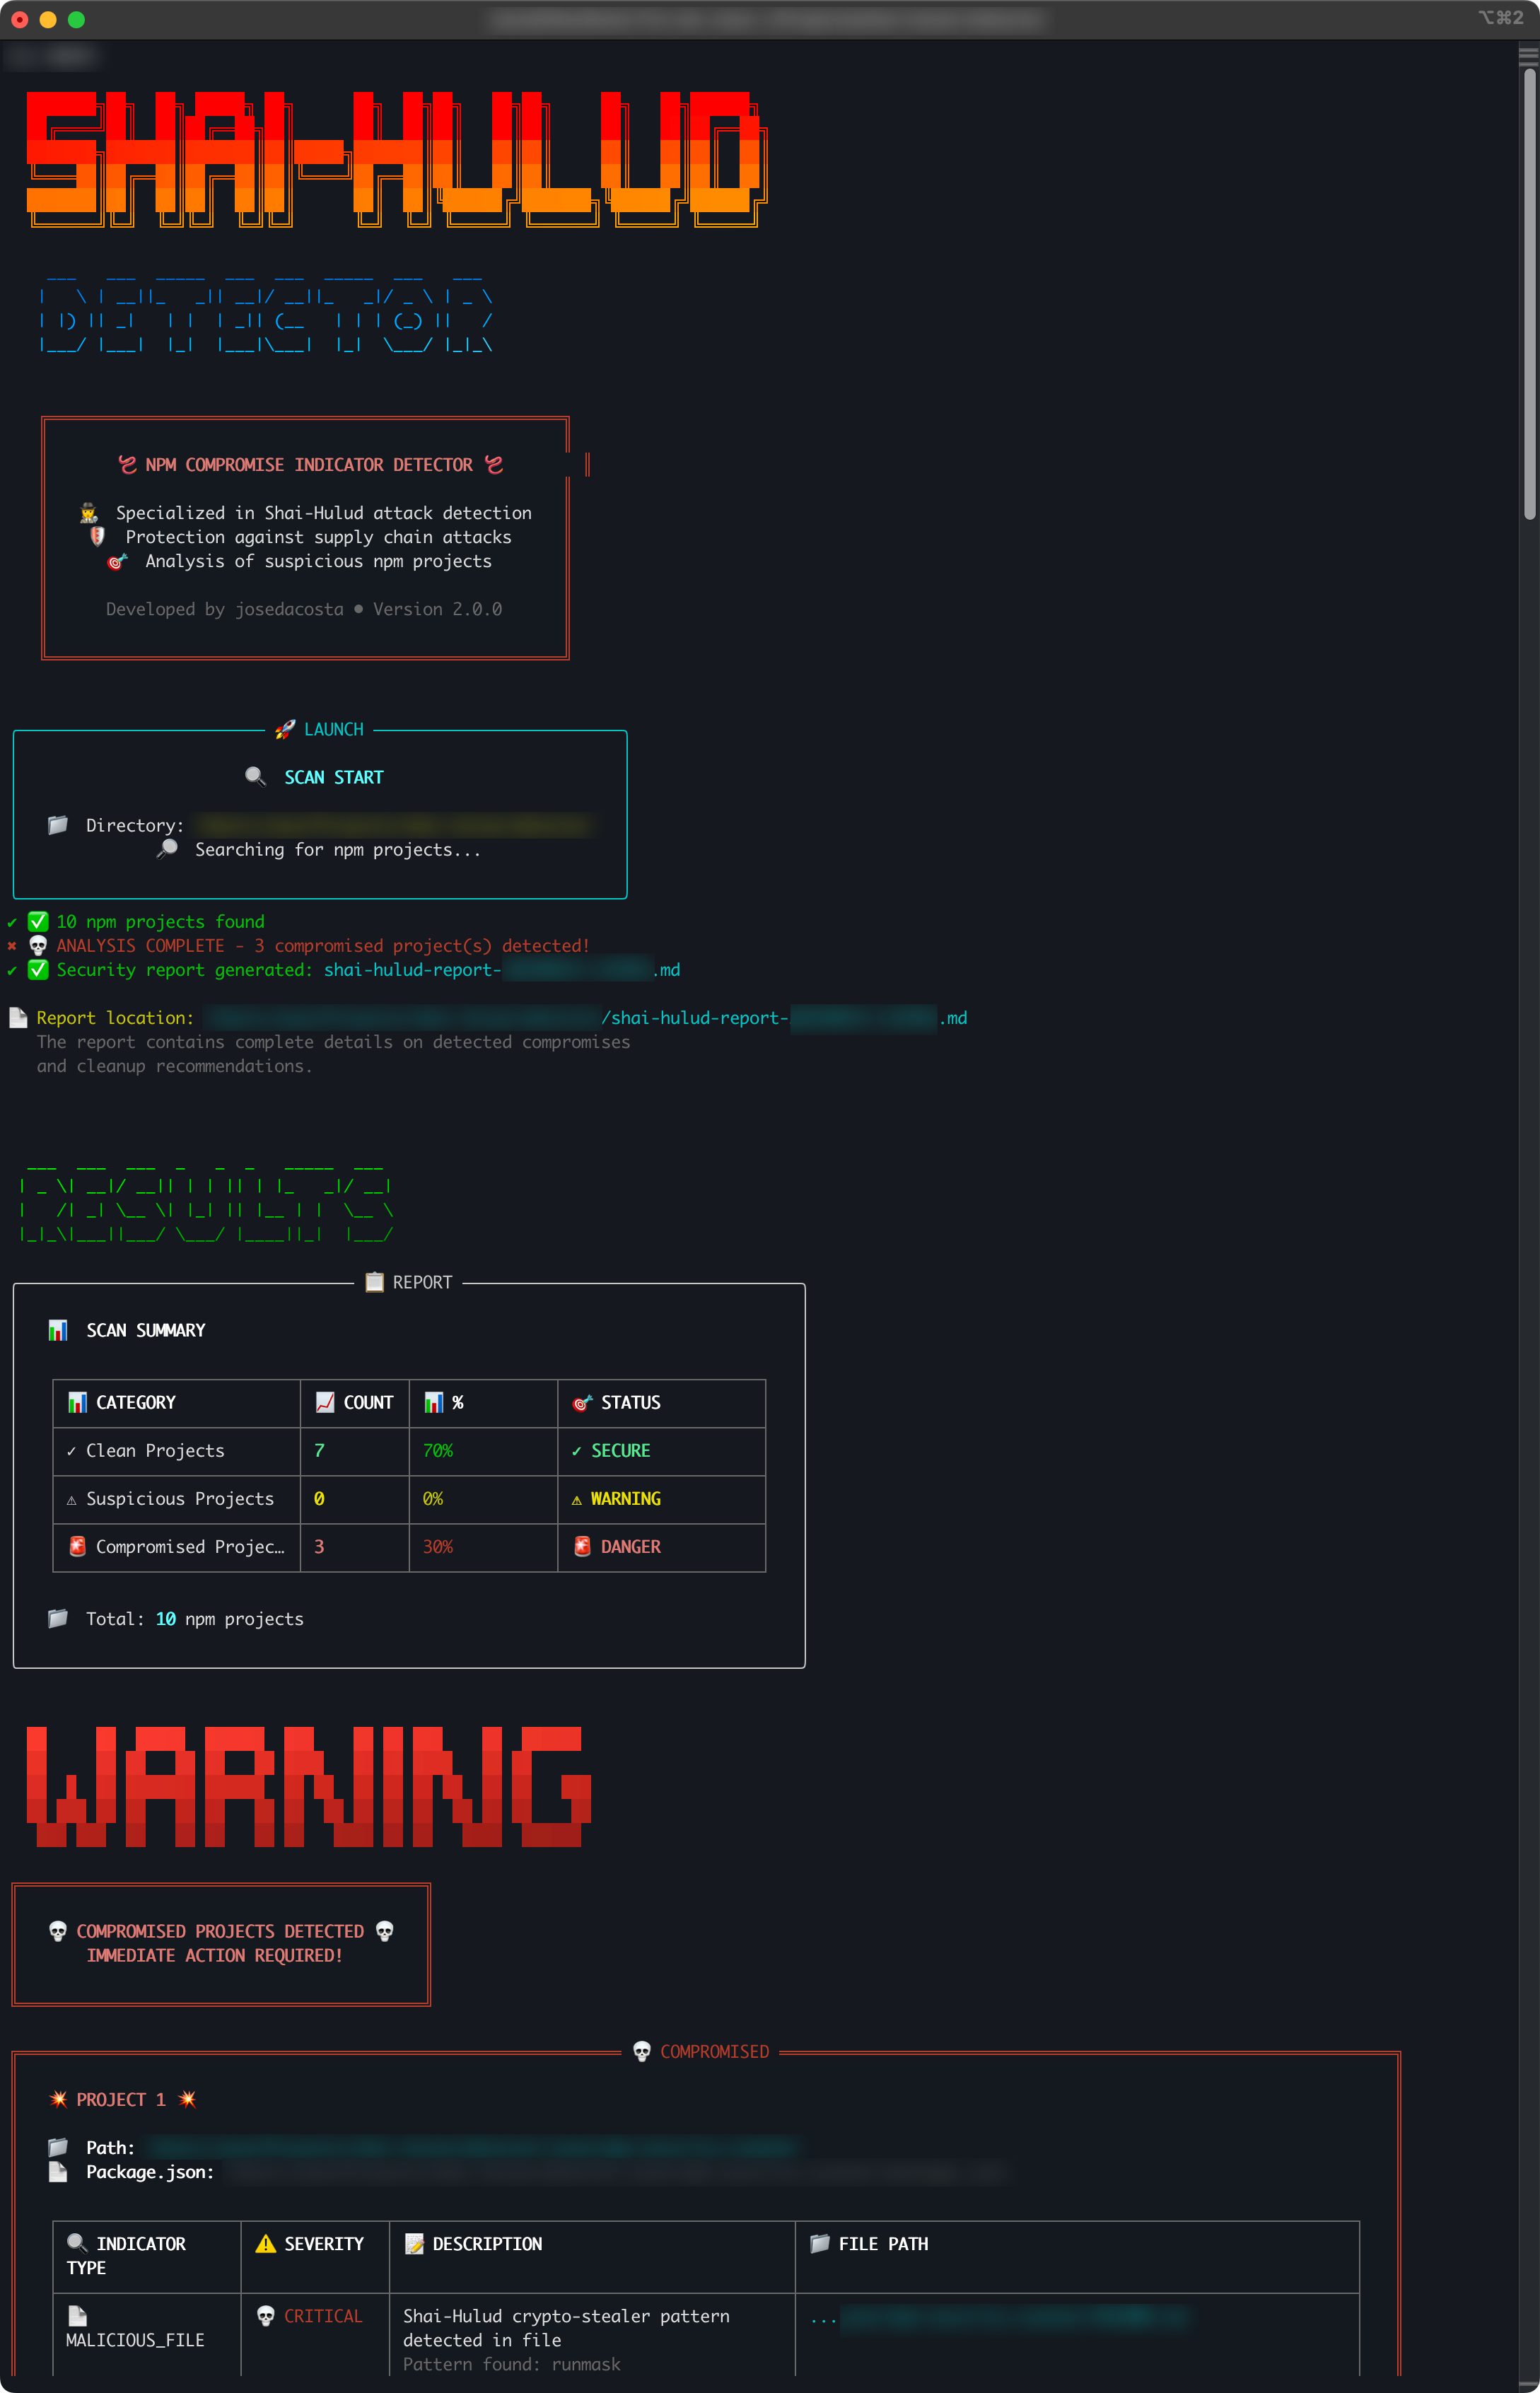
<img src="assets/img/warning.png" alt="Warning Project Status">
</td>
</tr>
</table>
Shai-Hulud Detector
A detection tool for compromise indicators of the Shai-Hulud attack in npm projects.
📖 Description
Following major attacks on the npm ecosystem in 2025, notably the sophisticated "Shai-Hulud" attack, this tool allows you to scan your system for
potentially compromised npm projects.
The detector analyzes:
package.json files📚 References
> [!CAUTION]
> For more information about the Shai-Hulud attack
>
> Check the NEWS.md file which contains a complete and detailed analysis of the Shai-Hulud attack, including the timeline of
> events, technical analysis and compromise indicators.
Based on analysis of documented attacks in:
📦 Installation
🚀 Usage
Interactive mode (default)
Command line mode
⚙️ Options
-d, --directory <path> : Directory to scan (default: /)-e, --exclude <dirs> : Directories to exclude from scan (comma-separated: dir1,dir2,dir3)- : mode with additional details-j, --json : JSON output format--no-interactive : Disable interactive mode🔍 Detected indicators
Malicious files
bundle.js files larger than 3MB with known SHA-256 hashnode-gyp.dllshai-hulud-workflow.ymlSuspicious scripts
stealthProxyControl, runmask, checkethereumw)0xFc4a4858bafef54D1b1d7697bfb5c52F4c166976GitHub workflows
webhook.site📊 Se levels
📈 Project statuses
🛠️ De
🔒 Security
This tool is designed for defensi only. It helps identify potentially compromised projects without exposing sensiti.
⚠️ Disclaimer
IMPORTANT: READ-ONLY TOOL
This detection tool operates in READ-ONLY MODE ONLY. It NEVER modifies, deletes, or creates any files in the scanned directories. The tool
only reads and analyzes existing files to detect compromise indicators.
What the tool does:
What the tool NEVER does:
LIMITATION OF LIABILITY
We are not responsible for any deterioration or damage to any files or systems that may occur during the execution of this tool. While we have made
our best efforts to ensure the tool operates safely in read-only mode, you remain fully responsible for its execution and any consequences thereof.
By using this tool, you acknowledge that:
🤝 Contributing
Contributions are welcome! Feel free to open an issue or pull request on GitHub.
📋 Issues and Support
To report a problem or request a feature, visit: GitHub Issues
📜 License
MIT - See the LICENSE file for more details.
---
🏷️ Keywords
<details>
<summary><b>🔍 SEO Keywords</b> (click to expand)</summary>
Shai-Hulud Attack & Detection:shai-hulud attack • shai-hulud detector • shai-hulud malware • shai-hulud npm attack • shai-hulud scanner • detect shai-hulud •shai-hulud compromise • shai-hulud indicators • shai-hulud security tool • shai-hulud analysis
Security Scanning & Analysis:npm security scanner • nodejs security tool • package.json analyzer • malware detector npm • compromise detection tool •supply chain attack detector • malicious package detector • crypto stealer detection • github actions malware • npm project scanner
Malware & Compromise Detection:detect malware npm • find compromised packages • scan infected projects • malicious bundle.js • node-gyp.dll malware •crypto wallet stealer • ethereum address stealer • suspicious npm scripts • compromised dependencies • infected node modules
Clean Code & Security : clean code • check code integrity • scan for malware • code security audit • project security check • npm security audit •detect code injection • malicious code scanner • security scanner • code compromise detection
Technical Security Keywords:npm supply chain attack • package.json security • malicious scripts detector • github workflow injection • crypto stealer patterns •suspicious file hash • malware signature detection • security indicators analysis • threat detection tool • compromise assessment
De Security Tools:security cli tool • malware detection cli • npm security cli • project security scanner • de security tool •security analysis tool • malware scanner nodejs • package security checker • dependency security audit • code security
</details>
项目信息
开发语言:TypeScript
Star 数:2
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🛡️ Advanced NPM supply chain attack detection tool - Specialized in detecting Shai-Hulud compromise indicators with beautiful CLI interface and automated security reporting展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | shai-hulud-detector - 🛡️ Advanced NPM supply chain attack detection tool |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:23:09 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 468 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |