 防护思路
点击放大
AttackMap - AI-assisted defensive security analysis for codeba
项目说明
AttackMap
> [!IMPORTANT]
> Acti, slow pace. AttackMap is under acti, but
> progress may be slow until more contributors or co-maintainers join. Help is
> very welcome with the core engine, an analyzer, the macOS app, or the docs —
> see CONTRIBUTING.md or open an issue on
> mlaify/AttackMap to say hello.
> Security reports are still welcome at .
Local-first, AI-assisted defensi analysis for codebases. AttackMap
reads a repository (or a whole fleet of them), reconstructs the attack surface —
routes, data stores, external calls, auth signals, trust boundaries — traces
request-to-sink data flow, and produces an e, prioritized security
review. It finds the cross-cutting weaknesses single-file scanners miss, and never
sends your code anywhere.

![Python: 3.11+]()
> Status: beta (v0.5.0). Core engine + 15 analyzer plugins, installed straight
> from GitHub and on real codebases. AttackMap is heuristic by
> design — findings are confidence-tiered e, not proof. Roadmap to 1.0:
> issue #209.
Full documentation: docs.mlaify.io ·
architecture & internals: wiki.
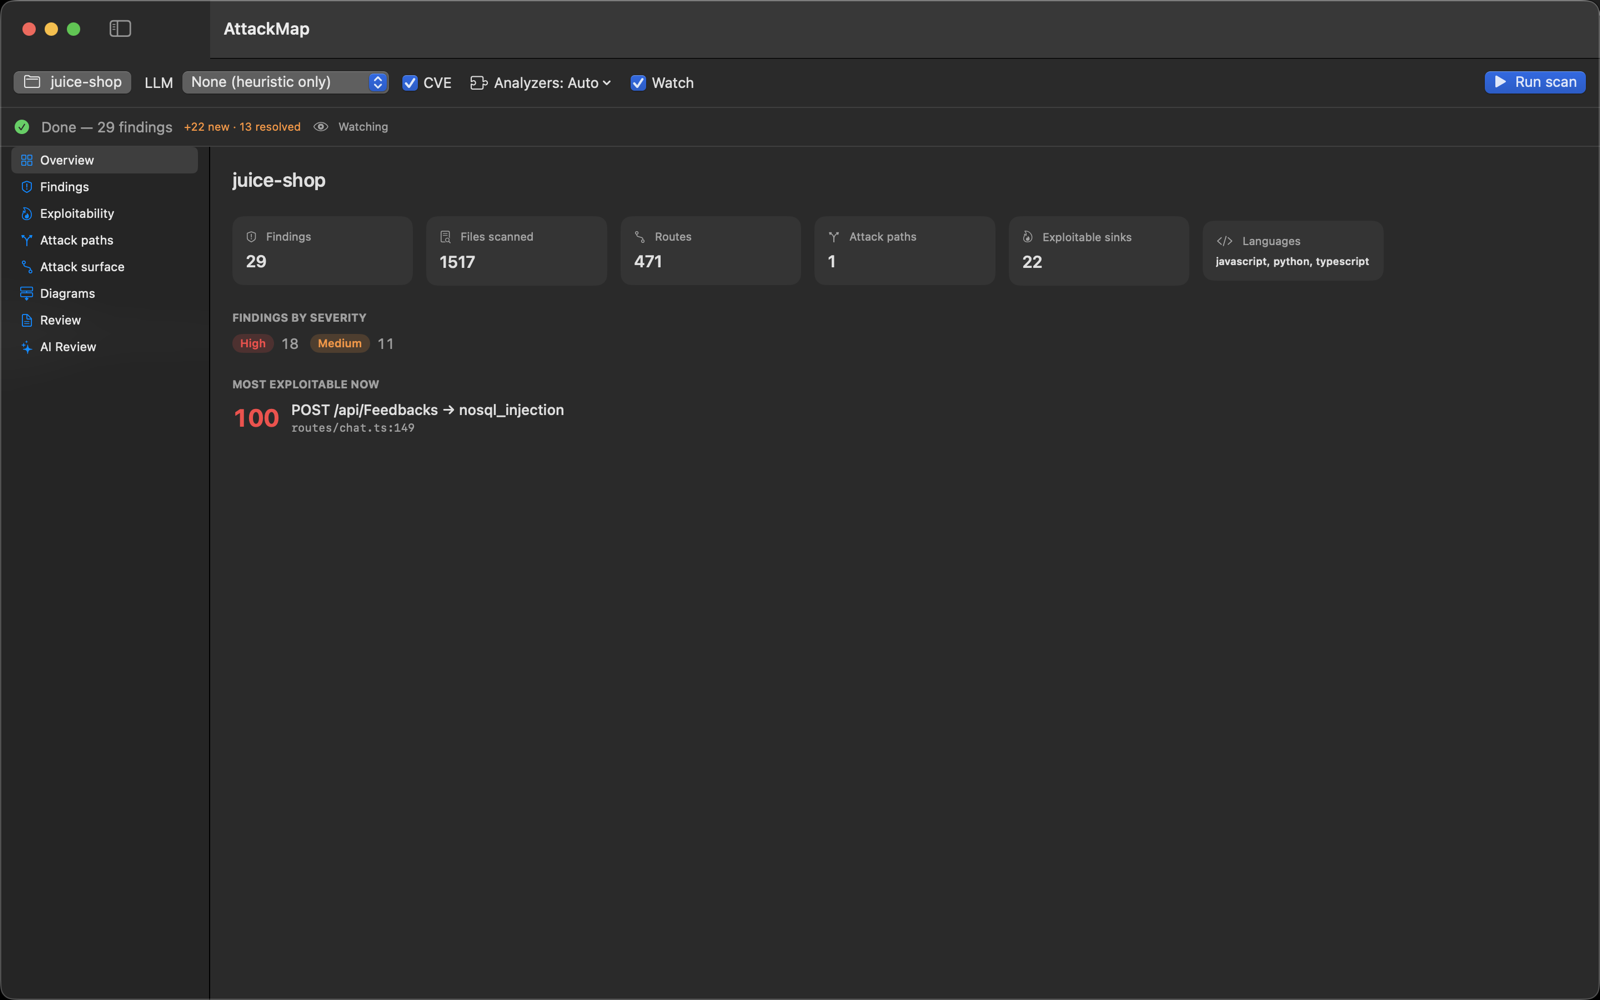
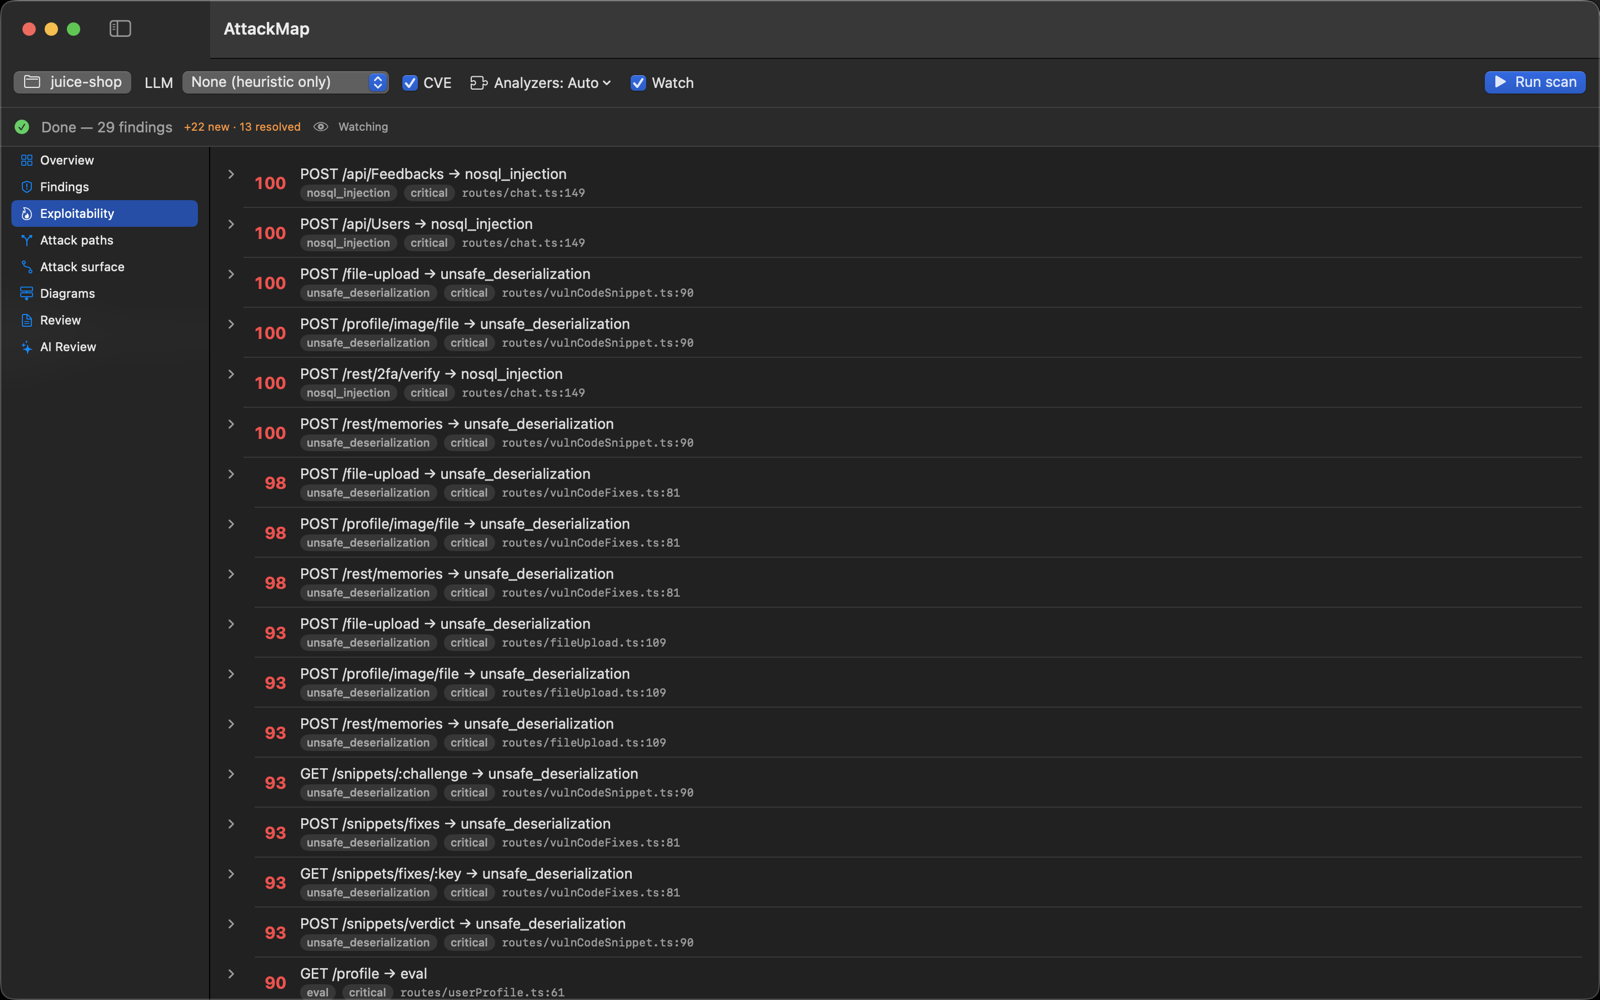
The macOS app
Prefer a GUI? A nati front-end drives this CLI and renders every result
view. Install it with Homebrew (this also installs the CLI), or build it from
source at mlaify/AttackMap-mac:
| O | Exploitability |
|---|---|
| ![AttackMap macOS app — o]() | ![AttackMap macOS app — exploitability]() |
*Scanning OWASP Juice Shop. Walkthrough in the macOS app docs; source at mlaify/AttackMap-mac.*
Quickstart
Read reports/defensi.md for the heuristic review, and (with --llm)reports/defensi.md for the AI narration. --llm resolves auth
automatically (ANTHROPIC_API_KEY, or your Claude/codex CLI subscription); add--llm-provider openai for OpenAI/Codex.
Other install paths: pip install git+ (core
only), or the [llm] extra for AI narration. Not sure
which analyzer plugins a repo needs? attackmap suggest ./repo. Full install and
CI setup: install guide.
What it finds
secrets, frameworks, entrypoints; every signal carries a
file:line citation,e snippet, and confidence.
SQL, shell, eval/code and expression (SpEL/OGNL) injection, JNDI, SSRF, SSTI,
NoSQL, LDAP, XPath, path tra and zip-slip, deserialization, open
redirect, header and regex injection — traced source → → sink
inside each handler, with flow-bound sanitizers, SARIF
codeFlows, aplugin-extensible sink registry (
taint_sinks.yaml), and a deterministic0–100 exploitability score.
insecure upload, GraphQL exposure; BOLA/IDOR authorization; insecure-crypto
& web-hardening; anomaly/outlier + signature-free in mining.
--cve) — SBOM + lockfile resolution against OSV.dev,folded into the exploitability score.
--hunt -- (a multi-pass, majority-vote LLMjury),
--recall, and cross-repo / fleet analysis:confused-deputy flows, trust-assumption gaps, and the sibling service that omits
a control its peers enforce.
--triage, --remediate, finding suppression, baseline diffgating, SARIF + Mermaid/Graph, and a GitHub Action + PR bot.
Each run writes Markdown, JSON (attackmap-report.json), SARIF 2.1.0, and
diagram artifacts; fleet runs add fleet-summary.{md,json} + fleet-graph.md.
See the outputs reference for the full list.
Supported ecosystems
Fourteen analyzer plugins (each installable on its own; [all] installs every one):
Python, Ja/TypeScript (Node services), Go, Ja
(Spring), C# (ASP.NET Core), Rust, PHP (web / Laminas / Omeka-S),
C, C++, Terraform, IaC (Docker / compose / GitHub Actions),
AT Protocol. Specialty and experimental analyzers are opt-in: when one
matches a repo, analyze says so, and -m <name> runs it (attackmap modules
shows which). Details: analyzers reference.
Write your own against the documented analyzer SDK.
CLI cheat-sheet
knobs (-- / --hunt-lenses / --hunt-rounds /--hunt-budget) and suppression (--no-suppress / --suppress-file) are
documented in the CLI reference.
What AttackMap is *not*
SIEM team, not deployable rules.
--cve folds C into anarchitecture-aware narrati/Grype/Dependabot go deeper on resolution.
function (intra-procedural def-use) and a call-graph-refined import walk
*across* files; it does not follow a value into a helper it is passed to, and
branches are not distinguished. Precision o; findings are e,
not proof. See the limits in
src/attackmap/taint_flow.py.guardrails for stale signals.
Documentation & links
analyzers, SDK
contributor references
project boards · Road to 1.0
CHANGELOG.md · CONTRIBUTING.md ·SECURITY.md · .mdSpecial thanks
AttackMap is built by its contributors.
<a href=" src=" alt="AttackMap contributors" /></a>
Contributing
Issues and PRs welcome — see CONTRIBUTING.md. By contributing
you agree your contributions will be MIT-licensed.
License
MIT. Copyright (c) 2026 Matthew Davis and AttackMap Contributors.
项目信息
开发语言:Python
Star 数:1
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-assisted defensive security analysis for codebases.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AttackMap - AI-assisted defensive security analysis for codeba |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:24:00 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 491 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |