剑庭安
首页
黑客安全首页全部安全栏目 黑客技术黑客技术、渗透测试、漏洞利用工具与教程 安全软件安全工具、扫描器、检测与审计软件 病毒分析恶意软件分析、样本、逆向与沙箱 CTF思路CTF 题目、writeup、解题思路与工具 防护思路防御技术、加固、检测响应与蓝队 红蓝攻防红队攻击模拟、蓝队对抗、攻防演练 漏洞知识库漏洞、CVE、PoC、EXP 与安全研究
逆向|反编译
PHP源码PHP 网站源码、程序、系统 APP源码安卓/iOS APP 源码 ASP源码ASP 网站源码与程序 NET源码.NET 网站源码与系统 小程序源码微信/支付宝小程序源码 Dedecms风格模板Dedecms 织梦风格模板 Empirecms风格模板EmpireCMS 帝国风格模板 Discuz商业模板/插件Discuz 商业模板与插件 WordPress主题/插件WordPress 主题与插件 其它源码、模板其它各类源码与模板 游戏源码游戏源码与引擎项目 加密货币源码加密货币、区块链、钱包、USDT/比特币相关源码与工具 手游源码手机游戏源码、服务端、客户端与引擎项目 传奇源码热血传奇、传奇世界、复古传奇等客户端/服务端/引擎源码 页游源码网页游戏、H5 游戏、浏览器游戏源码 端游源码电脑单机游戏、PC 网游客户端/服务端源码
最新万能免驱动支持所有型号打印机下载程序 日历天气老黄历 · 每天同步真实日期与天气
站长工具站长工具 自助开通会员浏览该分类 其他资源qtziy SEO工具SEO工具 站群源码站群源码 泛程序泛程序 蜘蛛模板蜘蛛模板 蜘蛛池蜘蛛池 外链工具外链工具
搜索 自助开通会员🔓 破甲 API
登录 注册
首页 分类列表 防护思路 omnisec - A Cyber-security D…
omnisec - A Cyber-security Defensive and Hardening Suite 防护思路 点击放大
作者:admin 发布:2026-10-06

omnisec - A Cyber-security Defensive and Hardening Suite

项目说明<p align="center"> <img src="omnisec.png" alt="OMNISEC" width="300"/></p><h1 align=&q…
资源可下载 免费下载 0 条讨论
会员资源
开通会员后即可下载全部资源。
登录后开通会员
会员方案
175浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-06
人工审核发布
评论区答疑

omnisec - A Cyber-security Defensive and Hardening Suite

omnisec - A Cyber-security Defensive and Hardening Suite

项目说明

<p align="center">
<img src="omnisec.png" alt="OMNISEC" width="300"/>
</p>

<h1 align="center">OMNISEC</h1>

<p align="center">
<b>Comprehensi Security Suite</b>
</p>

<p align="center">
<strong>Codeberg:</strong> <a href=" • <strong>GitHub:</strong> <a href=" • <strong>License:</strong> Proprietary
</p>

<p align="center">
<a href="mailto:">
<img src=" alt="Email"/>
</a>
</p>

---

<p align="center">
<img src="omnisec1.png" alt="OMNISEC" width="1260"/>
</p>

---

O

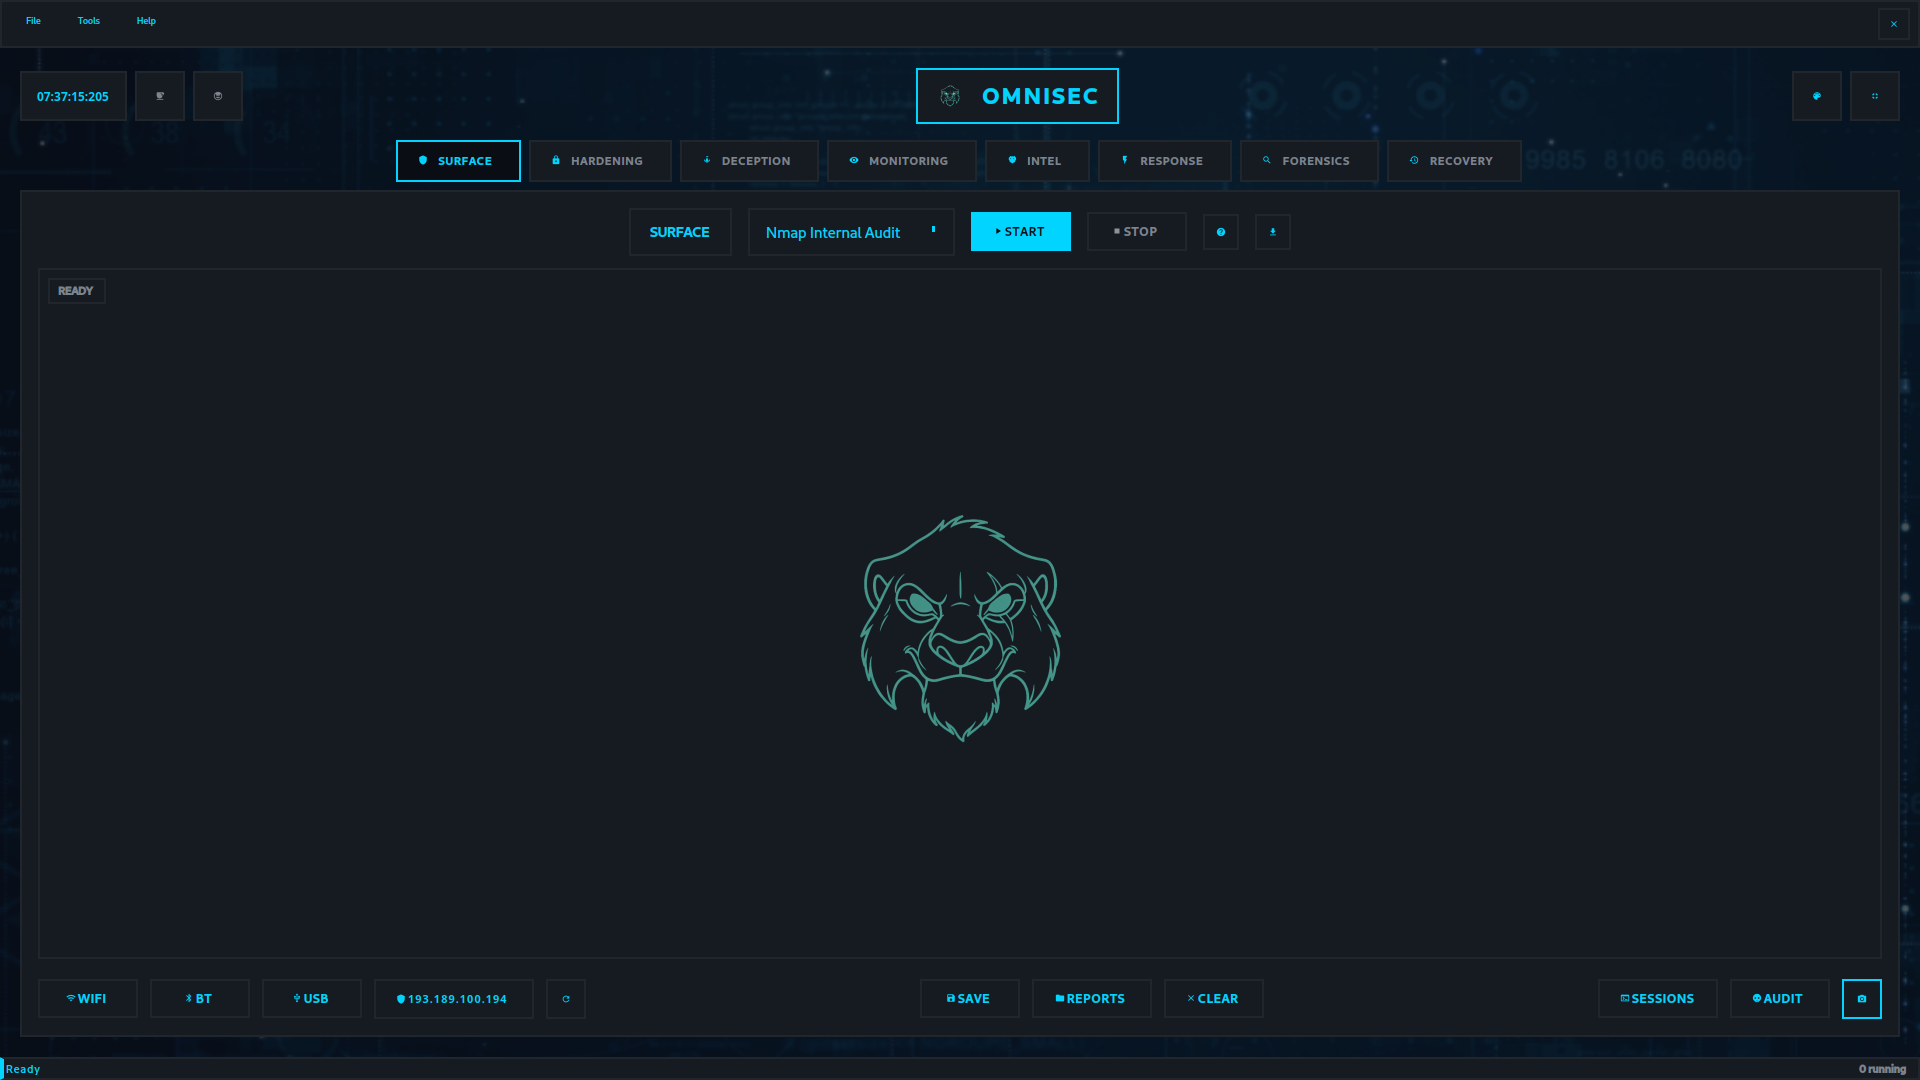
OMNISEC is a comprehensi security platform that integrates 80+ security tools into a unified PyQt6 GUI interface, following the NIST Cybersecurity Framework. It provides a complete security operations center (SOC) solution designed for organizations and security professionals who need to defend against modern cyber threats.

The suite transforms complex security operations into an intuiti experience, eliminating the need to manage multiple disparate tools and interfaces. OMNISEC orchestrates the entire defensi lifecycle from threat detection to incident response and recovery.

---

Core Purpose

OMNISEC addresses the fundamental challenges in modern cybersecurity defense:

  • Tool Fragmentation: Security teams waste time switching between different tools and interfaces

  • Complex Workflows: Manual coordination of multiple security tools leads to inefficiencies

  • Skill Gaps: Not all team members are experts in every security tool

  • Response Time: Slow incident response due to tool switching and manual processes

  • Reporting Complexity: Difficulty in generating comprehensi reports
  • OMNISEC sol problems by pro a single, integrated platform that handles the entire defensi workflow.

    ---

    Architecture & Design

    Unified Interface


  • Single Application: One GUI for all 80+ security tools

  • Consistent Experience: Uniform interface across all security operations

  • Theme Support: Multiple themes for different en

  • Session Management: Save and resume security assessments
  • High-Performance Execution


  • Parallel Processing: Run multiple tools simultaneously

  • Async Architecture: Non-blocking operations for responsive UI

  • Real-time Output: Li of tool results

  • Resource Optimization: Efficient use of system resources
  • Intelligent Automation


  • Smart Tool Selection: Automatic tool recommendations based on context

  • Workflow Orchestration: Automated progression through security phases

  • Output Parsing: Structured data extraction from tool outputs

  • Report Generation: Automated security report creation
  • ---

    Security Phases

    OMNISEC organizes defensi into 8 comprehensi aligned with the NIST Cybersecurity Framework:

    1. Surface Analysis (IDENTIFY)


    Purpose: Understand and map the attack surface before ad find it.

    Capabilities:

  • Network asset discovery and in

  • Service enumeration and fingerprinting

  • scanning and assessment

  • Infrastructure as Code security analysis

  • Attack surface mapping and
  • Tools: Nmap, OpenVAS/G, Checkov, ARP Scan, and more

    2. System Hardening (PROTECT)


    Purpose: Reduce attack surface through system configuration and access controls.

    Capabilities:

  • Firewall management and configuration

  • Mandatory access control implementation

  • USB device whitelisting and control

  • Application sandboxing and isolation

  • SSH ser and key management

  • Kernel security parameter optimization
  • Tools: UFW, IPTables, Fail2Ban, AppArmor, USBGuard, Firejail, and more

    3. Deception Technology (DETECT)


    Purpose: Mislead attackers and gather intelligence on their methods.

    Capabilities:

  • Honeypot deployment and management

  • Tripwire systems for unauthorized access detection

  • Canary token implementation

  • Web application honeypots

  • Multi-service honeypot orchestration
  • Tools: Cowrie, Dionaea, Honeyd, Glastopf, OpenCanary, Artillery

    4. Intrusion Detection (DETECT)


    Purpose: Real-time monitoring and threat detection across network and hosts.

    Capabilities:

  • Network intrusion detection and pre

  • Host-based intrusion detection

  • Log analysis and correlation

  • Runtime security monitoring

  • Packet capture and analysis

  • Bandwidth monitoring and anomaly detection
  • Tools: Suricata, Snort, Wazuh HIDS, OSSEC, Zeek, Falco, and more

    5. Threat Intelligence (DETECT)


    Purpose: Enrich security events with threat intelligence and IOC analysis.

    Capabilities:

  • IOC scanning and analysis

  • Malware pattern matching

  • Threat intelligence platform integration

  • IP reputation checking

  • Domain and URL analysis

  • Multi-engine malware scanning
  • Tools: MISP, , AlienVault OTX, YARA, Loki, ClamAV, and more

    6. Incident Response (RESPOND)


    Purpose: Rapid containment, eradication, and recovery from security incidents.

    Capabilities:

  • Emergency network isolation

  • Malicious process termination

  • IP address blocking and quarantine

  • Connection tracking and management

  • User account lockdown and in

  • Automated incident response workflows
  • Tools: Iron Curtain, TheHi, GRR, TCPKill, Conntrack, and more

    7. Digital Forensics (RESPOND)


    Purpose: E collection, preser, and analysis for in.

    Capabilities:

  • Memory forensics and analysis

  • Disk image analysis and file carving

  • Metadata extraction and timeline creation

  • Malware analysis and reverse engineering

  • Network traffic forensics

  • E preser and chain of custody
  • Tools: 3, Autopsy, The Sleuth Kit, Binwalk, Foremost, ExifTool, and more

    8. System Recovery (RECOVER)


    Purpose: Restore systems to trusted state and prevent future incidents.

    Capabilities:

  • System snapshot and backup management

  • Malware removal and cleanup

  • File integrity

  • Configuration management and automation

  • Secure file deletion and sanitization

  • System restoration and
  • Tools: Timeshift, ClamA, Restic, Ansible, AIDE, and more

    ---

    Key Features

    Ad GUI


  • Modern Interface: Clean, professional design with multiple themes

  • Tabbed Organization: Logical grouping by security phases

  • Real-time Monitoring: Li indicators and status updates

  • Screenshot Capability: Built-in screen capture for documentation
  • Performance & Scalability


  • Parallel Execution: Run multiple tools simultaneously

  • Batch Processing: Queue operations for multiple targets

  • Resource Management: Efficient CPU and memory utilization

  • Background Processing: Non-blocking operations for responsive UI
  • Intelligence & Automation


  • Smart Recommendations: Context-aware tool suggestions

  • Automated Workflows: Guided progression through security phases

  • Output Intelligence: Structured data extraction and correlation

  • Report Automation: Comprehensi report generation
  • Enterprise Integration


  • API Support: Integration with existing security infrastructure

  • Export Capabilities: Multiple output formats (PDF, JSON, XML)

  • Session Persistence: Save and resume complex assessments

  • Team Collaboration: Multi-user session management
  • ---

    Applications & Use Cases

    Enterprise Security Operations


  • SOC Operations: Centralized security monitoring and response

  • Incident Response: Rapid containment and in workflows

  • Compliance Auditing: Automated security assessments and reporting

  • Threat Hunting: Proacti detection and analysis
  • Security Consulting


  • Penetration Testing: Comprehensi assessments

  • Management: Continuous scanning and remediation

  • Security Audits: Automated compliance and configuration auditing

  • Forensic In: Digital e collection and analysis
  • Educational & Research


  • Security Training: Hands-on cybersecurity education platform

  • Research Projects: Security research and tool de

  • Red Team Operations: Offensi simulation and testing

  • Blue Team Training: Defensi skills de
  • Go & Critical Infrastructure


  • Go Networks: Secure go system management

  • Critical Infrastructure: Protection of essential services and utilities

  • Military Applications: Secure communication and system defense

  • Intelligence Operations: Secure data handling and analysis
  • ---

    Technical Specifications

    System Requirements


  • Operating System: Linux (Ubuntu, Debian, Kali Linux recommended)

  • Python : 3.10 or higher

  • Memory: 4GB RAM minimum, 8GB recommended

  • Storage: 10GB free space for tools and data

  • Display: 1920x1080 resolution minimum
  • Supported Platforms


  • Primary: Linux distributions (Ubuntu, Debian, Kali)

  • Secondary: macOS and Windows (limited functionality)

  • Container: Docker support for isolated deployments
  • Dependencies


  • Core Framework: PyQt6 for GUI, asyncio for concurrency

  • Security Tools: 80+ integrated security tools and frameworks

  • Data Processing: XML, JSON, and text parsing libraries

  • System Integration: Nati service management
  • ---

    Security & Compliance

    Framework Alignment


  • NIST Cybersecurity Framework: Complete IDENTIFY, PROTECT, DETECT, RESPOND, RECO

  • ISO 27001: Information security management system compliance

  • PCI DSS: Payment card industry data security standards

  • HIPAA: Healthcare data protection and privacy

  • GDPR: General data protection regulation compliance
  • Security Features


  • Encrypted Communications: Secure data transmission and storage

  • Access Controls: Role-based access and permission management

  • Audit Logging: Comprehensi event logging

  • Data Protection: Sensitive data handling and encryption

  • Secure Updates: Authenticated software update mechanisms
  • ---

    Author Information

    funbinet is a cybersecurity specialist and automation engineer currently pursuing a Computer Science degree at Chuka Uni. With a focus on red teaming, penetration testing, and defensi, funbinet de comprehensi solutions that bridge the gap between offensive and defensi.

    Background


  • Education: Computer Science student at Chuka Uni

  • Specialization: Cybersecurity, Red Teaming, Penetration Testing

  • Experience: De security tools and frameworks

  • Philosophy: "Automation is not luxury; it is survival"
  • Projects


  • OMNISEC: Comprehensi security suite

  • LE: Complete penetration testing framework

  • Security Tools: Custom security automation and analysis tools
  • Contact


  • Email:

  • Codeberg:

  • GitHub:
  • ---

    License

    Proprietary Software License

    Copyright (c) 2024 funbinet

    All rights reserved.

    This software is the property of funbinet and is protected by copyright laws and international copyright treaties. No part of this software may be reproduced, distributed, or transmitted in any form or by any means, including photocopying, recording, or other electronic or mechanical methods, without the prior written permission of funbinet, except in the case of brief quotations embodied in critical reviews and certain other noncommercial uses permitted by copyright law.

    Restrictions:

    1. No Redistribution: You may not redistribute this software, in whole or in part, to any third party.
    2. No Modification: You may not modify, adapt, translate, reverse engineer, decompile, or disassemble this software.
    3. No Commercial Use: You may not use this software for commercial purposes, including but not limited to selling, renting, licensing, or distributing the software for a fee.
    4. No Transfer: You may not transfer, lease, or sublicense this software to any other party.

    Limited License:

    A limited, non-exclusi license is granted to the original licensee for personal, non-commercial use only. This license is subject to all terms and conditions of this agreement.

    Disclaimer:

    This software is provided "as is" without warranty of any kind, express or implied. funbinet shall not be liable for any damages arising from the use of this software.

    Termination:

    This license will terminate automatically if you any of these terms and conditions. Upon termination, you must immediately cease all use of the software and destroy all copies in your possession or control.

    Source Code Access

    The source code for OMNISEC is proprietary and not publicly a. If you are interested in accessing the source code for research, educational, or legitimate security purposes, please contact the author directly at to discuss licensing and access arrangements.

    ---

    Getting Started

    OMNISEC is designed for authorized security professionals and organizations. To obtain access to the software:

    1. Review Requirements: Ensure your system meets the technical specifications
    2. Contact Author: Email with your use case and requirements
    3. License Agreement: Discuss licensing terms and access arrangements
    4. Installation: Recei instructions and support
    5. Training: Optional training and documentation provided

    ---

    <p align="center">
    <b>OMNISEC</b> — Comprehensi Security Suite
    <br>
    <small>© 2025 funbinet • Proprietary Software • All Rights Reserved</small>
    </p>

    项目信息

    开发语言:未知

    Star 数:1

    技术要点

    该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A Cyber-security Defensive and Hardening Suite展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。

    从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。

    使用与学习建议

    1. 下载源码压缩包,解压到本地环境。

    2. 根据项目类型准备对应的运行环境与依赖。

    3. 按照 README 中的步骤完成配置与部署。

    4. 在隔离的测试环境中运行验证,避免影响生产系统。

    免责声明

    本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。

    资源标题omnisec - A Cyber-security Defensive and Hardening Suite
    所属分类防护思路
    发布作者admin
    发布时间2026-10-06 00:24:07
    下载权限 免费下载
    附件数量2 个下载链接
    浏览次数175
    讨论数量0
    主题状态正常讨论中

    本资源免费,登录后即可在本页「下载链接」区域获取全部附件。

    请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。

    请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
    还没有讨论,快来抢沙发~
    登录 后才能参与讨论
    下载链接
    会员才能下载
    登录后开通会员
    同分类推荐
    暂无同类资源
    免费登录即可下载
    查看会员
    放大预览

    © 2026 剑庭安 - 网站开发定制 SEO 优化蜘蛛池代做 在线看手相算命. 保留所有权利。

    Powered by 酷像SEOv3.0

    网站地图 Sitemap.xml
    首页 全部分类 黑客安全 逆向|反编译 精品源码 站长工具自助开通会员其他资源SEO工具站群源码泛程序蜘蛛模板蜘蛛池外链工具创意乐园 搜索 会员服务 登录 注册