 防护思路
点击放大
RedOPS - Defensive security assessment framework — OSINT re
项目说明
RedOPS Framework
![CI Pipeline]()
![Python 3.10+]()
![License: MIT]()
Defensi assessment framework — OSINT reconnaissance, metadata forensics, threat modeling, and attack surface analysis for authorized security e.
> ⚠️ Important: RedOPS is NOT a hacking tool. It is a professional OSINT + metadata + threat-modeling automation system designed for authorized security assessments only.
---
The Problem
Modern cybersecurity teams face critical challenges:
RedOPS addresses these challenges by pro a unified, modular framework for defensi assessments, threat intelligence gathering, and risk quantification.
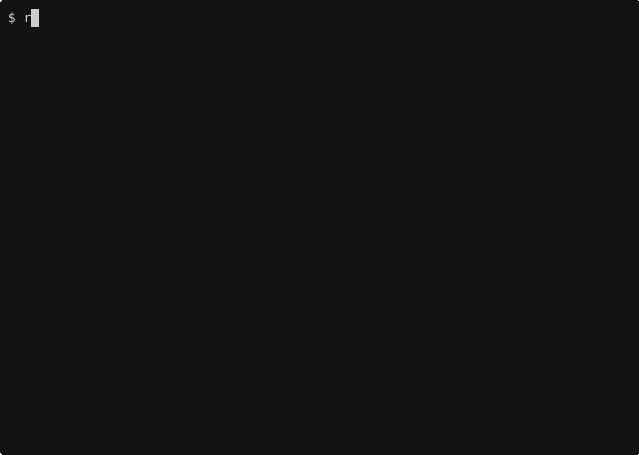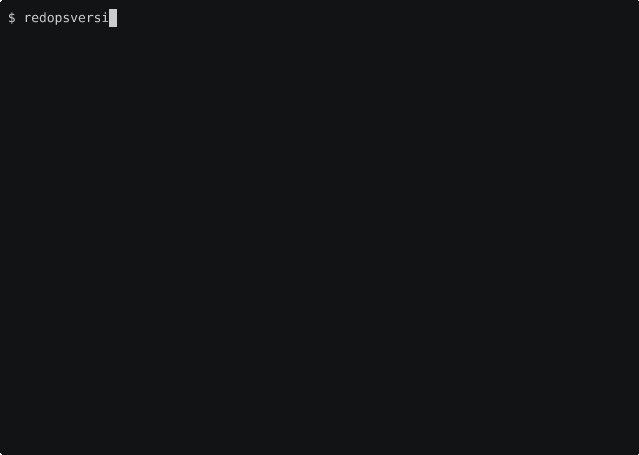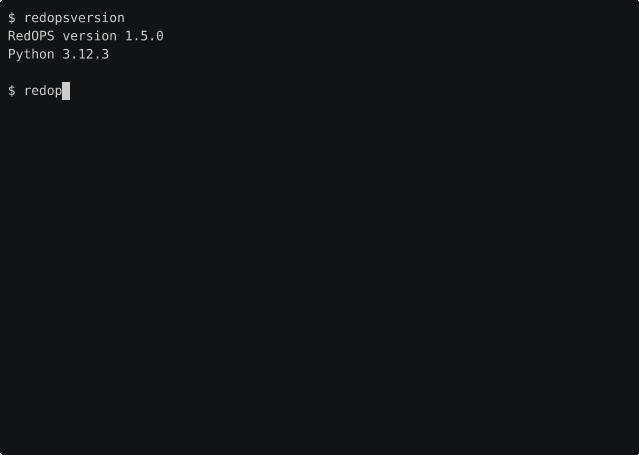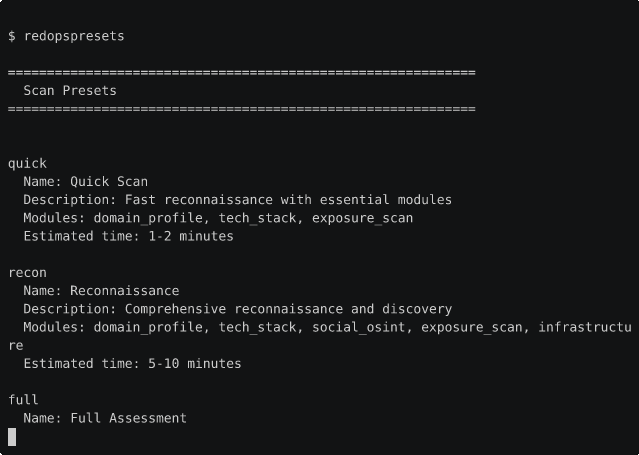
!RedOPS presets and modules
---
Why RedOPS?
RedOPS is a comprehensi platform designed for red teams, blue teams, security analysts, and penetration testers to:
Core Capabilities
---
Solutions Implemented
RedOPS implements a modular pipeline architecture that addresses cybersecurity assessment challenges through specialized, composable modules:
🔍 Reconnaissance & OSINT
Problem: Manual reconnaissance is time-consuming and inconsistent
Solution: Automated OSINT pipelines for systematic intelligence gathering
Value: Reduces reconnaissance time from hours to minutes while ensuring comprehensi
📄 Metadata & Digital Forensics
Problem: Hidden metadata in documents and files can reveal sensiti information
Solution: Automated metadata extraction and forensic analysis
Value: Identify data exposure risks that manual reviews typically miss
🧠 Threat Intelligence & Analysis
Problem: Raw data doesn't translate directly into actionable security insights
Solution: Automated intelligence processing and risk quantification
Value: Transforms raw reconnaissance data into prioritized, actionable intelligence
🎯 Threat Modeling & Attack Simulation
Problem: Understanding ad perspectives and potential attack paths requires specialized expertise
Solution: Non-intrusi path analysis mapped to industry frameworks
Value: Enables proacti by modeling ad behavior without performing actual attacks
📊 Reporting & Documentation
Problem: Communicating technical findings to diverse stakeholders (executives, technical teams, auditors)
Solution: Multi-format automated reporting system
Value: Eliminates hours of manual report writing while ensuring consistent, professional deli
🤖 AI-Powered Analysis
Problem: Interpreting security findings and generating actionable recommendations requires deep expertise
Solution: Integrated AI assistants for analysis, explanation, and remediation guidance
Supported Pro: OpenAI, Anthropic, Google Gemini, Groq, and Ollama (local)
Value: Accelerates analysis and makes security insights accessible to technical and non-technical stakeholders
🛡️ Compliance & Go
Problem: Security assessments must operate within strict legal and ethical boundaries
Solution: Built-in scope and audit logging
Value: Reduces legal/ethical risks and simplifies compliance with regulations and assessment agreements
---
Impact on Cybersecurity Workflows
For Red Teams
For Blue Teams / Defenders
For Security Analysts
For Penetration Testers
---
Constraints & Design Philosophy
RedOPS is designed with strict ethical and operational boundaries:
✅ Authorized Use Cases
❌ What RedOPS Does NOT Do
🔒 Security & Ethics
---
Installation
Requirements
From Source
Using pip
For more detailed installation options, dependency management, and troubleshooting, please refer to the SETUP.md guide.
Quick Start
RedOPS uses pipeline-based workflows to chain together security assessment modules.
1. List A Pipelines
2. Run Security Assessment Pipelines
3. Review Assessment Results
Reports are saved to the ./output directory (or your specified --output-dir):
executi*.md - High-level risk o for leadership and clientstechnical_report_*.md - Detailed findings for security teamsreport_*.html - Styled HTML reports for presentationsdata_*.json - Machine-readable data for integration with security platforms (SIEM, SOAR)<details>
<summary><strong>Sample Executi Output</strong></summary>
See examples/sample_output/ for full JSON reports across 7 scan profiles (quick, recon, full, executi, infrastructure, threat_intel).
</details>
4. AI-Powered Analysis
5. Run AI-Enhanced Scans
6. Web Dashboard
Features:
7. Claude Code Integration (MCP)
RedOPS can be used directly from Claude Code via the Model Context Protocol.
Setup:
A tools in Claude Code:
redops_scan - Run security reconnaissanceredops_explain - Get AI explanations of security conceptsredops_analyze - Analyze scan resultsredops_suggest - Get remediation suggestionsredops_summarize - Generate executi---
Use Cases in Cybersecurity
🎯 Red Team Engagements
Scenario: Authorized penetration testing engagement
Workflow:
1. Run corporate assessment pipeline on target domain
2. Generate MITRE ATT&CK mapped attack paths
3. Use findings to identify realistic attack
4. Create professional client deli
Benefit: Reduces reconnaissance phase from days to hours
🛡️ Blue Team Posture Assessment
Scenario: Quarterly external exposure review
Workflow:
1. Run reconnaissance pipeline on your organization's domains
2. Analyze metadata leakage in publicly a documents
3. Review risk scores and prioritize remediation
4. Track impro over time
Benefit: Proacti of security gaps before ad exploit them
🔍 Threat Intelligence Collection
Scenario: Competitor analysis or threat actor profiling
Workflow:
1. Configure scope with allowed targets
2. Run OSINT and metadata extraction pipelines
3. Extract entities and build relationship graphs
4. Export to threat intelligence platforms
Benefit: Structured, repeatable intelligence gathering process
📋 Compliance & Audit Support
Scenario: Annual security audit preparation
Workflow:
1. Run compliance-enabled pipelines with audit logging
2. Generate executi for auditors
3. Provide technical reports demonstrating security controls
4. Submit audit logs showing assessment scope adherence
Benefit: Comprehensi reduces audit preparation time
---
4. Installation
Use Cases
🎯 Corporate Security Assessment
Assess your organization's external attack surface:
What it analyzes:
🔍 Forensic Analysis
Analyze metadata from documents and images in a directory:
What it extracts:
🧪 Threat Modeling
Model potential attack paths for your infrastructure:
What it generates:
Practical Examples
Example 1: Domain Reconnaissance
Sample Output:
Example 2: Document Metadata Analysis
Findings might include:
Example 3: Custom Pipeline
Create your own pipeline for specific needs:
Save as config/pipelines/quick_scan.json and run:
Architecture
RedOPS implements a modular pipeline architecture designed for flexibility, extensibility, and security.
Design Principles
Plugin System
RedOPS includes a comprehensi system for extending functionality:
Plugin Types:
ModulePlugin - Custom reconnaissance/analysis modulesReporterPlugin - Custom report formattersEnricherPlugin - Data enrichmentHookPlugin - Pipeline lifecycle hooks (before/after module, on error)Plugins can be placed in ~/.config/redops/plugins/ or ./plugins/ for auto-discovery.
Third-Party Intelligence
RedOPS integrates with external threat intelligence APIs:
| Service | Module | Description |
|---------|--------|-------------|
| Shodan | shodan | Host/port intelligence, , banners |
| Censys | censys | Certificate transparency, host discovery |
Project Structure
Pipeline System
Pipelines are JSON-defined security workflows that execute modules sequentially. This approach enables:
Pipeline Structure:
Context Object
The Context object is the data pipeline that flows through each module, accumulating findings and intelligence:
Benefits:
Module System
All modules follow a simple, consistent interface for easy de and testing:
Module Categories:
recon/ - Reconnaissance and OSINT modulesmetadata/ - Forensic analysis and metadata extractionintel/ - Intelligence processing and analysissimulation/ - Threat modeling and attack simulationreporting/ - Report generation and data exportcompliance/ - Scope and audit logging---
Configuration
Security Configuration
Create a security_config.json file to enforce assessment boundaries:
Configuration Options:
scope.strict_mode: Reject any target outside allowed listsscope.allowed_domains: Authorized domains for assessmentscope.allowed_ips: Authorized IP ranges (CIDR notation supported)scope.allowed_directories: Authorized filesystem paths for analysisoutput.include_logs: Include audit logs in reports for complianceApply configuration:
En
RedOPS respects standard en for operational flexibility:
REDOPS_OUTPUT_DIR - O default output directoryREDOPS_ - Enable detailed logging (true/false)REDOPS_STRICT_SCOPE - Enforce strict scope (true/false)Example:
---
Creating Custom Pipelines
Extend RedOPS with custom assessment workflows tailored to your requirements:
Step 1: Define Your Pipeline
Create a JSON file in config/pipelines/ or your preferred location:
Step 2: Execute Your Pipeline
Step 3: Review Results
Check the ./results directory for generated reports and data exports.
Best Practices
continue_on_error strategically (false for critical steps, true for optional)---
Value to the Cybersecurity Community
RedOPS provides significant value to security professionals and organizations:
🎓 Education & Training
🏢 Professional Use
🔬 Research & De
🤝 Community Collaboration
💼 Organizational Benefits
---
Security & Ethics
⚠️ Legal & Ethical Use Only
RedOPS is a professional security tool that must be used responsibly:
RedOPS is designed for:
Never use RedOPS for:
Scope & Compliance
RedOPS enforces security boundaries through multiple mechanisms:
Example Scope Configuration:
Transparency & Accountability
Responsible Disclosure
If RedOPS is used in security research and are discovered:
1. Do not exploit beyond proof-of-concept
2. Follow responsible disclosure practices (90-day disclosure timelines)
3. Document findings professionally and comprehensively
4. Coordinate with before public disclosure
5. Comply with bug bounty program rules if applicable
---
Contributing
We welcome contributions from the cybersecurity community!
How to Contribute
1. Fork the Repository - Create your own copy of RedOPS
2. Create a Feature Branch - git checkout -b feature/new-module
3. Follow Code Standards - Maintain consistency with existing code structure
4. Add Tests - Include unit tests for new modules (if applicable)
5. Document Changes - Update documentation and module docstrings
6. Submit Pull Request - Describe your changes and their security impact
Contribution Ideas
Module De Guidelines
When creating new modules:
Context in/out)Security Issues
If you discover a security in RedOPS itself:
---
License
MIT License - See LICENSE file for full details.
RedOPS is free and open-source software, a for commercial and non-commercial use. However, users must always obtain proper authorization before conducting any security assessments, regardless of the software license.
---
Disclaimer
⚠️ CRITICAL: READ BEFORE USE
This tool is provided for educational and authorized security assessment purposes ONLY.
By using RedOPS, you acknowledge that you:
1. Have explicit written authorization for any targets you assess
2. Will comply with all applicable laws and regulations
3. Understand the legal and ethical implications of security assessments
4. Accept full responsibility for your actions and their consequences
---
Frequently Asked Questions
Is RedOPS a penetration testing tool?
RedOPS is a reconnaissance and threat modeling framework, not an exploitation tool. It analyzes and models security posture without performing acti.
Can I use RedOPS for bug bounty programs?
Yes, if the program allows reconnaissance and OSINT gathering. Always read and follow the specific program rules and scope definitions.
How does RedOPS differ from commercial solutions?
RedOPS is open-source, modular, and extensible. It focuses on OSINT, threat modeling, and risk assessment rather than acti scanning.
Is RedOPS safe to use on production systems?
RedOPS performs passi only, but always obtain proper authorization and configure scope to prevent accidental o.
Can I integrate RedOPS with other security tools?
Yes! RedOPS exports data in JSON and CS that can be imported into SIEM, SOAR, GRC platforms, and other security tools.
How do I get support?
---
Community
Discord — Join the community
---
Acknowledgments
RedOPS builds upon the work of the cybersecurity community and le industry-standard frameworks:
We are grateful to all contributors and users who help impro.
---
RedOPS Framework - Professional Cybersecurity Intelligence & Attack Surface Management
*Empowering security professionals with systematic, ethical assessment capabilities*
🔗 Repository:
📚 Issues & Support: GitHub Issues
项目信息
开发语言:Python
Star 数:1
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive security assessment framework — OSINT reconnaissance, metadata forensics, threat modeling, and attack surface analysis for authorized security evaluations.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | RedOPS - Defensive security assessment framework — OSINT re |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:26:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 294 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |