 防护思路
点击放大
claude-skills-security - Defensive security audit skills for Claude — tech-
项目说明
<p align="center">
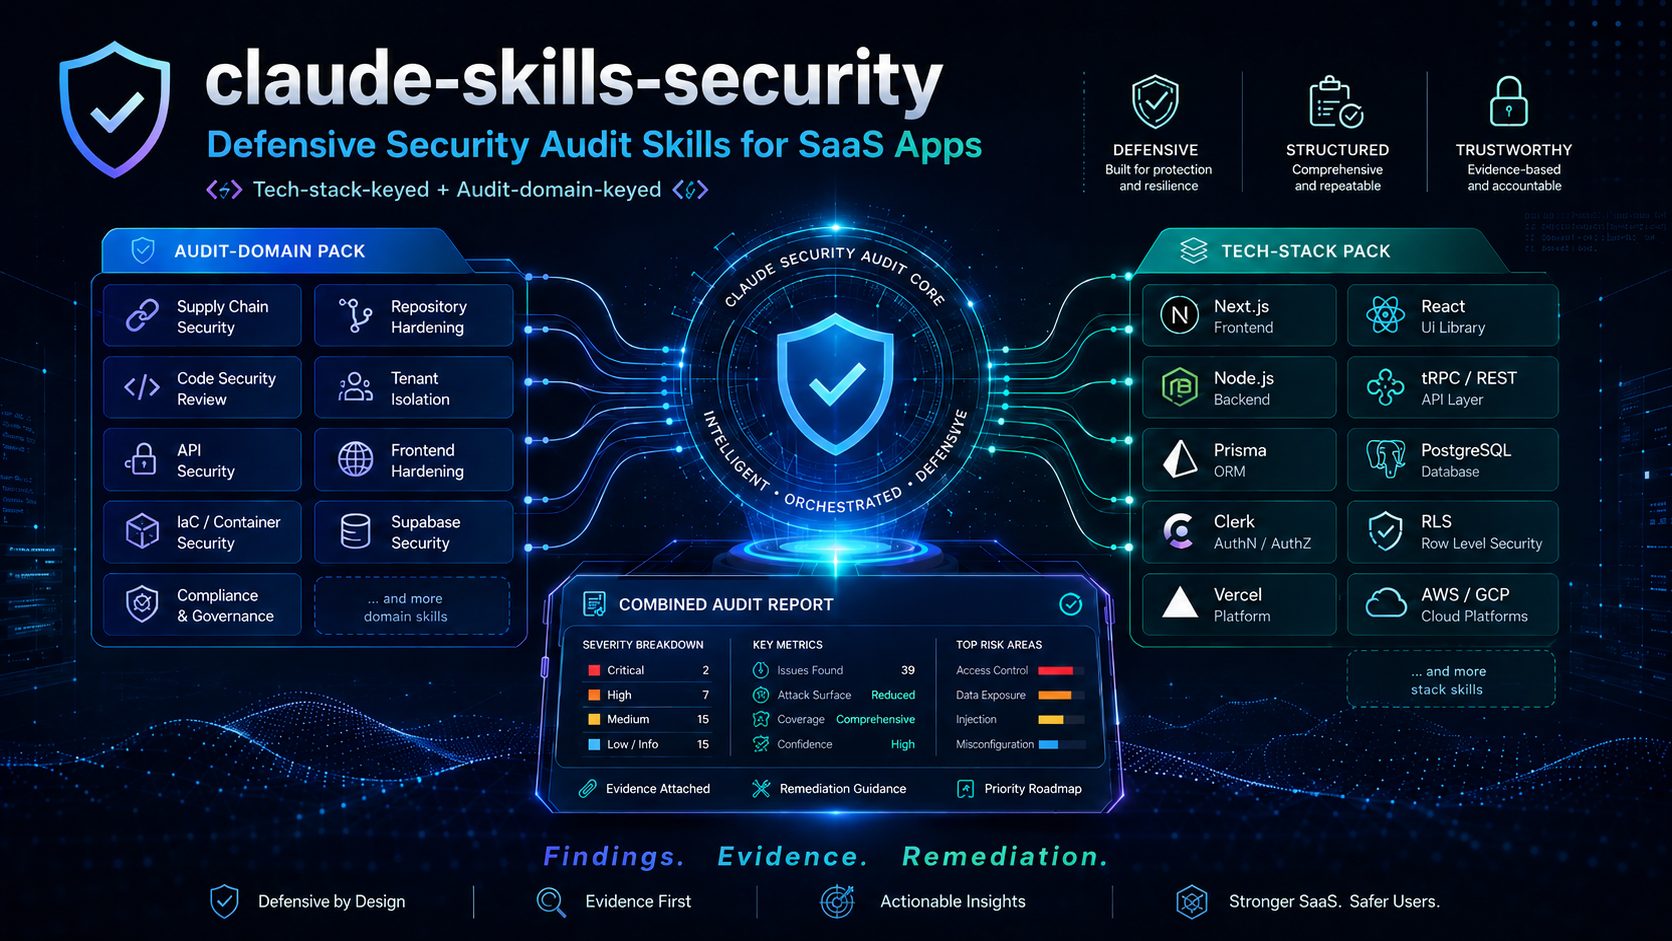
<img src="docs/banner-v2.png" alt="claude-skills-security — Defensi Audit Skills for SaaS Apps" width="100%">
</p>
<p align="center">
<a href="SECURITY.md"><img alt="Security policy" src="
<a href="LICENSE"><img alt="License: MIT" src="
<a href=".github/workflows/.yml"><img alt=" skills" src="
<a href=".github/workflows/secret-scan.yml"><img alt="Secret scan" src="
<a href=".github/tech-in.yml"><img alt="Tech in" src="
<a href="docs/ENHANCEMENT_PLAN.md"><img alt="Drift watch" src="
</p>
claude-skills-security
A collection of 40 defensi audit skills for Claude, organized as two complementary packs.
> 🛡️ Found a security issue in the skill content? See SECURITY.md — private GitHub ad or . Acknowledged within 3 business days; Critical fixes within 14.
At a glance
| Metric | Value |
|--------|-------|
| Skills | 40 total — 9 audit-domain + 31 tech-stack |
| Check IDs | 1,591 unique findings across the 40 skills |
| Reference files | 40 deep-di docs |
| Content | 15,570 lines of authored audit guidance |
| Tech in | 61 tracked technologies with 141 cited sources (.github/tech-in.yml) |
| Drift watch | 4 Critical · 21 High · 16 Medium · 16 Low — current as of 2026-05-24 |
| CI | Per-skill schema + in schema v3 (.github/workflows/.yml) |
| Secret scanning | gitleaks on every PR + weekly full-history rescan (.github/workflows/secret-scan.yml) |
| Security policy | Responsible disclosure — see SECURITY.md |
| License | MIT — see LICENSE |
The packs answer different questions, and Claude picks skills from either (or both) based on what the user is asking:
| Pack | Skills | Organized by | Activates when |
|------|-------:|--------------|----------------|
| saas-security-pack | 9 | Audit domain | "Review my supply chain", "Audit our RLS", "Check tenant isolation", "Compliance review" |
| appsec-stack-pack | 31 | Technology stack | "Audit my Next.js app", "Review my Prisma queries", "Is my Clerk webhook safe", "Cloudflare Workers security", "Review my CORS / CSP / cookies" |
For a typical "audit my SaaS" request on a modern stack, both packs activate skills that work together — domain-keyed audits (RLS, supply chain) running alongside stack-keyed audits (Next.js, Prisma, Clerk). The quick example below shows 7 skills acti concurrently on a single audit request.
Quick example
User asks: *"Audit my Next.js + Prisma + Clerk app on for security issues."*
Claude activates:
nextjs-security (NXT-) — App Router, Ser, enprisma-orm-security (PRI-) — raw queries, mass assignment, IDORclerk-security (CLK-) — webhook signatures, key handling, middlewaresaas-code-security-review (SCSR-) — generic auth/IDOR/SSRF patternssaas-frontend-hardening (SFH-) — CSP, cookies, headerssaas-tenant-isolation (STI-) — multi-tenant data partitioningSe run, each emitting findings with its own prefix. The combined report is se and de-duplicated.
The 40 skills
saas-security-pack — domain-keyed (9)
| Skill | Prefix | Covers |
|-------|--------|--------|
| github-supply-chain | GHSC | Actions pinning, dependabot, secret scanning, SBOM |
| github-repo-hardening | GHRH | Branch protection, en, CODEOWNERS, signed commits |
| saas-code-security-review | SCSR | Auth, AuthZ, IDOR, SSRF, JWT, secrets, sinks, deserialization |
| supabase-security-audit | SUPA | RLS policies, SECURITY DEFINER, anon role exposure, storage policies |
| saas-tenant-isolation | STI | Per-tenant scoping across DB, cache, search, files, queues |
| saas-api-security | SAPI | REST con, rate limits, webhooks, idempotency, CORS |
| saas-frontend-hardening | SFH | CSP, cookies, CORS, headers, secrets in bundle |
| iac-container-security | IACS | Terraform, Dockerfile, Kubernetes manifests, image scanning |
| saas-compliance-audit | SCMP | SOC 2, GDPR/CCPA, e collection, audit logs |
appsec-stack-pack — tech-keyed (31)
Frontend (7): react · nextjs · vite · · s · angular · electron
Backend Node (4): nodejs-express · nestjs · fastify · hono
Backend Python (3): django · fastapi · flask
Other backends (5): go · rails · laravel · spring-boot · dotnet-aspnetcore
API protocols (3): graphql · trpc · websocket
Data layer (3): prisma-orm · mongoose-mongodb · redis
Auth pro (2): clerk · nextauth
Edge/Cloud (3): · cloudflare-workers · aws-lambda
Web platform (1): web-platform-security — CORS, CSP, COOP/COEP/CORP, modern cookies (SameSite, __Host-, CHIPS), Permissions-Policy, SRI, Trusted Types, HSTS, postMessage, iframe sandbox, Private Network Access, WebAuthn / Passkeys, FedCM. Sourced from web.de.chrome.com.
See appsec-stack-pack/README.md for the full table with triggers.
Skill format
Every skill follows the same shape:
Every audit emits findings using the shared schema in each pack's _shared/findings-schema.md. Finding IDs are prefixed with a 3-letter skill code so combined reports don't collide — 40 unique prefixes across the two packs, 1,591 indi check IDs in total.
Installation
Each pack is independently installable. For Claude Code:
For Claude Desktop or claude.ai, follow the platform's skill installation flow.
Each pack also has a scripts/package_skills.sh that produces per-skill .zip files in dist/ for selecti.
Design principles
Security
> 🛡️ This repository is the source of truth for 40 defensi audit skills. A flaw in the *content* (a check recommending an insecure pattern, a "GOOD" example with a subtle bug, a missing C) can propagate to downstream audits — so we treat content bugs as security issues.
How to report (machine + human readable)
The same info is published in standards-compliant form at /.well-known/security.txt (RFC 9116) for automated scanners.
| Channel | Use when |
|---------|----------|
| GitHub private report | Preferred. Only the maintainer is notified; coordinated disclosure. |
| (subject [claude-skills-security]) | Fallback if you don't have a GitHub account. |
SLA: acknowledged within 3 business days · triaged within 7 days · Critical fixes shipped within 14 days · 90-day coordinated disclosure unless otherwise agreed.
In scope
.github/tech-in.yml — particularly Critical / High se ones referenced by upstream .Out of scope
Full policy: SECURITY.md.
Repo-side guarantees
.github/CODEOWNERS)..github/workflows/secret-scan.yml)..github/workflows/.yml).permissions: {} at workflow level, contents: read per job, all third-party actions SHA-pinned (the same supply-chain guidance the skills teach).Companion projects
Contributing
See CONTRIBUTING.md for skill format, triggers, and contribution flow.
License
MIT — see LICENSE.
项目信息
开发语言:Shell
Star 数:1
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Defensive security audit skills for Claude — tech-stack-keyed and audit-domain-keyed packs for SaaS apps.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | claude-skills-security - Defensive security audit skills for Claude — tech- |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:28:07 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 519 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |