 防护思路
点击放大
edy-shield - Endpoint integrity and defensive security platform
项目说明
<di="center">
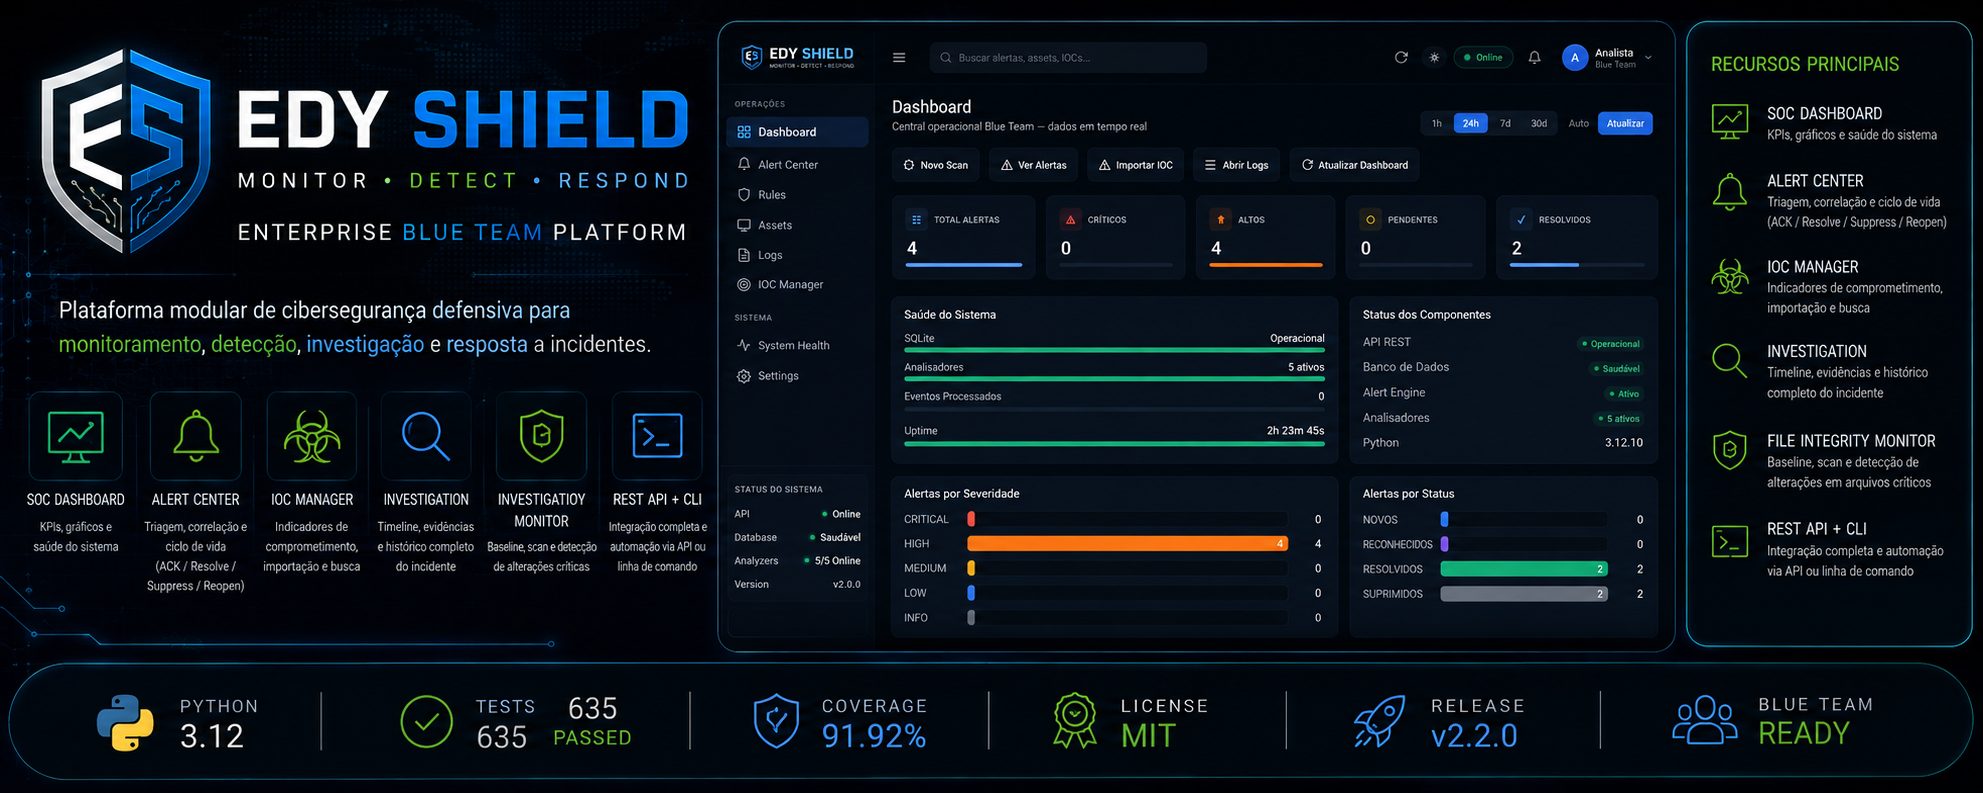
EDY Shield — Endpoint Integrity & Defense
Modern defensi toolkit for file integrity, hash analysis and incident in.
!EDY Shield Banner
![Python]()

![Release]()
![Tests]()
![Co]()
![Platform]()
</div>
---
Apresentação em vídeo
O
EDY Shield is an Endpoint Integrity & Defense platform written in Python 3.12 with a 100% standard-library core (zero runtime dependencies). It is local-first: FIM, baselines, scans, hash analysis and the local alert workflow remain a even when the SIEM receiver is una.
It solves a practical problem: small security teams and blue-team operators need a lightweight, self-contained toolkit — no cloud, no agents, no license fees — to monitor critical files, triage alerts and in indicators of compromise on their own infrastructure.
Capabilities
---
Features
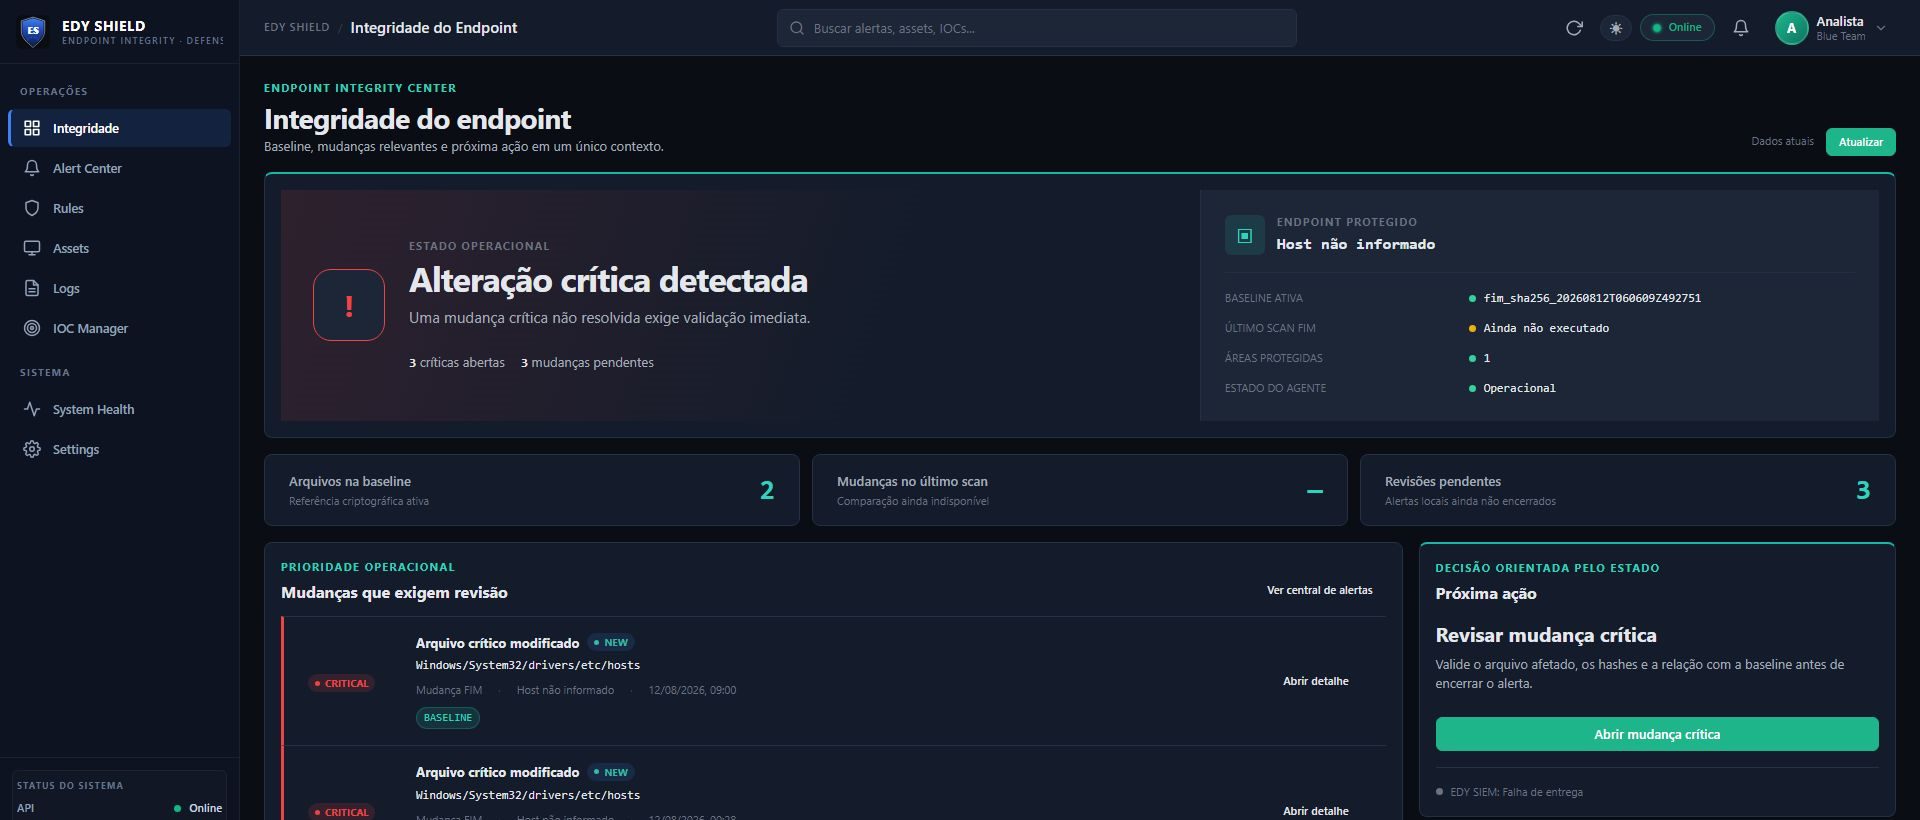
Endpoint Integrity Center — Operational posture, baseline state, scan context and changes requiring review.
Alert Center — Triage table with filters, sorting, pagination and batch actions (ACK, resol, reopen).
Change in — Factual change → e → impact → decision flow with hash comparison, baseline context and delivery state.
Rules — View acti engine rules with se and thresholds.
Assets — In view of monitored assets.
IOC Manager — Interface for indicator-of-compromise workflows.
Logs — System log with le.
System Health — API, database, analyzer and uptime KPIs with plugin list.
Export — Alert in export to Markdown and JSON.
REST API — JSON API for alerts, health, history, analysis and FIM baselines.
Dark / Light — Full theme support persisted in browser.
Responsive — Optimized layout for desktop, tablet and mobile.
---
Release screenshots
| Endpoint Integrity Center | Delivered change with SIEM handoff |
|---|---|
| !Endpoint Integrity Center | !FIM change with confirmed EDY SIEM handoff |
---
Architecture
The application is layered with a strict one-way dependency rule: UI → Services → Core. The core ne from UI or services.
Frontend — HTML/CSS/JS single-page application (no frameworks). Ser by the built-in HTTP server.
Backend — http.server-based REST API (Python standard library). Routes for alerts, health, history, analysis, FIM and plugins.
Services — Business orchestration: alert service, alert store, history, report engine, analysis.
Storage — SQLite via the standard library. Default database path o through EDYSHIELD_DB_PATH.
Plugins — Contract-based plugin system: log_analyzer, hash_checker, file_integrity, string_analyzer, entropy_analyzer.
API — JSON endpoints under /api/* (see docs/API_STABILITY.md).
---
Project Structure
---
Installation
Requirements
Windows
Linux
macOS
---
Running
Start the web dashboard:
Then open <
The REST API is a on the same host: <
CLI usage:
---
Configuration
Configuration is en (prefix EDY_):
| | Description | Default |
|---|---|---|
| EDYSHIELD_DB_PATH | SQLite database file path | ~/.edyshield/edy_shield.db |
| EDYSHIELD_LOG_LEVEL | Logging | INFO |
| EDY_SIEM_ENABLED | Enables the optional Shield → SIEM delivery worker | disabled |
| EDY_SIEM_URL | SIEM receiver URL; HTTP is accepted only on loopback | — |
| EDY_SIEM_TOKEN | M2M ingestion token supplied only at runtime | — |
| EDY_SIEM_UI_URL | Safe SIEM UI base URL used for in handoff | — |
SQLite — All persistence (alerts, history, analysis, FIM baselines) lives in a single SQLite database.
Plugins — Enabled through the plugin registry; each analyzer implements the plugin contract (app/plugins/contracts.py).
Directories — Static assets, brand assets and documentation are organized under app/ui/static/, brand/ and docs/.
---
Testing
Current release gates: 687 tests passing, 2 skipped, 86.68% co, mypy strict clean, ruff clean, Ja syntax checks and wheel/sdist build.
---
EDY security ecosystem
Release details: EDY Shield 2.3.0 notes.
---
Security
HTTP hardening includes Content-Security-Policy, X-Frame-Options, nosniff, Referrer-Policy and Permissions-Policy headers, plus a 1 MB request body limit. See docs/THREAT_MODEL.md for details.
---
Roadmap
---
Contributing
Contributions are welcome. Please review the guidelines:
1. Open an issue describing the bug or feature before sending a pull request.
2. Follow the existing code style (ruff + mypy strict must pass).
3. Add or update tests; co must stay above the quality gate.
4. Update CHANGELOG.md for user- changes.
See CONTRIBUTING.md and CODE_OF_CONDUCT.md.
---
License
Distributed under the MIT License. See LICENSE for details.
项目信息
开发语言:Python
Star 数:1
技术要点
该项目属于防护思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Endpoint integrity and defensive security platform for Blue Team: FIM, baselines, hash verification, scans, local-first monitoring and EDY SIEM integration.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | edy-shield - Endpoint integrity and defensive security platform |
| 所属分类 | 防护思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:30:22 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 149 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |