 红蓝攻防
点击放大
Claude-OSINT - 8 Claude skills · 100+ recon capabilities · 80 sec
项目说明
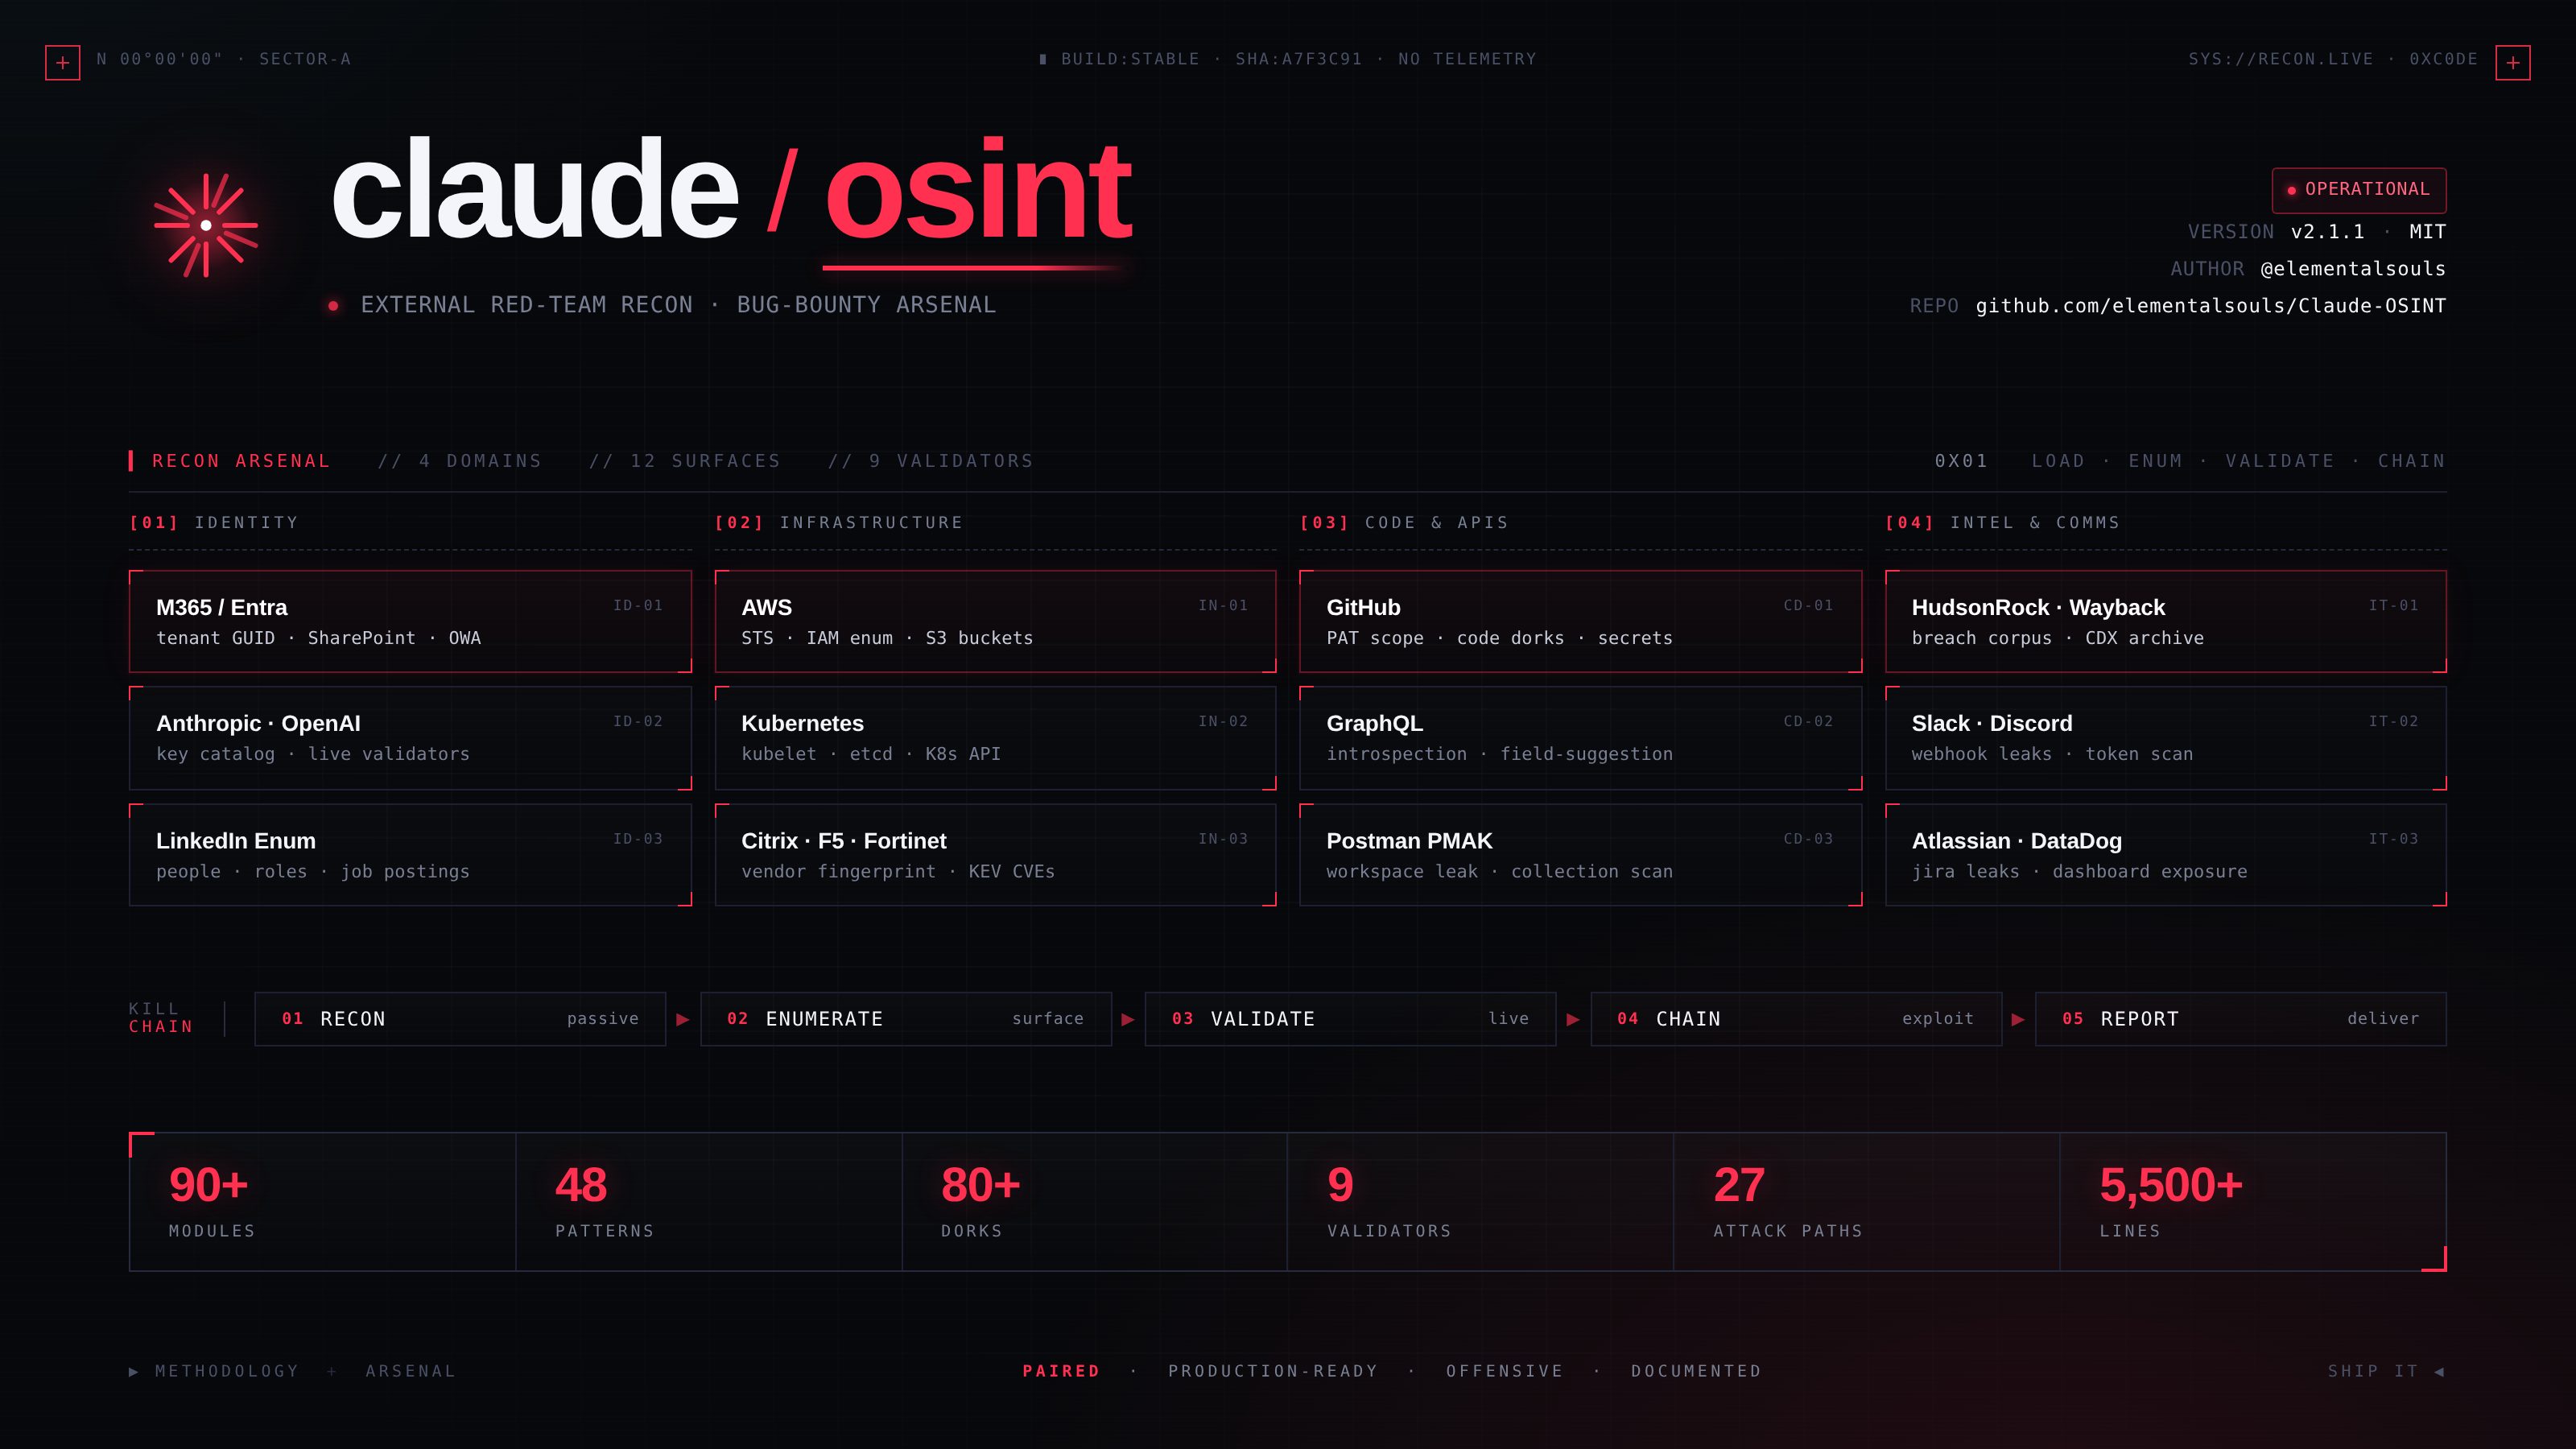
!claude-osint banner
claude-osint
> 8 Claude skills · 100+ recon capabilities · 80 secret-regex patterns · 80+ dorks · 9 read-only credential · 27 attack-path templates · ~10,000 lines of structured tradecraft. Drop-in SKILL.md files that turn Claude into a god-mode external recon operator for authorized red-team and bug-bounty engagements.
Built by Sachin Sharma — GenAI Security Research.
<p align="center">
<sub>SPONSORED BY</sub>
<br/>
<a href="
<picture>
<source media="(prefers-color-scheme: dark)" srcset="assets/sponsors/atlas-cloud-dark.svg">
<img alt="Atlas Cloud" src="assets/sponsors/atlas-cloud-light.svg" height="36">
</picture>
</a>
<a href="
<picture>
<source media="(prefers-color-scheme: dark)" srcset="assets/sponsors/tw360-dark.svg">
<img alt="ThreatWatch360" src="assets/sponsors/tw360-light.svg" height="30">
</picture>
</a>
</p>
---
What is this?
claude-osint is a library of skills for the Claude skills system. Each skill is a structured SKILL.md file that primes Claude with expert-le for one part of the offensi problem.
The core pair — the recon backbone:
osint-methodology - *how to think.* Strategic + procedural. Asset-graph discipline, se rubric, time budgeting, identity-fabric mapping, deli templates.offensi - *what to reach for.* Tactical arsenal. Probe paths, regexes, payloads, scoring rules, curl one-liners, tool URLs.Six organization-grade depth skills — enterprise-scale attack-surface reasoning the core pair doesn't carry:
org-attack-surface - legal entity → owned footprint (GLEIF org-tree, org-first RIR "dark netblock" recall, ASN hyperscaler-scope guard). Disco.email-domain-security - composite spoofability (en ; SPF -all alone ≠ spoof-proof) + SPF supply-chain analysis.exposure-risk-quantification - FAIR 0–100 + A–F risk score, $-denominated loss model, board one-pager, ownership/proof honesty caps.continuous-exposure-monitoring - re-scan/diff loop + CTI/ransomware chatter + finding-lifecycle FP discipline + durable alert outbox.cloud-saas-exposure - bucket ownership-gated se + offline AWS account-ID decode + dependency-confusion confirmation + K8s/CI fingerprint.identity-pro - tenant/federation mapping + pre-auth user-enumeration oracle + name×pattern login synthesis, with a hard enumeration boundary.Drop them into your Claude en and it behaves like a senior recon analyst: it knows the techniques, the tooling, the edge cases, and the escalation paths — and it stays in scope.
~10,000 lines of structured tradecraft · 56/56 PASS on a 56-prompt self-e (100%, zero fabrications) · ~85–90% practitioner co for the recon phase of authorized engagements.
---
Structure
Each skill directory is self-contained (its own SKILL.md + README.md). Drop into ~/.claude/skills/ and Claude auto-triggers on relevant phrases.
---
Skill Index
100+ capabilities across 13 domains. Pick a domain to drill in.
Organization-Grade Depth
The six skills that lift the library from single-target recon to enterprise attack-surface reasoning.
| Capability | Skill |
|---|---|
| Legal-entity → owned-footprint attribution (GLEIF org-tree by exact LEI · EDGAR / OpenCorporates / Wikidata · re · crt.sh ?O= · org-first RIR "dark netblock" recall · ASN hyperscaler-scope guard · disco) | org-attack-surface |
| Composite email spoofability (en · SPF -all ≠ spoof-proof · only DMARC governs) + SPF supply-chain (RFC 7208 >10-lookup PermError · dead-include takeover) | email-domain-security |
| FAIR risk quantification (0–100 + A–F score · $-loss IBM/Ponemon per-record bands · board one-pager · ownership/proof demotion cap) | exposure-risk-quantification |
| Continuous exposure monitoring (baseline → re-scan → diff → threshold alert · CTI / ransomware-leak-site chatter · finding-lifecycle FP discipline · durable alert outbox) | continuous-exposure-monitoring |
| Cloud & supply-chain depth (bucket ownership-gated se · offline AWS account-ID base32 decode · dependency-confusion confirmation · K8s / CI control-plane fingerprint) | cloud-saas-exposure |
| Identity-provider recon (domain→tenant + federation map · pre-auth user-enumeration oracle · name×pattern login synthesis · hard enumeration boundary) | identity-pro |
Reconnaissance & Asset Discovery
| Capability | Skill |
|---|---|
| 6-stage external recon pipeline + time-budget profiles (1h / 4h / 1d / 1w) | methodology |
| Subdomain-source stack (crt.sh + 7-source fallback chain when crt.sh 502s) | arsenal |
| Common-prefix subdomain sweep (100+ ordered prefixes, PowerShell + bash) | arsenal |
| Wayback CDX deep mining + legacy-app pivot (.asp/.php/.jsp/.cfm) | arsenal |
| WHOIS / RDAP / historical-WHOIS + re pivots | arsenal |
| Public records (OpenCorporates · SEC EDGAR · GSXT · Rusprofile · Companies House) | arsenal |
| Bulk IP → ASN (Cymru / RIPEstat / bgp.tools) | arsenal |
Identity & SSO Mapping
| Capability | Skill |
|---|---|
| Microsoft Entra (Azure AD) tenant fingerprint + GUID extraction | arsenal |
| M365 deep enum (Teams federation · SharePoint · OneDrive · OAuth · de phishing) | arsenal |
| Autodiscover IP correlation (passive M365 confirm even when MX wrapped by Mimecast/Proofpoint) | arsenal |
| Okta tenant slug + /api/v1/authn user-enum | arsenal |
| ADFS fingerprint + mex endpoint | arsenal |
| Google Workspace OIDC discovery | arsenal |
| Generic OIDC (Auth0 · Keycloak · Ping · OneLogin · Duo) | arsenal |
| SAML metadata (5 paths) | arsenal |
| AWS account-ID extraction from headers + ARN regex | arsenal |
Web Application Attack Surface
| Capability | Skill |
|---|---|
| Swagger / OpenAPI discovery (28 paths) | arsenal |
| GraphQL discovery + introspection POST body (13 paths) | arsenal |
| GraphQL field-suggestion enum (when introspection disabled) + alias batching + depth bypass | arsenal |
| Always-on HTTP checks (15 paths: .git/.en/heapdump/etc.) | arsenal |
| Missing security header audit (HSTS/CSP/XFO/etc.) | arsenal |
| Endpoint extraction regex tiers (3 tiers) | arsenal |
| Endpoint interest score (0–100 rubric) | arsenal |
| JS deep analysis · sourcemap leakage · internal-host regex | arsenal |
| Subdomain takeo (27 pro) | arsenal |
Cloud & Container
| Capability | Skill |
|---|---|
| Cloud bucket arsenal (S3 / GCS / Azure · 6 prefixes × 15 suffixes × 47 stems) | arsenal |
| Cloud-nati (Lambda URLs · Cloud Run · Azure Functions · · Netlify · Workers) | arsenal |
| Kubernetes / etcd / kubelet exposure (12 ports + probes) | arsenal |
| Container registry leak hunting (Docker Hub · Quay · GHCR · ECR · GCR · ACR) | arsenal |
| CI/CD platform exposure (Jenkins · GitLab · TeamCity-KEV · Argo CD · Spinnaker · CircleCI) | arsenal |
Secret & Credential Hunting
| Capability | Skill |
|---|---|
| 80-pattern secret-regex catalog (48 core + 32 pro) — §17 ↔ secret_scan.py ↔ §48 kept byte-identical | arsenal |
| Modern AI API keys (Anthropic / OpenAI / HuggingFace / Cloudflare) | arsenal |
| Package-registry & provider tokens (npm / PyPI / Docker Hub / GitLab / Stripe / Shopify / Atlassian / +25 more) | arsenal |
| GitHub code-search dorks (13 templates) | arsenal |
| 9 read-only credential (Postman / AWS / GitHub / Slack / Anthropic / OpenAI / npm / Atlassian / DataDog) | arsenal |
| Post-discovery enumeration workflows (IAM enum · repo enum · workspace enum · JWT triage) | arsenal |
| secret_scan.py runnable helper (stdlib-only, JSONL output) | arsenal |
| h1_reference.py — HackerOne disclosed-reports reference agent (no API key, top-voted / top-bounty / keyword / program filter) | arsenal |
| 80+ dork corpus across 9 categories | arsenal |
Breach Intelligence
| Capability | Skill |
|---|---|
| HudsonRock Ca direct API (free; FYI: web-UI wraps a public JSON endpoint) | arsenal |
| Domain-le se mapping | arsenal |
| SSO_EXPOSURE finding + legacy-mail-decommissioned escalation pattern | arsenal |
| Breach × identity correlation (HudsonRock + HIBP + DeHashed + IntelX) | methodology |
& Edge-Appliance Fingerprinting
| Capability | Skill |
|---|---|
| Citrix Netscaler · F5 BIG-IP · Pulse Secure / Ivanti · FortiGate | arsenal |
| PaloAlto GlobalProtect · Cisco AnyConnect · / ESXi / Horizon | arsenal |
| Microsoft Exchange OWA (ProxyShell / ProxyLogon / ProxyNotShell) | arsenal |
| KEV C + EPSS scoring + Metasploit a | arsenal |
| WAF / CDN bypass + origin discovery (8 techniques) | methodology, arsenal |
Email Security
| Capability | Skill |
|---|---|
| SPF / DMARC / DKIM / BIMI / MTA-STS / TLS-RPT / DNSSEC audit (bash + PowerShell) | arsenal |
| DMARC reporting- inference (Kratikal / dmarcian / / Agari / EasyDMARC) | arsenal |
| TXT token catalog (35+ SaaS tenants) | arsenal |
| MX → IdP / mail-host inference | arsenal |
Human Intelligence
| Capability | Skill |
|---|---|
| LinkedIn employee enumeration (P0–P5 role tiers · sock-puppet hygiene) | arsenal |
| Job posting tech-stack analysis (Lever · Greenhouse · AshbyHQ · Workable) | arsenal |
| Slack / Discord /
| Sat imagery for physical recon (Google Earth · NearMap · Sentinel Hub) | arsenal |
| Email-pattern inference (8 templates) | arsenal |
Supply Chain
| Capability | Skill |
|---|---|
| Package-registry leak hunting (npm · PyPI · RubyGems · Cargo · Packagist · NuGet · Maven) | arsenal |
| Typosquat sur | arsenal |
| Postman public-workspace search ( endpoint) | arsenal |
| Stack Exchange OSINT sweep (8 sites) | arsenal |
Reporting & Deli
| Capability | Skill |
|---|---|
| Findings rubric (CRITICAL/HIGH/MED/LOW/INFO + escalation) | methodology |
| Se decision matrix (88 worked examples) | arsenal |
| Attack-path hint patterns (27 templates) | arsenal |
| Bug-bounty submission templates (HackerOne / Bugcrowd / Intigriti) | methodology |
| Client deli templates (exec summary · risk-translation matrix · cadence) | methodology |
| Reproduction package | methodology |
Sector-Specific
| Capability | Skill |
|---|---|
| Healthcare (DICOM · HL7 v2 · FHIR · Epic / Cerner / Allscripts) | arsenal |
| Finance (SWIFT · FIX · Bloomberg · Temenos / Finacle / FIS / Fiserv) | arsenal |
| ICS / SCADA (Modbus · BACnet · Siemens S7 · DNP3 · EtherNet/IP) | arsenal |
| IoT (MQTT · CoAP · UPnP · Hik / Dahua DVRs) | arsenal |
| Go (.gov / .mil · FedRAMP · FISMA · CUI · SAM.gov) | arsenal |
---
Capability Map
Eight skills, thirteen capability domains — the core recon pair plus six organization-grade depth skills. Drill into the Skill Index above for concrete sub-capabilities.
---
Engagement Flow
---
Usage
With Claude Code
Then, in any Claude Code session, ask an OSINT question — the skills auto-load and each triggers on its own relevant phrases. Install only the core pair (osint-methodology + offensi) if you want the recon backbone without the org-grade depth skills.
With the Claude Skills System
Manual (Claude.ai / Claude API)
Paste the contents of any SKILL.md into a Project's system prompt or prepend it to your con. Both files are plain Markdown — also usable as a personal cheat-sheet without Claude.
---
Authorization
These skills are intended for assets you own or have written authorization to assess (red-team rules of engagement, bug-bounty in-scope assets, ASM contracts).
All eight skills include a soft scope-check when you ask Claude to act against an un third-party target, and the depth skills carry explicit hard-boundary sections (e.g. identity-pro ends at user *enumeration* — ne spray or credential submission; cloud-saas-exposure decodes an AWS account ID offline but ne AWS APIs with it). They explicitly exclude acti, post-exploitation, credential submission, token forging/replay, malware de, and other acti beyond OSINT-dri. See SECURITY.md for the full posture.
---
Documentation
| Doc | Contents |
|---|---|
| docs/architecture.md | Design philosophy · asset-graph model · confidence/se/detectability models · sidecar coordination · diagrams |
| docs/co.md | Honest practitioner-co breakdown by archetype + engagement phase |
| docs/installation.md | Symlink installs and multi-en install patterns |
| docs/usage.md | Trigger-phrase reference and prompt templates |
| examples/ | 4 end-to-end engagement walk-throughs (quick recon · bug-bounty · M365 deep · secret hunting) |
| tests/smoke-test-prompts.md | 56-prompt self-e suite (current grade: 56/56 PASS) |
| CHANGELOG.md | history |
| CONTRIBUTING.md | Pull-request guidelines |
---
Sponsors
<p align="center">
<a href="
<source media="(prefers-color-scheme: dark)" srcset="assets/sponsors/atlas-cloud-dark.svg">
<img alt="Atlas Cloud" src="assets/sponsors/atlas-cloud-light.svg" width="340">
</picture></a>
</p>
Atlas Cloud is a full-modal AI inference platform that gi a single AI API to access video generation, image generation, and LLM APIs. Instead of managing multiple integrations, you connect once and get unified access to 300+ curated models across all modalities.
Check out Atlas Cloud's new coding plan promotion for more budget-friendly API access: <
<p align="center">
<a href="
<source media="(prefers-color-scheme: dark)" srcset="assets/sponsors/tw360-dark.svg">
<img alt="ThreatWatch360" src="assets/sponsors/tw360-light.svg" width="430">
</picture></a>
</p>
ThreatWatch360 is an AI-powered offensi platform: continuous Attack Surface Management, AI-assisted penetration testing, brand protection, dark-web monitoring, and Cyber Threat Intelligence in one platform. findings with proof-of-concept and business-impact prioritization — signal o fatigue.
---
About
Operational tradecraft accumulated across external attack-surface engagements, codified into Claude skills. Engagement-platform agnostic - slot into any ASM / ticketing / asset-graph platform you already use, or none.
Author: ElementalSoul
Original framework: SnailSploit/offensi (v1.x)
Inspired by: Bellingcat's Online In Toolkit
· IntelTechniques
· OSINT Framework
Tool in:
. ProjectDiscovery
· Six2dez reconftw
· SecLists
· Assetnote Wordlists
License
This project is dual-licensed:
To be precise about the boundary: *.py, *.sh, and other source files are MIT; *.md documentation, wordlists, regex catalogs, and rubrics are CC BY 4.0.
Reuse the content freely — including commercially — as long as you credit Sachin Sharma / Claude-OSINT and link back to this repository.
---
> *"Gi the right skill and it stops being a chatbot. It becomes an operator."*
项目信息
开发语言:Python
Star 数:2770
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕8 Claude skills · 100+ recon capabilities · 80 secret-regex patterns · 80+ dorks · 9 read-only credential validators · 27 attack-path templates · ~10,000 lines of structured tradecraft. Drop-in SKILL.md files that turn Claude into a god-mode external recon operator for authorized red-team and bug-bounty engagements.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Claude-OSINT - 8 Claude skills · 100+ recon capabilities · 80 sec |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:34:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 252 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |