 红蓝攻防
点击放大
inventory - Asset inventory of over 800 public bug bounty prog
项目说明
<h1 align="center">In <a href=" src=" alt="Tweet" height="20"/></a></h1>
<h3 align="center">Attack Surface Management of public bug bounty programs.</h3>
The data we collect here includes DNS and Web Server data of public bug bounty programs.
Our aim with this project is to:
<img src="screenshots/banner.png" />
How it works
The setup consists of two workflows
* In 3.0 - Targets
* In 3.0
In 3.0 - Targets
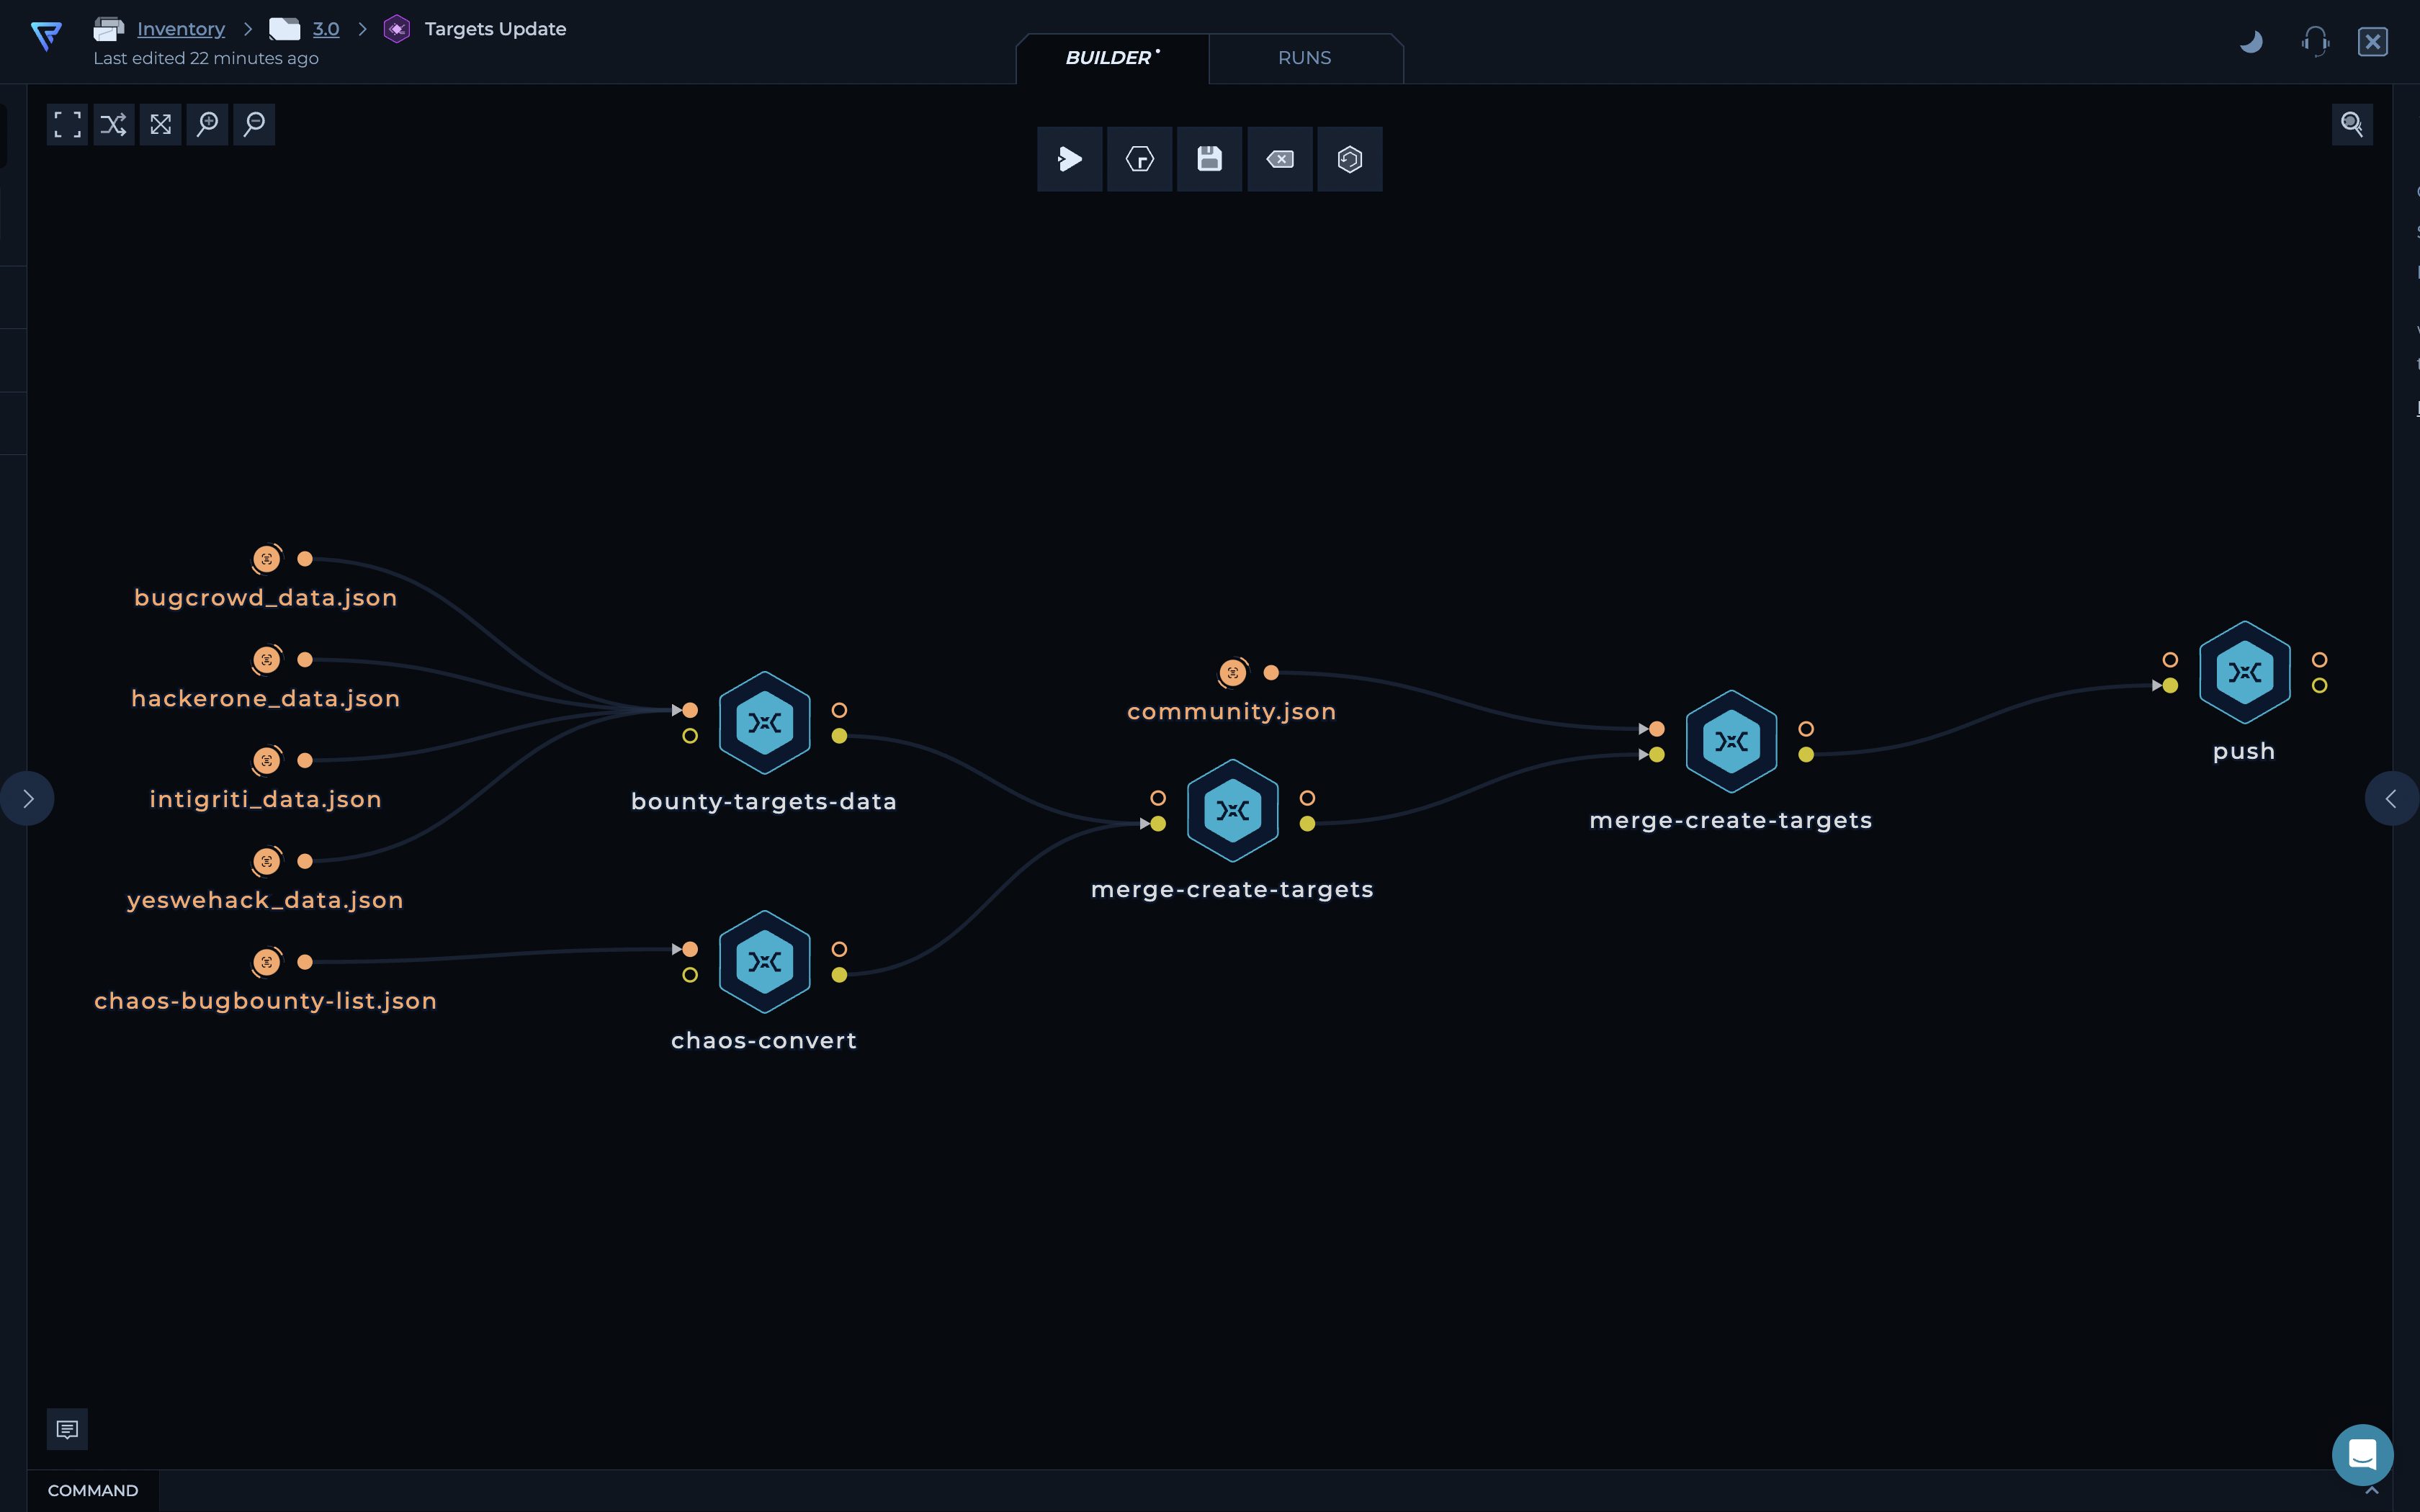
This workflow streamlines the consolidation of bug bounty program data from sources, ensuring a comprehensive and organized view. Let's break it down:
1. Data collection: The workflow fetches data from two important sources:
- Bounty Targets Data: This repository contains a wealth of bug bounty program information.
- Chaos Public Bug Bounty Programs: It provides additional bug bounty program data.
2. Data transformation: The collected data undergoes transformation using Python scripts. The scripts convert the data into a specific format, ensuring consistency and ease of analysis. You can find the detailed data format in the targets.json file.
3. Program merging: To avoid duplication, the workflow merges programs with the same URL together. This consolidation eliminates redundancies and presents a unified view of bug bounty programs.
4. Community program inclusion: The workflow incorporates an additional set of programs from the community.json file. These programs are merged with the existing dataset, enhancing its co and di.
5. Final output: The workflow generates a final consolidated JSON file, targets.json, which encompasses all the merged bug bounty program data. This file serves as a resource for bug bounty researchers, pro a centralized and comprehensive view of programs.
!Trickest Targets
Note: The screenshot abo a representation of the workflow.
In 3.0
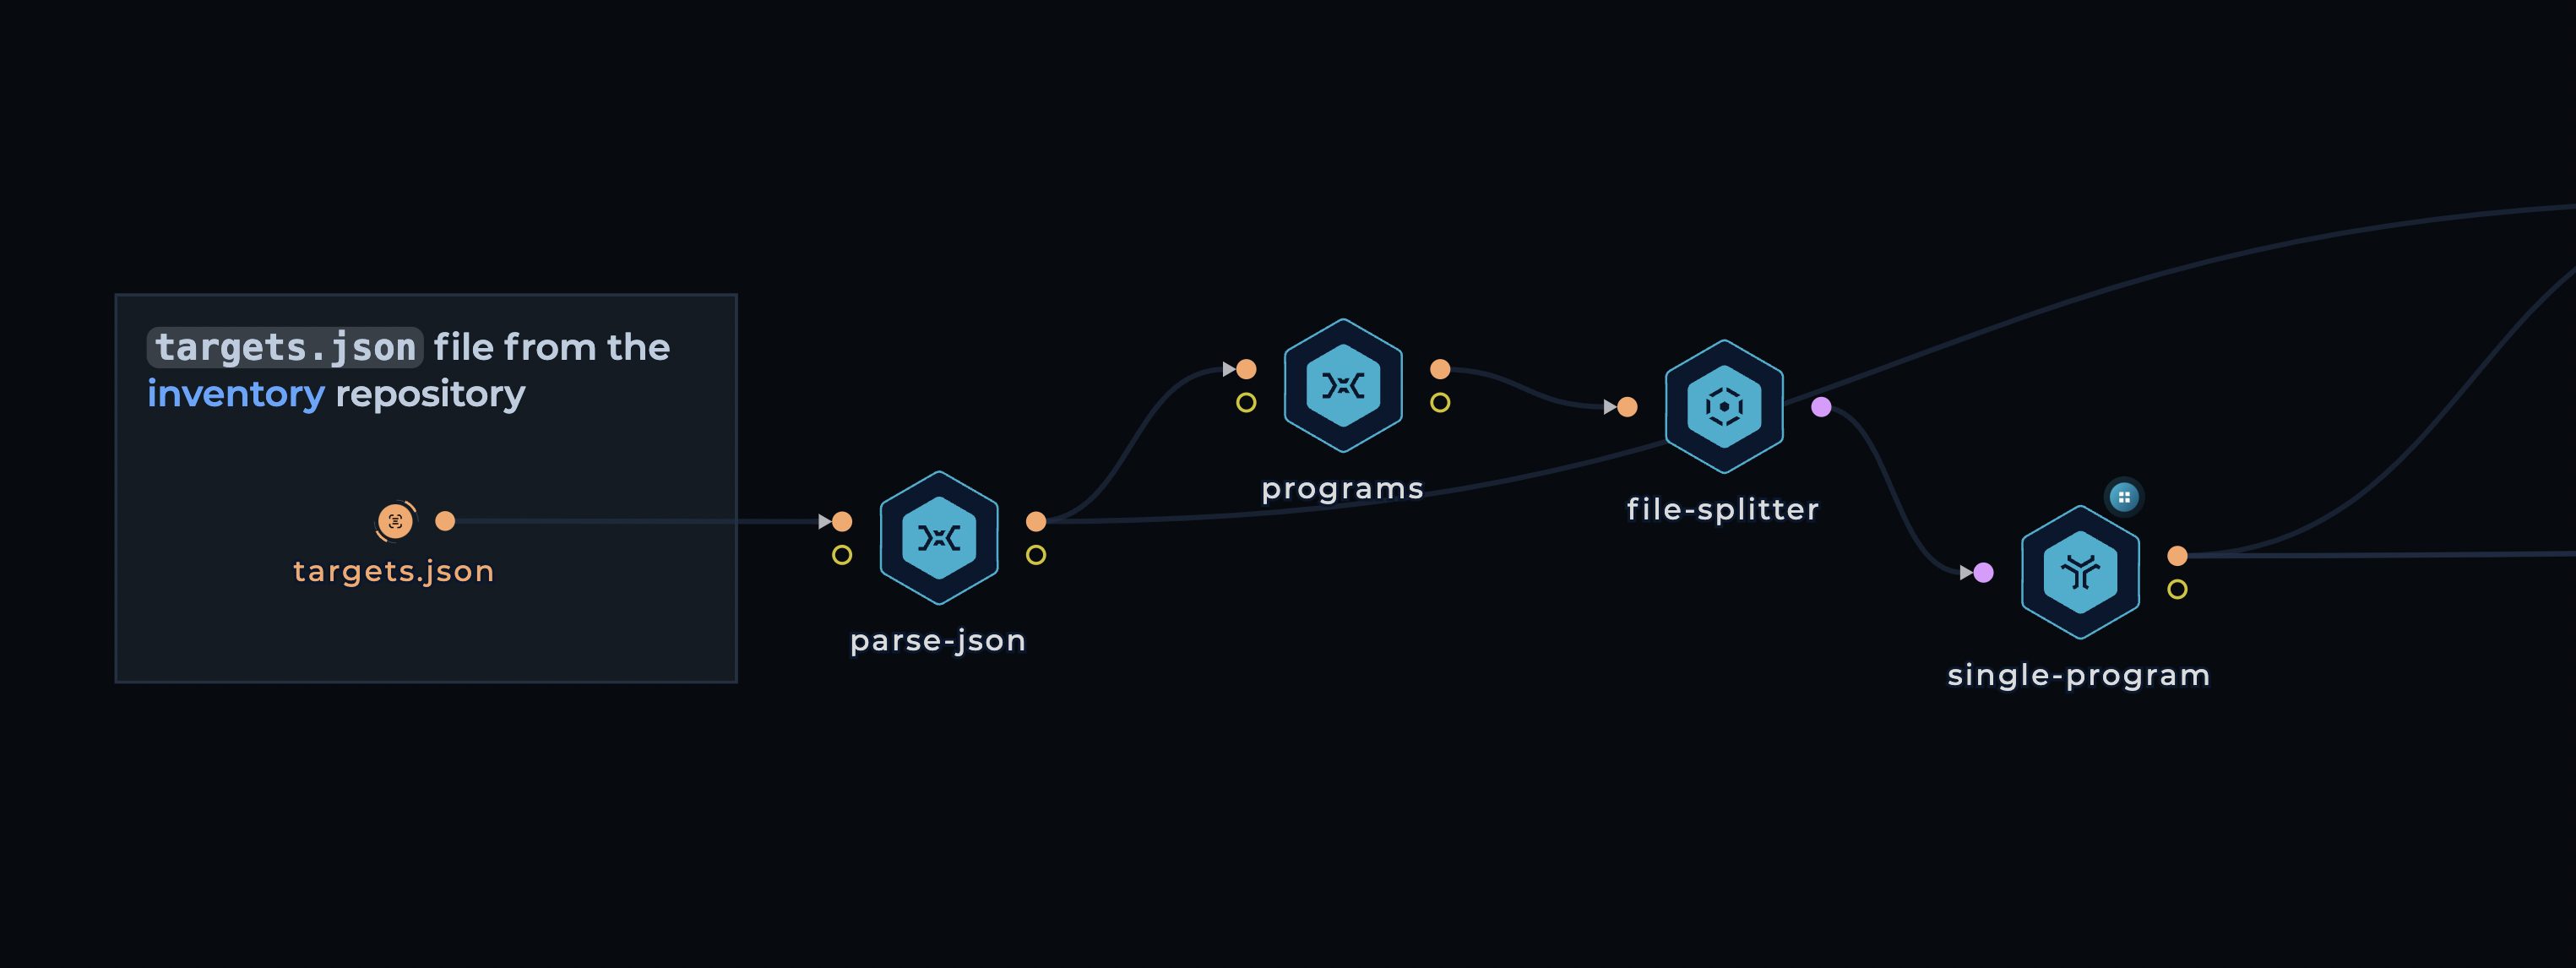
1. Gathering the tagets: Get the list of domains from targets.json, and extract program names.
2. Making workflow run in parallel: Extracted program names are connected file-splitter node to make the whole workflow distributed per program
!Trickest Parsing Targets
3. Passi:
* Use subfinder, vita, findomain to get passi data.
* Use mksub to create a custom list of potential subdomains
* Resolve with puredns and trickest resolvers
* Generate custom-wordlists from passi with custom bash script
!Trickest Passi
4. Acti
* Use passi data and create a new bruteforce wordlist
* Use dsieve to get en per subdomain level
* Generate new potential subdomains with mksub and custom wordlist, with additional level2.txt wordlist
* Resol with puredns
!Trickest Acti
5. Permutations
* Merge active and passi from previous steps
* Extract en per subdomain le
* Use alterx to generate permutations and resolve with puredns
!Trickest Permutations
6. Collecting previous results
* Use python script that will get all of the previous hostnames.txt per program
* Use anew to get the new hostnames found
* zip acti, permutations per program to be pushed to repository
!Trickest Previous Results
7. Reporting
* Use dnsx to resol hostnames and python script for dns-report.csv; mark newly found domains coming from anew with [x]
* Use httpx to gather web servers and python script for `ser.csv
* Push to the repository
!Trickest Reporting
Final workflow
!Trickest In 3.0 Workflow
---
> Note: As described, almost e in this repository is generated automatically. We carefully designed the workflows (and continue to develop them) to ensure the results are as accurate as possible.
Contribution
All contributions/ideas/suggestions are welcome! If you want to add/edit a target/workflow, feel free to send us a PR with new targets through community.json, tweet at us , or join the con on Discord.
Build your own workflows!
We believe in the value of tinkering. Sign up for a demo on trickest.com to customize this workflow to your use case, get access to many more workflows, or build your own from scratch!
<img src="screenshots/banner.png" />
项目信息
开发语言:Shell
Star 数:1614
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Asset inventory of over 800 public bug bounty programs.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | inventory - Asset inventory of over 800 public bug bounty prog |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:35:20 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 179 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |