 红蓝攻防
点击放大
GooFuzz - GooFuzz is a tool to perform fuzzing with an OSINT
项目说明
<p align="center">
<img width="460" height="300" src="images/goofuzz.png">
</p>
<p align="center">
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
<a href="
<img src="
<a href="">
<img src="
</a>
<br>
<h1 align="center">GooFuzz - The Power of Google Dorks</h1>
<br>
</p>
Credits
###### Author: M3n0sD0n4ld
###### Twitter: @Da
Description:
GooFuzz is a script written in *Bash Scripting* that uses ad Google search techniques to obtain sensiti in files or directories without making requests to the web server.
What's new
Want to learn about the new features in 2.0 and how to use the tool correctly?
Check out the following article and get the most out of the tool.
Prerequisites
cxId and apikey to a file. Both are free.
#### Get your API Key
1. Go to Google Cloud Console.
2. Create a new project (give it a name, such as GooFuzz-Project).
3. In the search bar at the top, type "Custom Search API" and click the Enable button.
4. Once enabled, go to the "Credentials" tab in the left-hand menu.
5. Click on "Create credentials" -> "API key".
6. Keep it safe! That's your API key.
#### 2. Get your CX ID (Programmable Search Engine)
1. Go to the Programmable Search Engine dashboard.
2. Click “Add” to create a new search engine.
3. In the “What to search” section, select “Search the entire Web” (this is vital so that GooFuzz is not limited to a single website).
4. Give it a name (e.g., GooFuzz-Search) and click Create.
5. Now go to the settings for the search engine you just created and look for “Search engine ID.”
6. That alphanumeric code is your cxId.
Download and install:
Docker :
Use:
Menu
Lists files by extensions separated by commas.
Lists files by extensions contained in a txt file.
List files, directories and e by means of a wordlist (it is recommended to use only very small files).
Lists directories and files by specifying paths, words or file names.
Exclusion of subdomains in your searches (separated by commas or by a list)
Example 1:
In this example we remove the subdomain "*www.earthdata.nasa.gov*" from the search.
Example 2:
Using the previous example, we create a file called "*exclusion_list.txt*" and insert the three subdomains to exclude, we perform the same search again, but passing the list of excluded targets.
Subdomains enumeration
The functionality to list subdomains (parameter "*-s*") and in conjunction with a number of between 10 and 20 pages (parameter "*-p*"), it is possible to obtain a large number of subdomains of the organization.
Files found containing enumeration
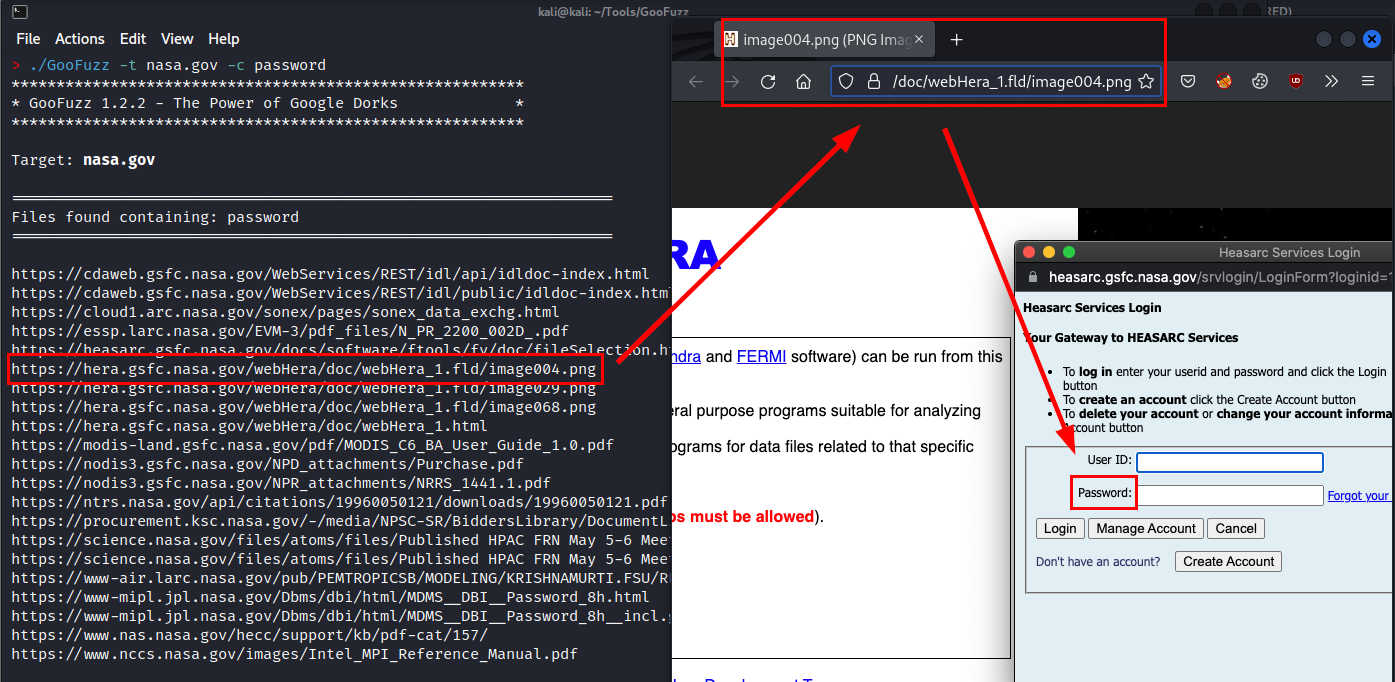
The functionality to list files by their content (parameter "*-c*"), is very useful to identify relevant files (e.g. containing the word "*password*"), even if the word is in an image file (e.g. *.png*).
#### Proof of concept with an image
!Screenshot
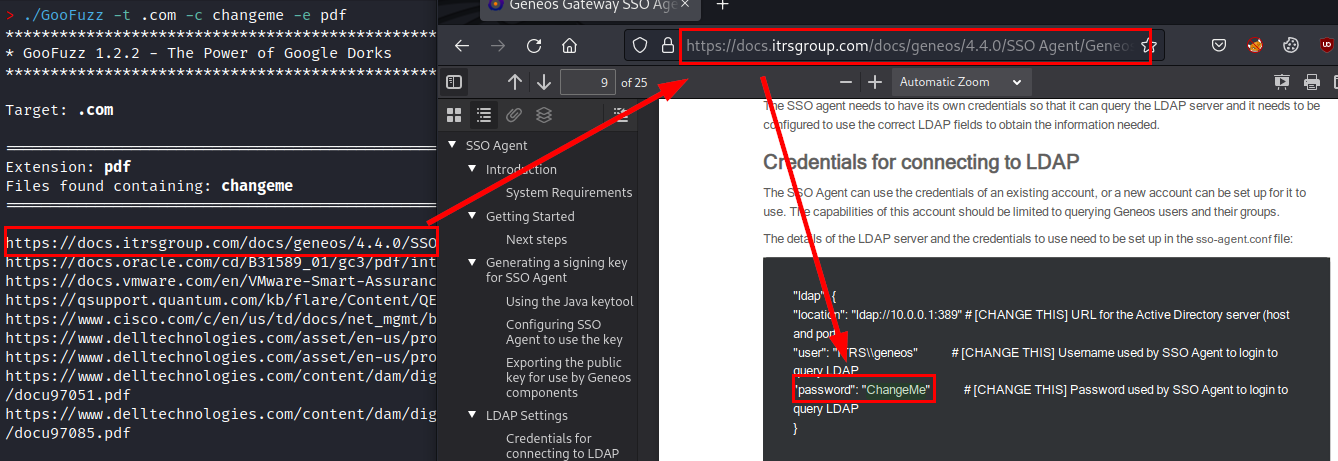
Or even, search for a possible password in a pdf file:
#### Proof of concept with an PDF file
!Screenshot
Disclaimer
Useful?
If you like the tool, find it useful in your work, Bug Bounty or as a hobby, you could help me like this:
<p align="left">
<a href=" target="_blank">
<img src="images/paypal.png"></img></a>
</p>
项目信息
开发语言:Shell
Star 数:1592
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕GooFuzz is a tool to perform fuzzing with an OSINT approach, managing to enumerate directories, files, subdomains or parameters without leaving evidence on the target's server and by means of advanced Google searches (Google Dorking).展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | GooFuzz - GooFuzz is a tool to perform fuzzing with an OSINT |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:35:25 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 399 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |