 红蓝攻防
点击放大
项目说明
<p align="center"><img width=450 alt="AutoRDPwn" src="
AutoRDPwn is a post-exploitation framework created in Powershell, designed primarily to automate the Shadow attack on Microsoft Windows computers. This (listed as a feature by Microsoft) allows a remote attacker to view his 's desktop without his consent, and e it on demand, using tools native to the operating system itself.
Thanks to the additional modules, it is possible to obtain a remote shell through Netcat, dump system hashes with Mimikatz, load a remote keylogger and much more. All this, Through a completely intuitive menu in se languages.
Additionally, it is possible to use it in a reverse shell through a series of parameters that are described in the usage section.
Requirements
Powershell 4.0 or higher
Changes
5.1
• Many bugs fixed
• Aesthetic impro and impro times
• Proxy-Aware connection through system settings
• It is now possible to use the offline tool by downloading the .zip file
• Language auto-detection by pressing the enter key
• In has been replaced by SharpRDP
• PowerUp has been replaced by In
• Creation of the automatic cleaning subroutine in the
• New module a: SMB Shell encrypted with AES
• New module a: Change user with RunAs
*The rest of the changes can be consulted in the CHANGELOG file
Usage
This application can be used locally, remotely or to pi teams.
When used remotely in a reverse shell, it is necessary to use the following parameters:
| Parameter | Description |
| :---------------------- | :--------------------------------------------------------------------------------------------- |
| -admin / -noadmin | Depending on the permissions we have, we will use one or the other |
| -nogui | This will avoid loading the menu and some colors, guaranteed its functionality |
| -lang | We will choose our language (English, Spanish, French, German, Italian, Russian or Portuguese) |
| -option | As with the menu, we can choose how to launch the attack |
| -shadow | We will decide if we want to see or control the remote device |
| -createuser | This parameter is optional, the user AutoRDPwn:AutoRDPwn will be created on the machine |
| -noclean | Disables the process of undoing all changes on the computer |
Local execution on one line:
Example of remote execution on a line:
The detailed guide of use can be found at the following link:
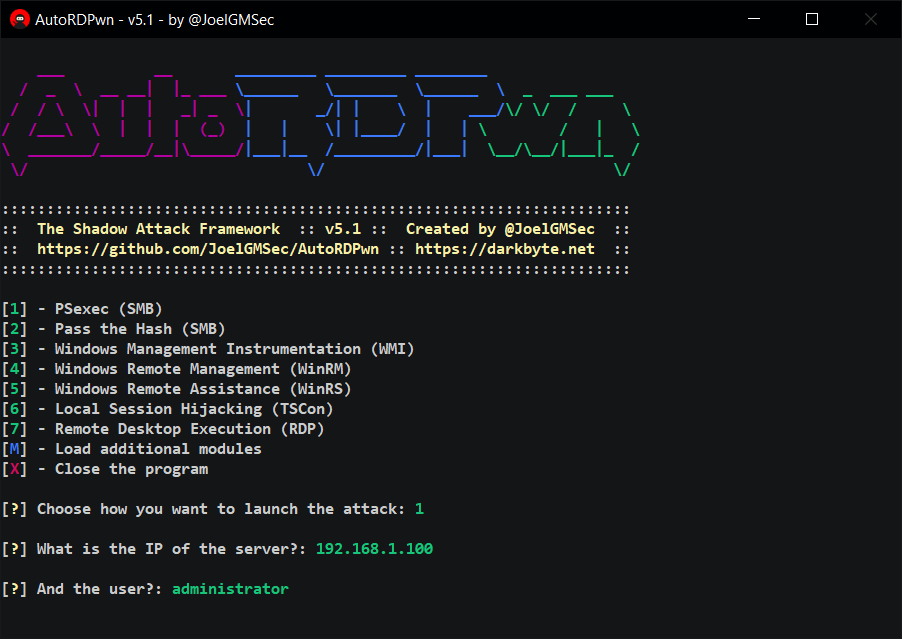
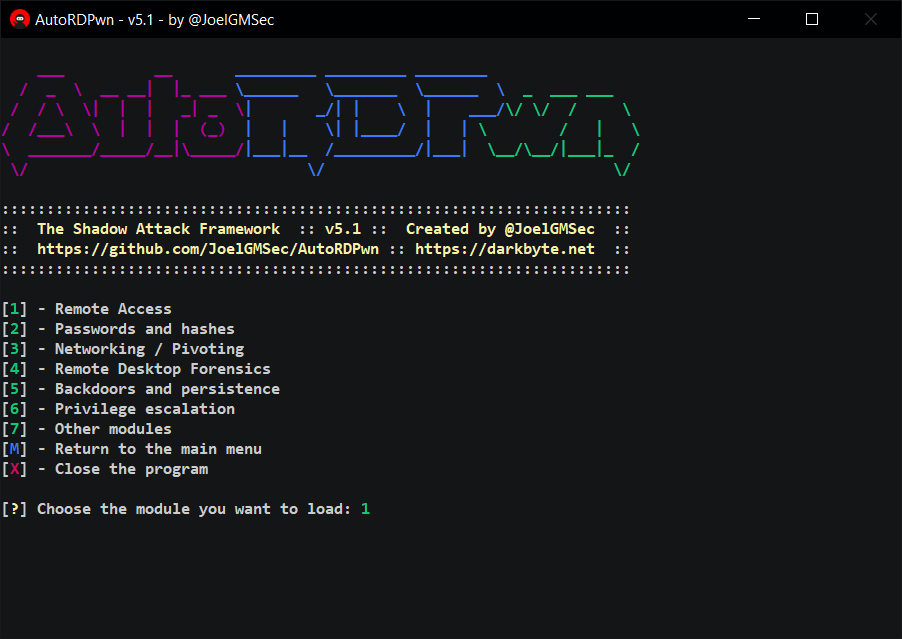
Screenshots
!AutoRDPwn1_en
!AutoRDPwn2_en
License
This project is licensed under the GNU 3.0 license - see the LICENSE file for more details.
Credits and Acknowledgments
This framework has been created and designed from scratch by Joel Gámez Molina //
Some modules use third-party code, scripts, and tools, particularly:
• Chachi-Enumerator by *Luis Vacas* -->
• In by *Halil Dalabasmaz* -->
• In by *Nikhil "SamratAshok" Mittal* -->
• In by *Ke* -->
• Mimikatz by *Benjamin Delpy* -->
• PsExec by *Mark Russinovich* -->
• RDP Wrapper by *Stas'M Corp.* -->
• SharpRDP by *Steven F* -->
And many more, that do not fit here.. Thanks to all of them and their excellent work.
Contact
This software does not offer any kind of guarantee. Its use is exclusive for educational en and / or security audits with the corresponding consent of the client. I am not responsible for its misuse or for any possible damage caused by it.
For more information, you can find me on Twitter as and on my blog darkbyte.net.
Support
You can support my work buying me a coffee:
<img width=250 alt="buymeacoffe" src="
项目信息
开发语言:PowerShell
Star 数:1117
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The Shadow Attack Framework展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AutoRDPwn - The Shadow Attack Framework |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:36:10 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 312 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |