 红蓝攻防
点击放大
ProtectMyTooling - Multi-Packer wrapper letting us daisy-chain variou
项目说明
!1.png
Don't Detect Tools - Detect Techniques
Rationale behind releasing this software was outlined in an acompanying blog post:
Intro
Script that wraps around multitude of packers, protectors, obfuscators, shellcode loaders, encoders, generators to produce complex protected Red Team implants.
Your perfect companion in Malware De CI/CD pipeline, helping watermark your artifacts, collect IOCs, backdoor and more.
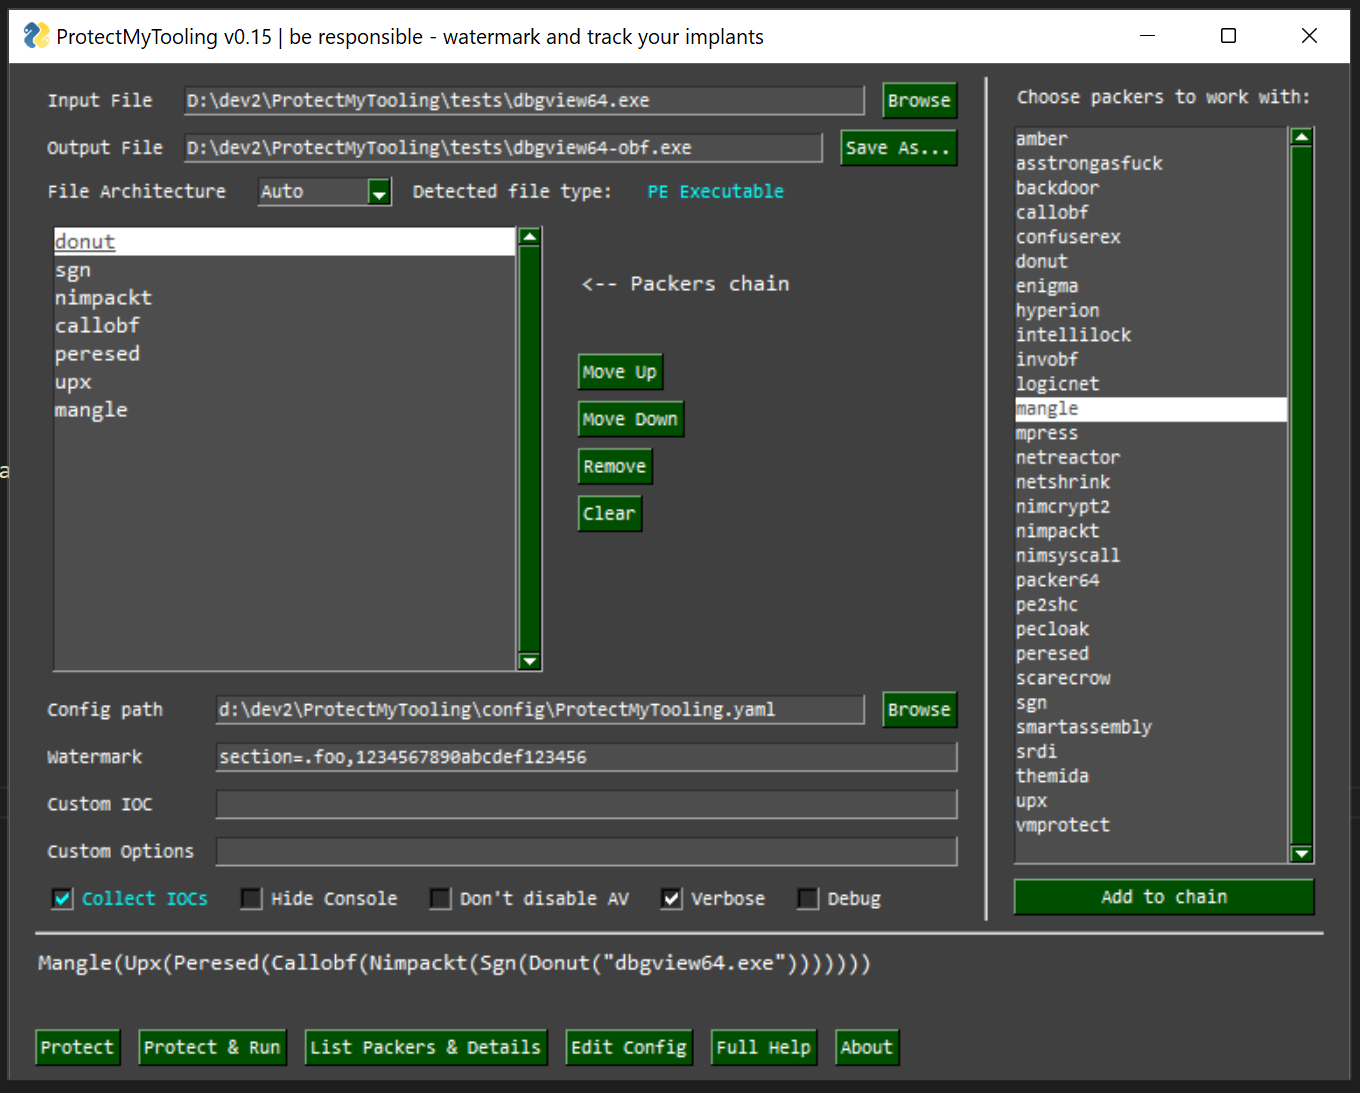
ProtectMyToolingGUI.py
!3.png
With ProtectMyTooling you can quickly obfuscate your binaries without having to worry about clicking through all the Dialogs, interfaces, menus, creating projects to obfuscate a single binary, clicking through all the options a and wasting time about all that nonsense. It takes you straight to the point - to obfuscate your tool.
Aim is to offer the most con interface possible and allow to le _a daisy-chain of multiple packers_ combined on a single binary.
That's right - we can launch ProtectMyTooling with several packers at once:
The abo will firstly pass mimikatz.exe to the Hyperion for obfuscation, and then the result will be provided to UPX for compression. Resulting with UPX(Hyperion(file))
Features
callobf,hyperion,upx will produce artifact UPX(Hyperion(CallObf(file)))protected-upload and protected-execute-assembly commandsInstallation
This tool was designed to work on Windows, as most packers natively target that platform.
Some features may work however on Linux just fine, nonetheless that support is not fully tested, please report bugs and issues.
1. First, disable your AV and add contrib directory to exclusions. That directory contains obfuscators, protectors which will get flagged by AV and removed.
2. Then clone this repository
3. Actual installation is straightforward:
Windows
Linux
Gimmicks
For ScareCrow packer to run on Windows 10, there needs to be WSL installed and bash.exe a (in %PATH%).
Then, in WSL one needs to have golang installed in at least 1.16:
Configuration
To plug-in supported obfuscators, change default options or point ProtectMyTooling to your obfuscator executable path, you will need to adjust config\ProtectMyTooling.yaml configuration file.
There is also config\sample-full-config.yaml file containing all the a options for all the supported packers, serving as reference point.
Friendly reminder
---
Usage
Before ProtectMyTooling's first use, it is essential to adjust program's YAML configuration file ProtectMyTooling.yaml.
The order of parameters processal is following:
There, supported packer paths and options shall be set to enable.
Scenario 1: Simple ConfuserEx obfuscation
Usage is very simple, all it takes is to pass the name of obfuscator to choose, input and output file paths:
.;;;;;;`;;;; .;;;;;;;;;;;;;;;\''';;;;\'\''',;;;''
[[ ,[[ \[[,[[ \[[,[[[ [[[ [[[[[. '[[[[ [[[[[[/
$$ $$$, $$$$$, $$$$$' $$$ $$$ "Y$c$"$$c. "$$
88, "888,_ _,88"888,_ _,88o88oo,._888 888 Y88Y8bo,,,o88o'YMUP"YMM
MMM "YMMMMMP" "YMMMMMP"""""YUMMMMM MMM YM
Red Team implants protection swiss knife.
Multi-Packer wrapping around multitude of packers, protectors, shellcode loaders, encoders.
Mariusz Banach / mgeeky '20-'22, <>
v0.16
[.] Processing x86 file: "\Rubeus.exe"
[.] Generating output of ConfuserEx(<file>)...
[+] SUCCEEDED. Original file size: 417280 bytes, new file size ConfuserEx(<file>): 756224, ratio: 181.23%
C:\> py ProtectMyTooling.py confuserex Rubeus.exe Rubeus-obf.exe -r --cmdline "hash /password:foobar"
[...]
[.] Processing x86 file: "\Rubeus.exe"
[.] Generating output of ConfuserEx(<file>)...
[+] SUCCEEDED. Original file size: 417280 bytes, new file size ConfuserEx(<file>): 758272, ratio: 181.72%
Running application to test it...
______ _
(_____ \ | |
_____) )_ _| |__ _____ _ _ ___
| __ /| | | | _ \| ___ | | | |/___)
| | \ \| |_| | |_) ) ____| |_| |___ |
|_| |_|____/|____/|_____)____/(___/
v2.0.0
[*] Action: Calculate Password Hash(es)
[*] Input password : foobar
[*] rc4_hmac : BAAC3929FABC9E6DCD32421BA94A84D4
[!] /user:X and /domain:Y need to be supplied to calculate AES and DES hash types!
PS> py .\ProtectMyTooling.py callobf,upx,hyperion beacon.exe beacon-obf.exe -i -I operation_chimera -w dos-stub=fooobar -w checksum=0xaabbccdd
[...]
[.] Processing x64 file: "beacon.exe"
[>] Generating output of CallObf(<file>)...
[.] Before obfuscation file's PE IMPHASH: 17b461a082950fc38b80c
[.] After obfuscation file's PE IMPHASH: 378d9692fe91eb54206e98c224a25f43
[>] Generating output of UPX(CallObf(<file>))...
[>] Generating output of Hyperion(UPX(CallObf(<file>)))...
[+] Setting PE checksum to 2864434397 (0xaabbccdd)
[+] Successfully watermarked resulting artifact file.
[+] IOCs written to: beacon-obf-ioc.csv
[+] SUCCEEDED. Original file size: 288256 bytes, new file size Hyperion(UPX(CallObf(<file>))): 175616, ratio: 60.92%
csv
timestamp,filename,author,context,comment,md5,sha1,sha256,imphash
2022-06-10 03:15:52,beacon.exe,mgeeky File,test,dcd6e13754ee753928744e27e98abd16,298de19d4a987d87ac83f5d2d78338121ddb3cb7,0a64768c46831d98c5667d26dc731408a5871accefd38806b2709c66cd9d21e4,17b461a082950fc38b80c
2022-06-10 03:15:52,y49981l3.bin,mgeeky artifact: CallObf(<file>),test,50bbce4c3cc928e274ba15bff0795a8c,15bde0d7fbba1841f7433510fa9aa829f8441aeb,e216cd8205f13a5e3c5320ba7fb88a3dbb6f53ee8490aa8b4e1baf2c6684d27b,378d9692fe91eb54206e98c224a25f43
2022-06-10 03:15:53,nyu2rbyx.bin,mgeeky artifact: UPX(CallObf(<file>)),test,4d3584f10084cded5c6da7a63d42f758,e4966576bdb67e389ab1562e24079ba9bd565d32,97ba4b17c9bd9c12c06c7ac2dc17428d509b64fc8ca9e88ee2de02c36532be10,9aebf3da4677af9275c461261e5abde3
2022-06-10 03:15:53,beacon-obf.exe,mgeeky artifact: Hyperion(UPX(CallObf(<file>))),test,8b706ff39dd4c8f2b031c8fa6e3c25f5,c64aad468b1ecadada3557cb3f6371e899d59790,087c6353279eb5cf04715ef096a18f83ef8184aa52bc1d5884e33980028bc365,a46ea633057f9600559d5c6b328bf83d
2022-06-10 03:15:53,beacon-obf.exe,mgeeky obfuscated artifact,test,043318125c60d36e0b745fd38582c0b8,a7717d1c47cbcdf872101bd488e53b8482202f7f,b3cf4311d249d4a981eb17a33c9b89eff656fff239e0d7bb044074018ec00e20,a46ea633057f9600559d5c6b328bf83d
C:\> py ProtectMyTooling.py -L
[...]
Red Team implants protection swiss knife.
Multi-Packer wrapping around multitude of packers, protectors, shellcode loaders, encoders.
Mariusz Banach / mgeeky '20-'22, <>
v0.16
+----+----------------+-------------+-----------------------+-----------------------------+------------------------+--------------------------------------------------------+
| # | Name | Type | Licensing | Input | Output | Author |
+----+----------------+-------------+-----------------------+-----------------------------+------------------------+--------------------------------------------------------+
| 1 | amber | open-source | Shellcode Loader | PE | EXE, Shellcode | Ege Balci |
| 2 | asstrongasfuck | open-source | .NET Obfuscator | .NET | .NET | Charterino, klezVirus |
| 3 | atompepacker | open-source | PE EXE/DLL Protector | PE | EXE, DLL | ORCA (, ) |
| 4 | backdoor | open-source | Shellcode Loader | Shellcode | PE | Mariusz Banach, |
| 5 | callobf | open-source | PE EXE/DLL Protector | PE | PE | Mustafa Mahmoud, |
| 6 | confuserex | open-source | .NET Obfuscator | .NET | .NET | mkaring |
| 7 | donut-packer | open-source | Shellcode Con | PE, .NET, , JScript | Shellcode | TheWover |
| 8 | enigma | commercial | PE EXE/DLL Protector | PE | PE | The Enigma Protector De Team |
| 9 | freeze | open-source | Shellcode Loader | Shellcode | PE | Matt Eidelberg () |
| 10 | hyperion | open-source | PE EXE/DLL Protector | PE | PE | nullsecurity team |
| 11 | intellilock | commercial | .NET Obfuscator | PE | PE | Eziriz |
| 12 | invobf | open-source | Powershell Obfuscator | Powershell | Powershell | Daniel Bohannon |
| 13 | logicnet | open-source | .NET Obfuscator | .NET | .NET | AnErrupTion, klezVirus |
| 14 | mangle | open-source | Executable Signing | PE | PE | Matt Eidelberg () |
| 15 | mpress | freeware | PE EXE/DLL Compressor | PE | PE | E |
| 16 | netreactor | commercial | .NET Obfuscator | .NET | .NET | Eziriz |
| 17 | netshrink | open-source | .NET Obfuscator | .NET | .NET | Bartosz Wójcik |
| 18 | nimcrypt2 | open-source | Shellcode Loader | PE, .NET, Shellcode | PE | |
| 19 | nimpackt | open-source | Shellcode Loader | .NET, Shellcode | PE | Cas (@ch) |
| 20 | nimsyscall | sponsorware | Shellcode Loader | PE, .NET, Shellcode | PE | |
| 21 | packer64 | open-source | PE EXE/DLL Compressor | PE | PE | John Adams, |
| 22 | pe2shc | open-source | Shellcode Con | PE | Shellcode | |
| 23 | pecloak | open-source | PE EXE/DLL Protector | PE | PE | Mike Czumak, , buherator / v-p-b |
| 24 | peresed | open-source | PE EXE/DLL Protector | PE | PE | Martin Vejnár, Avast |
| 25 | peunion | freeware | PE EXE/DLL Compressor | PE, .NET | PE | Martin Fischer / bytecode77 <> |
| 26 | scarecrow | open-source | Shellcode Loader | Shellcode | DLL, JScript, CPL, XLL | Matt Eidelberg () |
| 27 | sgn | open-source | Shellcode Encoder | Shellcode | Shellcode | Ege Balci |
| 28 | smartassembly | commercial | .NET Obfuscator | .NET | .NET | Red-Gate |
| 29 | srdi | open-source | Shellcode Encoder | DLL | Shellcode | Nick Landers, |
| 30 | themida | commercial | PE EXE/DLL Protector | PE | PE | Oreans |
| 31 | upx | open-source | PE EXE/DLL Compressor | PE | PE | Markus F.X.J. Oberhumer, László Molnár, John F. Reiser |
| 32 | | commercial | PE EXE/DLL Protector | PE | PE | |
+----+----------------+-------------+-----------------------+-----------------------------+------------------------+--------------------------------------------------------+
py ProtectMyTooling [...] -w dos-stub=fooooobar -w checksum=0xaabbccdd -w section=.coco,ALLYOURBASEAREBELONG
py RedWatermarker.py beacon-obf.exe -c 0xaabbccdd -t fooooobar -e bazbazbaz -s .coco,ALLYOURBASEAREBELONG
cmd> py RedWatermarker.py --help
;
ED.
,E#Wi
j. f#iE###G.
EW, .E#t E#fD#W;
E##j i#W, E#t t##L
E###D. L#D. E#t .E#K,
E#jG#W; :K#Wfff; E#t j##f
E#t t##f i##WLLLLtE#t :E#K:
E#t :K#E: .E#L E#t t##L
E#KDDDD###i f#E: E#t .D#W; ,; G: ,;
E#f,t#Wi,,, ,WW; E#tiW#G. f#i j. j. E#, : f#i j.
E#t ;#W: ; .D#;E#K##i .. GEEEEEEEL .E#t EW, .. : .. EW, E#t .GE .E#t EW,
DWi ,K.DL ttE##D. ;W, ,;;L#K;;. i#W, E##j ,W, .Et ;W, E##j E#t j#K; i#W, E##j
f. :K#L LWL E#t j##, t#E L#D. E###D. t##, ,W#t j##, E###D. E#GK#f L#D. E###D.
EW: ;W##L .E#f L: G###, t#E :K#Wfff; E#jG#W; L###, j###t G###, E#jG#W; E##D. :K#Wfff; E#jG#W;
E#t t#KE#L ,W#; :E####, t#E i##WLLLLt E#t t##f .E#j##, G#fE#t :E####, E#t t##f E##Wi i##WLLLLt E#t t##f
E#t f#D.L#L t#K: ;W#DG##, t#E .E#L E#t :K#E: ;WW; ##,:K#i E#t ;W#DG##, E#t :K#E:E#jL#D: .E#L E#t :K#E:
E#jG#f L#LL#G j###DW##, t#E f#E: E#KDDDD###i j#E. ##f#W, E#t j###DW##, E#KDDDD###E#t ,K#j f#E: E#KDDDD###i
E###; L###j G##i,,G##, t#E ,WW; E#f,t#Wi,,,.D#L ###K: E#t G##i,,G##, E#f,t#Wi,,E#t jD ,WW; E#f,t#Wi,,,
E#K: L#W; :K#K: L##, t#E .D#; E#t ;#W: :K#t ##D. E#t :K#K: L##, E#t ;#W: j#t .D#; E#t ;#W:
EG LE. ;##D. L##, fE tt DWi ,KK:... #G .. ;##D. L##, DWi ,KK: ,; tt DWi ,KK:
; ;@ ,,, .,, : j ,,, .,,
Watermark thy implants, track them in
Mariusz Banach / mgeeky '22, ()
<>
usage: RedWatermarker.py [options] <infile>
options:
-h, --help show this help message and exit
Required arguments:
infile Input implant file
Optional arguments:
-C, --check Do not actually inject watermark. Check input file if it contains specified watermarks.
- mode.
-d, --debug Debug mode.
-o PATH, --outfile PATH
Path where to sa file with watermark injected. If not given, will modify infile.
PE Executables Watermarking:
-t STR, --dos-stub STR
Insert watermark into PE DOS Stub (This program cannot be run...).
-c NUM, --checksum NUM
Preset PE checksum with this value (4 bytes). Must be number. Can start with 0x for hex value.
-e STR, --o STR
Append watermark to the file's O (at the end of the file).
-s NAME,STR, --section NAME,STR
Append a new PE section named NAME and insert watermark there. Section name must be shorter than 8 characters. Section will be marked Read-Only, non-executable.
PS> py ProtectMyTooling.py sgn,backdoor,amber beacon64.bin dbg.exe -B dbg.exe
::::::::::.:::::::.. ... :::::::::::.,:::::: .,-::::::::::::::::
;;;;;;;;;;;
]]nnn]]' [[,/[[[' ,[[ \[[, [[ [[cccc [[[ [[88bo,__,o, 88,
$$$"" $$$$$$c $$$, $$$ $$ $$"""" $$$ $$
888o 888b "88bo"888,_ _,88P 88, 888oo,_
. YMMMb :.-:.MM ::-. "YMMMMMP" MMM """"YUMMM"YUMMMMMP" MMM
;;,. ;;;';;. ;;;;'
[[[[, ,[[[[, '[[,[[['
$$$$$$$$"$$$ c$$"
888 Y88" 888o,8P"
    ::::::::::::mM...        ...     :::    :::::.    :::. .,-:::::/
;;;;;;;;.;;;;;;;. .;;;;;;;. ;;; ;;;;,;;-'
Full RedBackdoorer usage:
Cobalt Strike Integration
There is also a script that integrates ProtectMyTooling.py used as a wrapper around configured PE/.NET Packers/Protectors in order to easily transform input executables into their protected and compressed output forms and then upload or use them from within CobaltStrike.
The idea is to have an automated process of protecting all of the uploaded binaries or .NET assemblies used by execute-assembly and forget about protecting or obfuscating them manually before each usage. The added benefit of an automated approach to transform executables is the ability to have the same executable protected each time it's used, resulting in unique samples launched on target machines. That should nicely deceive EDR/A IOC sweeps while looking for the same artefact on different machines.
Additionally, the protected-execute-assembly command has the ability to look for assemblies of which
only name were given in a preconfigured assemblies directory (set in dotnet_assemblies_directory setting).
To use it:
1. Load CobaltStrike/ProtectMyTooling.cna in your Cobalt Strike.
2. Go to the menu and setup all the options
![options
3. Then in your Beacon's console you'll ha commands a:
* protected-execute-assembly - Executes a local, pre protected and compressed .NET program in-memory on target.protected-upload
* - Takes an input file, protects it if its PE executable and then uploads that file to specified remote location.bofnet_load_protected
* - Takes input .NET assembly file, passes it through configured .NET packers chain, loads generated output with bofnet_load. BOFNET needs to be loaded separetely for this to work.
Basically these commands will open input files, pass the firstly to the CobaltStrike/cobaltProtectMyTooling.py script, which in turn calls out to ProtectMyTooling.py. As soon as the binary gets obfuscated, it will be passed to your beacon for execution/uploading.
Cobalt Strike related Options
Here's a list of options required by the Cobalt Strike integrator:
* python3_interpreter_path - Specify a path to Python3 interpreter executableprotect_my_tooling_dir
* - Specify a path to ProtectMyTooling main directoryprotect_my_tooling_config
* - Specify a path to ProtectMyTooling configuration file with packers optionsdotnet_assemblies_directory
* - Specify local path .NET assemblies should be looked for if not found by execute-assemblycache_protected_executables
* - Enable to cache already protected executables and reuse them when neededprotected_executables_cache_dir
* - Specify a path to a directory that should store cached protected executablesdefault_exe_x86_packers_chain
* - Native x86 EXE executables protectors/packers chaindefault_exe_x64_packers_chain
* - Native x64 EXE executables protectors/packers chaindefault_dll_x86_packers_chain
* - Native x86 DLL executables protectors/packers chaindefault_dll_x64_packers_chain
* - Native x64 DLL executables protectors/packers chaindefault_dotnet_packers_chain
* - .NET executables protectors/packers chain
---
Known Issues
is very tricky to run from Windows. What worked for me is following:1. Run on Windows 10 and have WSL installed (bash.exe
 command a in Windows)
  2. Have
golang installed in WSL at 1.16+ (tested on 1.18)
3. Make sure to have PackerScareCrow.Run_ScareCrow_On_Windows_As_WSL = True set---
Credits due & used technology
All packer, obfuscator, con, loader credits goes to their authors. This tool is merely a wrapper around their technology!
- Hopefully none of them mind me adding such wrappers. Should there be concerns - please reach out to me._ProtectMyTooling_ also uses denim.exe by moloch-- by some Nim-based packers.---
TODO
Write custom PE injector and offer it as a "protector"
Add watermarking to other file formats such as Office documents, WSH scripts (VBS, JS, HTA) and containers
Add support for a few other Packers/Loaders/Generators in upcoming future:
- GadgetToJScript
-
-
- ---
Disclaimer
Use of this tool as well as any other projects I'm author of for illegal purposes, unsolicited hacking, cyber-espionage is strictly prohibited.
This and other tools I distribute help professional Penetration Testers, Security Consultants, Security Engineers and other security personnel in improving their customer networks cyber-defence capabilities.
In no event shall the authors or copyright holders be liable for any claim, damages or other liability arising from illegal use of this software.
If there are concerns, copyright issues, threats posed by this software or other inquiries - I am open to collaborate in responsibly addressing them.
The tool exposes handy interface for using mostly open-source or commercially a packers/protectors/obfuscation software, therefore not introducing any immediately new threats to the cyber-security landscape as is.
---
☕ Show Support ☕
This and other projects are outcome of sleepless nights and plenty of hard work. If you like what I do and appreciate that I always give back to the community,
Consider buying me a coffee _(or better a beer)_ just to say thank you! 💪
---
Author
项目信息
开发语言:PowerShell
Star 数:1102
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking, IOCs collection & PE Backdooring. You feed it with your implant, it does a lot of sneaky things and spits out obfuscated executable.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ProtectMyTooling - Multi-Packer wrapper letting us daisy-chain variou |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:36:17 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 353 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |