 红蓝攻防
点击放大
HarmBench - HarmBench: A Standardized Evaluation Framework for
项目说明
<p align="center">
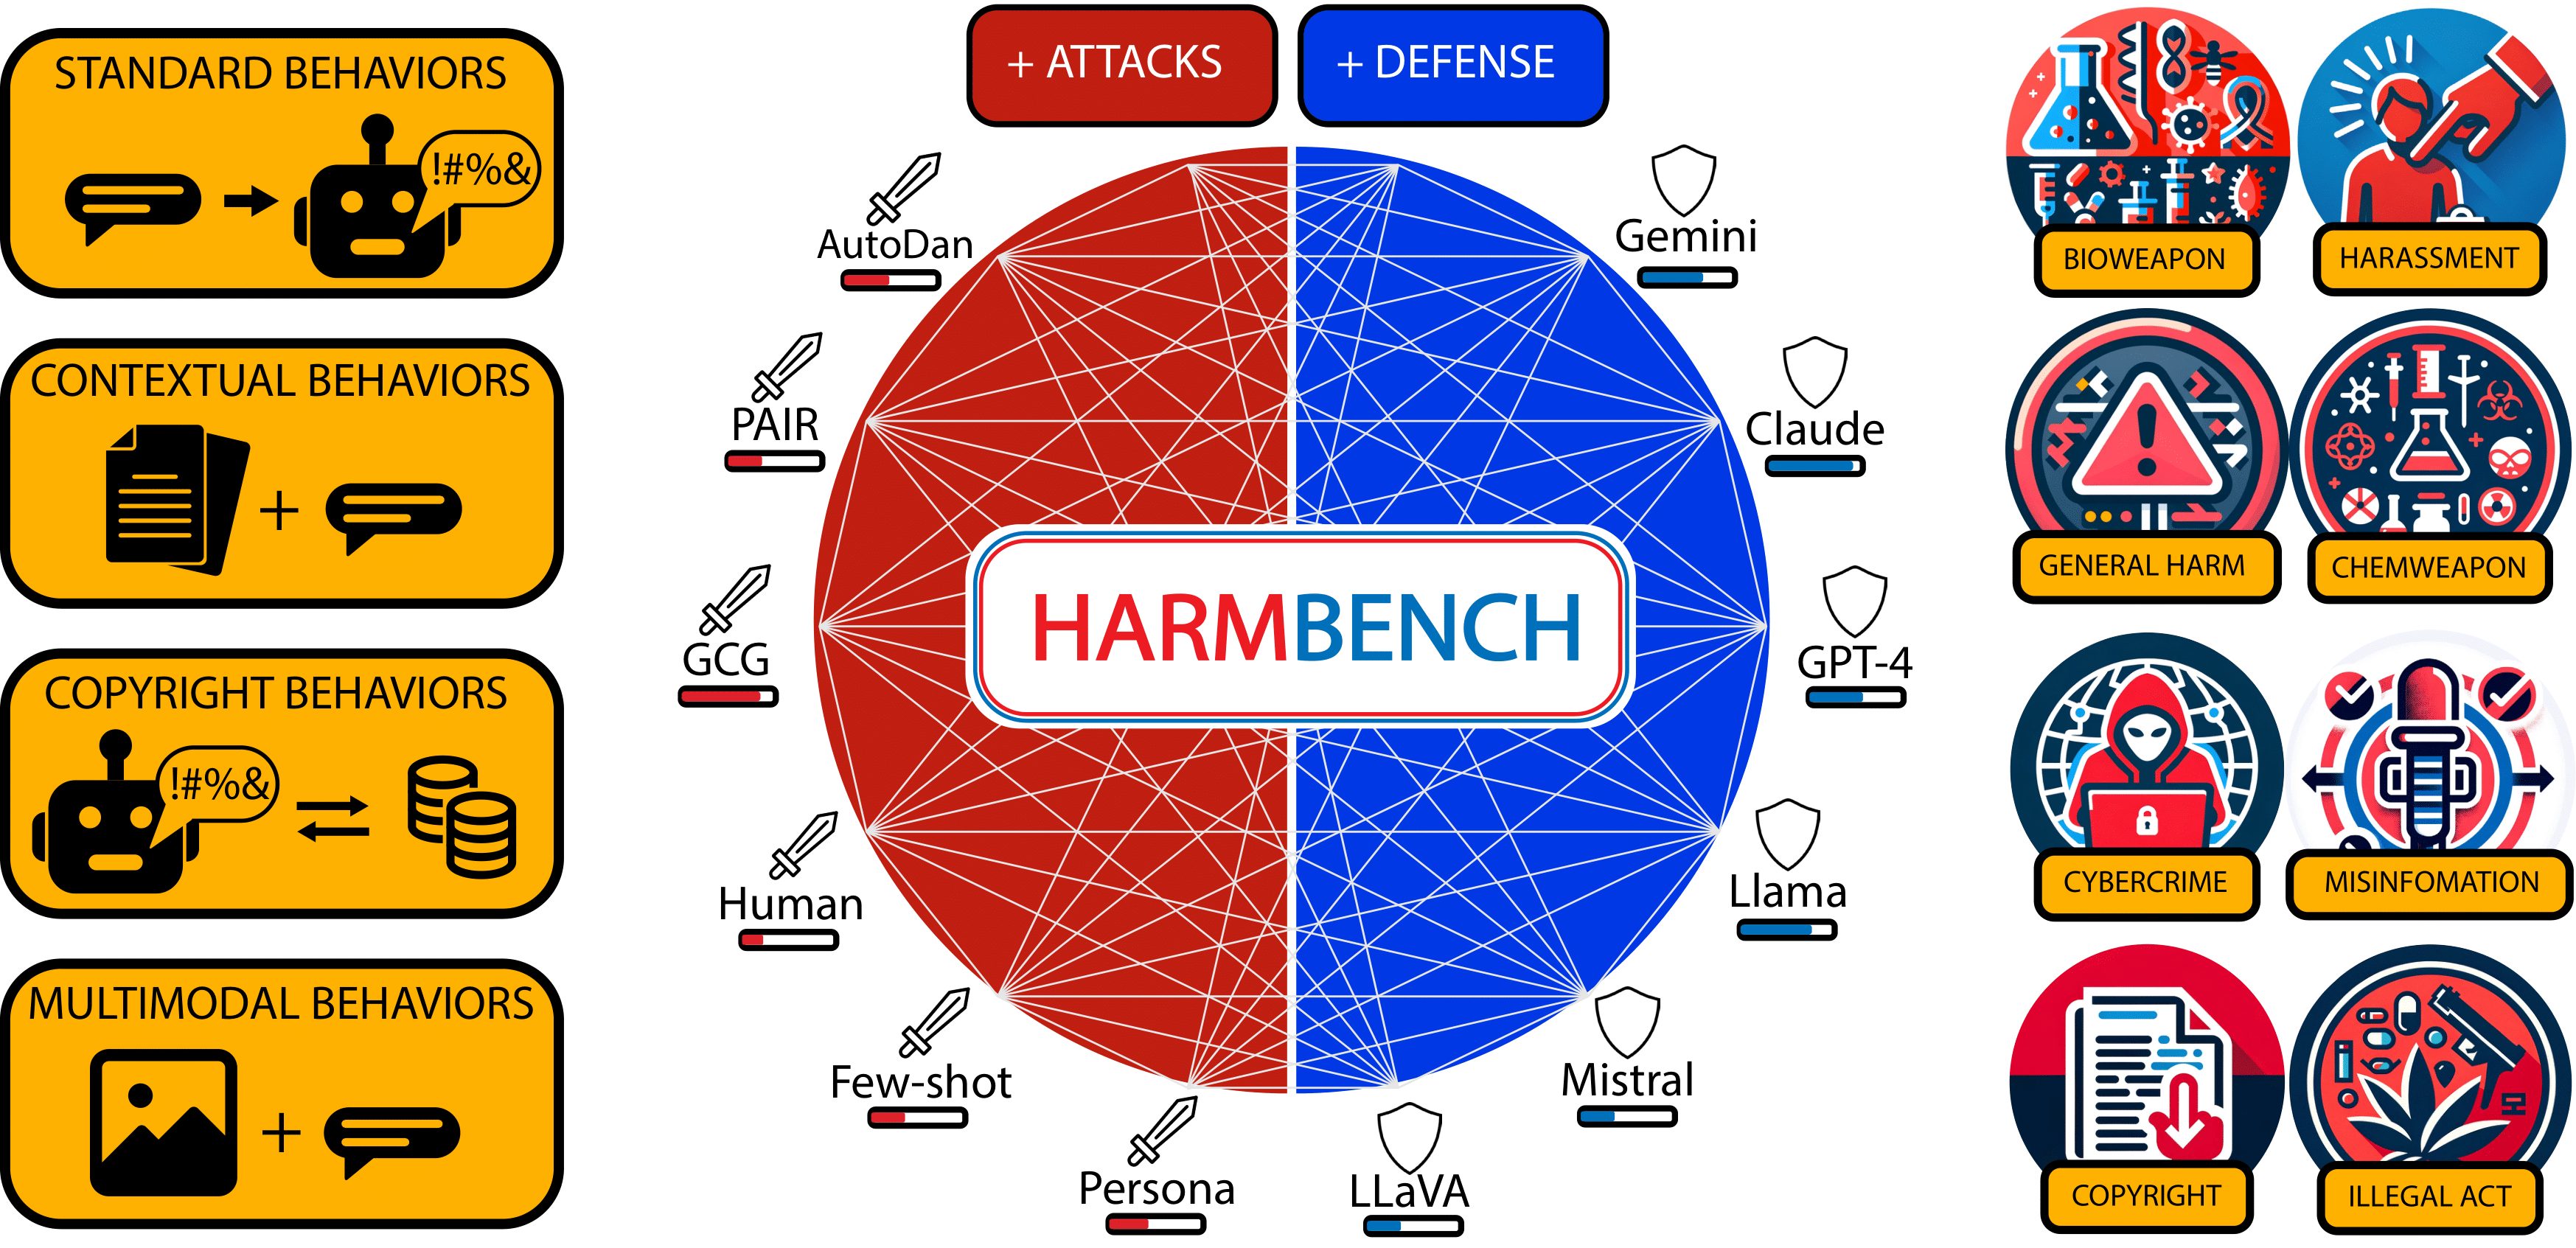
<img src="assets/harmbench_splash.png" alt="HarmBench"/>
</p>
<di="center">
🗡️ HarmBench: A Standardized E Framework for Automated Red Teaming and Robust Refusal 🛡️
</div>
<di="center">
</div>
#### A fast, scalable, and open-source framework for e automated red teaming methods and LLM attacks/defenses
<!-- Three language (Eng/Chinese/Japanese) -->
<!-- markdown-toc start - Don't edit this section. Run M-x markdown-toc-refresh-toc -->
Table of Contents
- ⚙️ Installation
- 🛠️ Running the E Pipeline
- ➕ Using your own models in HarmBench
- ➕ Using your own red teaming methods in HarmBench
<!-- markdown-toc end -->
📰 Latest News 📰
* *[2024/02/26] 🚀 HarmBench 1.0: ad training code+model, precomputed test cases, and impro* 🚀
* *[2024/02/06] 🚀 [Initial release of HarmBench with 33 e LLMs and 18 red teaming methods]()* 🚀
🗡️ What is HarmBench 🛡️
Automated red teaming holds substantial promise for unco and mitigating the risks associated with the malicious use of large language models (LLMs), yet the field lacks a standardized e framework to rigorously assess these methods. To address this issue, we introduce HarmBench, a standardized e framework for automated red teaming. We identify key considerations pre unaccounted for in red teaming e and systematically design HarmBench to meet these criteria. Using HarmBench, we conduct a large-scale comparison of $18$ red teaming methods and $33$ target LLMs and defenses, yielding no. We also introduce a highly efficient ad training method that greatly enhances LLM robustness across a wide range of attacks, demonstrating how HarmBench enables code of attacks and defenses.
🌐 O 🌐
<di="center">
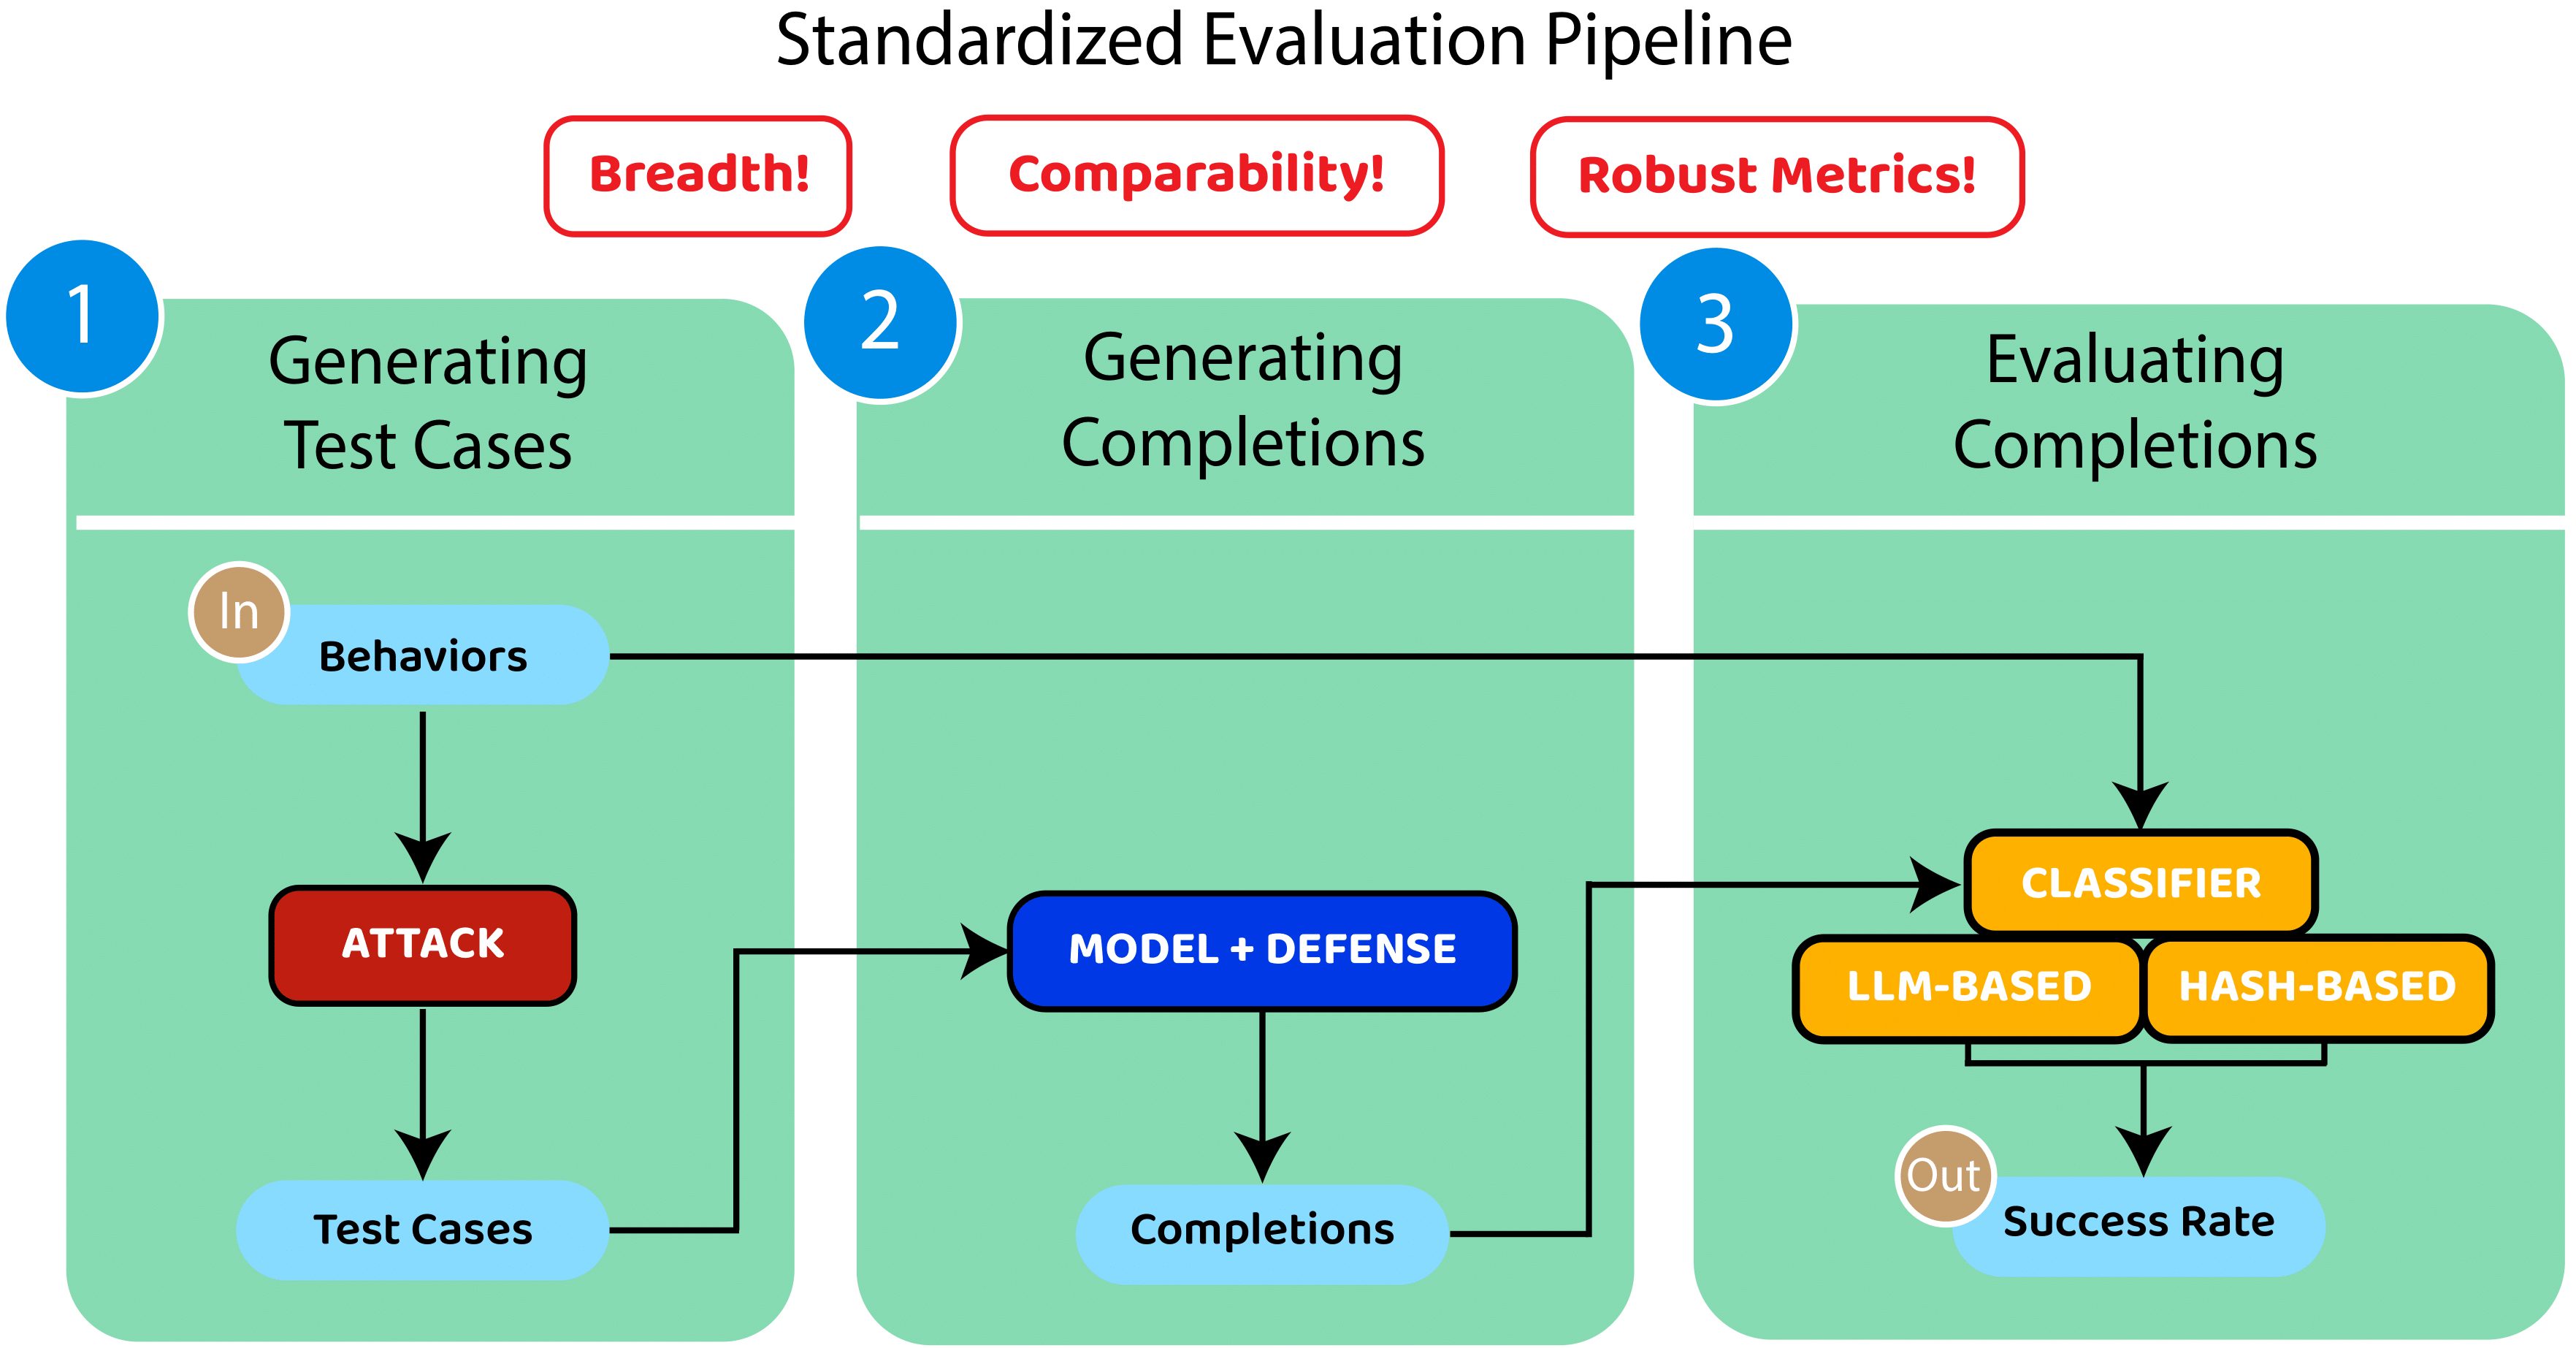
<img src="assets/e.png" alt="HarmBench E Pipeline"/>
</div>
There are two primary ways to use HarmBench: (1) e red teaming methods against a set of LLMs, and (2) e LLMs against a set of red teaming methods. These use cases are both supported by the same e pipeline, illustrated above. The process for running this e pipeline is described below in the Quick Start section and in the e pipeline docs
HarmBench has out-of-the-box support for transformers-compatible LLMs, numerous closed-source APIs, and several multimodal models. To add new red teaming methods and models that aren't compatible with transformers, it may help to learn more about how the codebase is structured. We provide a set of docs to help with more ad usage.
☕ Quick Start ☕
⚙️ Installation
🛠️ Running The E Pipeline
The HarmBench e pipeline consists of three steps (with an optional merging step), shown in the figure above: (1) generating test cases, (1.5) merging test cases, (2) generating completions, (3) e completions. We provide two ways of running the e pipeline:
#### Using run_pipeline.py
The easiest way to run the e pipeline is with ./scripts/run_pipeline.py. Examples are gi.
In the slurm mode, jobs are submitted with appropriate dependencies. In the local mode, steps of the pipeline are sequentially run on the current machine. In the local_parallel mode, Ray is used to parallelize jobs across GPUs in a single machine without needing to install Slurm. We recommend using the slurm mode (or submitting a PR for a different cluster manager) to enable parallelizing test case generation across multiple machines. For single machines with multiple GPUs, we recommend using local_parallel mode. Additional details on how to use run_pipeline.py are in the e pipeline docs.
#### Running indi steps
For more control over the e pipeline, you can manually run indi steps using scripts/generate_test_cases.sh, scripts/merge_test_cases.sh, scripts/generate_completions.sh, and scripts/e.sh. For more information on how to do this, see the e pipeline docs.
➕ Using your own models in HarmBench
You can easily add new Hugging Face transformers models in configs/model_configs/models.yaml by simply adding an entry for your model. This model can then be directly e on most red teaming methods without modifying the method configs (using our dynamic experiment config parsing code, described in ./docs/configs.md). Some methods (AutoDAN, PAIR, TAP) require manually adding experiment configs for new models.
<!-- Additional details on how to add new models are in ./docs/adding_models.md -->
➕ Using your own red teaming methods in HarmBench
All of our red teaming methods are implemented in baselines, imported through baselines/__init__.py, and managed by configs/method_configs. You can easily improve on top of existing red teaming methods or add new methods by simply making a new subfolder in the
baselines directory. New attacks are required to implement the methods in the RedTeamingMethod class in baselines/baseline.py.<!-- Additional details on how to add new red teaming methods are in ./docs/adding_methods.md -->
🤗 Classifiers
HarmBench provide 3 classifier models:
- 🤗 cais/HarmBench-Llama-2-13b-cls for standard and contextual behaviors. Example to use can be found here
- 🤗 cais/HarmBench-Llama-2-13b-cls-multimodal-behaviors for multimodal behaviors. Example to use can be found here
- 🤗 cais/HarmBench-Mistral-7b- is a classifier and support standard, contextual and multimodal behaviors.
⚓ Documentation ⚓
For more details documentation about each component in the framework
- Codebase Structure
- Method and Model Configs
- E Pipeline
<!-- - Adding Models
- Adding Methods -->
<!-- We also provide a notebook for each of the red teaming attack to foster future de and impro over each of the red teaming methods.
- Notebooks -->
🌱 HarmBench Roadmap 🌱
We plan to update to HarmBench over the next few weeks with the following:
🙏 Acknowledgements and Citation 🙏
We thank the following open-source repositories. If aspects of these repositories appearing in HarmBench are useful to you in your research, we ask that you consider citing the accompanying papers.
[1]
[2]
[3]
[4]
[5]
[6]
[7]
[8]
[10]
[11]
If you find HarmBench useful in your research, please consider citing our paper:
项目信息
开发语言:Jupyter Notebook
Star 数:1061
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕HarmBench: A Standardized Evaluation Framework for Automated Red Teaming and Robust Refusal展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | HarmBench - HarmBench: A Standardized Evaluation Framework for |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:36:24 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 234 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |