 红蓝攻防
点击放大
OffensivePipeline - OfensivePipeline allows you to download and build
项目说明
Offensi

Offensi allows you to download and build C# tools, applying certain modifications in order to impro e for Red Team exercises.
A common use of Offensi is to download a tool from a Git repository, randomise certain in the project, build it, obfuscate the resulting binary and generate a shellcode.
Features
What's new in 2.0
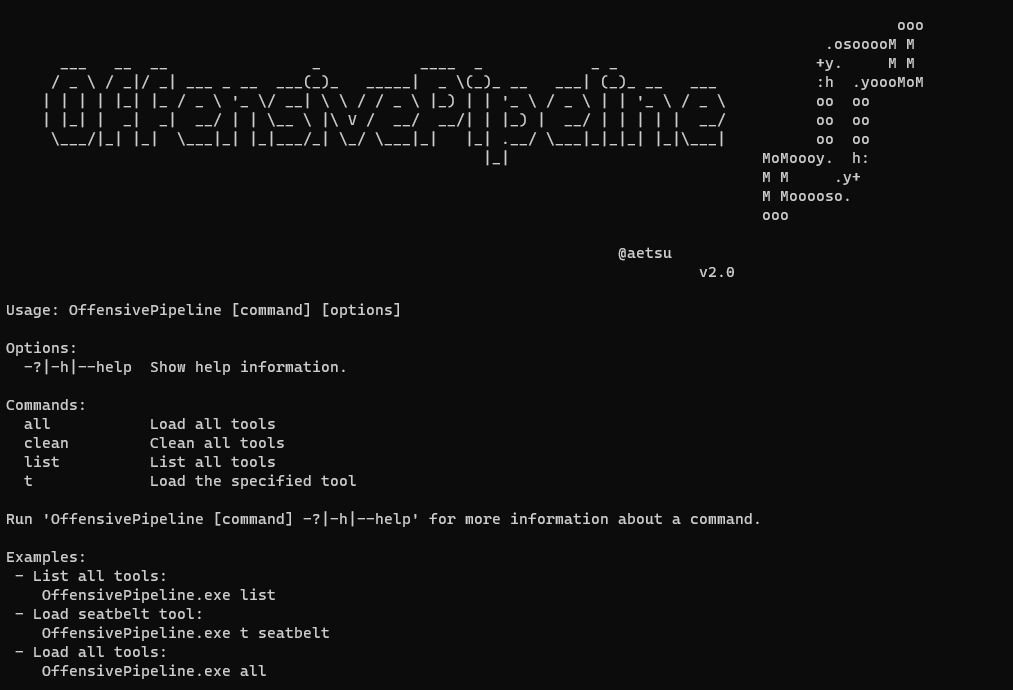
Examples
Output example
Plugins
Add a tool from a remote git
The scripts for downloading the tools are in the Tools folder in *yml* format. New tools can be added by creating new *yml* files with the following format:
Where:
Add a tool from a private git
Where:
Add a tool from local git folder
Where:
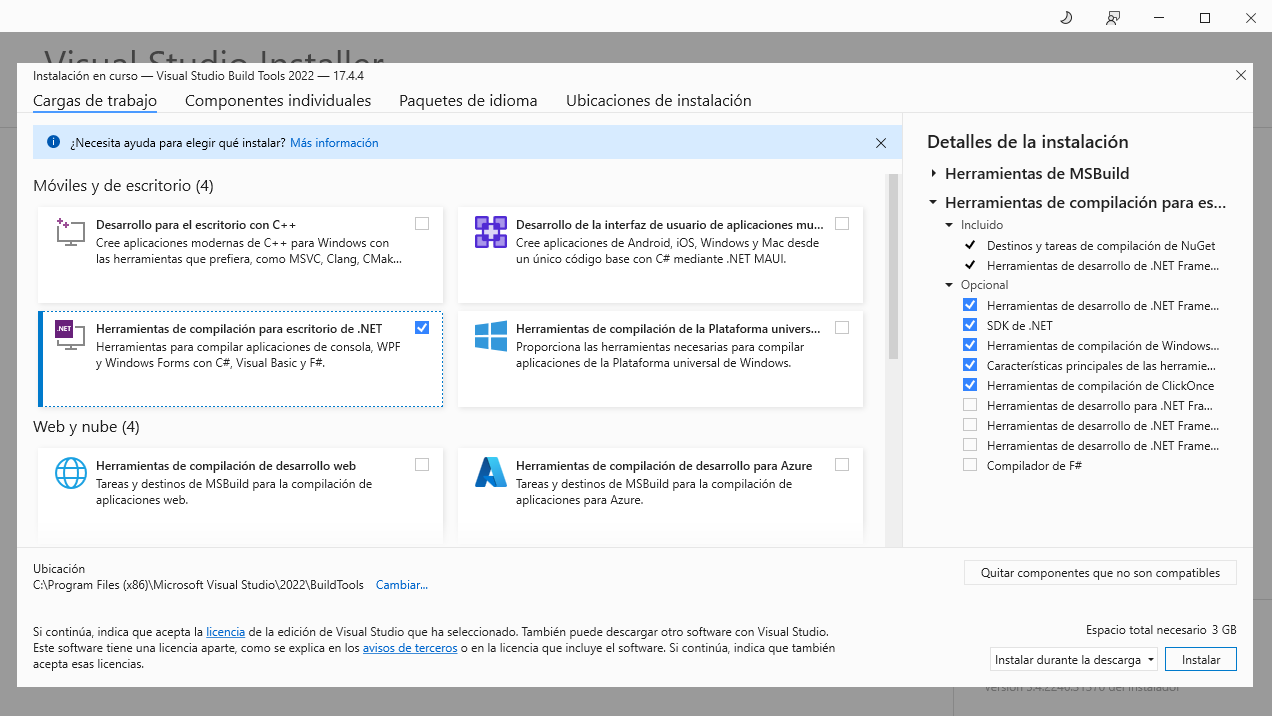
Requirements for the release ( Studio 2019/2022 is not required)
- Install .NET desktop build tools

In the Offensi.dll.config file it's possible to change the of the build tools used.
Requirements for build
- Install .NET desktop build tools
Credits
Supported tools
- Description: ADCollector is a lightweight tool that enumerates the Acti en to identify possible attack .
- Link:
- Description: A tool to escalate pri in an acti network by coercing authenticate from machine accounts (Petitpotam) and relaying to the certificate service.
- Link:
- Description: A C# tool to dump all sorts of goodies from AD FS
- Link:
- Description: A tool written for cobalt-strike's execute-assembly command that allows for more efficent querying of AD.
- Link:
- Description: This modified fork of SafetyKatz dynamically fetches the latest pre-compiled release of Mimikatz directly from the gentilkiwi GitHub repo, runtime patching on detected signatures and uses SharpSploit DInvoke to get it into memory.
- Link:
- Description: Certify is a C# tool to enumerate and abuse misconfigurations in Acti Certificate Services (AD CS).
- Link:
- Description: C# tool for installing a shared network printer abusing the PrinterNightmare bug to allow other network machines easy privesc!
- Link:
- Description: Enumerate Domain Data is designed to be similar to PowerView but in .NET. PowerView is essentially the ultimate domain enumeration tool, and we wanted a .NET implementation that we worked on ourselves. This tool was largely put together by implementations of different functionality across a wide range of existing projects and combining them into EDD.
- Link:
- Description: C# tool to find in AD Group Policy, but do it better than Grouper2 did.
- Link:
- Description: Rubeus is a C# toolset for raw Kerberos interaction and abuses
- Link:
- Description: C# Framework for Kerberos relaying
- Link:
- Description: Simple wrapper around some of the features of Rubeus and KrbRelay
- Link:
- Description: LockLess is a C# tool that allows for the enumeration of open file handles and the copying of locked files.
- Link:
- Description: A small Proof-of-Concept tool that allows authenticating against an LDAP/S server with a certificate to perform different attack actions
- Link:
- Description: PurpleSharp is an open source ad simulation tool written in C# that executes ad techniques within Windows Acti en
- Link:
- Description: Rubeus is a C# toolset for raw Kerberos interaction and abuses
- Link:
- Description: SafetyKatz is a combination of slightly modified of 's Mimikatz project and 's .NET PE Loader.
- Link:
- Description: SauronEye is a search tool built to aid red teams in finding files containing specific keywords.
- Link:
- Description: A C# tool to search through a running instance of Outlook for keywords
- Link:
- Description: Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensi perspectives.
- Link:
- Description: A native C# con of Ke In powershell script
- Link:
- Description: C# port of the Get-AppLockerPolicy PowerShell cmdlet with extended features.
- Link:
- Description: C# tool for UAC bypasses
- Link:
- Description: C# Wrapper of Chisel from
- Link:
- Description: SharpChromium is a .NET 4.0+ CLR project to retrieve data from Google Chrome, Microsoft Edge, and Microsoft Edge Beta. Currently, it can extract
- Link:
- Description: SharpCloud is a simple C# utility for checking for the existence of credential files related to Amazon Web Services, Microsoft Azure, and Google Compute.
- Link:
- Description: SharpCOM is a c# port of In
- Link:
- Description: This is a Sharp port of 's cookie-crimes module - full credit for their awesome work!
- Link:
- Description: Crashes the Windows e service locally or remotely using OpenE/ElfClearE.
- Link:
- Description: SharpDir is a simple code set to search both local and remote file systems for files using the same SMB process as dir.exe, which uses TCP port 445
- Link:
- Description: SharpDPAPI is a C# port of some DPAPI functionality from 's Mimikatz project.
- Link:
- Description: SharpDump is a C# port of PowerSploit's Out-Minidump.ps1 functionality
- Link:
- Description: Checks running processes, process metadata, Dlls loaded into your current process and each DLLs metadata, common install directories, installed services and each service binaries metadata, installed drivers and each drivers metadata, all for the presence of known defensi such as AV's, EDR's and logging tools.
- Link:
- Description: Windows persistence toolkit written in C#
- Link:
- Description: SharpExec is an offensi C# tool designed to aid with lateral mo.
- Link:
- Description: SharpGPOAbuse is a .NET application written in C# that can be used to take ad of a user's edit rights on a Group Policy Object (GPO) in order to compromise the objects that are controlled by that GPO.
- Link:
- Description: This project reuses open handles to lsass to parse or minidump lsass, therefore you don't need to use your own lsass handle to interact with it. (Din)
- Link:
- Description: SharpHose is a C# password spraying tool designed to be fast, safe, and usable o Strike's execute-assembly.
- Link:
- Description: C# Rewrite of the BloodHound Ingestor
- Link:
- Description: Porting of mimikatz sekurlsa::logonpasswords, sekurlsa::ekeys and lsadump::dcsync commands
- Link:
- Description: This executable is made to be executed within Cobalt Strike session using execute-assembly. It will retrieve the LAPS password from the Acti.
- Link:
- Description: Sharpen of CrackMapExec
- Link:
- Description: Create a minidump of the LSASS process from memory (Windows 10 - Windows Server 2016). The entire process uses dynamic API calls, direct syscall and Native API unhooking to evade the AV / EDR detection.
- Link:
- Description: .NET authenticated execution for remote hosts
- Link:
- Description: This project is a C# tool to use Pass-the-Hash for authentication on a local Named Pipe for user Impersonation. You need a local administrator or SEImpersonate rights to use this.
- Link:
- Description: File less command execution for lateral mo.
- Link:
- Description: Printer is a modified and console of ListNetworks
- Link:
- Description: Remote Desktop Protocol Console Application for Authenticated Command Execution
- Link:
- Description: SharpReg is a simple code set to interact with the Remote Registry service API using the same SMB process as reg.exe, which uses TCP port 445
- Link:
- Description: SharpSCCM is a post-exploitation tool designed to le Microsoft Endpoint Configuration Manager (a.k.a. ConfigMgr, formerly SCCM) for lateral mo and credential gathering without requiring access to the SCCM administration console GUI.
- Link:
- Description: Extracts data from the Windows Sticky Notes database. Works on Windows 10 Build 1607 and higher. This
- Link:
- Description: Project to quickly filter through a file share for targeted files for desired information.
- Link:
- Description: .Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
- Link:
- Description: Quick and dirty binary to list network share information from all machines in the current domain and if they're readable.
- Link:
- Description: SharpSniper is a simple tool to find the IP address of these users so that you can target their box.
- Link:
- Description: SharpSphere gives red teamers the ability to easily interact with the guest operating systems of machines managed by
- Link:
- Description: SharpSpray a simple code set to perform a password spraying attack against all users of a domain using LDAP and is compatible with Cobalt Strike.
- Link:
- Description: C# tool to identify and exploit weaknesses with MSSQL instances in Acti en
- Link:
- Description: .NET Persistence
- Link:
- Description: SharpSvc is a simple code set to interact with the SC Manager API using the same DCERPC process as sc.exe, which open with TCP port 135 and is followed by the use of an ephemeral TCP port
- Link:
- Description: SharpTask is a simple code set to interact with the Task Scheduler service API using the same DCERPC process as schtasks.exe, which open with TCP port 135 and is followed by the use of an ephemeral TCP port.
- Link:
- Description: SharpUp is a C# port of PowerUp functionality
- Link:
- Description: .NET port of PowerView
- Link:
- Description: Red Team oriented simple HTTP & WebDA written in C# with functionality to capture Net-NTLM hashes
- Link:
- Description: Retrieves in clear-text the Wi-Fi Passwords from all WLAN Profiles saved on a workstation
- Link:
- Description: SharpWMI is a C# implementation of WMI functionality.
- Link:
- Description: An exploit for C, a.k.a. Zerologon. This tool exploits a cryptographic in Netlogon to achie bypass.
- Link:
- Description: While Sysmon's driver can be renamed at installation, it is always loaded at altitude 385201. The objective of this tool is to challenge the assumption that our defensi are always collecting events.
- Link:
- Description: Snaffler is a tool for pentesters and red teamers to help find delicious candy needles (creds mostly, but it's flexible) in a bunch of horrible boring haystacks (a massi/AD en).
- Link:
- Description: C# .NET mssql client for accessing database data through beacon.
- Link:
- Description: StandIn is a small AD post-compromise toolkit
- Link:
- Description: A collection of nati pri escalation techniques from service accounts to SYSTEM
- Link:
- Description: Modified of Matterpreter's DefenderCheck
- Link:
- Description: C# POC for the token pri removal flaw reported
- Link:
- Description: Iterative AD discovery toolkit for offensi
- Link:
- Description: Watson is a .NET tool designed to enumerate missing KBs and suggest exploits for Pri Escalation .
- Link:
- Description: Whisker is a C# tool for taking o Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute, effectively adding "Shadow Credentials" to the target account.
- Link:
- Description: Pri Escalation Awesome Scripts SUITE
- Link:
- Description: Whisker is a C# tool for taking o Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute.
- Link:
项目信息
开发语言:C#
Star 数:820
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OffensivePipeline - OfensivePipeline allows you to download and build |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:37:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 383 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |