 红蓝攻防
点击放大
aiodnsbrute - Python 3.5+ DNS asynchronous brute force utility
项目说明
Async DNS Brute
A Python 3.5+ tool that uses asyncio to brute force domain names asynchronously.
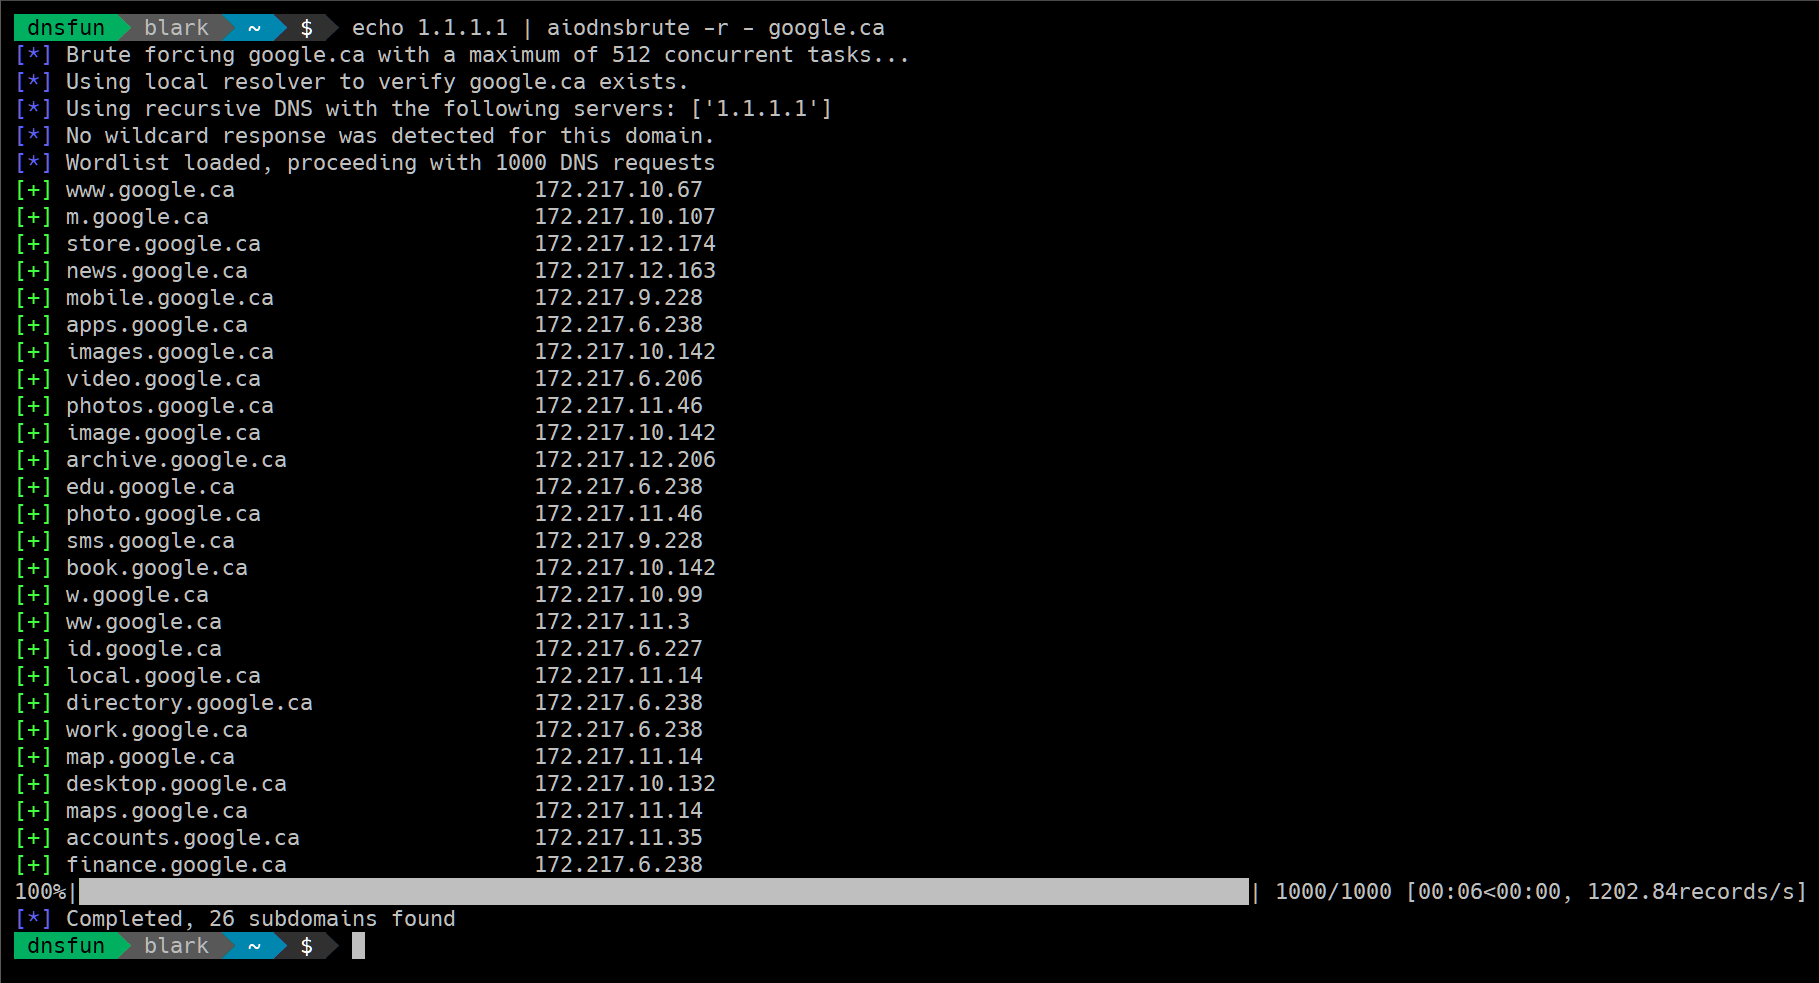
!aiodnsbrute screenshot
Speed
*It's fast.* Benchmarks on small put around 100k DNS resoultions at 1.5-2mins. An amazon M3 box was used to make 1 mil requests in just over 3 minutes. Your mileage may vary. It's probably best to avoid using Google's resolvers if you're purely interested in speed.
DISCLAIMER
Installation
$ pip install aiodnsbrute
Note: using a is highly recommended.
Alternate install
Alternately you can install the usual way:
$ git clone
$ cd aiodnsbrute
$ python setup.py install .
Usage
Get help:
$ aiodnsbrute --help
Usage: cli.py [OPTIONS] DOMAIN
aiodnsbrute is a command line tool for brute forcing domain names
utilizing Python's asyncio module.
credit: blark ()
Options:
-w, --wordlist TEXT Wordlist to use for brute force.
-t, --max-tasks INTEGER Maximum number of tasks to run asynchronosly.
-r, --resol FILENAME A text file containing a list of DNS resolvers
to use, one per line, comments start with #.
Default: use system resolvers
- Increase output
-o, --output [csv|json|off] Output results to DOMAIN.csv/json (extension
automatically appended when not using -f).
-f, --outfile FILENAME Output filename. Use '-f -' to send file
output to stdout o normal output.
--query / --gethostbyname DNS lookup type to use query (default) should
be faster, but won't return CNAME information.
--wildcard / --no-wildcard Wildcard detection, enabled by default
-- / --no- domain name is sane before beginning,
enabled by default
-- Show the and exit.
--help Show this message and exit.
Examples
Run a brute force with some custom options:
$ aiodnsbrute -w wordlist.txt -vv -t 1024 domain.com
Run a brute force, supppess normal output and send only JSON to stdout:
$ aiodnbrute -f - -o json domain.com
...for an ad pattern, use custom resovers and pipe output into the awesome jq:
$ aiodnsbrute -r resolvers.txt -f - -o json google.com | jq '.[] | select(.ip[] | startswith("172."))'
Wildcard detection enabled by default (--no-wildcard turns it off):
$ aiodnsbrute foo.com
[*] Brute forcing foo.com with a maximum of 512 concurrent tasks...
[*] Using recursive DNS with the following servers: ['50.116.53.5', '50.116.58.5', '50.116.61.5']
[!] Wildcard response detected, ignoring answers containing ['23.23.86.44']
[*] Wordlist loaded, proceeding with 1000 DNS requests
[+] www.foo.com 52.73.176.251, 52.4.225.20
100%|██████████████████████████████████████████████████████████████████████████████| 1000/1000 [00:05<00:00, 140.18records/s]
[*] Completed, 1 subdomains found
NEW use gethostbyname (detects CNAMEs which can be handy for potential subdomain takeo)
$ aiodnsbrute --gethostbyname domain.com
Supply a list of resolvers from file (ignoring blank lines and starting with #), specify -r - to read list from stdin.
$ aiodnsbrute -r resolvers.txt domain.com
Thanks
- Creds to Sublist3r for pointing me there.
Notes
ulimit -n to see how many open files are allowed. You can also increase that number using the same command, i.e. ulimit -n <2048>项目信息
开发语言:Python
Star 数:674
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Python 3.5+ DNS asynchronous brute force utility展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | aiodnsbrute - Python 3.5+ DNS asynchronous brute force utility |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:38:30 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 178 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |