 红蓝攻防
点击放大
whonow - A "malicious" DNS server for executing DNS Rebindi
项目说明
Whonow DNS Server
A malicious DNS server for executing DNS Rebinding attacks on the fly. whonow lets you specify DNS responses and rebind rules dynamically *using domain requests themselves*.
What's great about dynamic DNS Rebinding rules is that you don't have to spin up your own malicious DNS server to start exploiting the browser's Same-origin policy. Instead, e can share the same public whonow ser on port 53 of rebind.network.
Note: You should include UUIDs (e.g. a06a5856-1fff-4415-9aa2-823230b05826) as a subdomain in each DNS lookup to a whonow server. These have been omitted from examples in this README for brevity, but assume requests to *.rebind.network should be *.a06a5856-1fff-4415-9aa2-823230b05826.rebind.network. See the Gotchas section for more info as to why.
DISCLAIMER: This software is for educational purposes only. This software should not be used for illegal activity. The author is not responsible for its use. Don't be a dick.
Subdomains = Rebind Rules
The beauty of whonow is that you can define the behavior of DNS responses in the domain name itself. Using only a few simple keywords: A, (n)times, forever, and repeat, you can define complex and powerful DNS behavior.
Anatomy of a whonow request
A: The type of DNS request. Currently only A records are supported, but AAAA should be coming soon.<ip-address>: an ipv4 (ipv6 coming soon) address with each octet seprated by a period (e.g. 192.168.1.1.<rule>: One of three rules-
(n)time[s]: The number of times the DNS ser reply with the previous IP address. Accepts both plural and singular strings (e.g. 1time, 3times, 5000times)-
forever: Respond with the previous IP address forever.-
repeat: Repeat the entire set of rules starting from the beginning.[uuid/random-string]: A random string to keep DNS Rebind attacks against the same IP addresses separate from each other. See Gotchas for more info.example.com: A domain name you ha to a whonow nameserver, like the publicly a rebind.network:53 whonow instance.Rules can be chained together to form complex response behavior.
Examples
Limitations
> Each label [subdomain] may contain zero to 63 characters... The full domain name may not exceed the length of 253 characters in its textual representation. (from the DNS Wikipedia page)
Additionally, there may not be more than 127 labels/subdomains.
Gotchas
Use Unique Domain Names
Each unique domain name request to whonow creates a small state-saving program in the server's RAM. The next time that domain name is requested the program counter increments and the state may be mutated. All unique domain names are their own unique program instances. To avoid clashing with other users or having your domain name program's state inad incremented you should add a UUID subdomain after your rule definitions. That UUID should never be reused.
--max-ram-domains
The program state associated with each unique domain name is stored by whonow in RAM. To avoid running out of RAM an upper-bound is placed on the number of unique domains who's program state can be managed at the same time. By default, this value is set to 10,000,000, but can be configured with the --max-ram-domains. Once this limit is reached, domain names and their sa state will be removed in the order they were added (FIFO).
Running your own whonow server
To run your own whonow server in the cloud use your domain name provider's admin panel to configure a custom nameser to your VPS. Then install whonow on that VPS and make sure it's running on port 53 (the default DNS port) and that port 53 is accessible to the Internet.
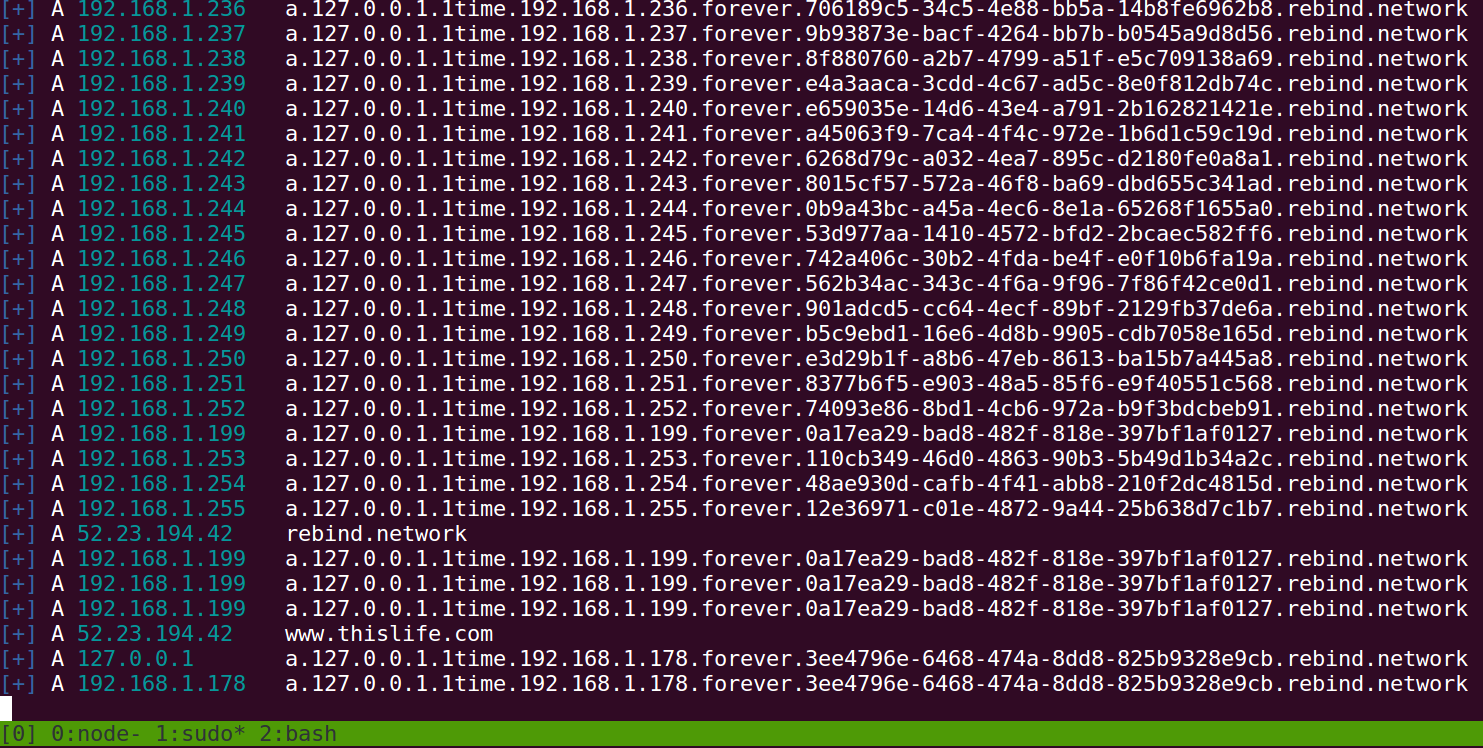
!whonow screenshot
If that ☝ is too much trouble, feel free to just use the public whonow ser on port 53 of rebind.network.🌐.
Usage
Testing
A whonow server must be running on localhost:15353 to perform the tests in test.js
项目信息
开发语言:JavaScript
Star 数:658
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A "malicious" DNS server for executing DNS Rebinding attacks on the fly (public instance running on rebind.network:53)展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | whonow - A "malicious" DNS server for executing DNS Rebindi |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:38:33 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 407 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |