 红蓝攻防
点击放大
ARES - ARES - authorized red-team engagement automation w
项目说明
<di="center">
<img src="frontend/public/brand/ares-logo-v2.png" alt="ARES Logo" width="440">
Operator-Directed Red Team Orchestration & Continuous Security Platform
The open-core platform empowering enterprise red teams, MSSPs, and security operations centers to execute targeted offensi, disco attack paths, and continuously defensi with deterministic scope enforcement and fail-closed isolation controls.
<br>

![Python]()
![FastAPI]()
![React]()


![GitHub Sponsor]()
![Saweria]()
<br><br>
<a href=" target="_blank" rel="noopener noreferrer"><img src=" alt="Mafifrizi%2FARES | Trendshift" style="width: 340px; height: 72px;" width="340" height="72"/></a>
<br><br>
Platform Showcase • Why ARES? • Competiti • Architecture • MITRE Matrix • Quickstart • Sponsorship • Credits • Zero-Trust Security • Documentation
</div>
---
Executi
Traditional penetration testing is fundamentally flawed: it is expensi, point-in-time, and lea blind to newly introduced misconfigurations and emerging ad tradecraft. Meanwhile, automated scanners o SOC teams with thousands of hypothetical C demonstrating exploitability or multi-stage lateral attack paths.
ARES bridges this gap. Built from the ground up for modern enterprise infrastructure, ARES delivers an operator-directed red team engagement platform that models real-world threat actors. By combining deterministic application-layer ScopeGuard fail-closed enforcement, adapti noise profiling, an interacti acyclic graph (DAG) attack solver, and 66 acti execution modules (70 total catalogued) co 60+ mapped ad techniques across MITRE ATT&CK, ARES allows security teams to pro exploitability, locate shortest compromise paths to Acti Crown Jewels, and generate executi deli with zero operational downtime.
---
Why Enterprises Choose ARES
Core Value Pillars
1. Zero-Collateral Scope Go (Dual-Layer Scope Firewall): Every campaign executes inside a hardened, isolated boundary. ARES pairs deterministic application-layer ScopeGuard pre-checks with a dual-layer Scope Firewall & Egress Filter that integrates OS-le filtering (Windows Defender Firewall / Linux Netfilter when elevated) with transport-le interception (socket.connect, socket.sendto, asyncio.create_connection) in Python user space. Guarantees fail-closed enforcement so zero offensi reach unapproved IP addresses or subnets.
2. Goal-Directed Attack Planning: Operators set high-le (e.g. domain_admin, full_compromise, cloud_audit), and the ARES decision engine synthesizes multi-stage execution paths using graph heuristics and optional LLM agents (Claude / OpenAI / local Ollama) under explicit operator authorization.
3. Multi- Attack Graph (DAG): Ingest BloodHound collections or map acti sessions in real time. The built-in graph engine calculates shortest attack paths, highlights chokepoints, and simulates lateral pi.
4. Defense-in-Depth Security Model: Engineered for zero-trust en. Database-authoritati, memory-only short-lived JWT access tokens, HttpOnly rotating refresh credentials, and AES-256-GCM AEAD encrypted local (PBKDF2-HMAC-SHA256 600k iterations) protect har hashes and sensiti e.
5. Automated Deli Pipeline: One-click generation of branded, audit-ready compliance deli in PDF, HTML, Markdown, and JSON formats. Features automated headless browser PDF rendering on Windows/Linux without external GTK dependencies.
---
Market Comparison Matrix
| Operational Capability | Traditional Manual Pentest | Legacy Scanners | ARES Orchestration Platform |
| :--- | :---: | :---: | :---: |
| Testing Frequency | Annual / Semi-Annual | Scheduled Daily / Weekly | Continuous / On-Demand |
| Exploitability | Manual & Labor Intensive | Theoretical C (No ) | Deterministic Multi-Stage Proof |
| Multi-Hop Attack Paths | Manual Drawing | None | Real-Time Interactive DAG |
| Scope Enclave & Egress Guard | Operator Discipline Only | Network Firewalls Only | Fail-Closed Dual-Layer ScopeGuard & OS/Transport Firewall |
| Acti Lateral Paths | Slow Script Execution | No Acti | Nati, Kerberos Suite & Linux AD RFC Track |
| Credential Security & Storage | Loose Flat Files / Cleartext | Logs | AES-256-GCM Authenticated Vault |
| OPSEC & Telemetry Throttling | Manual Jitter Scripts | High Network Noise | Adapti Profiles & Go |
| Delivery Time for Reports | 1-2 Weeks Post-Engagement | Raw Data Dumps | Instant Multi-Format Artifacts |
| Deployment Footprint | External Consultants | Bulky Cloud Agents | Air-Gapped Local / Self-Hosted |
---
Platform Showcase & Control Surfaces
The ARES Platform features a high-performance, responsi dashboard engineered with dark-tech aesthetics, low cognitive load, and audited operational control.
---
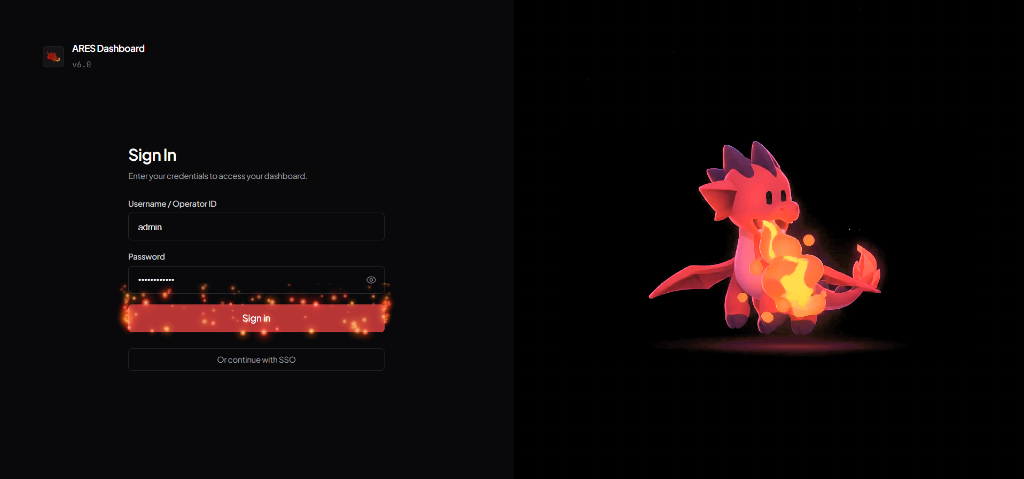
1. Operator Enclave & Zero-Trust Gateway
*Access barrier designed specifically for authorized offensi and security personnel.*
<di="center">
!ARES Operator Enclave & Zero-Trust Authentication Gateway
*ARES Operator Enclave - Sign In button erupts with crimson plasma fire on hover, click, and Enter key. Minimalist Ri showcase featuring the animated ARES Ruby Dragon mascot on the right panel.*
</div>
- Crimson Fire Signature Interaction: Real-time HTML5 Can fire system en the Sign In button on hover (continuous), click (burst), and Enter key (burst without pointer) - physics-based particles with buoyancy, turbulence, and radial glow using
requestAnimationFrame.- ARES Ruby Dragon Living Mascot: Integrated brand mascot showcase with calibrated ruby red palette, fire-breathing animation, and clean dark backdrop.
- Live Dynamic Architectural Grid Canvas: Low-o hardware-accelerated 60 FPS HTML5 canvas with real-time tra data pulses and cursor proximity illumination.
- Memory-Only Token Isolation: Short-lived JWTs reside strictly in memory; refresh credentials use host-only, HttpOnly cookies with one-time rotation.
- Enterprise Multi-Tenant SSO (SAML 2.0 & OIDC): SP-initiated federated authentication with Okta, Azure AD, and Google Workspace. Features App-le credential encryption, one-time replay protection (
InResponseTo/nonce), JIT role mapping, and strict local password lockout for federated identities. (See SSO Setup Guide).- HMAC Double-Submit CSRF Protection: Constant-time on all state-mutating requests (
X-ARES-CSRF).- Cryptographic Brute-Force Shield: Enforces exponential backoff and IP-based rate limiting on authentication attempts.
---
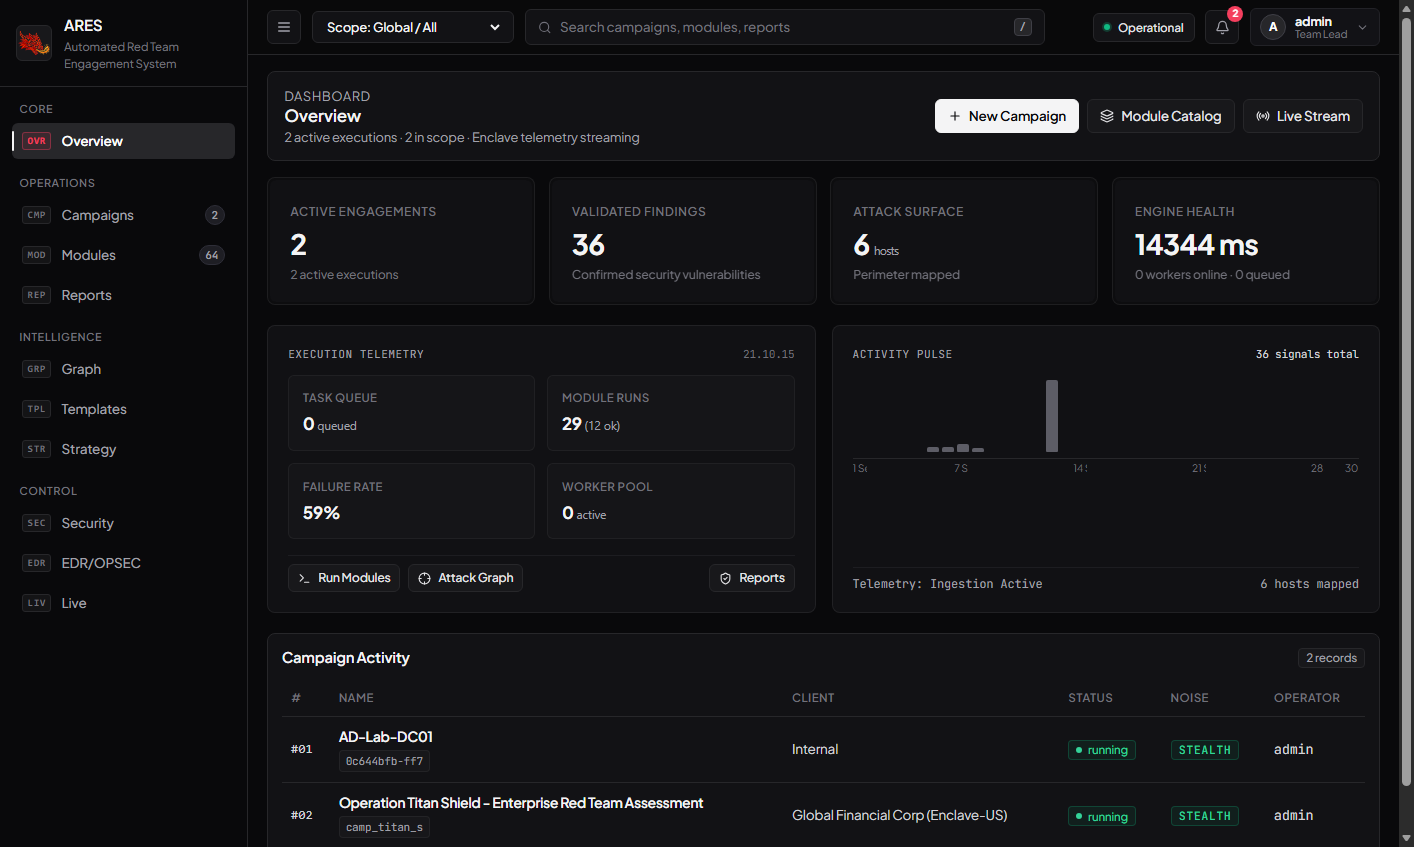
2. Executi Center & Telemetry
*Real-time operational command console pro instant posture across acti.*
<di="center">
!ARES Executi Center & Telemetry
*Executi Center displaying real-time telemetry, findings, attack surface metrics, and activity pulse.*
</div>
- Executi HUD: Clean 4-card operational matrix featuring
Acti, Findings, Attack Surface, and Engine Health (P95 latency, worker pool, and queue depth). Engineered with crisp typography (Plus Jakarta Sans & JetBrains Mono), eliminating redundant counts and distracting indicator dots.- Balanced Execution Workstation (50/50 Split):
- *Execution Telemetry*: Real-time operational health tracking Task Queue depth, Module Runs with success/failure breakdown, Failure Rate, Worker Pool health, and instant action links to Modules, Attack Graph, and Reports.
- *Activity Pulse*: 14-day security signal distribution sparkline with li stream status.
- Campaign In Matrix: Single source of truth for all scoped engagements with click-to-filter reactivity, status badges, noise controls, and operator identity.
- Streamlined Topbar Heartbeat: Minimalist li status indicator (
Operational / Offline) with on-demand subsystem health inspection from any view.- Tactical Fresh-Install Hero: Automatic empty-state fallback with a centered initialization CTA and minimal readiness strip when starting with zero campaigns.
---
3. Scoped Campaign & Target Boundary Management
*Zero-collateral target go enforcing hard CIDR whitelist boundaries, dual-layer Scope Firewall egress interception, and encrypted e isolation.*
<di="center">
!ARES Scoped Campaign & Target Boundary Management
*Campaign Management interface showing target scopes, CIDR boundaries, noise controls, and encrypted credential vault.*
</div>
- Dual-Layer Scope Firewall & Egress Filter: Combines nati packet filtering (
OSFirewallController Defender Firewall / Linux Netfilter when elevated) with transport-le interception (socket.connect, socket.sendto, asyncio.create_connection) enforcing strict fail-closed CIDR boundaries. Features async ContextVar task isolation (zero bleed to database pools or web dashboard handlers), anti-re-entrancy DNS protection, loopback/Windows Proactor pipe safeguards, cloud provider allowlists, and recursi scanning.- Hard CIDR Whitelists: Network-le enforcement. The engine intercepts and drops any request targeting unapproved IP addresses or subnets.
- Recon & Port Scan Scope Enforcement: Reconnaissance and discovery modules are strictly bound to authorized campaign scope, closing out-of-scope port scanning loopholes.
- Persistent Operator Guidance: Persistent
<label> definitions across all campaign pickers and parameter inputs, pre operator ambiguity during rapid engagements.- Noise Profiles & Jitter: Configure engagement throttle levels (
Stealth, Normal, Aggressive) with randomized delay distributions.- AES-256-GCM Authenticated Encla: Har NTLM hashes, Kerberos tickets, and service credentials are encrypted at rest using AES-256-GCM authenticated encryption (AEAD with PBKDF2-HMAC-SHA256 600k iterations and per-record random salt/nonce) and masked in all structlog streams.
- Clean Teardown Workflows: Single-click campaign deletion that securely cleans up all associated database rows, graph , and temporary artifacts.
---
4. Modular Ad Orchestration (66 Acti, 60+ Techniques)
*Extensi of weaponized ad techniques aligned with the MITRE ATT&CK enterprise matrix.*
<di="center">
!ARES Modular Ad Orchestration
*Module Catalog with MITRE ATT&CK categorization, dynamic parameter generation, and dry-run safety modes.*
</div>
- Comprehensi Co: 66 acti execution modules (70 total catalogued) co 60+ mapped ad techniques across Acti (
ad.kerberoast, ad.adcs, ad.enum_users), Windows (windows.uac_bypass, windows.lsass_dump), Linux, Cloud (AWS, Azure, GCP), and Network infrastructure.- Streamlined Execution Panel: Clean execution view with persistent field labels, demoted low-weight dependency hints, and focused on-submit replacing intrusi warning cards.
- Dynamic Typed Schemas: UI forms are generated dynamically from Python Pydantic models with strict .
- Dry-Run Safety Engine: target responsi, parameters, and expected outcome before transmitting offensi.
- Role-Gated Execution: Operator and Team Lead permissions required for execution; sensiti modules require explicit confirmation.
---
5. Multi- Pi & ARES Beacon Terminal Console
*Interacti lateral pi graph with perimeter firewall flame effects, slide-o Inspector Drawer, and a real-time docked Beacon session terminal console.*
<di="center">
!ARES Multi- Pi & Interacti Terminal Console
*ARES Tactical Pi & Interacti Terminal Console - Li campaign topology (Kali test), perimeter ingress firewall with animated flames, Linux/Windows compromised footholds, slide-o Inspector Drawer, and real-time interacti terminal.*
</div>
- Hierarchical Enterprise Pi: Strict left-to-right ad tra topology showing perimeter ingress firewall (
PERIMETER INGRESS 0.0.0.0/0), initial foothold workstations and services, internal servers, and high-value Acti Domain Controllers (DC01).- Perimeter Ingress Firewall with Animated Flames: Dedicated perimeter boundary node featuring an ambient breathing aura and multi-layered CSS animated flame particle effects above a classic red brick firewall icon, designating the external ingress boundary.
- Slide-O Inspector Drawer: Instant deep-dive host and lateral tra intelligence panel:
- Li & OS State: Real-time status indicators (
COMPROMISED (ACTIVE) vs RECON TARGET), OS detection, and perimeter access ports (e.g. 22/TCP).- Confirmed & Findings: Full-fidelity finding titles without premature truncation, MITRE ATT&CK technique badges (e.g.
T1548.001, T1552.001), and pattern summaries.- Intelligent Finding Deduplication: Redundant finding records on the same target are automatically grouped with instance multipliers (
×4, ×3) to preserve a clean, high-signal view.- Unified Dark Scrollbar: Single sleek custom scrollbar matching the dark theme, eliminating nested OS scrollbars.
- Authentic Pri Semantics: Dynamic glowing border indicators reflecting actual compromise tiers - Crimson
SYSTEM * for Tier-0 Domain Controllers and root access, Amber ADMIN for internal servers, Cyan BEACON for compromised user workstations, and Red Brick Firewall nodes for perimeter ingress.- Organic Cubic Bezier Routing & Telemetry Stream: Fluid curves with directional arrowheads and animated glowing particle pulses li and pi.
- Persistent Click-to-Lock Pathway Tracking: Click any node to instantly freeze its upstream compromise lineage and downstream lateral reachability, complete with a tactical HUD banner (
• PATHWAY LOCKED: [HOST] | N NODES | N HOPS). Freely zoom and pan across complex topologies without losing situational focus.- Docked Multi-Row Beacon Terminal Console (
CobaltSessionDock):- Dual-Row Ja Session Tabs: Automatic focus and session switching when clicking nodes on the canvas.
- Real-Time Status Bar: Pri context (
[HOST] root or [DC01] SYSTEM *) and heartbeat interval (last: 2s).- Interacti Prompt (
beacon>):-
whoami: Resol level and active user context (TARGET\SYSTEM * or root).-
hashdump / creds: Harvests and displays cached NTLM SAM/LSA hashes.-
ps / process: Enumerates acti trees and resol PIDs.-
ppid <pid>: Tasks beacon to spoof parent process IDs for EDR e.-
ssh <host> <user> <pass>: Tasks interacti SSH tra.-
net view / hosts / recon: Lists discovered network scope and adjacent nodes.-
clear: Clears current session terminal scrollback buffer.-
help: Quick reference of supported beacon tasking commands.- Operational Modes:
-
Mode: LI: Renders li engagement targets and findings discovered during reconnaissance. Use the [Acti Only] filter to focus exclusively on confirmed lateral compromise routes.-
Mode: DEMO SAMPLE: Instant reference 9-node interconnected lateral pi demonstrating enterprise multi-hop infiltration chains.---
6. Automated Report Engine & E Library
*Instant deli generation producing branded, audit-ready compliance reports across multiple enterprise formats (Executive PDF, Technical Markdown, Defect CSV).*
<di="center">
!ARES Automated Report Engine & E Library
*Report Engine and Artifact Library supporting multi-format exports with synchronized real-time lifecycle management.*
</div>
- Structured Generation Grid: Aligned multi-column layout with persistent
<label> elements (Target Campaign, Export Format) and clean inline error feedback.- Multi-Format Export: One-click generation of PDF, HTML, Markdown, and JSON deli.
- Automated Headless PDF Engine: Integrated fallback using Microsoft Edge / Chromium headless mode for clean PDF export without complex GTK dependencies on Windows.
- Automated E Redaction: Automatically redacts sensitive raw passwords and private keys in customer deli while retaining audit proofs.
- Synchronized Report Library: Authenticated artifact repository with instant downloads, per-report deletion, and real-time UI state synchronization.
---
7. Goal-Directed Strategy & Attack Planner
*Goal-directed engine that plans, prioritizes, and stages complex attack chains with operator o while respecting OPSEC limits.*
<di="center">
!ARES Goal-Directed Strategy & Attack Planner
*Strategy Console for goal-based campaign planning and adapti go.*
</div>
- Dynamic Engine : Real-time asynchronous healthchecks against local Ollama daemons (
GET /api/tags) with sub-second timeouts and TTL caching, paired with dynamic ser cloud key (Claude, OpenAI).- Clean Operator-Centric Design: Persistent field labels (
Target Campaign, Strategic Objective, AI Planning Engine, Explicit Authorizations), human-readable goal descriptions, and complete elimination of ser leakage in UI labels.- Focused On-Submit : Warning boxes removed from default page render; errors display inline beneath target fields only upon execution attempt.
- Adapti Go: Continuously e defensi and noise thresholds, automatically slowing down or aborting aggressi when detection risk peaks.
---
8. Multi-Stage Ad Execution Chains
*Deterministic, multi-step kill chains orchestrating reconnaissance, credential har, and lateral mo in sequence.*
<di="center">
!ARES Multi-Stage Ad Execution Chains
*Automated execution chains including AD Kerberos Exposure Chain and AD Domain Enumeration Chain.*
</div>
- Pre-Built Attack Sequences: Out-of-the-box chains for Kerberos exposure (
asreproast -> kerberoast -> hashcat), domain enumeration, and cloud pri escalation.- Dynamic Context Passing: Credentials and hashes har in step 1 are automatically populated into target arguments for subsequent steps.
- Integrated OPSEC Budgeting: Tracks cumulati and detection likelihood across the entire chain before initiating execution.
---
9. EDR / OPSEC E & Bypass Knowledge Base
*Empirical tracking of e efficacy across enterprise endpoint detection and response (EDR) platforms.*
<di="center">
!ARES EDR and OPSEC E Matrix
*Bypass Knowledge Base tracking technique success rates across CrowdStrike Falcon, SentinelOne, and Microsoft Defender.*
</div>
- Empirical Success Rates: Historical success rates categorized by specific e techniques (AMSI patching, syscall unhooking, process hollowing) and EDR .
- Cross-Session E Memory: Engagement outcomes update a unified knowledge base, warning operators before they execute techniques with low success probabilities.
- Defensi Controls: Granular delay distributions and packet spacing to evade beha heuristics and SIEM correlation rules.
---
10. Zero-Trust Security Go & Audit Trail
*Audited multi-role access control, cryptographic API key lifecycle, and continuous platform integrity .*
<di="center">
!ARES Zero-Trust Security Go
*Operator profile management, scoped API key pro, and automated system security audits.*
</div>
- Role-Based Access Control (RBAC): Strictly enforced permission tiers (
Team Lead, Operator, Recon, Reporter) go module execution and e .- Scoped API Keys: Cryptographically generated bearer tokens with configurable expiration and fine-grained permissions for CI/CD integration.
- Li Trail: Continuous append-only logging of every operator action, target scan, and credential retrieval for post-engagement review.
---
11. Li & Real-Time Event Stream
*High-frequency WebSocket event bus streaming operational telemetry, module output, and pipeline status.*
<di="center">
!ARES Li Stream
*Li event console with buffered telemetry and high-throughput WebSocket streaming.*
</div>
- Sub-Second Event Delivery: Asynchronous WebSocket bus streaming li/stderr, module completion events, and defensi.
- Buffered Log Telemetry: Reconnection-resilient event buffering ensuring zero lost log lines during network fluctuations.
- Multi-Operator Collaboration: Simultaneous operators see shared campaign execution events in real time.
---
12. Enterprise Playbooks & Campaign Templates
*Standardized engagement architectures for recurring red team exercises, compliance audits, and purple team drills.*
<di="center">
!ARES Enterprise Campaign Templates
*Built-in engagement templates including Internal Pentest, AD Full Compromise, Cloud Assessment, and Assumed Breach.*
</div>
- Turnkey Playbooks: Ready-to-deploy campaign templates with pre-configured target profiles, module sets, and report requirements.
- Custom Template Authoring: Export successful custom engagements as reusable templates for internal teams and MSSP clients.
- Safety Pre-Flights: Automated scope and permission before any template-based campaign goes live.
---
13. Interacti 3.1 & De Integration
*Fully documented, interactive REST API surface for custom tooling, SOC orchestration, and CI/CD pipeline integration.*
<di="center">
!ARES Interacti Documentation
*Interacti UI documentation exposing 70+ operational endpoints for enterprise automation.*
</div>
- 70+ Documented Endpoints: Complete REST co across authentication, campaigns, module execution, attack graphs, and deli.
- OpenAPI 3.1 Conformance: Strictly request/response schemas generated directly from Python Pydantic models.
- Interacti: In-browser API testing with Bearer token authentication and CSRF token support.
---
Control Surfaces Breakdown
| Surface | Core Responsibility | A Sub-Tabs | Primary Operators |
| :--- | :--- | :--- | :--- |
| O | Executi, telemetry counters, finding se metrics. | Single Pane | All Stakeholders |
| Campaigns | Scope whitelisting, noise profiles, encrypted credential vault. | List, Scope, Findings | Team Lead, Operator |
| Modules | 66 acti catalog (70 total, 60+ techniques), parameter input forms, execution console. | Catalog, Run Panel, Results | Operator |
| Reports | Deli builder, e packages, Report Library lifecycle. | Generate, Library | Operator, Reporter |
| Graph | Cobalt Strike pi, lateral mo tracking, Beacon session dock. | Li, Demo Sample, Beacon Console | Operator, Recon |
| Templates | Repeatable engagement playbooks and multi-stage workflow plans. | Templates, Plan Builder | Team Lead, Operator |
| Strategy | Goal-directed attack engine, automated planner integration. | Objective, Active, Result | Team Lead, Operator |
| Security | Operator credentials, API key lifecycle, dependency audit checks. | Account, API Keys, Audit | Team Lead |
| EDR/OPSEC | Defensi, bypass tracking, detection e rules. | Knowledge Base, Report Outcome | Operator |
| Live | Real-time WebSocket event streams and buffered telemetry logs. | Stream, Buffer | Operator |
---
System Architecture & Data Pipeline
ARES follows a strict defense-in-depth architecture separating presentation, execution orchestration, security go, and persistent cryptographic storage:
---
Ad Techniques & MITRE ATT&CK Matrix
ARES implements 66 acti execution modules (70 total catalogued) mapping to 60+ ad techniques across the MITRE ATT&CK Enterprise Framework:
ad.kerberoast), AS-REP Roasting, ADCS Certificate Template abuse and enrollment checks (ad.adcs; ad.ghost_forge retained as disabled audit stub), DCSync account replication, and BloodHound data generation.linux.sssd_harvest), pure-Python Kerberos ccache ticket hunting (linux.ccache_hunt), keytab parsing & Sil generation (linux.keytab_abuse), Samba machine secrets extraction (linux.samba_secrets), and bidirectional ccache <-> kirbi ticket transcoding (credential.ticket_con).cloud.phantom_token retained as disabled audit stub).---
Quickstart: Up and Running in 60 Seconds
Prerequisites
Fast Path (PowerShell on Windows)
Open your browser to .
adminARES_DEFAULT_ADMIN_PASSWORD in .env (mandatory; minimum 12 characters; no hardcoded default).& Testing Architecture
ARES maintains a comprehensive test suite of 5,074 automated tests co core orchestration, cryptography, scope firewalls, Acti tradecraft, API security policies, and PostgreSQL database migrations:
Executing all 5,074 unit, integration, and simulation tests sequentially on a single thread requires approximately 45–65 minutes. Automated testing harnesses or CI pipelines should enforce partitioned or parallel execution (
tests/unit) rather than imposing short timeouts on the monolithic suite.Seamless Platform Updates & In-Place Upgrades (ares update & ares upgrade)
ARES includes a built-in Nuclei-style update engine. Operators do not need to git clone or manually recompile the frontend when new capabilities or impro are released:
> [!NOTE]
> Zero Data Loss Guarantee: User databases (~/.ares/ares.db or PostgreSQL), credentials, configuration files (config.yaml), audit reports, and custom user plugins (~/.ares/plugins/) are mathematically blacklisted from modification. Pre-flight Python AST and atomic file writes ensure zero risk of corruption.
---
Enterprise Security Model & Compliance
ARES was designed for en with the most stringent compliance and confidentiality requirements:
Defense-in-Depth Authentication
localStorage or sessionStorage.ares_refresh) with one-time rotation and automatic reuse re.X-ARES-CSRF headers matched against cryptographically secure cookie tokens.Role-Based Access Control (RBAC)
ARES enforces strict RBAC permissions across all API endpoints, background jobs, and UI surfaces:
| Role | API Value | Operational Scope | Administrati |
| :--- | :---: | :--- | :--- |
| Team Lead | team_lead | Complete platform authority: campaign creation/deletion, user pro, security audits, high-noise module o. | Full System Admin |
| Operator | operator | Day-to-day operations: execute authorized modules, review findings, explore attack graph, generate reports. Cannot register users. | Operational Tier |
| Recon | recon | Read-hea: execute safe discovery and network fingerprinting modules. Execution of disrupti is blocked. | Read-Heavy |
| Reporter | reporter | Stakeholder review: read-only access to campaign analytics, findings, attack graphs, and generated deli. No execution rights. | Read-Only Audit |
#### Role Pro & Anti-Pri Escalation Guarantees
row = await db.resoll(...)). Tampered JWT claims are mathematically discarded.team_lead via POST /auth/register (guarded by require_team_lead()) or automatically mapped from enterprise Identity Pro during SP-initiated SAML/OIDC SSO.PUT /users/{id} does not exist), eliminating horizontal and pri escalation (e.g., recon escalating to team_lead or reporter running offensi).Security console provides a transparent in of all registered identities and acti for engagement accountability.---
ARES MCP Gateway & Product-Grade CLI
ARES provides a production-grade Model Context Protocol (MCP) Gateway that enables modern AI coding assistants (Cursor IDE, Claude Desktop, Windsurf, VS Code Cline, Zed, Open-WebUI, LibreChat) to interact with the ARES purple-team offensi safely and under strict go.
<di="center">
!ARES MCP Two-Pane Terminal Monitor
*ARES MCP Two-Pane Split Terminal Monitor (OpenClaw style) with real-time tool telemetry, li inspection, and 1-key token authorization.*
</div>
Unlike basic MCP servers that expose raw endpoints to LLMs without guardrails, ARES enforces strict Pre-Flight Scope In (ScopeGuard), Anti-Prompt-Injection Taint Isolation, and Single-Use 60-second HMAC Confirmation Tokens before any li action can execute.
Where Do I Start First? (Step-by-Step Onboarding)
For operators or de connecting Cursor, Claude Desktop, or Windsurf to ARES:
1. Subsystem Readiness (doctor):
Ensure all core subsystems (Protocol Engine, 9 Tools, 3 Resources, 3 Prompts, 62 Descriptors, Security Gates) report PASS:
2. 1-Click AI Client Setup (No Manual JSON Editing):
Automatically configure your preferred IDE with a single command:
This writes your acti en path directly into the client config file (e.g. .cursor/mcp.json).
3. Reload Window in Cursor IDE:
- In Cursor, press Ctrl + Shift + P.
- Select De: Reload Window.
- Open Settings (Ctrl + ,) → Features → MCP Servers. The ares server will show a green dot (Connected).
4. Launch the Li Monitor (Optional Companion Window):
In a dedicated terminal window, run the OpenClaw-style two-pane monitor to watch real-time AI tool in, scope checks, and appro:
- Left Pane: Li of tool calls executed by the AI agent (ares_scope_check, ares_dry_run_module, ares_run_tool).
- Right Pane: ScopeGuard CIDR boundaries, staged action diffs, and the Authorization Gateway.
- Controls: Press A to approve a pending execution token, R to reject, C to clear stream, Q to quit.
5. Issue Your First Command to the AI Agent:
Open Cursor Composer / Chat (Ctrl + I or Ctrl + L), and try this prompt:
> *"Check acti status, scope for target 10.0.1.50, and stage a dry-run of module ad.kerberoast."*
For in-depth architecture, the 7 security in, CLI scriptability (--json), POSIX exit codes, and operational tool schemas, see ARES MCP Gateway & Product-Grade CLI Specification.
---
Extensible De SDK (Modular Architecture)
ARES provides a first-class, type-safe Python SDK (ares.sdk) to build custom ad modules, simulate techniques in isolated test harnesses, and automate engagements programmatically:
1. Type-Safe Module Authoring (Generic BaseModule[P, R] &
Declare parameter schemas with Pydantic v2 and write modules with full IDE autocomplete:
2. Isolated Testing & Simulation (ModuleTestHarness)
Unit test custom techniques locally with mock scope guards, synthetic credential , and fluent assertion matchers:
3. Programmatic Automation (AresClient)
Automate engagements, dispatch modules, and stream real-time WebSocket telemetry scripts or CI/CD pipelines:
See docs/module_sdk.md and docs/module-de.md for full de documentation, architecture specifications, and examples.
---
Documentation Sitemap
Comprehensi is a in the docs/ directory:
---
Support & Sponsorship
If ARES has accelerated your security assessments, helped protect your enterprise infrastructure, or ad your offensi research, consider sponsoring the project to fund continuous feature de, threat research, and lab infrastructure:
<di="center">
| Platform | Type | Link |
| :--- | :--- | :--- |
| GitHub Sponsors | International (Recurring / One-time) | ![Sponsor]() |
| Saweria | Indonesia (QRIS / GoPay / OVO / Dana) | ![Saweria]() |
</div>
> *Your support helps keep ARES open-source, robust, and continuously updated against the latest ad tradecraft.*
---
Credits
<di="center">
<a href="
<img src="docs/assets/credits/muhamad-d-alvito.png" width="96" height="96" alt="Muhamad D Alvito" style="border-radius: 50%;">
</a>
Muhamad D Alvito
My Partner Work for UI & UX
![LinkedIn]()
</div>
---
Responsible Use & Legal Disclaimer
> [!IMPORTANT]
> ARES is a dual-use software framework designed exclusively for authorized cybersecurity research, internal enterprise resilience , and professional red-team engagements with explicit written permission.
To report security in ARES, please follow our Security Policy.
---
License
ARES is distributed under the open-source MIT License.
<br>
<di="center">
ARES - Modern Red Team Engagement & Continuous Security System.
*Continuous Security . Deterministic Scope Containment.*
</div>
项目信息
开发语言:Python
Star 数:591
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕ARES - authorized red-team engagement automation with dashboard, campaign scope, module orchestration, OPSEC controls, encrypted vault, and reporting.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ARES - ARES - authorized red-team engagement automation w |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:39:14 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 459 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |