 红蓝攻防
点击放大
SockTail - Lightweight binary that joins a device to a Tailsc
项目说明
SockTail
<p align="center">
<img src="img/SockTail.png" width="250">
</p>
SockTail is a small binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy on port 1080. It's meant for red team operations where you need network access into a target system without setting up wonky port forwards, persistent daemons, or noisy tunnels.
Features
* SOCKS5 proxy on port 1080 o
* Supports IPv4, IPv6, and domain addresses
* Tailscale join via tsnet, no external dependencies
* Auth key can be hardcoded (XOR-obfuscated for static analysis e) or supplied at runtime
* Fully self-contained, no configuration files or (disk writes)
This is not meant for persistence. It's a one-shot SOCKS dropper for red team ops.
<p align="center">
<img src=" width="400">
</p>
<p align="center">
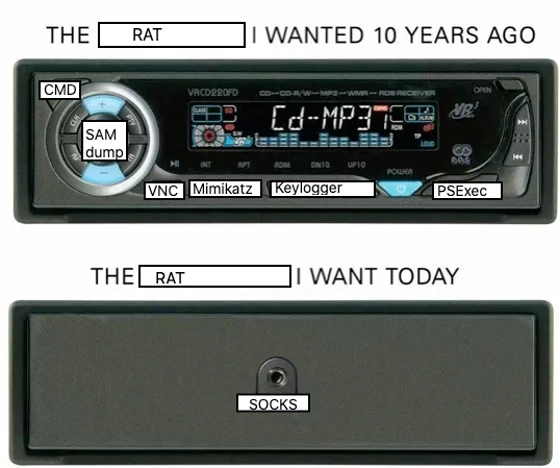
<em>Image credit: <a href=" SOCKS We Have at Home" by TrustedSec</a> — thanks for the memes.</em>
</p>
Usage
How It Works
1. On startup, SockTail creates a tsnet.Server using the provided (or embedded) Tailscale auth key and hostname.
2. It joins the Tailnet and starts listening on localhost:1080.
3. SOCKS5 negotiation is handled with no authentication (standard NO\_AUTH method).
4. Any CONNECT requests (IPv4, IPv6, domain) are accepted and forwarded using tsnet.Dial.
5. Data is relayed bi-directionally until the connection is closed.
There’s no persistence. Once the binary exits, the connection to your Tailnet is dropped.
Obfuscation
The project includes XOR-based obfuscation for the AuthKey to evade static detections. You can embed your auth key at build time using compiler flags - no manual editing required!
The key will be XOR-obfuscated and embedded automatically during the build process if no key is passed on the command line.
Build
Written in Go, no external dependencies:
The build system automatically XOR-obfuscates your auth key and embeds both the key and control URL at compile time - no manual source editing required!
Custom Control Servers: Perfect for self-hosted Tailscale solutions like Headscale. Just specify your control server URL and the appropriate auth key for that instance.
Notes
* Traffic is end-to-end encrypted /WireGuard.
* You can use this to pivot into a network, tunnel C2, or access internal services without exposing ports externally.
* Tailscale ACLs still apply. Make sure your Tailnet allows the correct access to and from the SockTail node.
项目信息
开发语言:Go
Star 数:570
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Lightweight binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy. Designed for red team operations and ephemeral access into restricted environments using Tailscale’s embedded client (tsnet). Zero config, no daemon, no persistence - just a fast way in.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SockTail - Lightweight binary that joins a device to a Tailsc |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:39:38 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 368 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |