 红蓝攻防
点击放大
ImpulsiveDLLHijack - C# based tool which automates the process of disco
项目说明
Impulsi
C# based tool which automates the process of disco and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be weaponized during RedTeam Operations to evade EDR's.
1. Methodological Approach :
The tool basically acts on automating following stages performed for DLL Hijacking:
Discovery Methodology :
Exploitation Methodology :
* The Confirmatory DLL present on the potentially Hijackable Path is loaded by the Target Binary we get following output on the console stating that the DLL Hijack was successful - DLL Hijack Successful -> DLLName: <DLLname> | <Target_binary_name>
* The Confirmatory DLL present on the potentially Hijackable Path is not loaded by the Target Binary we get following output on the console stating that the DLL Hijack was unsuccessful - DLL Hijack Unsuccessful -> <DLL_Path>
Entry Point Not Found Scenarios:
- The Confirmatory DLL present on the potentially Hijackable Path is not loaded by the Target Binary as the Entry Point of the DLL is different from our default entry point "DllMain" throwing an error - "Entry Point Not Found", we get following output on the console stating that the DLL Hijack was hijackable if the entry point was correct -> DLL Hijack Successful -> [Entry Point Not Found - Manual Analysis Required!]: <Hijack_path>
- The Confirmatory DLL present on the potentially Hijackable Path is executed by the Target Binary e the Entry Point of the DLL is different from our default entry point "DllMain" throwing an error "Entry Point Not Found", we get following output on the console stating that the DLL Hijack was success e the entry point was not correct -> DLL Hijack Successful -> [Entry Point Not Found]: <Hijack_path>
Note: The "Entry Point not found" Error is been handled by the code programmatically no need to close the MsgBox manually :) # Rather this would crash the code further
- <DLLHijack_path> --> DLL Hijack Successful (if the Hijack was successful)
- <DLLHijack_path> --> DLL Hijack Unuccessful (if the Hijack was unsuccessful)
- <DLLHijack_path> --> DLL Hijack Successful [Entry Point Not Found - Manual Analysis Required] (if the Entry point was not found but can be successful after manual analysis)
- <DLLHijack_path> --> DLL Hijack Successful [Entry Point Not Found] (if the hijack was successful e the entry point was not found)
- <DLLHijack_path> --> Copy: Access to Path is Denied (Access denied)
**These Confirmed DLL Hijackable paths can later be weaponized during a Red Team Engagement to load a Malicious DLL Implant via a legitimate executable (such as OneDri,MSEdge,"Bring your own LOLBINs" etc.) and bypass State of the art EDR's as most of them fail to detect DLL Hijacking as assessed by George Karantzas and Constantinos Patsakis as mentioned in there research paper:
2. Prerequisites:
- These are DLL files which assist the tool to get the confirmation whether the DLL's are been successfully loaded from the identified hijack path
- Compiled from the MalDLL project provided above (or use the precompiled binaries if you trust me!)
- 32Bit dll name should be: maldll32.dll
- 64Bit dll name should be: maldll64.dll
- Install NuGet Package: PeNet -> (Prereq while compiling the Impulsi project)
Note: i & ii prerequisites should be placed in the Impulsi.exe's directory itself.
- Impulsi
- Clone the repository in Studio
- Once project is loaded in Studio go to "Project" --> "Manage NuGet packages" --> Browse for packages and install "PeNet" ->
- Build the project!
- The Impulsi.exe will be inside the bin directory.
- And for Confirmatory DLL's:
- Clone the repository in Studio
- Build the project with x86 and x64
- Rename x86 release as maldll32.dll and x64 release as maldll64.dll
- Setup: Copy the Confirmatory DLL's (maldll32 & maldll64) in the Impulsi.exe directory & then execute Impulsi.exe :))
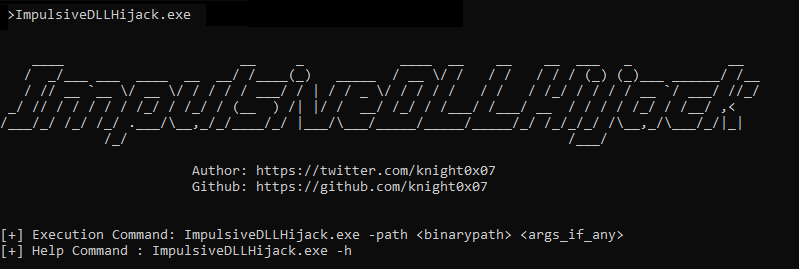
3. Usage:
!usage
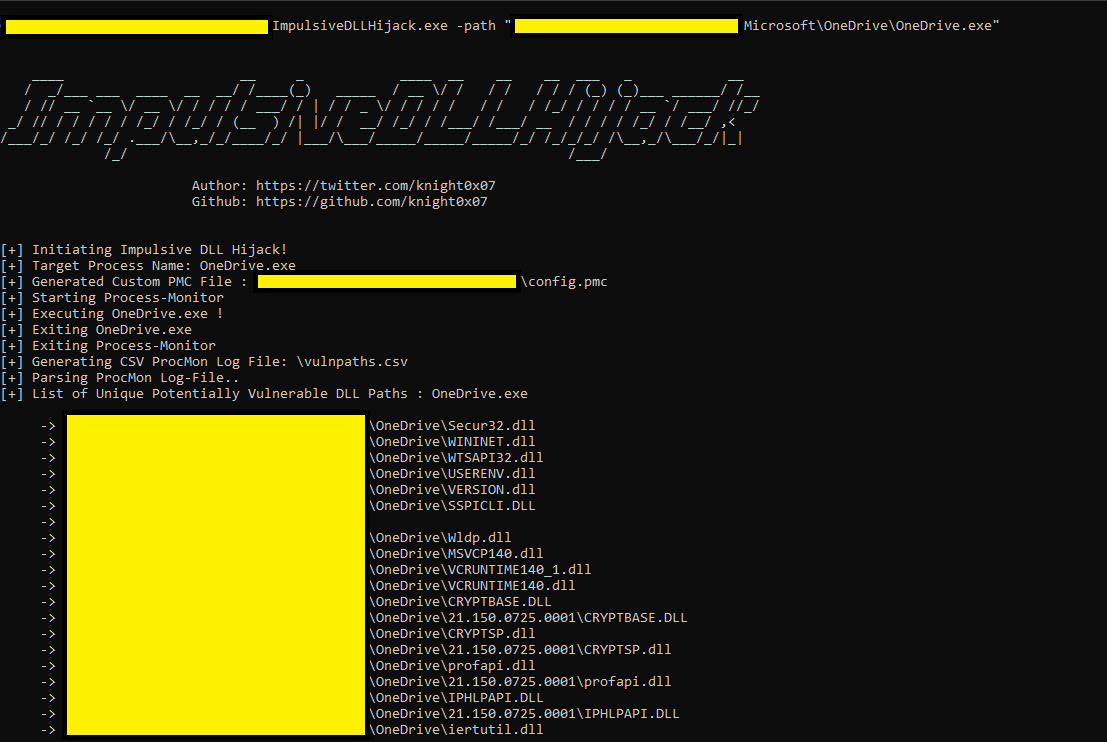
4. Examples:
!first
- Successful DLL Hijacks:
!success_one
- Unsuccessful DLL Hijacks:
!unsuccessful
- DLL is not loaded as the entry point is not identical! Manual Analysis might make it a successful DLL Hijack :)
!entrypoint_not_found
- DLL Hijack successful e unidentical entry point!
!entry_pointnot found - but dll is executed
- C:\DLLLogs\output_logs.txt:
!output_logs
Thankyou, Feedback would be greatly appreciated! - knight!
项目信息
开发语言:C#
Star 数:555
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be weaponized during Red Team Operations to evade EDR's.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ImpulsiveDLLHijack - C# based tool which automates the process of disco |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:39:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 117 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |