 红蓝攻防
点击放大
0xsp-Mongoose - a unique framework for cybersecurity simulation an
项目说明
![GPLv3 license]()
<img src="
<img src="
[<img align="right" src=" height="512" width="400">]()
<img src="
<img src="
Support the project for continuous de (ETH 0xf340c15c5e669a4ababab856e9f2bccd659d6e42)
0xsp Mongoose RED for Windows
Current Release 2.2.0
0xsp mongoose red is provided to assist your needs during cyber security simulation, by using this you will be able to audit a targeted windows operation system
for system , misconfigurations and pri escalation attacks and replicate the tactics and techniques of an ad ad in a network.
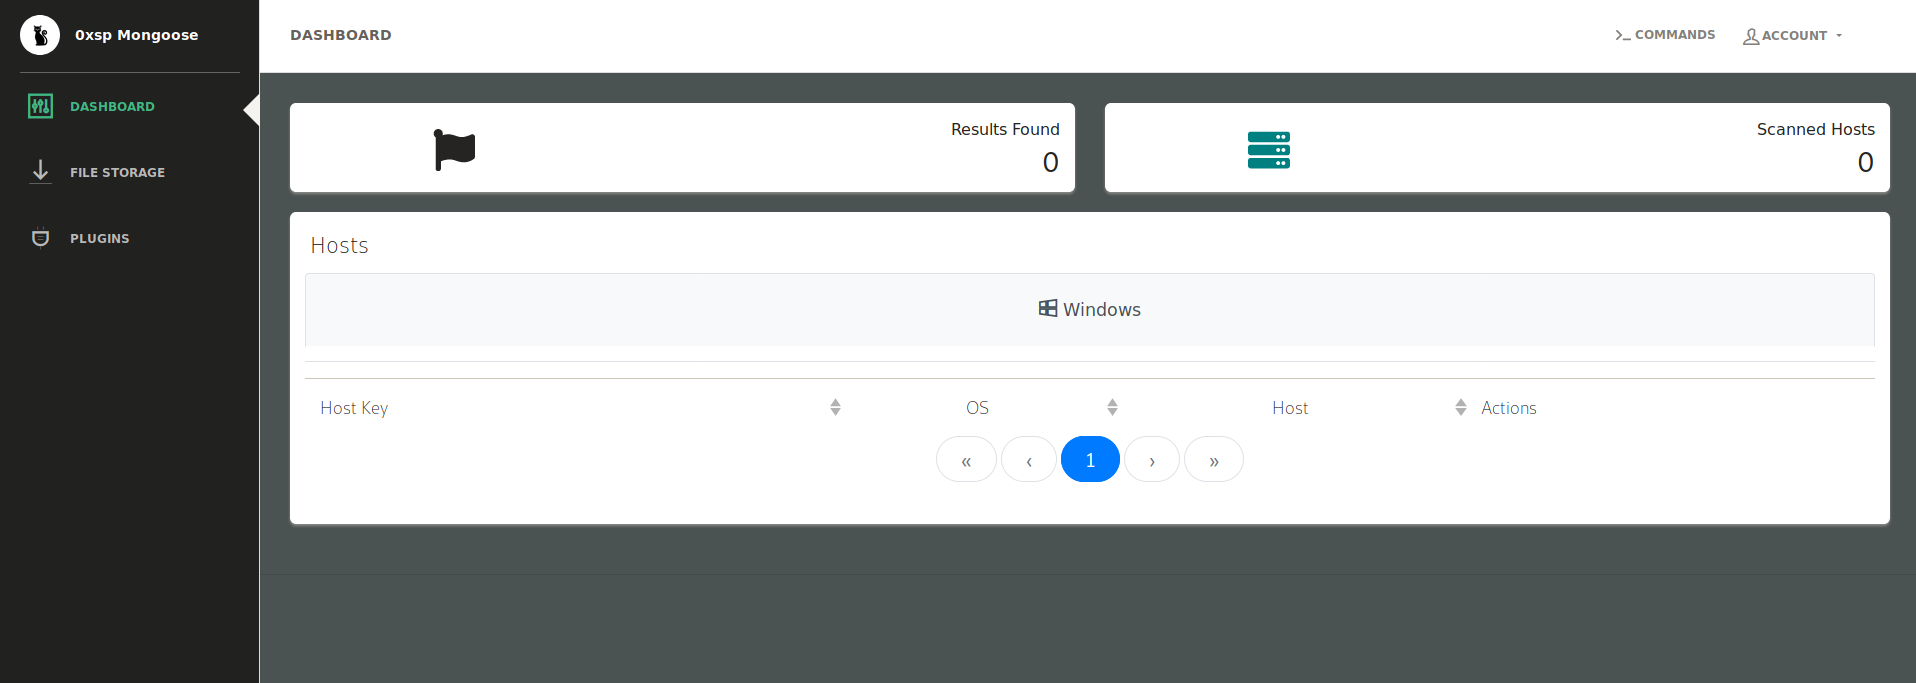
with node js support for web application API, it becomes much easier for installation and customization in timely manner, the windows sensor agent will communicate with application API to transfer results, and recei as bidirectional technique.
the agent is able to identify and detect windows exploits by using windows update api and exploit database definitions modules, the new release will detect also the following
.
* C
* C
* C
* C
* C
* C
* C
* C
* C
* C
* C
* C
* C
* C
Features
* Windows Pri escalation scanning techniques.
* web application built with NodeJS
* supports sqlite DB
* Lateral mo techniques. video
* Bidirectional communication channel. video
* Plugins online packaging.
* Enhanced exploit detecter scripting engine.
* Windows Account Bruteforce Module (Local / Domain)
* weaponization of run-as-user windows api function. Video
* local network scanning and shares enumeration.
* lsass memory dummping technique (plugin).
* DNS C2C interacti
installation
default access credentials :
* username : admin
* password : 0xsp
[<img align="right" src="]()
DNS C2C python script
quick deploy of agent
Usage
Documentations
detailed research site
Security Conferences
* Standoff365 - Russia ()
tool tutorials
make sure to subscribe into the following channel to be notified when new tutorial and tricks published for 0xsp
项目信息
开发语言:Pascal
Star 数:533
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and privilege escalations attacks, replicate the tactics and techniques of an advanced adversary in a network.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | 0xsp-Mongoose - a unique framework for cybersecurity simulation an |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:40:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 527 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |