 红蓝攻防
点击放大
OffensiveGo - Golang weaponization for red teamers.
项目说明
OffensiveGo - Golang Weaponization for red teamers.
!image
This repo is made by , & and contains some examples of offensi & utilities rewrote in Golang that can be used in a red team engagement.
Table of Content
- Installation
- Workspace Setup
- Compilation
- Assembly in Go
- Obfuscate Go Builds
- Golang Binary
️💾 Previous works
These repo inspires us to make OffensiveGo
📝 About Golang
OPSEC Consideration & Caveat of Golang
Go binaries generally have no installation dependencies, compiler statically links Go runtime and needed packages. Static linking results in larger binaries. 1.9 MB for "Hello World" compared to 54 KB in C.
🏗 Workspace Setup
go.mod file in your project directory, which will be used to manage dependencies :Compilation
go build file.go for compilation.Assembly in Go
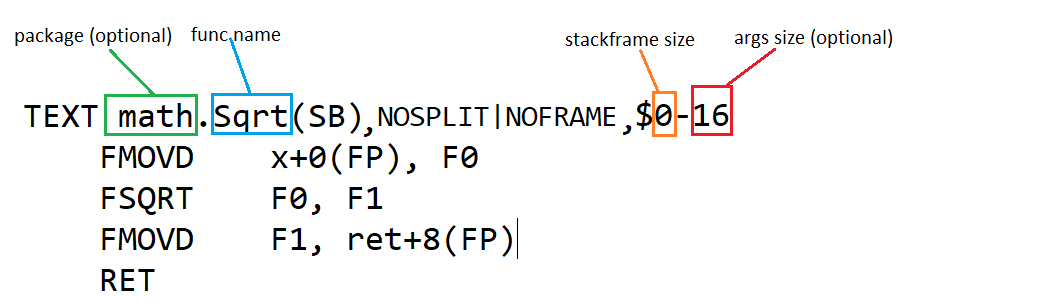
The assembly language used with Go is based on Plan9 (P9) and is a high-ledent language that includes mnemonics like CALL and RET, as well as higher-le like loops and conditionals, which are implemented using lower-le instructions by the assembler.
!image
- NOSPLIT : Don't insert the preamble to check if the stack must be split. The frame for the routine, plus anything it calls, must fit in the spare space remaining in the current stack segment. Used to protect routines such as the stack splitting code itself, which can impro.
- NOFRAME : skip the generation of a function prologue and epilogue, even if this is not a leaf function, which can also impro by reducing the o of setting up and tearing down the stack frame for each call.
> Note : It can be useful to use Assembly in Go for your loaders if you want to build direct / indirect syscall stub.
Obfuscate Go Builds
you can obfuscate Go builds using garble to replace strings and many other indcators with base64 encoding and remo intformations if necessary :
Golang Binary
symtab (symbol table) section contains symbol table information to map program addresses to their corresponding function and names. The symtab section in a Golang binary is generated by the Go linker.!image
Go-http-client/1.1 has the user-agent.!image
Examples
| File | Description |
|-------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------|
| Process Injection - APC | Execute a shellcode with NtQueueApcThread |
| Process Injection - CreateThread | Execute a shellcode with NtCreateThreadEx and CreateThread | | | | |
| AMSI Patching | bypass AMSI by patching in memory AmsiScanBuffer |
| ETW Patching | bypass ETW, by patching in memory with ret on NtTraceControl |
| Network | TCP, HTTP, and named pipes servers and clients for different communication channels. |
| WMI Query | List the AV/EDR solution with a wmi query |
| sRDI | Convert DLL files to position independent shellcode |
| Cryptography | Encryption algorithms for usage. Contains AES, RC4, chacha20 and xor. |
| Self Remove | Self remove a executable. Golang implementation of delete-self-poc |
| Process Dump | Dump any process with MiniDumpWriteDump. In this example, it dumps LSASS |
| Dllmain | DllMain() entrypoint in Golang from this. Can be used for dll hijacking. |
| Token Manipulation | Play with windows token. List all the token, ImpersonateLoggedOnUser and CreateProcessWithToken. |
| Sandbox detection/e| Sandbox detection and e techniques |
| Callback Injection| Callback shellcode injection using GrayStringA, EnumFonts and more... |
| Instrumentation Callback| Disable Instrumentation Callback on your process to reduce any potential direct syscall detection |
> Note : The misc folder contains some scripts like con_format.sh that can be written in other languages but but still relates to the Golang language.
> Note : More Examples will be added in the future :D
🔎 Interesting Tools in Golang
I would also mention the timwhitez's github that contains many re-implementations in Golang.
🎖 Credits
项目信息
开发语言:Go
Star 数:526
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Golang weaponization for red teamers.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OffensiveGo - Golang weaponization for red teamers. |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:40:11 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 278 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |