 红蓝攻防
点击放大
Wyrm - The dragon in the dark. A red team post exploitat
项目说明
Wyrm - v0.7.2 Hatchling
Wyrm (pronounced 'worm', an old English word for 'serpent' or 'dragon') is a post exploitation, open source, Red Team security testing framework framework, written in Rust designed to be used by Red Teams, Purple Teams,
Penetration Testers, and general infosec hobbyists. This project is fully built in Rust, with extra effort going into obfuscating artifacts which
could be present in memory. Project created and maintained by flux, for legal authorised security testing only.
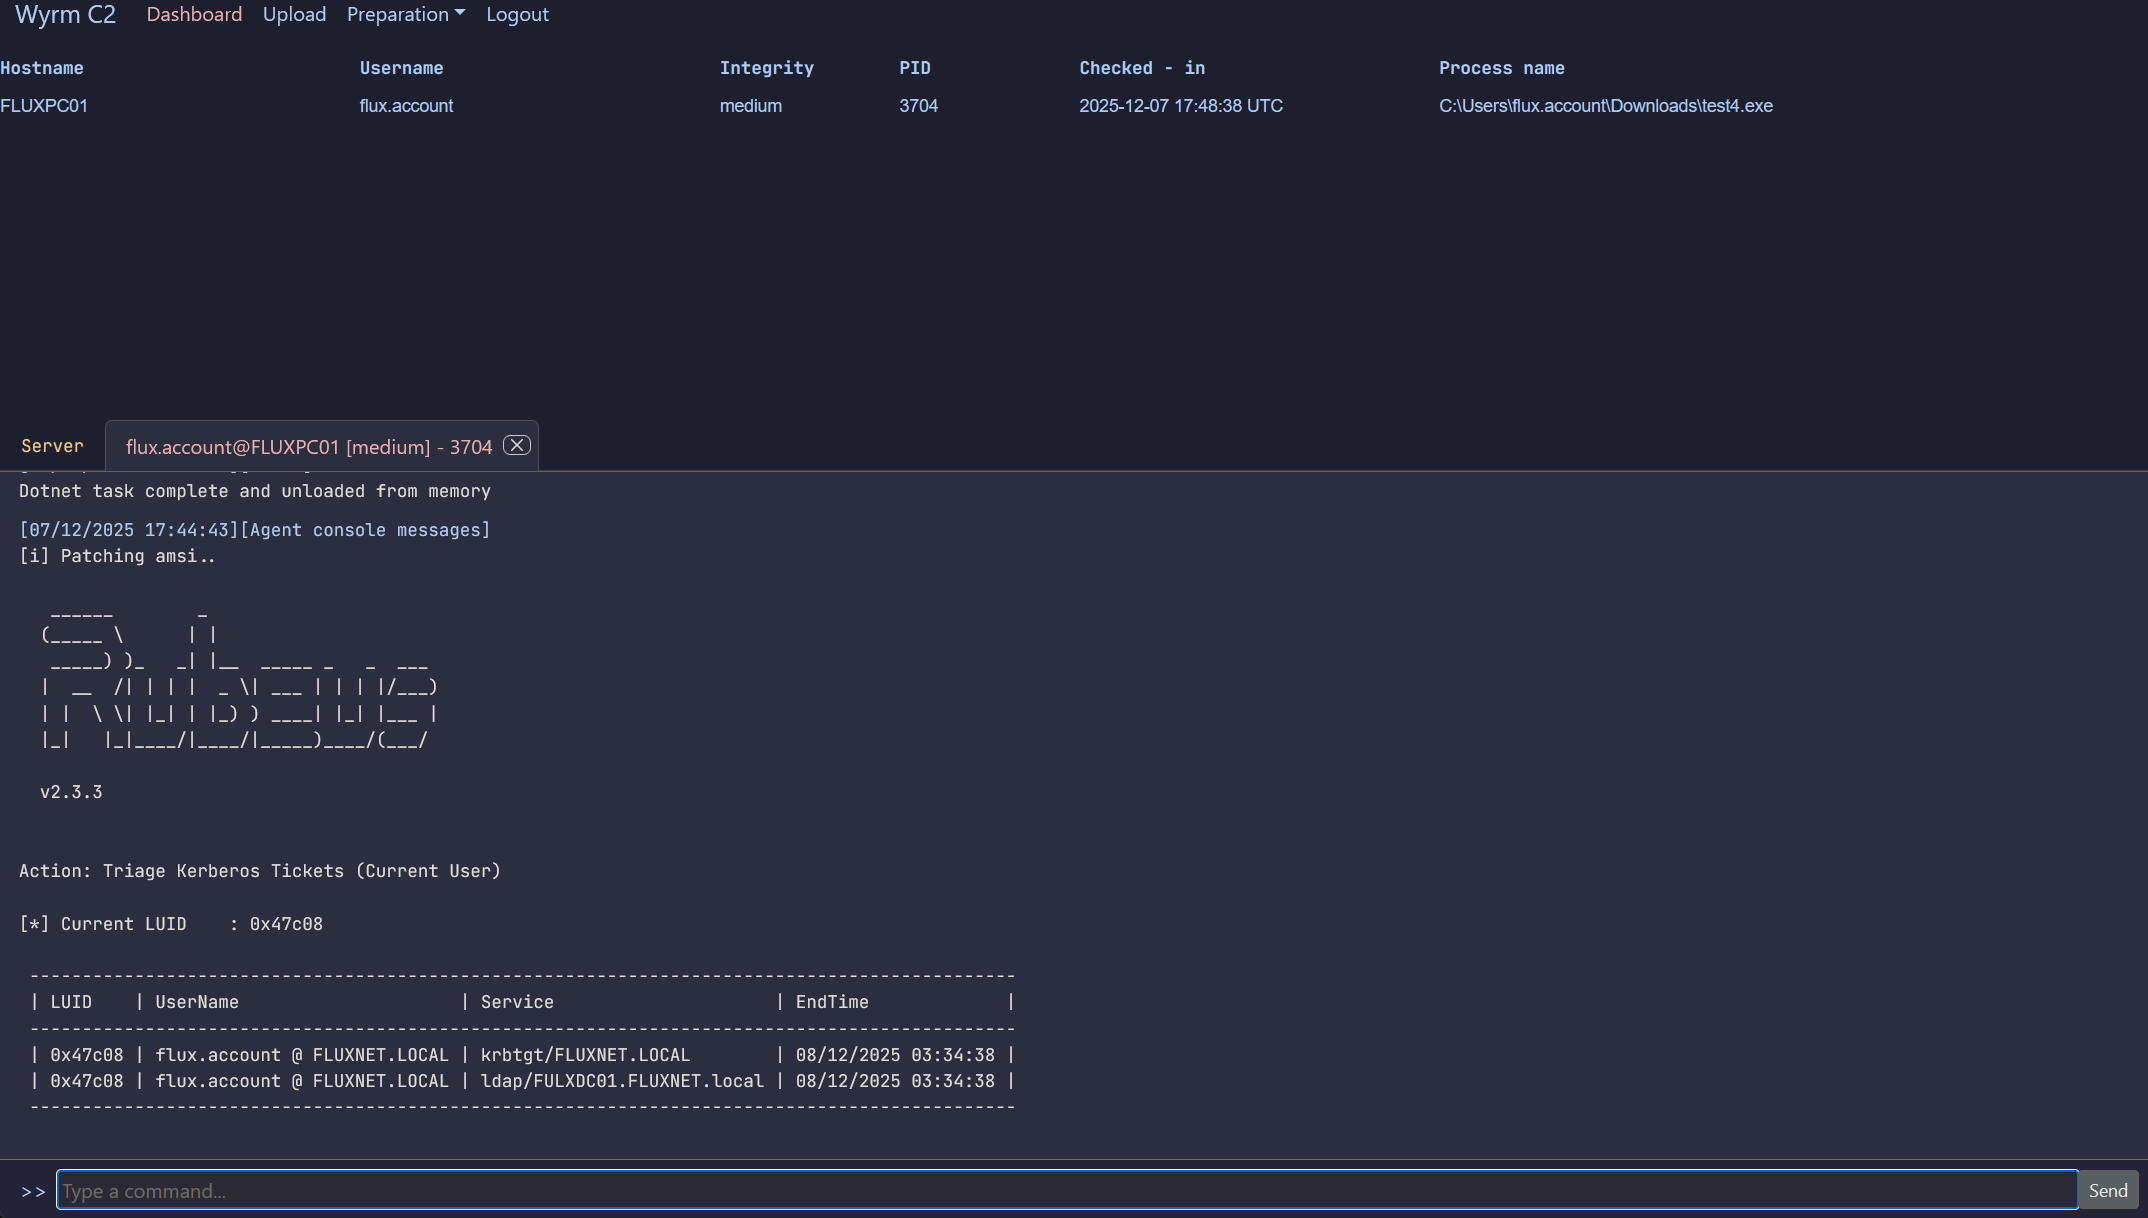
!Wyrm C2
Read the docs at for quick setup instructions. Or jump in to read about customisable profiles,
e, and obfuscation. The docs
will be updated as the project grows and gains more capabilities.
Pre-release . If you want to support this project, please give it a star! I will be releasing updates and
devlogs on my blog and YouTube to document progress, so please give me a follow there.
IMPORTANT: Before pulling updates, check the Release Notes for any
breaking changes to profiles / configs which you may need to manually adjust or migrate. This is done especially so that updates do not
o your local configs and agent profiles.
Post exploitation Red Team framework
Wyrm currently supports only HTTPS agents using a custom encryption scheme for encrypting traffic below TLS, with a unique packet design so that
the packets cannot be realistically decrypted e firewall level TLS inspection.
Updates are planned through 1,0, 2.0, 3.0, and 4.0. You can view
the planned roadmap in this project (see Milestones.md). In time, this is designed to be an open source competitor to Cobalt Strike, Mythic, Sliver, etc.
For any bugs, or feature requests, please use the Issues tab, and for anything else - please use GitHub Discussions. I am active on this project,
so I will be attentive to anything raised.
Features
This project is not currently accepting contributions, please raise issues or use GitHub Discussions and I will look into them, and help
answer any questions.
Loader
The Wyrm C2 comes with a loader for the reflective DLL component of the toolkit. The loader has the Wyrm postex payload encrypted in its
.text section; for more information please see the docs. the loader runs as follows:
!Wyrm reflective DLL loader
Updates
WARNING: Before pulling an update; please check the release notes to see whether there are any breaking changes - for example if the
configurable C2 profile changes in a breaking way from a previous profile you have, you will want to make sure you backup and migrate
your profile. I will be excluding /c2/profiles/* and .env from git once the project is published in pre-release to prevent accidentally o
your previous profile when running git pull to update your software.
As per the roadmap, this project will see significant de over the next 12 months. To pull updates, whether they are new features
or bug fixes, you simply just do a git pull, re-build : docker compose up -d --build c2 and docker compose up -d --build client.
The legal bit
Authorized Use Only
Permitted Users
The Software is intended exclusively for authorised penetration testers, Red Teams, Purple Teams, hobbyists, and security researchers who ha explicit, written authorisation from the owner of each target system.
Any use of the Software on systems for which you do not hold such authorisation is strictly prohibited and may constitute a criminal offence under the UK Computer Misuse Act 1990 (including sections on Unauthorised access to computer material, Unauthorised access with intent to commit further offences, and Unauthorised acts impairing operation) or equi laws elsewhere.
Prohibited Conduct
You must not use, distribute, or facilitate use of the Software for:
Or equi offenses in other jurisdictions.
No Encouragement of Misuse:
The Author expressly does not condone, support, or encourage any illegal or malicious activity. This Software is provided purely for legitimate security-testing purposes, in en where full authorisation has been granted.
Compliance with Laws & Regulations
Local Laws: You alone are responsible for ensuring your use of the Software complies with all applicable local, national, and international laws, regulations, and corporate policies.
No Warranty
The Software is provided “as is” and “as a”, without warranties of any kind, express or implied.
We make no warranty of merchantability, fitness for a particular purpose, or non-infringement.
We do not warrant that the Software is error-free, secure, or uninterrupted.
Limitation of Liability
To the fullest extent permitted by law, neither the Author nor contributors shall be liable for any:
This limitation applies even if we have been advised of the possibility of such damages. It is the responsibility of the professional operator to
use this tool safely.
项目信息
开发语言:Rust
Star 数:507
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕 The dragon in the dark. A red team post exploitation framework for testing security controls during red team assessments. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Wyrm - The dragon in the dark. A red team post exploitat |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:40:27 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 497 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |