 红蓝攻防
点击放大
Credential-Dumping - This cheatsheet is aimed at the Red Teamers to hel
项目说明
🔑 Credential Dumping for Pentesters
A practical credential dumping reference and cheat sheet designed for red teamers, penetration testers, and cybersecurity learners to understand how credentials can be extracted from compromised systems during post-exploitation.
🌐 Connect With Us
🔵
⚫ Twitter/X – Follow Us
🟣 Discord – Join Server
💼 LinkedIn – Follow HackingArticles
🎓 Training Program
🚀 Join Our Cybersecurity Training Program
Hands-on training in Penetration Testing, Red Teaming, and Cybersecurity.
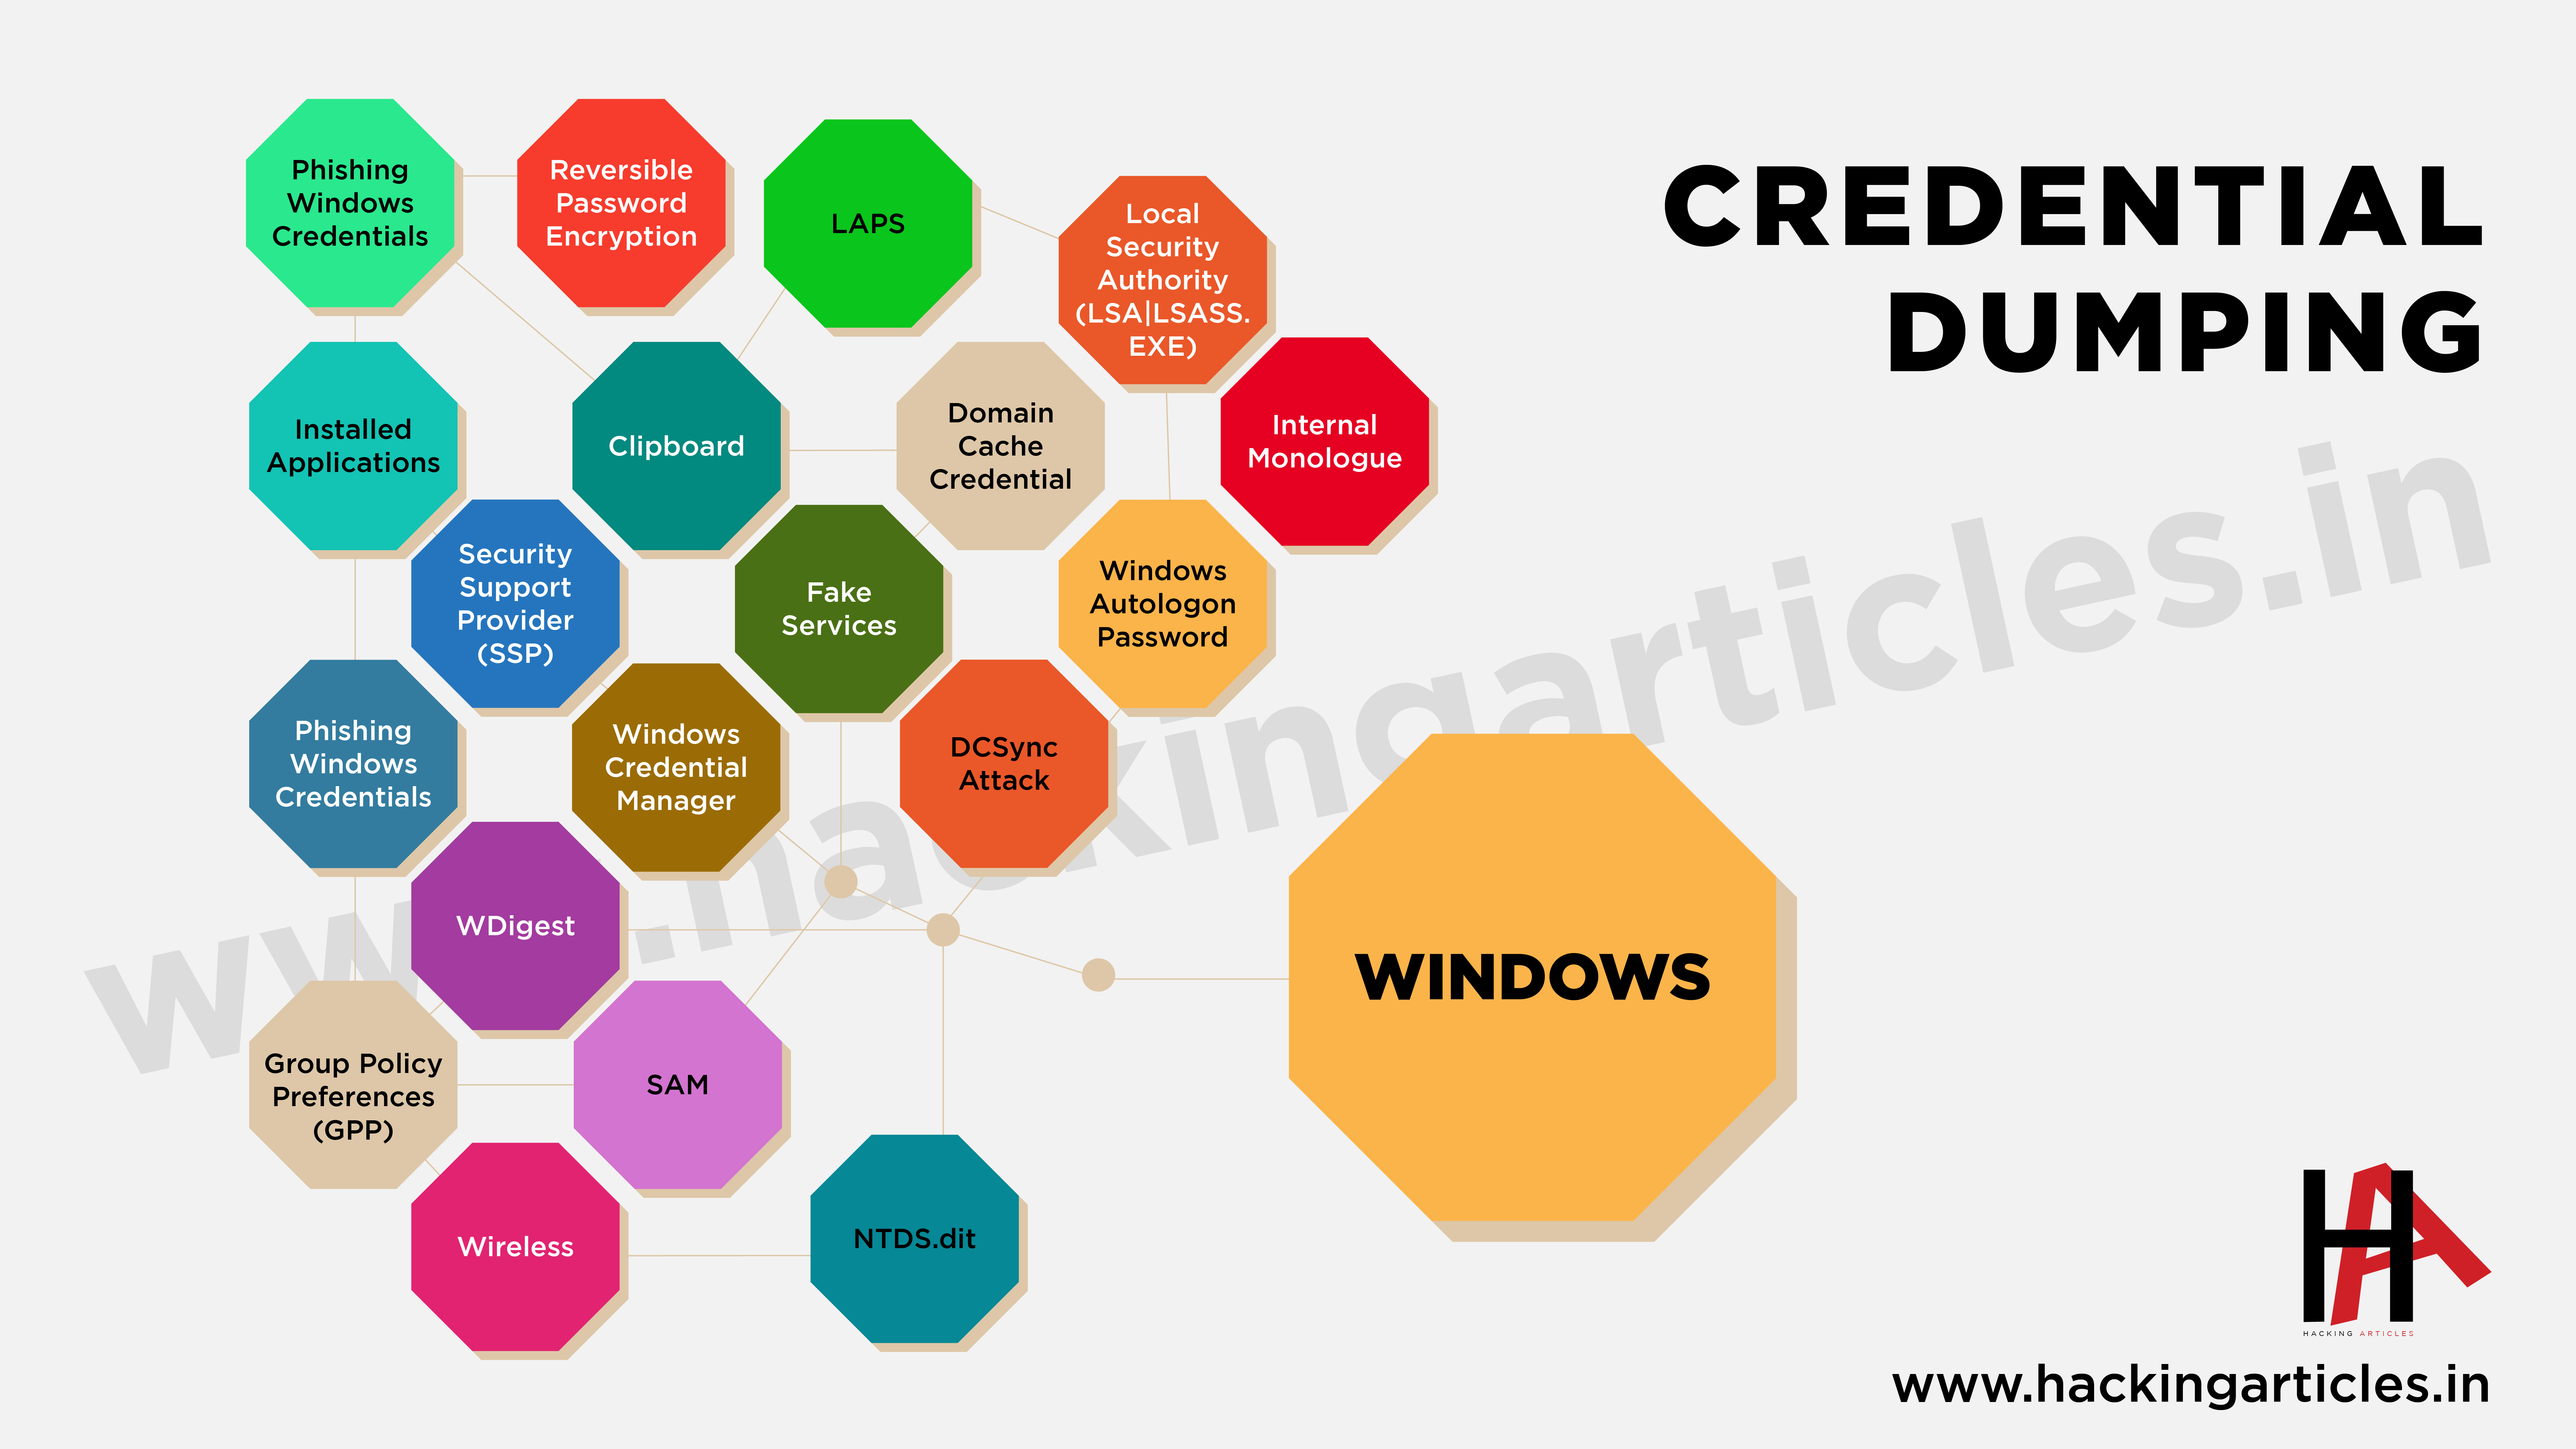
🔑 Credential Dumping Techniques
| # | Topic | Description | Article |
|---|---|---|---|
| 1 | 📶 Wireless | Extract stored wireless credentials from compromised systems | Read Article |
| 2 | 🗂️ Group Policy Preferences (GPP) | Dump passwords stored in Group Policy Preferences | Read Article |
| 3 | 🔐 Windows Credential Manager | Extract credentials stored in Windows Credential Manager | Read Article |
| 4 | 🧠 WDigest | Dump cleartext credentials from WDigest authentication protocol | Read Article |
| 5 | 🛠️ Security Support Provider (SSP) | Extract credentials via SSP injection techniques | Read Article |
| 6 | 💾 SAM | Dump password hashes from the Windows SAM database | Read Article |
| 7 | 📦 Installed Applications | Extract credentials stored by installed applications | Read Article |
| 8 | 🗄️ NTDS.dit | Dump Acti credentials from NTDS.dit database | Read Article |
| 9 | 🎣 Phishing Windows Credentials | Capture Windows credentials using phishing techniques | Read Article |
|10 | 🧬 Local Security Authority (LSA/LSASS) | Extract credentials directly from LSASS process memory | Read Article |
|11 | 📋 Clipboard | Capture sensiti copied to the clipboard | Read Article |
|12 | 🔄 DCSync Attack | Simulate a domain controller to dump AD credentials | Read Article |
|13 | 🔑 LAPS | Extract Local Administrator Password Solution credentials | Read Article |
|14 | 🧾 Domain Cache Credential | Dump cached domain credentials from Windows systems | Read Article |
|15 | ⚙️ Fake Services | Use malicious services to capture credentials | Read Article |
|16 | 🔓 Windows Autologon Password | Extract plaintext autologon passwords from registry | Read Article |
|17 | 🧠 Internal Monologue | NTLM downgrade attack to retrie credentials | Read Article |
|18 | 🔁 Re Password Encryption | Dump passwords stored using re encryption in AD | Read Article |
|19 | 🧾 GMSA | Extract Group Managed Service Account passwords | Read Article |
|20 | 📝 AD User Comment | Disco stored in Acti user comments | Read Article |
!image
项目信息
开发语言:未知
Star 数:502
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕This cheatsheet is aimed at the Red Teamers to help them understand the fundamentals of Credential Dumping (Sub Technique of Credential Access) with examples. There are multiple ways to perform the same tasks展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Credential-Dumping - This cheatsheet is aimed at the Red Teamers to hel |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:40:36 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 436 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |