 红蓝攻防
点击放大
AlanFramework - A C2 post-exploitation framework
项目说明
Alan Framework
Alan Framework is a post-exploitation framework useful during red-team acti.
If you find my tool useful, please consider to <a href=" me</a>.
⚠⚠⚠ Disclaimer ⚠⚠⚠
The creation of this kind of software has always caused contro. If you're wondering why I decided to create this tool, it's because I'm con that the ultimate learning experience is implementing what you learned. During the reverse engineering process, many small details are o. Little by little, these details prevent the researcher from having a complete picture of what is going on. Finally, I'm a programmer first, and I love to develop this kind of program 😄
Download
<a href=" Alan C2 Framework</a>
Notable Features
* You can run your preferred tool directly in-memory
* Ja script execution (in-memory without third party dependency)
* Fully compliant SOCKS5 proxy
* Supported agent types: Powershell (x86/x64), DLL (x86/x64), Executable (x86/x64), Shellcode (x86/x64)
* Server.exe can be executed in Linux ( core)
* The network communication is fully encrypted with a session key not reco from the agent binary or from a traffic dump
* Communication performed via HTTP/HTTPS
* No external dependencies or libraries need to be installed
* A powerful command shell
* The agent configuration can be updated on the fly (you can change port and protocol too)
Documentation:
Blog posts
* <a href=" c2 Framework v7.0: Hyper-Pi</a>
* <a href=" c2 Framework v6.0: Alan + Ja = ♡</a>
* <a href=" c2 Framework v5.0 - All you can in-memory edition</a>
* <a href=" post-exploitation framework v4.0 released</a>
* <a href=" - A post exploitation framework</a>
For more information on its usage please read the <a href="
Compile the source code
To compile _Alan_ the following actions must be performed:
* Ensure that you ha <a href=" and that it is in the PATH (run _cmake --help_ to see if it works)
* Install Studio 2022 (the Community Edition is fine). These steps were tested against VS 2022 17.3.1
* Be sure that _.NET Desktop De, _Desktop de with C++_ and the F# language are installed as part of the Studio suite
* Install .NET libraries by running: ./src/ser.exe install
* Open the file .src/ser.sln in Studio. Set the Ser project as the main one (right click -> Set as Startup Project)
* Run the Ser which will compile e
* If the compilation ended succesfully, the Alan .zip file will be located in the newly created directory Misc/out/release
:
Demo
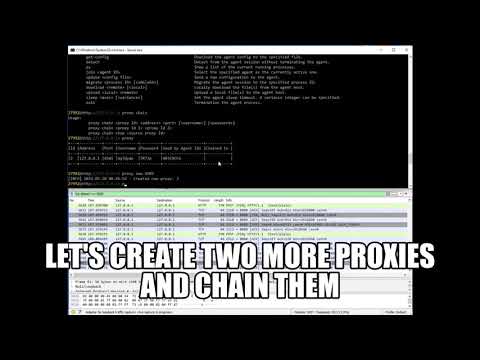
| Alan v7.0.514.10 - SOCKS5 Proxy ![Alan C2 Framework v7.0, codename: Hyper-Pi]() | Alan v6.0.511.28 - JS Execution ![Alan C2 Framework 6.0 - Alan + Ja = ♡]() | Alan v5.0.509.20 - In-Memory Execution ![Alan 5.0 C2 Framework - All You Can In-Memory Edition]() |
| :---: | :---: | :---: |
|Alan v4.0.0 - x64 Agent && Inject ![Alan post-exploitation framework v4.0 demo]()| Alan v3.0.0 - Misc Commands ![Alan v3.0 - Post-Exploitation Framework]() | Alan v2.0.500.23 ![Alan post-exploitation framework - Update the agent profile at runtime]() |
|Alan v1.0.0 ![Alan v1.0 - A Post-Exploitation Framework]() | | |
Changelog
v7.0.514.10 - 15/05/2022
* Implemented
proxy command for pi* The
info and info++ commands display if the agent is using a proxy* Fixed bug on network communication (Issue 2)
* Fixed error in PE loader when function are import
* Fixed JS module causing memory free ahead of time
* Fixed error in
run command that cause the & option to not work* The log messages are now saved to file
alan.log* All the generated output and user input is logged to an e file inside the
e folder* Added machine ID information to
info command* Added
v6.0.511.28 24/02/2022
* x86/x64 PE loaders modified to update the PEB->Ldr field. This allows the system to call DLL_PROCESS_DETACH on the injected DLL.
* Increase max response size to 1GB. This fix the download of big files.
* Added agent expiration date to the configuration.
* The
run was extended to support the execution of Ja files.*
info++ command now shows the label and the FS type.v5.0.509.20 - 13/12/2021
* Implemented
run command* Implemented
kill command* Implemented
exec command* Removed
inject message since it can be achieved with the run command in background* Created stager and PE loader to make the agent stealthier. Each generated agent file has a different hash
* Improved code injection to bypass Dynamic Code Policy Mitigation
* It is now possible to specify the agent file name to create during the wizard
* Fixed error in
upload and download commands* Fixed error in shell creation. The command shell process token did not have the same agent integrity level
* Remo function from DLL agent artifact
* Added current working directory to
info command* Extended
shell command to execute a single commandv4.0.0 - 26/09/2021
* Added
inject command. This command allows the operator to inject code into a remote process* Added
sleep command performed in short sleep of 400 msec each.* Introduced Jitter concept in
sleep* Ported agent to x64 bit (included PE32+ loader)
* Fixed errors in x86 PE loader
* .NET agent runner is now executed in a stealthier way to avoid detection
* It is now possible to specify a custom Web server in the HTTP/S listener response
* Remo
listeners since superfluous * Improved
info command with more information* Error message are more explanatory
* Added information on process token type (elevated or not)
* Added information on process token pri
* Added information on process token groups
v3.0.0 - 15/05/2021
* Renamed agent shell
quit command to exit* Implemented agent migration via
migrate command* Fixed error in retrieving OS
* Added DLL as agent format in the creation wizard.
* Implemented
ps command to list the currently running processes* Implemented
download command to locally download a file or an entire directory * Implemented
upload command to upload files to the compromised host* Implemented
SuccessRequest as HTTP ser option to customize the http/s listener response* Implemented
ErrorRequest to customize the http/s listener response for bad requests* Implemented
prepend and append as HTTP ser option to specify in the agent profv2.0.500.23 - 20/03/2021
* Implemented agent
detach command to temporary exit from a joined agent* Implemented shell
detach command to temporary exit from a command shell* Implemented
listeners command to list the a listeners* Implemented HTTPS listener to communicatewith the agent via TLS
* Implemented
get-config command to download the current agent configuration* Implemented
update command to update the agent configuration* Windows7 is now supported
v1.0.0 - 22/02/2021
* First Release
项目信息
开发语言:Assembly
Star 数:485
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A C2 post-exploitation framework展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AlanFramework - A C2 post-exploitation framework |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:40:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 524 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |