 红蓝攻防
点击放大
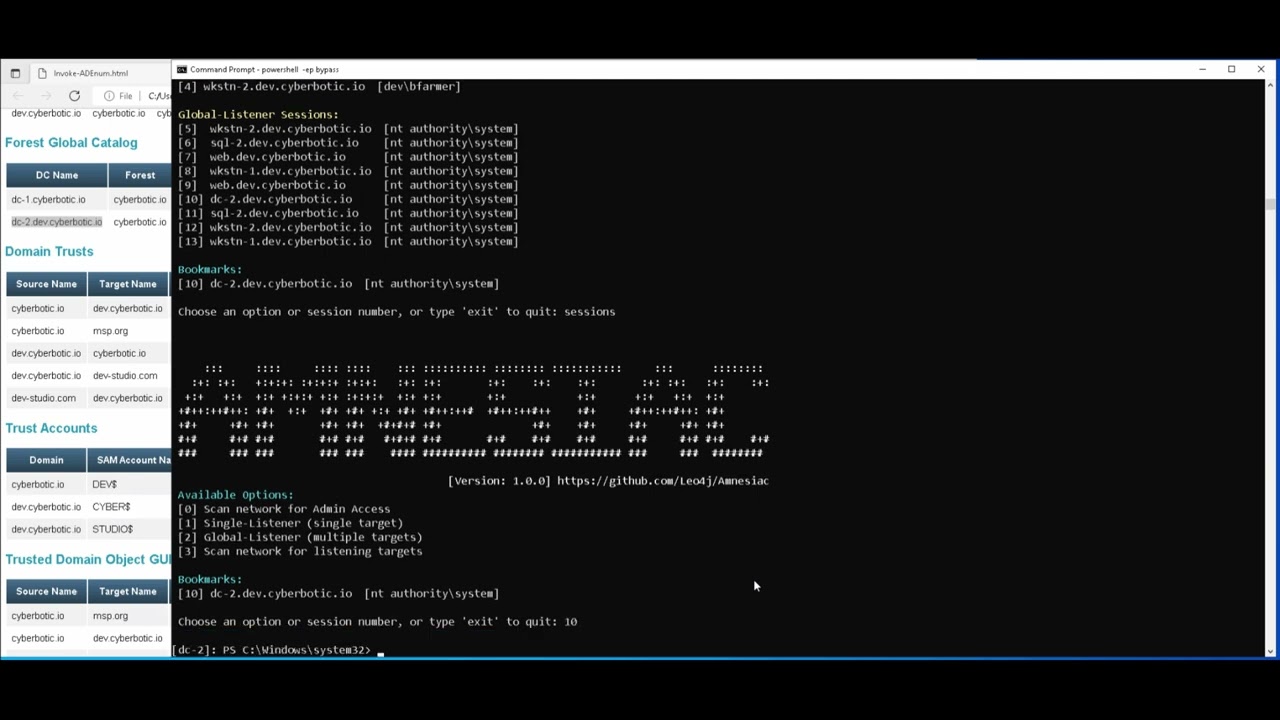
Amnesiac - Amnesiac is a post-exploitation framework entirely
项目说明
!Amnesiac3
!279440077-678ce24e-70c4-47b1-b595-ca0835ba35d9
Amnesiac
Amnesiac is a post-exploitation framework designed to assist with lateral mo within acti en.
Amnesiac is being de to bridge a gap on Windows OS, where post-exploitation frameworks are not readily a unless explicitly installed. In fact, it is entirely written in PowerShell, and can be loaded and executed in memory, just like any other PowerShell script.
If you find Amnesiac and you like this project, please consider giving us a star on GitHub. Your support motivates the de to continue improving and maintaining this project.
Please read the documentation to get the best out of Amnesiac:
Load and run
If you need to run Amnesiac through a shell, use Amnesiac_ShellReady.ps1 | No colors, shell compatible
Key Features
Command Execution o (SMB)
Amnesiac sends commands and recei through Named Pipes, ensuring discreet and efficient post-exploitation acti.
No Installation Required
Unlike traditional frameworks, Amnesiac does not require installation. It operates entirely in memory, reducing the risk of detection and forensic footprint.
User-Friendly Framework
Amnesiac is designed with usability in mind. It provides a user-friendly interface, making it accessible and efficient for both beginners and experienced users.
Post-Exploitation Modules
Amnesiac comes equipped with an array of post-exploitation modules, ranging from keyloggers to Kerberos ticket dumping tools. These modules can be seamlessly integrated into your testing and assessment workflows.
Acknowledgments
Amnesiac relies on few other projects for its modules. In each module, you'll find reference link information, ensuring proper attribution to the original creators.
Support and Contributions
Contributions and feedback from the community are highly encouraged and appreciated.
Preview
Watch on YouTube :point_down:
![Watch the video]()
!image
License
Amnesiac is distributed under the GPL-3.0 License. Please review the license for details on usage and redistribution.
Disclaimer
Amnesiac is intended exclusively for research, education, and authorized testing. Its purpose is to assist professionals and researchers in identifying and enhancing system security.
Users must secure explicit, mutual consent from all parties in before utilizing this tool on any system, network, or digital en, as unauthorized acti can lead to serious legal consequences. Users are responsible for adhering to all applicable laws and regulations related to cybersecurity and digital access.
The creator of Amnesiac disclaims liability for any misuse or illicit use of the tool and is not responsible for any resulting damages or losses.
THE SOFTWARE IS PROVIDED “AS IS,” WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE, AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES, OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT, OR OTHERWISE, ARISING FROM, OUT OF, OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
项目信息
开发语言:PowerShell
Star 数:452
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Amnesiac is a post-exploitation framework entirely written in PowerShell and designed to assist with lateral movement within Active Directory environments展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Amnesiac - Amnesiac is a post-exploitation framework entirely |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:41:23 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 325 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |