 红蓝攻防
点击放大
Mr.SIP - SIP Security Assessment Framework for VoIP Pentest
项目说明
<di="center">
<img src="assets/mrsip-banner.svg" alt="Mr.SIP" width="280">
SIP Security, Attack and Audit Framework

![CI]()
![Black Hat Arsenal]()
![Black Hat Arsenal]()
![Black Hat Arsenal]()
![Black Hat Arsenal]()
![Offzone Moscow]()
![DEF CON 28]()
![Black Hat Arsenal]()
![Securi-Tay 2023]()
![Black Hat MEA 2022]()
![Black Hat Arsenal]()
</div>
---
Mr.SIP is a simple, console-based SIP audit and attack tool. It was originally de for academic work on no DDoS attacks, and e into a fully functional SIP-based penetration testing tool. It has since been cited in several academic papers and journal articles, and can also be used as a SIP client simulator and traffic generator.
This public repository ships 3 modules — network scanning, user enumeration, and DoS attack simulation. Mr.SIP Pro extends this with more modules and a web GUI.
Documentation
chan_sip/Trixbox) labs, generalizing to other Asterisk-based PBXs--mt message type actually does, --if/--pps/--mtu in depth, ngrep, debug mode, architecture/data-flow diagramPublic Modules
| Module | Purpose |
|---|---|
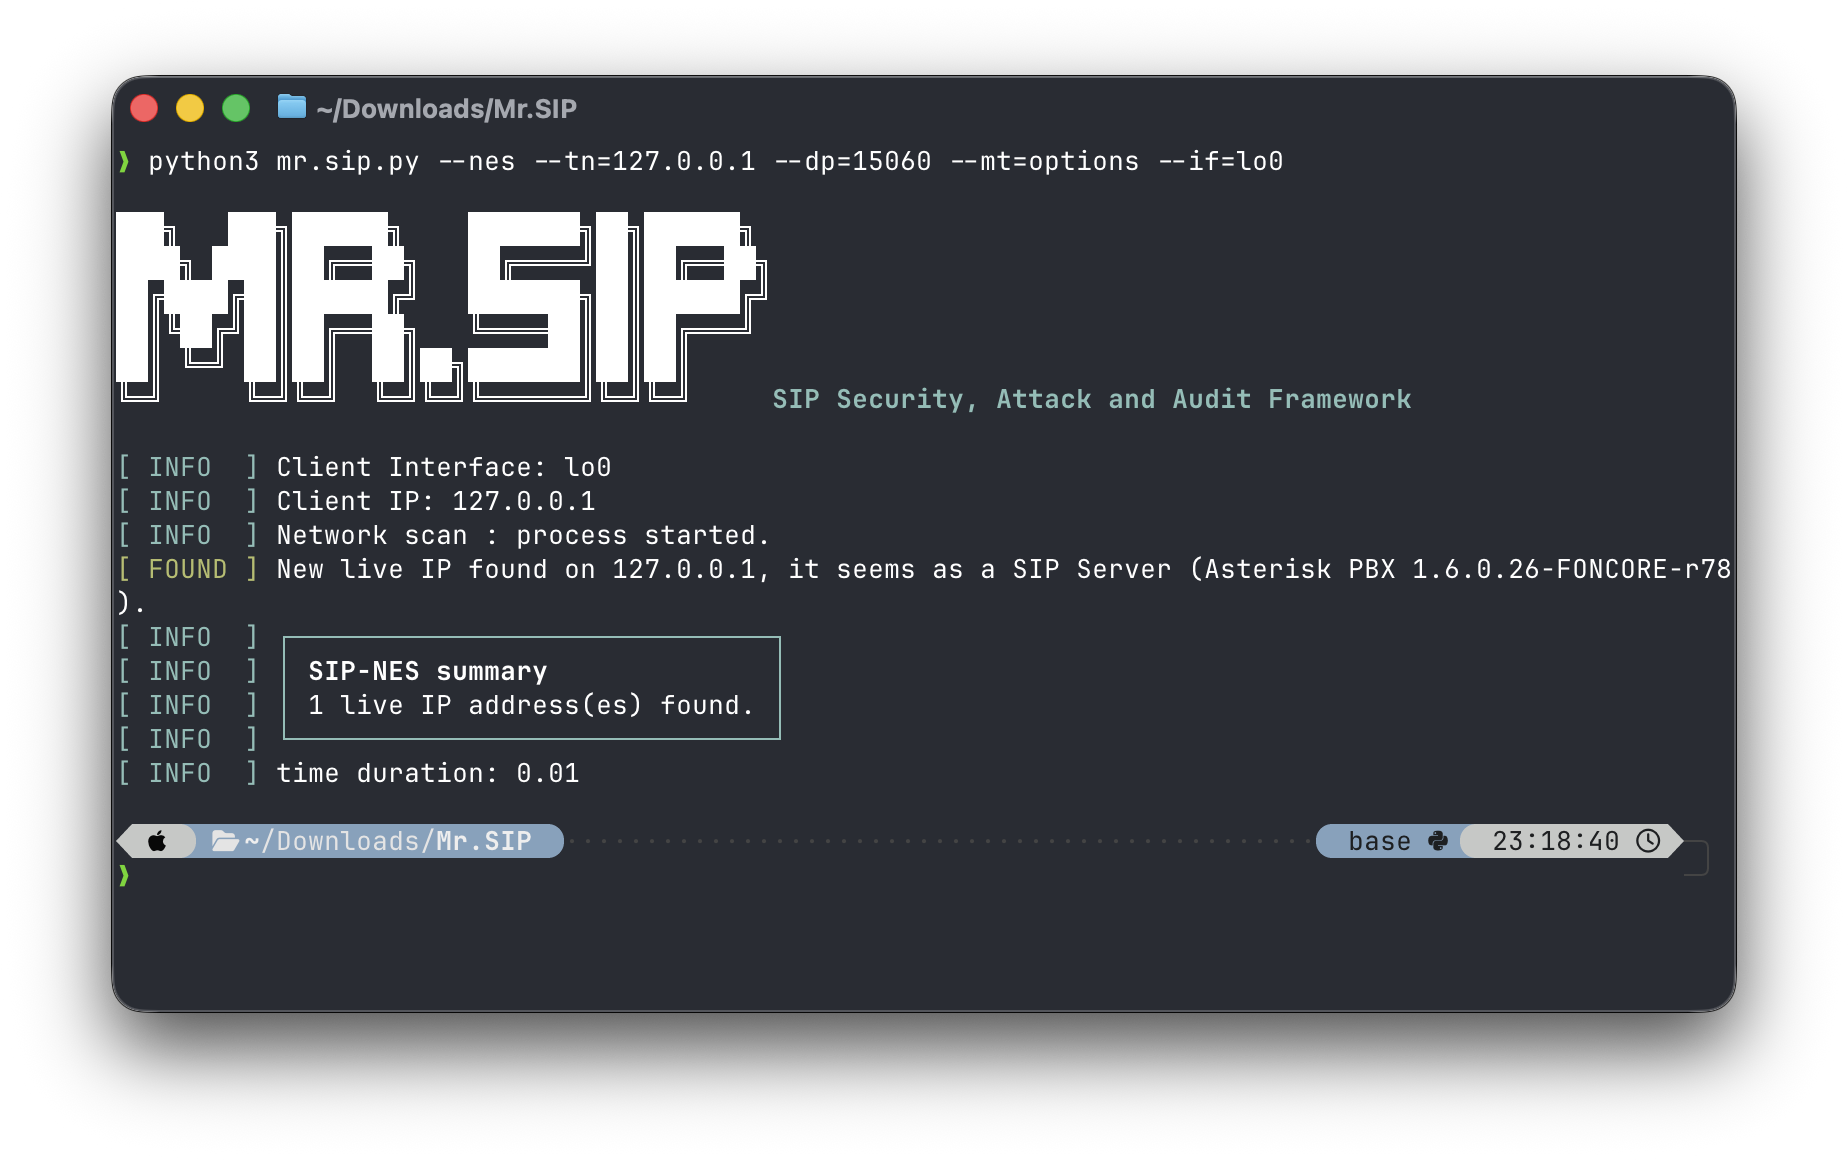
| SIP-NES (Network Scanner) | Detects SIP components on a network, along with manufacturer/product/ information. |
| SIP-ENUM (Enumerator) | Identifies valid SIP users and their authentication requirements. |
| SIP-DAS (DoS Attack Simulator) | Performs TDoS-based attacks, with a powerful IP-spoofing engine. |
Competiti across all three: high-performance multithreading, IP spoofing, and smart SIP message generation.
This is the public, 3-module — see what Mr.SIP Pro adds below.
Mr.SIP Pro
Mr.SIP Pro is the most comprehensi VoIP product a — 10 modules across 3 categories (Information Gathering, Scanning, Offensive), plus IP spoofing/message-generation helper components and a GUI, this repo's 3 console-only modules.
→ Full Public vs. Pro comparison · mrsip.pro · Pricing · Request a demo
Quick Start
See the Installation Guide for OS-specific setup and the Usage Guide for the full command/flag reference.
<di="center">
<img src="assets/screenshots/SIP-NES.png" alt="SIP-NES scan output" width="700">
</div>
De
This repo has a real test suite and CI - see CHANGELOG.md for the full technical history of fixes and hardening work.
---
Recognition
Mr.SIP started as academic research into no DDoS attacks and grew into a tool presented at some of the industry's largest security conferences, cited across peer-re literature, and recognized in national inno competitions.
Global Stage Recognition
See presentation links and video demos on the Demo Page.
Academic & Technical Impact
Research originating from and building on Mr.SIP has contributed to peer-re academic work on SIP/VoIP security, including DDoS and DRDoS attack techniques, defensi, and blockchain-based caller-ID authentication. This work has been published in well-established international journals, including IEEE Access, Applied Sciences, and Computers & Security.
Across these publications, Mr.SIP and the research built around it ha to the exploration of several SIP/VoIP attack and defense concepts, including:
Mr.SIP has also been reported as a reference in professional and graduate-le work, including Cisco Press material and graduate theses, representing additional practitioner and academic impact beyond the peer-re publications listed above.
Beyond academic research, Mr.SIP has also been used in practical VoIP security research and testing. In 2015, it was used in Caller-ID spoofing tests conducted as part of a Turkish Standards Institute (TSE) collaboration related to national VoIP security strategy.
The project has also recei security-community recognition. Mr.SIP was featured by Black Hat and showcased at major cybersecurity conferences, including Black Hat Arsenal and DEF CON.
Awards & Recognition
Mr.SIP Pro has earned recognition through inno challenges and national competitions — including awards for ideas, early prototypes, or research projects that contributed directly to its foundation and e.
Published References (full citations)
License
GPL-3.0
项目信息
开发语言:Python
Star 数:436
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Mr.SIP - SIP Security Assessment Framework for VoIP Pentest |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:41:34 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 83 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |