 红蓝攻防
点击放大
SAMDump - Extract the SAM and SYSTEM hives using the Volume
项目说明
SAMDump
Extracts Windows SAM and SYSTEM files using Shadow Copy Service (VSS) with multiple exfiltration options and XOR obfuscation:
It requires elevated pri, and if created the Shadow Copy is automatically deleted after ~5 minutes.
It is implemented in C++, C#, Crystal, Deno, Python, Rust, Golang and Nim, and it works on modern Windows .
<br>
Usage
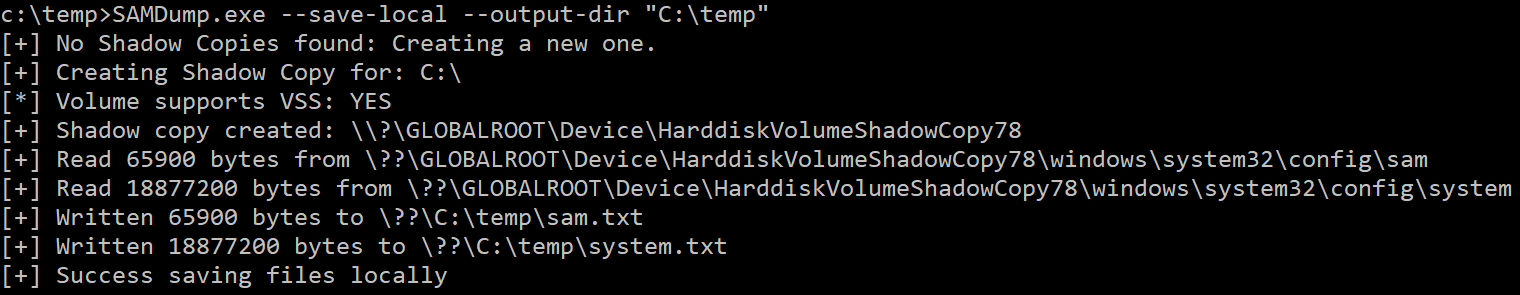
Sa without encoding:
!img1
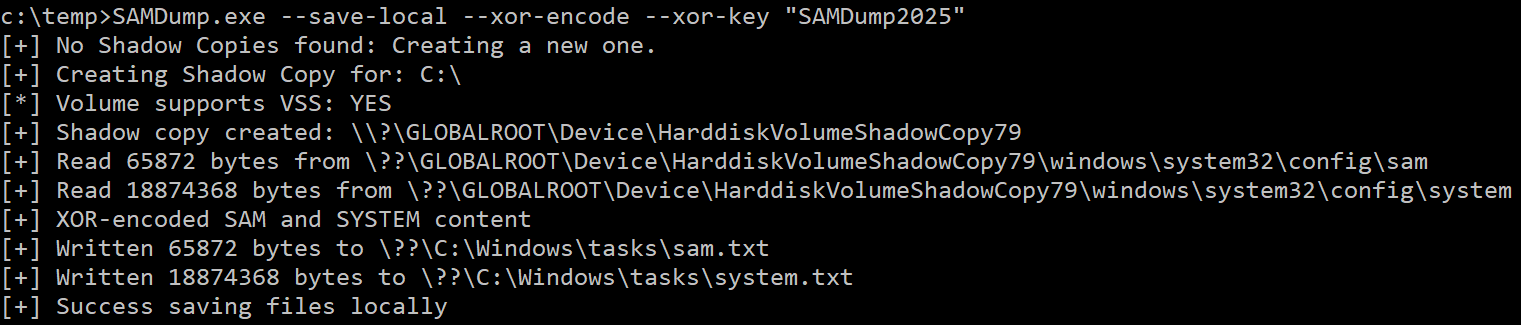
Sa with XOR encoding:
!img2
Send to remote server with XOR encoding and the default key:
!img3
<br>
Server to receive the files
*server.py* is a Python server that recei o with automatic XOR decoding and filename formatting:
Listener on specific interface and port with XOR key:
!img4
The filename contains the IP address and the date, so you can send the files from different systems, automating the process.
<br>
Script to decode the files
*xor-decoder.py* is a Python script to decode XOR-encoded SAM and SYSTEM files locally:
Decode with default key:
!img5
Decode with custom key and output directory:
!img6
<br>
Moti
I wanted to automate this process and most Windows I find run VSS, but security solutions detect the use of ** to create Shadow Copies and extract these files because it is a well-known technique.
This tool extracts the files without writing to the target filesystem when using remote transfer mode; and XOR-encoding offers basic obfuscation to evade signature-based detection (even when using remote mode).
Plus, it le NT API calls to bypass some monitoring and user-mode API hooks.
<br>
NT API Integration
The tool employs NT system calls instead of standard Windows API functions, which might bypass some user-mode API hooks commonly monitored:
NtCreateFile and NtReadFile: Used to open a handle and read the bytes of the SAM and SYSTEM files in the Shadow Copy
NtWriteFile: Used to save the files locally
<br>
Compilation (for Windows)
C++
Open SAMDump.sln in Studio and build.
C#
Compile using Studio or msbuild.
Crystal
Deno
Or run it directly from the repo without cloning:
Rust
Golang
Nim
Python
You can use the Python script:
Or create a stand-alone binary with:
<br>
Acknowledgements
Thanks to @ for identifying and suggesting optimizations in the Export Address Table (EAT) tra code, replacing unnecessary NtRead calls with direct pointer access.
项目信息
开发语言:C#
Star 数:386
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SAMDump - Extract the SAM and SYSTEM hives using the Volume |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:42:34 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 402 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |