 红蓝攻防
点击放大
smokedmeat - A CI/CD Red Team Framework for demonstrating Build
项目说明
SmokedMeat
![License: AGPL v3]()
CI/CD Red Team Framework
> Like Metasploit, but for CI/CD pipelines.
*From the makers of the poutine Build Pipeline SAST scanner at BoostSecurity Labs.*
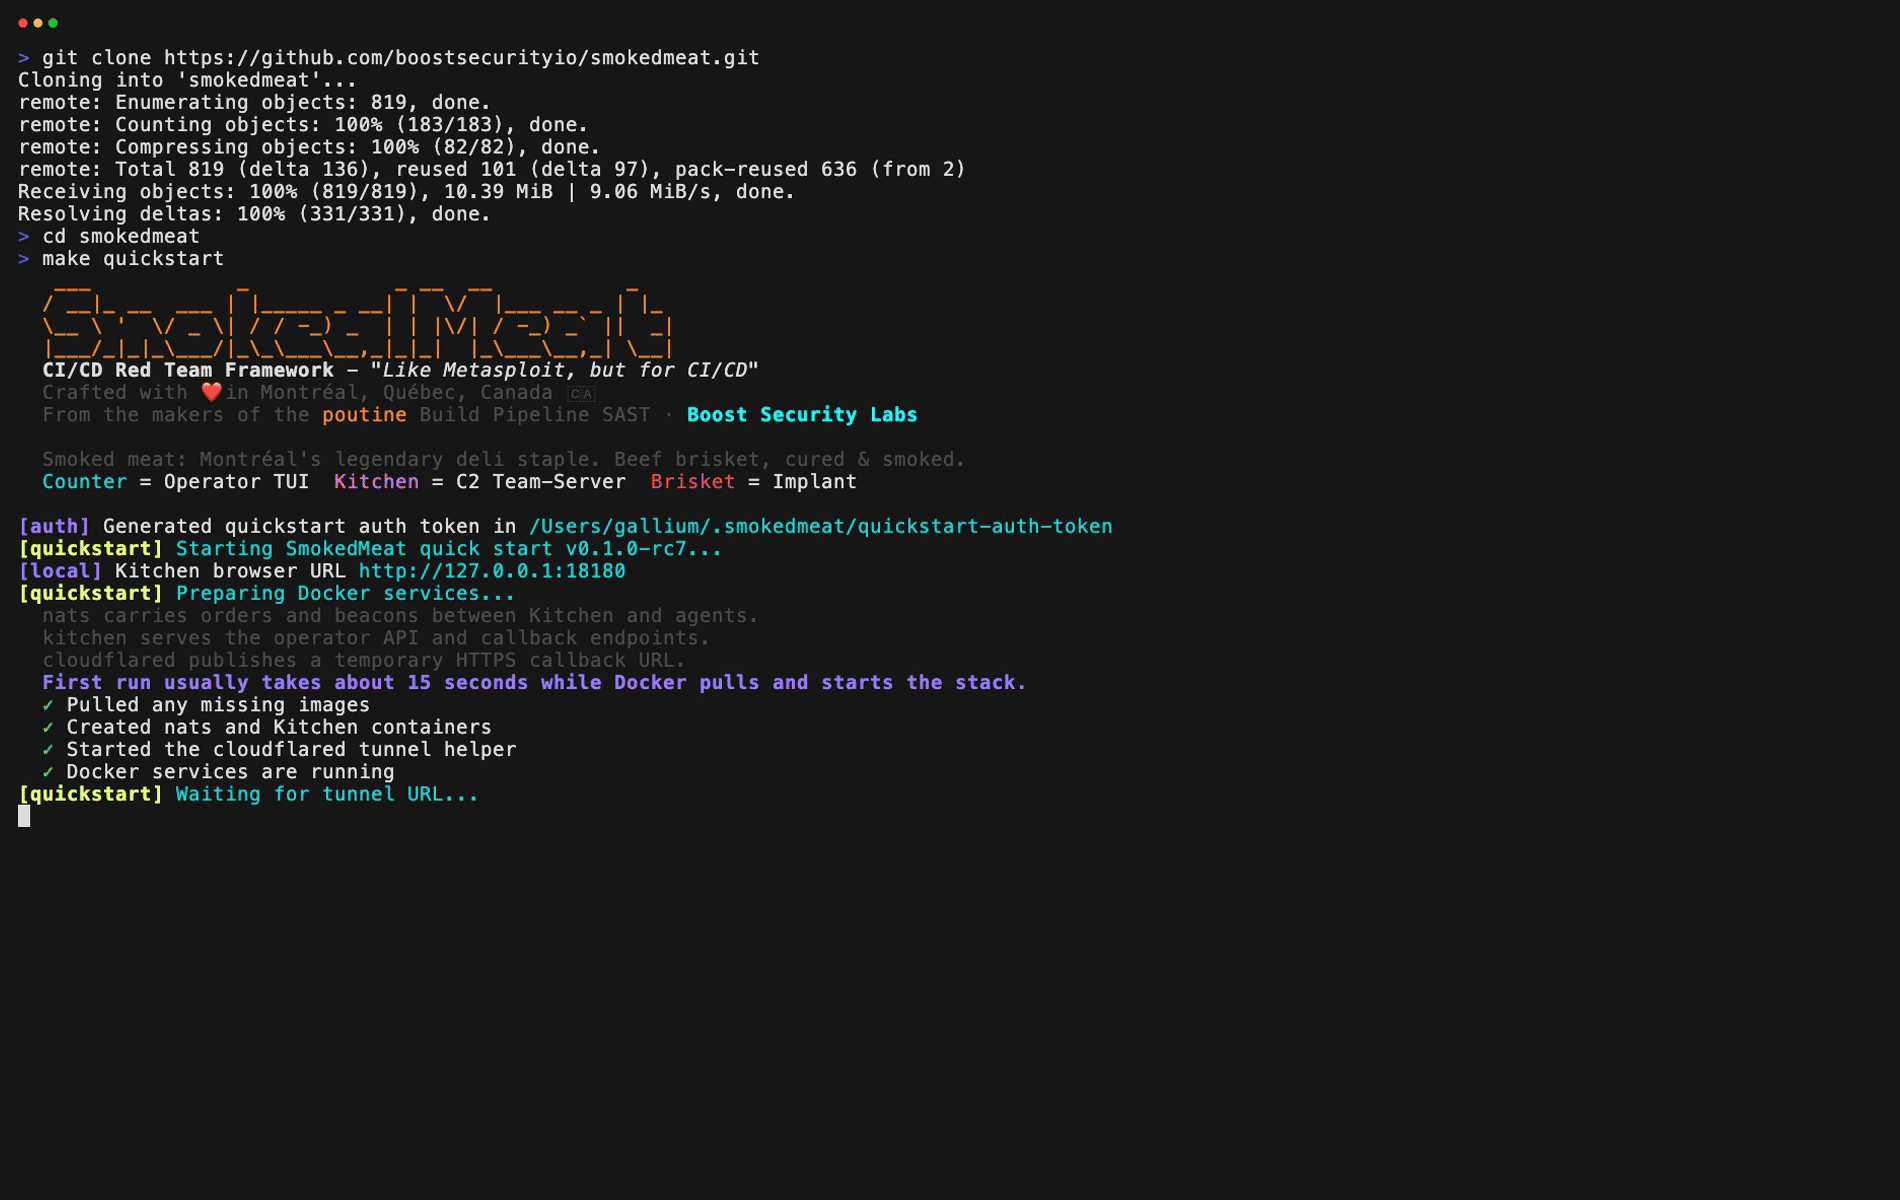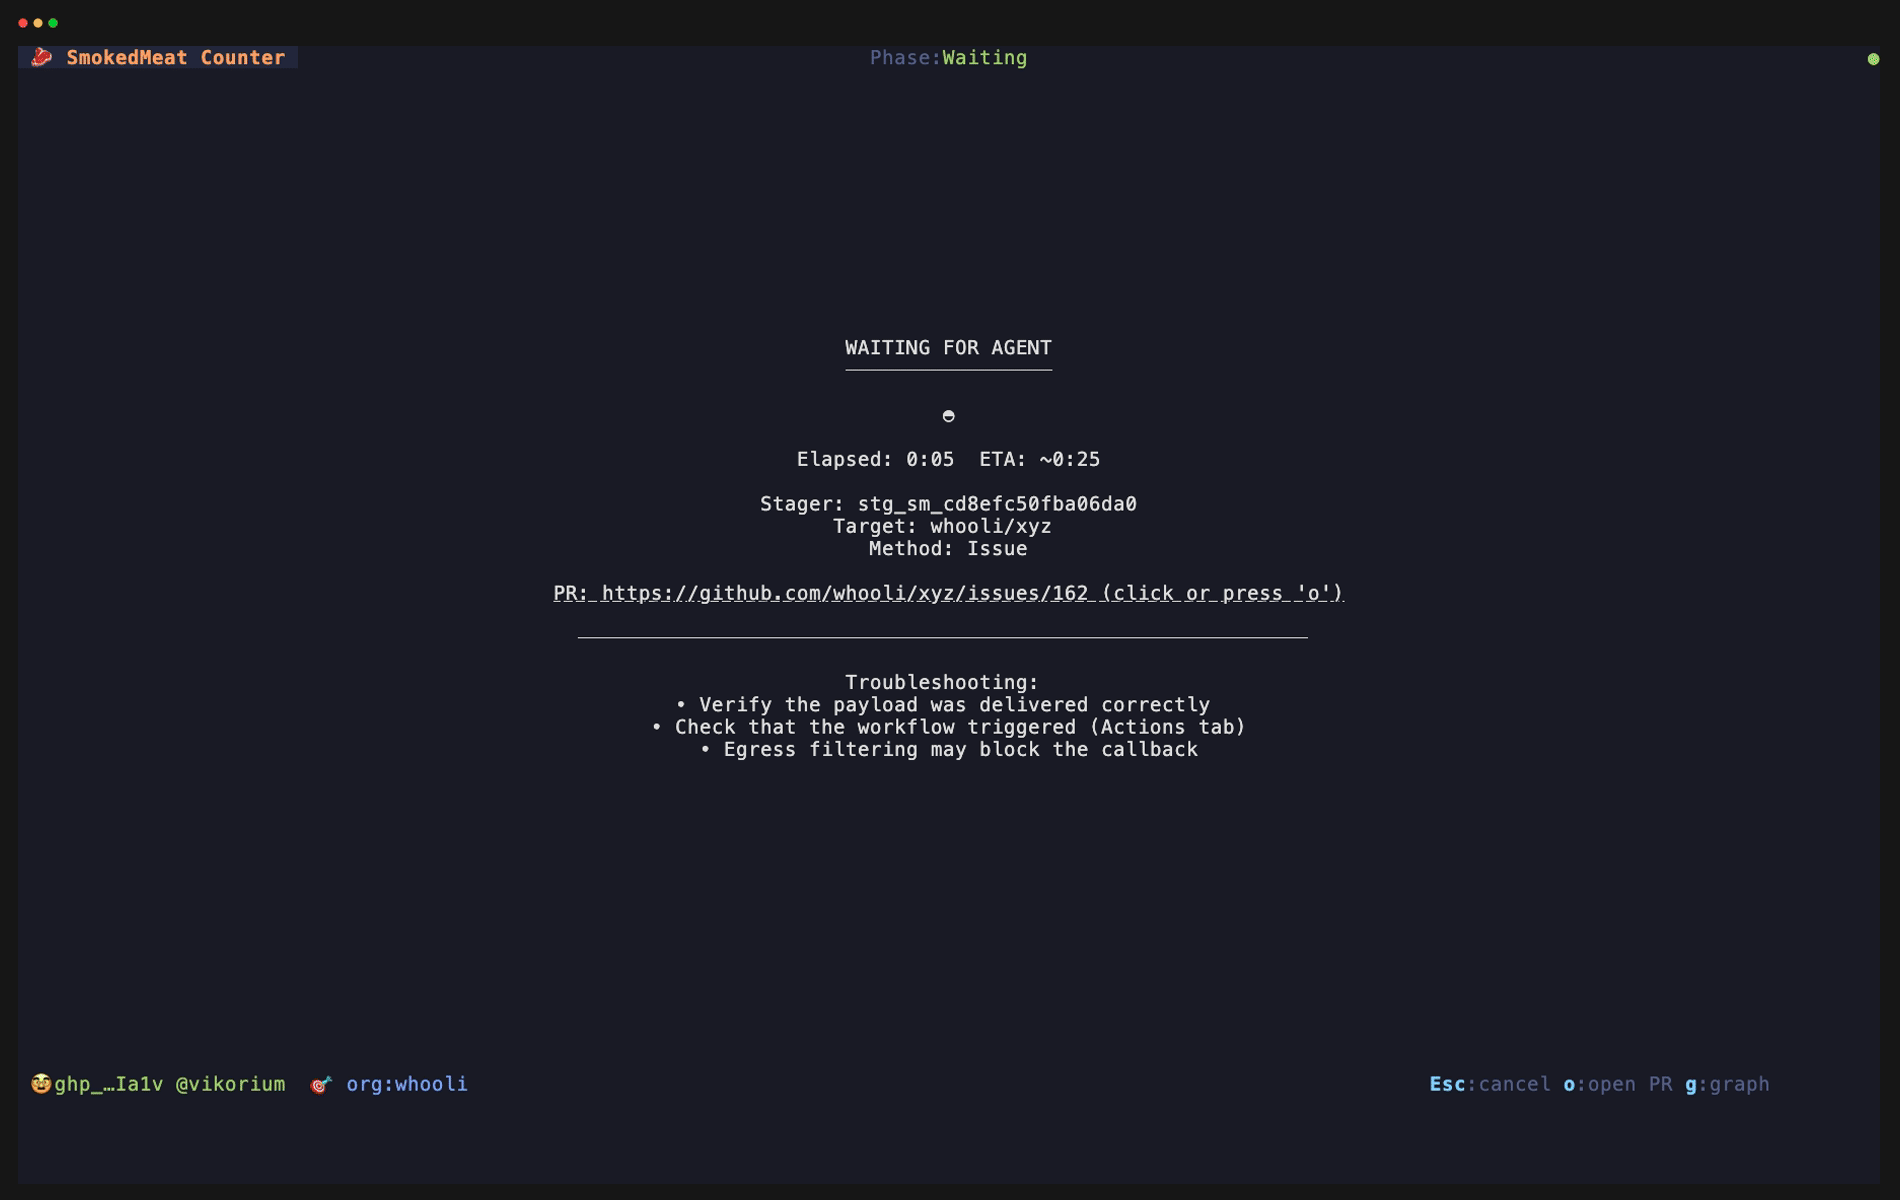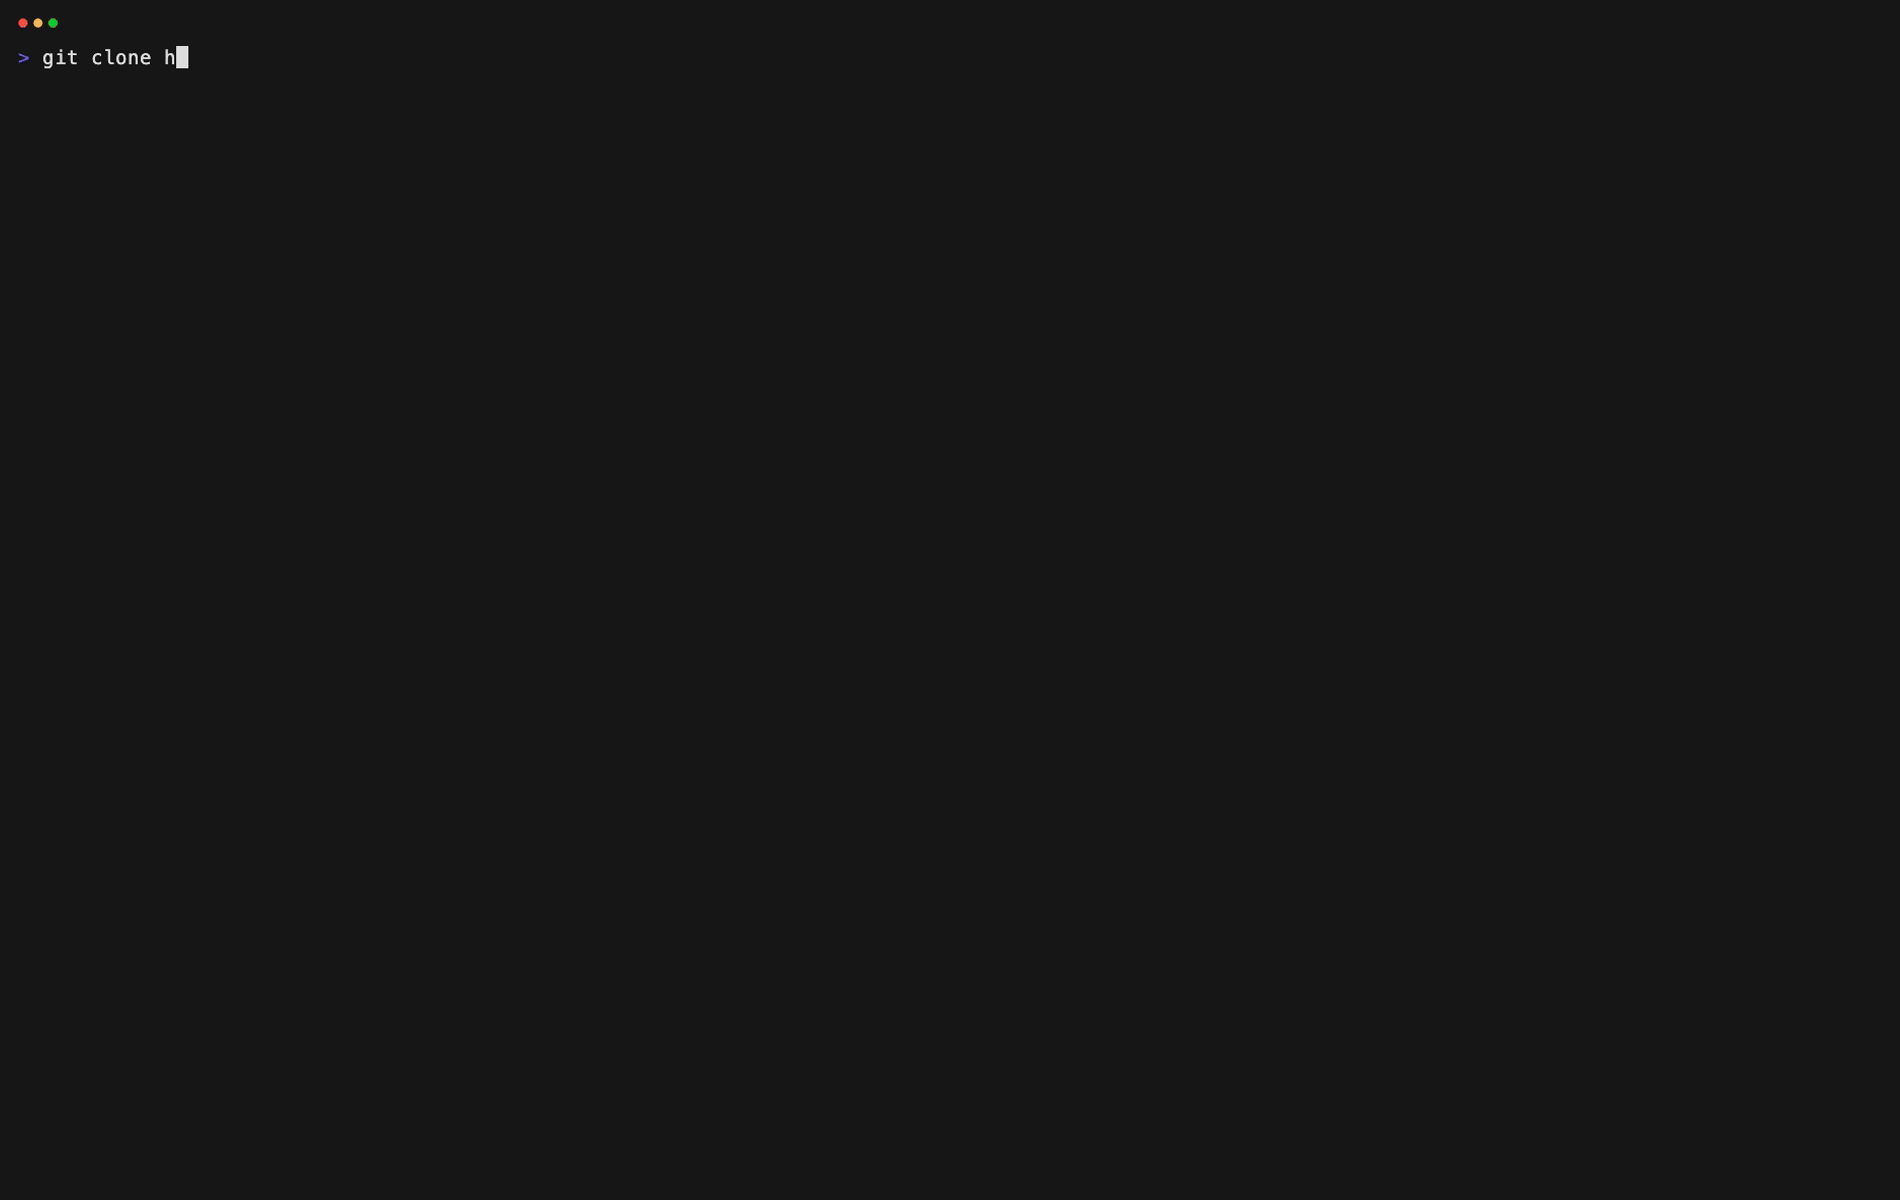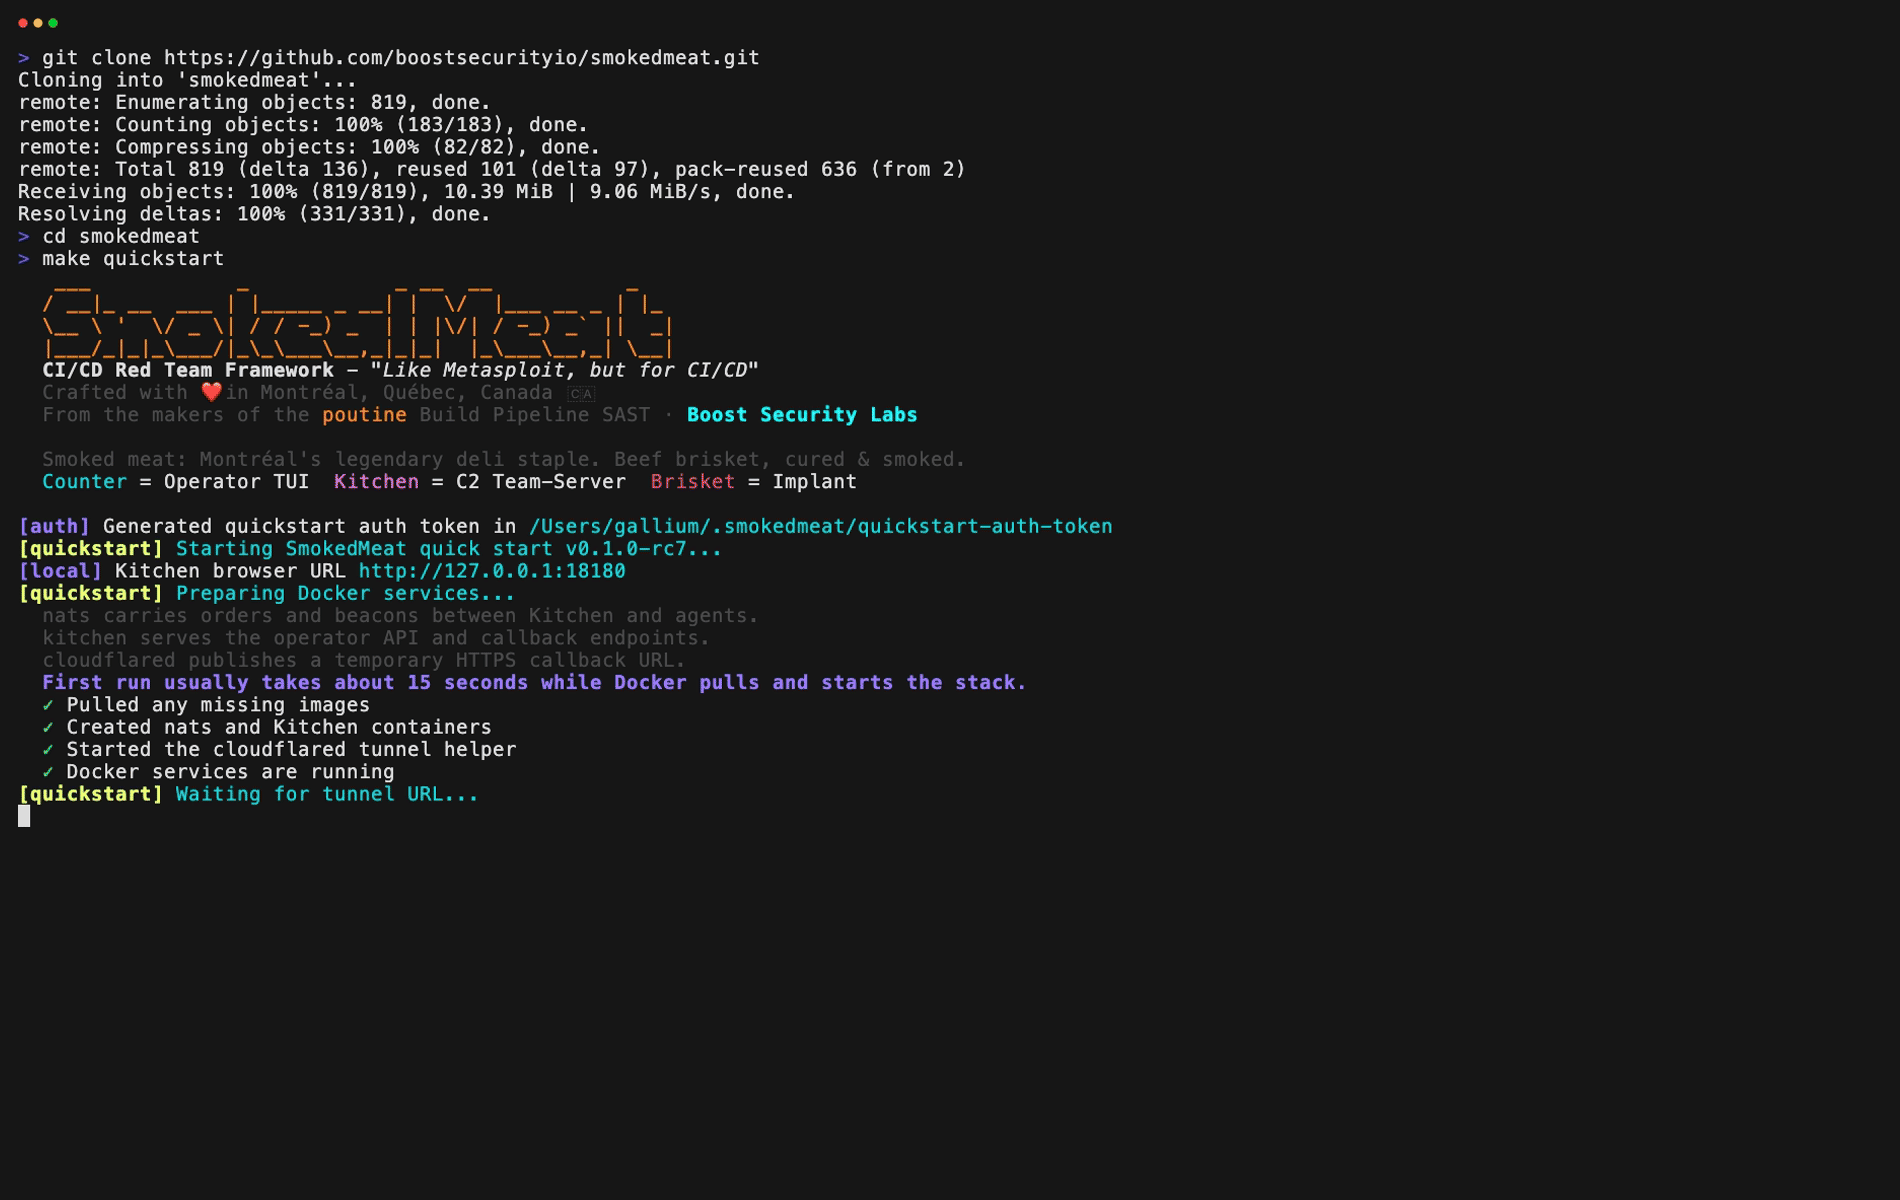
!SmokedMeat quickstart demo
---
> Warning: This tool is for authorized security testing only.
>
> SmokedMeat exists because CI/CD pipeline threats are deeply underestimated. Traditional security training rarely covers supply chain attacks, leaving defenders unprepared for techniques that ad actively exploit in the wild.
>
> We built this to gi teams the ability to learn, practice, and defenses against ad CI/CD attack techniques through realistic red team exercises.
>
> Only use against systems you own or ha written permission to test.
---
What is SmokedMeat?
SmokedMeat is a post-exploitation framework for CI/CD pipelines. Point it at a GitHub organization, let it find workflows, deploy an implant to a compromised runner, then pi cloud pro, extract secrets, and map the blast radius - all from a terminal UI.
What it does:
1. Analyze - Scan an org's GitHub Actions workflows for injection , dangerous triggers, and unsafe checkout patterns (powered by poutine)
2. Exploit - Deploy a stager via PR, issue, comment, or workflow dispatch. When the workflow runs, it downloads and executes the implant on the CI runner.
3. Post-exploit - Extract secrets from runner memory, enumerate GitHub token permissions, scan for private keys, and collect loot
4. Pivot - Use captured credentials to mo: disco repos, mint GitHub App tokens, exchange OIDC tokens for AWS/GCP/Azure access, probe SSH deploy keys
Philosophy: Bold and noisy. This isn't an EDR e tool. It's a demonstration framework that shows how deep a CI/CD compromise goes before anything triggers an alert.
Who is it for:
Quick Start
To try SmokedMeat for the first time, install Docker and make. Go is not required.
make quickstart is the recommended first run. It starts the stable release quickstart stack locally and launches the operator TUI (Counter) against the local C2 teamserver (Kitchen).
Recommended first run:
whoolipublic_repo⚠ Prefer a classic PAT. Fine-grained PATs can be too restrictive and may block testing public targets in other orgs, including whooli.
whooli is SmokedMeat's deliberately CI/CD attack playground. It is the recommended first target for the public path.
The setup wizard walks you through:
1. GitHub PAT - Enter your token. For private repos, a classic PAT will usually need repo.
2. Target - Enter whooli or your own org/repo
3. Analysis - Scans workflows for and presents exploitable findings
For the full challenge flow, see the whooli guide or go straight to the whooli GitHub org.
When you are done:
If you want to work from source instead, see De.
De
If you are contributing or iterating on the source tree locally, install Go 1.26+ and use the de:
make de builds the local smokedmeat-cloud-shell image, starts cloudflared, nats, and the C2 teamserver (Kitchen), then launches the operator TUI from source.
If you want the infrastructure first and the operator TUI later:
When you are done:
More deployment modes and local de details are in docs/deployment.md.
Check
Counter checks for newer SmokedMeat releases at startup. It can be disabled by setting the SMOKEDMEAT_DISABLE_ en .
Core Components
| Standard term | SmokedMeat name | Description |
|---------------|-----------------|-------------|
| Operator TUI | Counter | Terminal interface for analysis, payload delivery, and post-exploitation workflow. |
| C2 teamserver | Kitchen | API and WebSocket server for operator sessions, stagers, callbacks, and graph state. |
| Implant | Brisket | Agent delivered to compromised CI runners for beaconing, command execution, and pi. |
| Browser graph view | Browser View | Li graph served by the C2 teamserver at /graph. |
Deployment Modes
| Mode | Use it when | Entry point |
|------|-------------|-------------|
| Quickstart | Fastest first run on the pinned release | make quickstart |
| De | Working on the source tree locally | make de |
| Hosted Teamserver | Running a real engagement with a stable domain | docs/deployment.md |
Hosted Teamserver runs the C2 teamserver on a dedicated host and the operator TUI natively on each operator workstation.
Architecture
At a high level, the operator TUI (Counter) talks to the C2 teamserver (Kitchen), which manages implants (Brisket) running on compromised CI runners and serves the li graph.
Features
Full details in docs/FEATURES.md.
| Category | Capabilities |
|----------|-------------|
| Reconnaissance | Auto-detect 6 CI platforms (GitHub Actions, GitLab CI, Azure DevOps, CircleCI, Jenkins, Bitbucket). Classify secrets, probe OIDC a, gather runner metadata. |
| Secret Extraction | Scan Runner.Worker process memory via /proc to reco secrets.*, vars.*, and GITHUB_TOKEN permission maps that GitHub hides from logs. |
| Analysis | Embedded poutine SAST for injection , dangerous triggers, and workflow if: gate classification. Gitleaks deep scan for private keys and PATs in git history. |
| Delivery | 5 automated methods: PR, issue, comment, LOTP, workflow dispatch - plus copy-only and manual. Draft PR support, auto-close on callback, ser dispatch preflight. |
| Injection Payloads | Context-aware payload generation for 8 injection (branch name, PR title/body, commit message, issue title/body, github-script, bash run) with constraint-aware techniques. |
| LOTP | Living Off The Pipeline catalog: 15 build tools (npm, pip, cargo, make, docker, gradle, maven, and more) with config-file payloads for code execution during install/build/test. |
| Cache Poisoning | Writer/ classification, exact cache key prediction, archi via the Actions Cache API. Wizard-driven flow with implant arming. |
| Token Enumeration | Probe GitHub tokens against API endpoints to enumerate 10 permission scopes, identify token type, and list accessible repos and orgs. |
| Cloud Pivots | OIDC token exchange for AWS (sts:AssumeRoleWithWebIdentity), GCP (Workload Identity Federation), Azure (AAD), and Kubernetes. Post-pi enumeration. |
| Cloud Shell | Durable local sessions with cloud shell (pre-configured gcloud/aws/az), cloud export, and provider quick checks. |
| SSH Pi | Probe repos for SSH deploy key access (read/write), ssh shell with temporary agent, confirmed access persisted to graph. |
| GitHub Pi | pi for repo discovery, pivot app for GitHub App PEM-to-installation-token exchange. Discovered repos auto-queued for analysis. |
| Attack Graph | Persistent directed graph (BBolt) with org/repo/workflow/job/vuln/token/cloud nodes. Li.js browser at /graph. |
| Operator TUI | Phase-aware workflow, 7-step setup wizard, attack tree na, exploit wizard, loot stash, omnibox search, tab completion, OSC 8 hyperlinks. |
| Teamserver | SSH or token auth, NATS JetStream message bus, GitHub API proxy (tokens stay ser), auto-TLS , operation history. |
Technology Stack
| Layer | Technology |
|-------|------------|
| Language | Go 1.26+ |
| TUI Framework | Bubbletea v2 + Lipgloss v2 |
| TUI Layout | Ultra layout + ANSI-safe screen compositing |
| Message Bus | NATS JetStream |
| Attack Graph | hmdsefi/gograph |
| Graph | Cytoscape.js |
| Database | BBolt |
| CI/CD Scanner | poutine (embedded) |
| Secret Scanner | gitleaks (embedded, custom rules) |
| Runner Secret Extraction | gump (embedded, /proc memory scanning) |
| Cloud SDKs | AWS SDK v2, Google Cloud, Azure SDK for Go |
| Reverse Proxy | Caddy (auto-TLS) |
Testing
Prior Art
SmokedMeat builds on research from:
License
GNU Affero General Public License v3.0 - see LICENSE for details.
---
*Built for defenders who want to understand attacker techniques.*
项目信息
开发语言:Go
Star 数:384
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | smokedmeat - A CI/CD Red Team Framework for demonstrating Build |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:42:37 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 529 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |