 红蓝攻防
点击放大
项目说明
---
description: ruby for pentesters
---
Module 0x0 | Introduction
 (1) (5).png>)\
_Rubyfu, where Ruby goes evil!_\
!Twitter Follow
Introduction
This book is a great collection of ideas, tricks, and skills that could be useful for Hackers. It's a unique extraction reference, summarizes a lot of research and experience in order to achieve your w00t in the shortest and smartest way. Rubyfu is where you'll find plug-n-hack code. Rubyfu is a book to use not only to read, it's where ruby goes evil.
Who should read this book?
Ideally, Hackers! Those who ha experience to hack our world and have _at least_ basics in the Ruby programming language. To get the best benefits of the book, open Rubyfu.net and pin its browser tab. Use the irb/pry interacti to run the code, or run it as a script. Enhance the code to fit your needs and yeah, tweet the code and its output to to share it with our awesome community.
Organization of the book
#### Module 0x0 | Introduction
Module 0x0 is just a smooth start for you, whether you're a reader, writer, hacker or someone who came to say hi. In this module you'll find a great start for you as a contributor, where all kinds of contributions are welcome starting from proofreading all the way up to topic writing.
#### Module 0x1 | Basic Ruby Kung Fu
Module 0x1 is an awesome collection of the most commonly needed string manipulation, extraction and con tasks; dealing with real cases that you might face during your hack. Your encoding and data con may be a trivial or complex challenge and here we don't care, we'll solve it.
#### Module 0x2 | System Kung Fu
Module 0x2 digs more into system hacking, where system commands, file manipulation, cryptography and generating common hashes are often needed. Getting simple bind and reverse shells with Ruby is a useful skill, no doubt. Almost all mainstream Linux systems are shipped with ruby and if not, no problem, we always ha ways to make use of our knowledge.
#### Module 0x3 | Network Kung Fu
Module 0x3 di into network sockets, protocols, packet manipulation, service enumeration and gives us more hacky and awesome code to get the job done. Working with network protocols needs a deeper knowledge of how these protocols work in order to exchange understandable data and yeah, we'll figure it out right here.
#### Module 0x4 | Web Kung Fu
Module 0x4 covers web topics. The web is the most common place to share information, making it one of the most delicious places to hack. Web hacking challenges, known for their uniqueness and with many potential technologies within a single page, require a tool with easily adaptable capabilities. Here we'll learn how to deal with GET & POST requests, web services, databases, APIs and manipulating the browser to make it our soldier.
#### Module 0x5 | Exploitation Kung Fu
Module 0x5 builds your exploitation abilities with Ruby. Whatever the may be, remote (FTP, IMAP, SMTP, etc.) or local (file format, local system) you'll need to know how to build fuzzers and skeleton exploits for it. If you get there you'll need a simple, clean and stable way to build your exploit. Here you'll learn how to build your fuzzer, exploit, and port your exploit to Metasploit -- and even how to write your own Metasploit modules too.
#### Module 0x6 | Forensic Kung Fu
Module 0x6 explores forensic capabilities with Rubyfu. Whoever you are: redteam, blueteam, or in-between you'll need some forensic skills in your hack and/or in. Here you'll learn more about how to deal with registry tasks, extracting browser information, and much more.
![]()
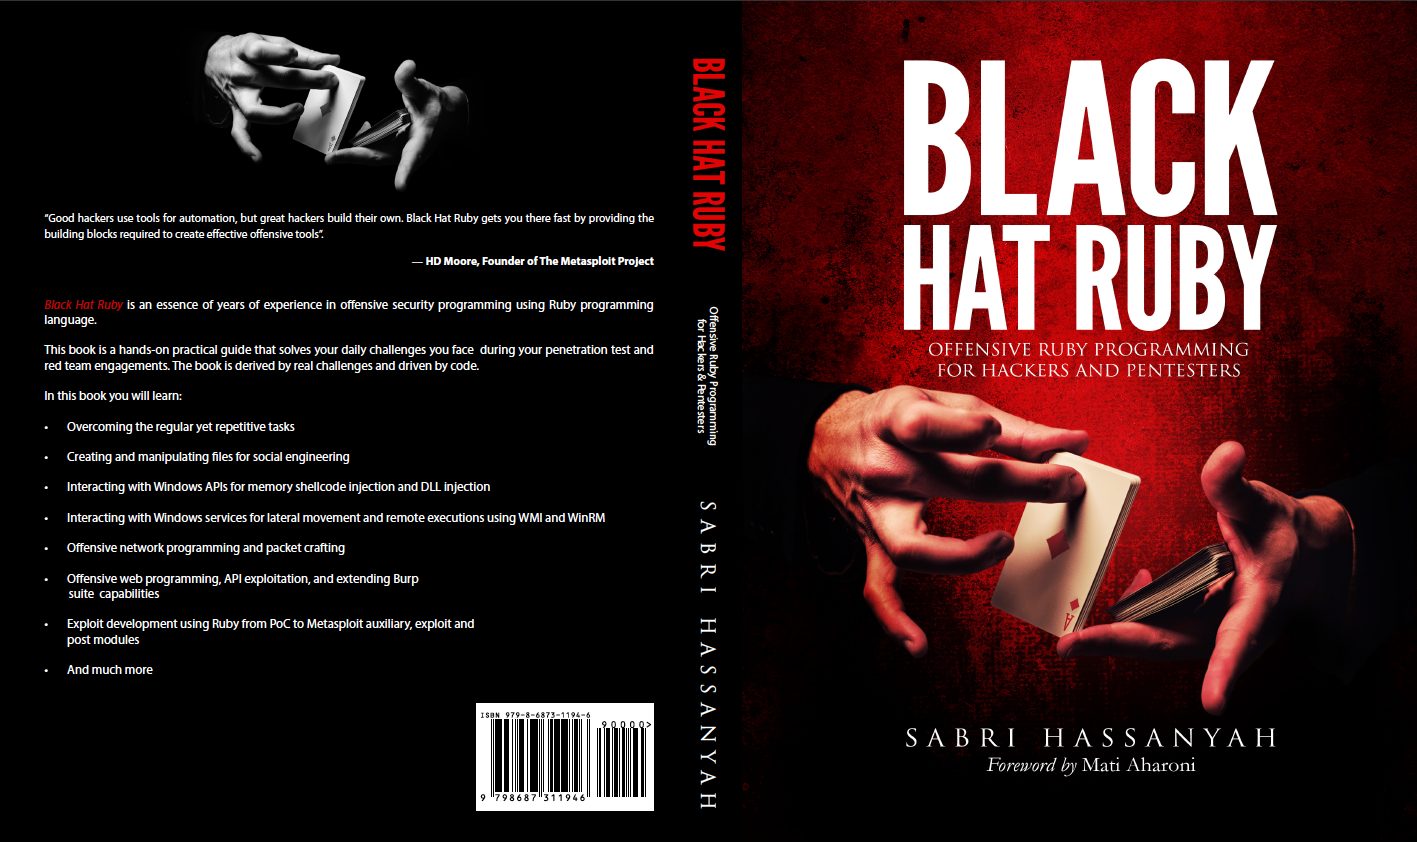
Black Hat Ruby — Offensive Ruby programming book for hackers & pentesters
Black Hat Ruby is the commercial edition of Rubyfu. The book contains many new topics and solving a lot of real-world challenges with detailed explanations targeting professionals.
!Black Hat Ruby cover
{% hint style="success" %}
You can purchase Black Hat Ruby on Amazon
{% endhint %}
The primary goal of Black Hat Ruby book is to provide you with a vast angle of using Ruby as an information security professional in an offensi. The book meant to help you with weaponizing Ruby language in offensi whether you are testing web applications, networks, systems, or exploit de to carve your ideas into working and achieving code.
Another intended goal of the book is to route you to the code that achieves your goal in the shortest time. This book is aimed at security researchers, security consultants, penetration testers, red teamers, or any professional who is interested in writing offensive Code.
In this book, you will learn:
* Hacker's day to day string manipulation, con, and extraction. 
* Compiling ruby to exe, parsing, and files such as XML, JSON, HTML, and binary. 
* Manipulating files stamps, creating malicious Shortcut, Excel & PDF files. 
* Generating the most common hashes for platforms. 
* Using ruby to execute system commands. 
* Tactical code for red teaming acti, such as lateral mo , WMI and creating malicious OLE and malicious Excel files for spear phishing. 
* Importing Windows system internal for execute shellcode, dll injection. 
* Introduction to the network Socket operations in Ruby and creating a remote shell. 
* Malicious use for network services such as HTTP, SSH, DNS, FTP, TFTP for exploitation and data exfiltration. 
* Packet manipulation and building network packet from the ground up to for ARP spoofing, rogue wireless access point (AP), SNMP spoofing and parsing captured pcap files. 
* Introduction about dealing with services and creating covert C2 for data exfiltration. 
* Automating the hunting of XSS and blind-XSS. • Exploiting Web socket and WSDL services and its APIs. 
* Using Slack as a C2 
* Understanding and creating ad Burp Suite scanner extensions (active and passive) and manipulate the Burp user interface in detail. 
* Step by step basic buffer o exploit de using ruby. 
* Porting your stand-alone exploit to Metasploit and creating Auxiliary, Exploit and Post modules.
Happy Hacking!
项目信息
开发语言:CSS
Star 数:357
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Rubyfu, where Ruby goes evil!展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | RubyFu - Rubyfu, where Ruby goes evil! |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:42:52 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 421 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |